#e2ee

47 posts · Last used 6d

So, the @EUCommission@ec.social-network.europa.eu has rolled out @element@mastodon.matrix.org chat as a backup system to their default #Teams for the 33k officials. One official defended the new #Matrix-based system on an internal chat, according to Politico, by saying Teams wasn't as secure because "all we have is a guarantee that #Microslop [sic!] will not peek inside," and how can anyone not love that official. #DigitalSovereignty #DigitalSecurity #e2ee
29
0
42
0
:haacknet: Haack's Networking :haacknet: ✍️ We would like to introduce everyone to our latest addition to the #pubglug PubGLUG community offerings. Ente #E2EE encrypted photos, files, and secrets is now live for testing. All users get 10GB upon sign up, but/and more is available upon request (DMs). The technical setup notes are here: 🔗 https://tech.haacksnetworking.org/2026/09/21/ente/ 💡 The instance link is here: 🔗 https://gnulinux.pics 📜 We are in testing right now and there will definitely be bugs and/or other issues that need addressing. Please let us know in replies, DMs, and/or hit us on Matrix or DC. For now, registration is open - if it proves to be a problem we will close it. Until then, happy hacking! #ente #sysadmin #selfhosted #caddy #debian #freesoftware #floss #opensource
2
0
2
0
In case you are falsely feeling protected outside of Europe: Chat Control doesn't just concern Europeans. It concerns all of us. These kind of regulations will come for all of us, everywhere, if we do not ALL push against it everywhere. If you do not understand how this is all intertwined, I invite you to read more privacy news and in-depth analysis. Because we must all support each other's privacy fights. Privacy is a human right 💚 Fight for a better world, together ✊🌍 #ChatControl #AgeVerification #DataMinimization #HumanRights #DigitalRights #Privacy #Encryption #E2EE #RootForE2EE 🎉
143
4
147
0
Embeddable Live Chat Widget (Intercom Alternative) Say hello to the ETHOS Live Chat Widget! 💬 You can now embed a 100% serverless, E2EE live chat on any website — like Intercom or Crisp, but with zero central backend, databases, or monthly fees! 🔹 Single tag setup 🔹 Isolated via Shadow DOM 🔹 Captures visitor page context 🔹 Direct E2EE to your ETHOS app Source & guide: github.com/aitherapp/ethos-core #WebDev #Privacy #Intercom #E2EE #OpenSource
0
0
1
0

Fedi, I have a design problem I'd appreciate thoughts on.

I've been building a federated E2EE messenger (based on MLS) where the server learns as close to nothing as possible about you, so there's no accounts or user records. Which raised the obvious question: how do you rate limit anything?

The answer I went with is PrivacyPass. You authenticate once to get a batch of tokens, so the server knows who you are at that moment. Then you spend them anonymously - they're blinded at issuance, so when one comes back the server can verify it's valid but can't tell who it gave it to. Rate limiting happens at issuance, not at send time. You get a budget: 2,000 tokens/hour, 10,000 burst. (the numbers are based on napkin math and can be adjusted)

Now the actual problem: one token buys one envelope, and an envelope goes to one device. Group messages fan out client-side, so a message to a group of D devices costs D tokens. At two devices per person, a 250-person group is 500 tokens per message which is about 4 messages/hour. So groups pretty much have to cap out around 200-250 people.

I can't just make fan-out cheaper, because the server can't see group membership. It genuinely cannot distinguish "500 envelopes because my group is large" from "500 envelopes because I'm spamming 500 strangers." Any discount that makes fan-out affordable makes spam affordable by exactly the same factor.

The only structural escape I've found is to stop fanning out - one envelope that many people fetch. But then the server sees N people reading one mailbox, which hands it the group membership the per-recipient design exists to hide.

So:

  1. Is there a way to prove "this batch is fan-out to a group I belong to" without revealing the group or its members? Feels anonymous-credential-shaped but I haven't found the primitive.
  2. Is ~250 people a reasonable ceiling to just accept?
  3. Anything obvious I'm missing?

#Cryptography #Privacy #InfoSec #E2EE #SecureMessaging
0
3
0
0
Like most social networks, Mastodon is not end-to-end encrypted. If you're sending sensitive info it's better to use a separate end-to-end encrypted messaging app. Mastodon itself warns you about this if you are sending a DM through the web interface (see the screenshot). More info about the risks and how to mitigate them in the guide at: ➡️ https://fedi.tips/is-mastodon-end-to-end-encrypted TL:DR - Main risk is your server admin reading your DMs, but they would need techy skills to do this. #FediTips #Mastodon #E2EE
70
7
82
2
#FediHood is now available! Talk with people near you. A local chat on the #Fediverse where you share only your city, never your exact location. You adjust your timeline with distance and topic filters. It's in early beta and web only for now. It connects to the whole Fediverse, and you can send #E2EE DMs between FediHood and Holos users. The source code will be published soon. Don't hesitate to share! Instance: https://fedihood.social
109
8
128
3

Decentralized browser-based P2P E2EE messaging.

The key detail that sets this apart from other messaging apps is the browser-based client-side cryptography philosophy.

No need to install anything. Your ID is crypto-random and so the app doesnt need to rely on any central registration system like phone numbers. Your ID is unguessable and to connect to someone, you have to explicitly share it.

WebRTC has other nuances like being to route through a shared network for secure/faster transfer.

I hope this project has reached a level i can share the following details. I've made a genuine effort towards documentation and transparancy. I dont think it'll ever be enough and so im still concerned it isnt ready to share. While im using AI throughout. This is not a vibecoded project. There is attention throughout for unit tests and formal-verification. With your feedback, id like to make improvements for clarity throughout.

This version of the app demonstrates a fairly unique approach using a browser-based, local-only and webrtc approach. I know it's impossible for any system to be the "world's most secure", but that isnt a reason to not try. By rigorously implementing an exhaustive list of security features and practices, the aim is to get as close as possible.

This is intended to demonstrate client-side managed secure cryptography.

I know ive tried to compress a lot of my journey into one post. The project above is going to be tricky to understand. Feel free to reach out for clarity on any of the details.

IMPORTANT: While this is aiming to provide a secure experience, It is not audited or reviewed. Shared for testing, feedback and demo purposes only. Please use responsibly.

#Privacy #OnlinePrivacy #DataPrivacy #Infosec #CyberSecurity #OpSec #DigitalRights #AntiSurveillance #DataOwnership #E2EE #P2P #PeerToPeer #WebRTC #LocalFirst #LocalOnly #NoCloud #NoRegistration #PWA #SignalProtocol #PostQuantum #Cryptography #SecureMessaging #PrivateChat #EncryptedChat #Decentralized #OpenSource #SelfHosted #BetaTesting #FeedbackWelcome #TechDemo #ProofOfConcept #BuildInPublic #IndieDev #DevCommunity

4
0
4
0
Boosted by @fedicat@pc.cafe
FEP-0806: Simple client-side encryption https://codeberg.org/silverpill/feps/src/branch/main/0806/fep-0806.md The FEP now includes the recommended algorithm parameters. I consider it finished but I don't plan to continue working on my implementation or publishing to the main FEP repository. It would be better to focus on group messaging with forward secrecy (MLS or similar). #fep_0806 #e2ee
0
0
2
0
Replying to
@brayd@social.brayd.blog there is always #matrix but from my experience it is way heavier than xmpp. OMEMO, the XMPP E2E thing, is/was based on the Signal (Axolotl) crypto protocol and probably doesn't work worse than what Matrix gives you in that regard. Both have ample selection on servers and clients these days. Give both a try. #xmpp #omemo #axolotl #e2ee #e2e #matrix #selfhosing #decentralized #instantmessaging
4
0
0
0

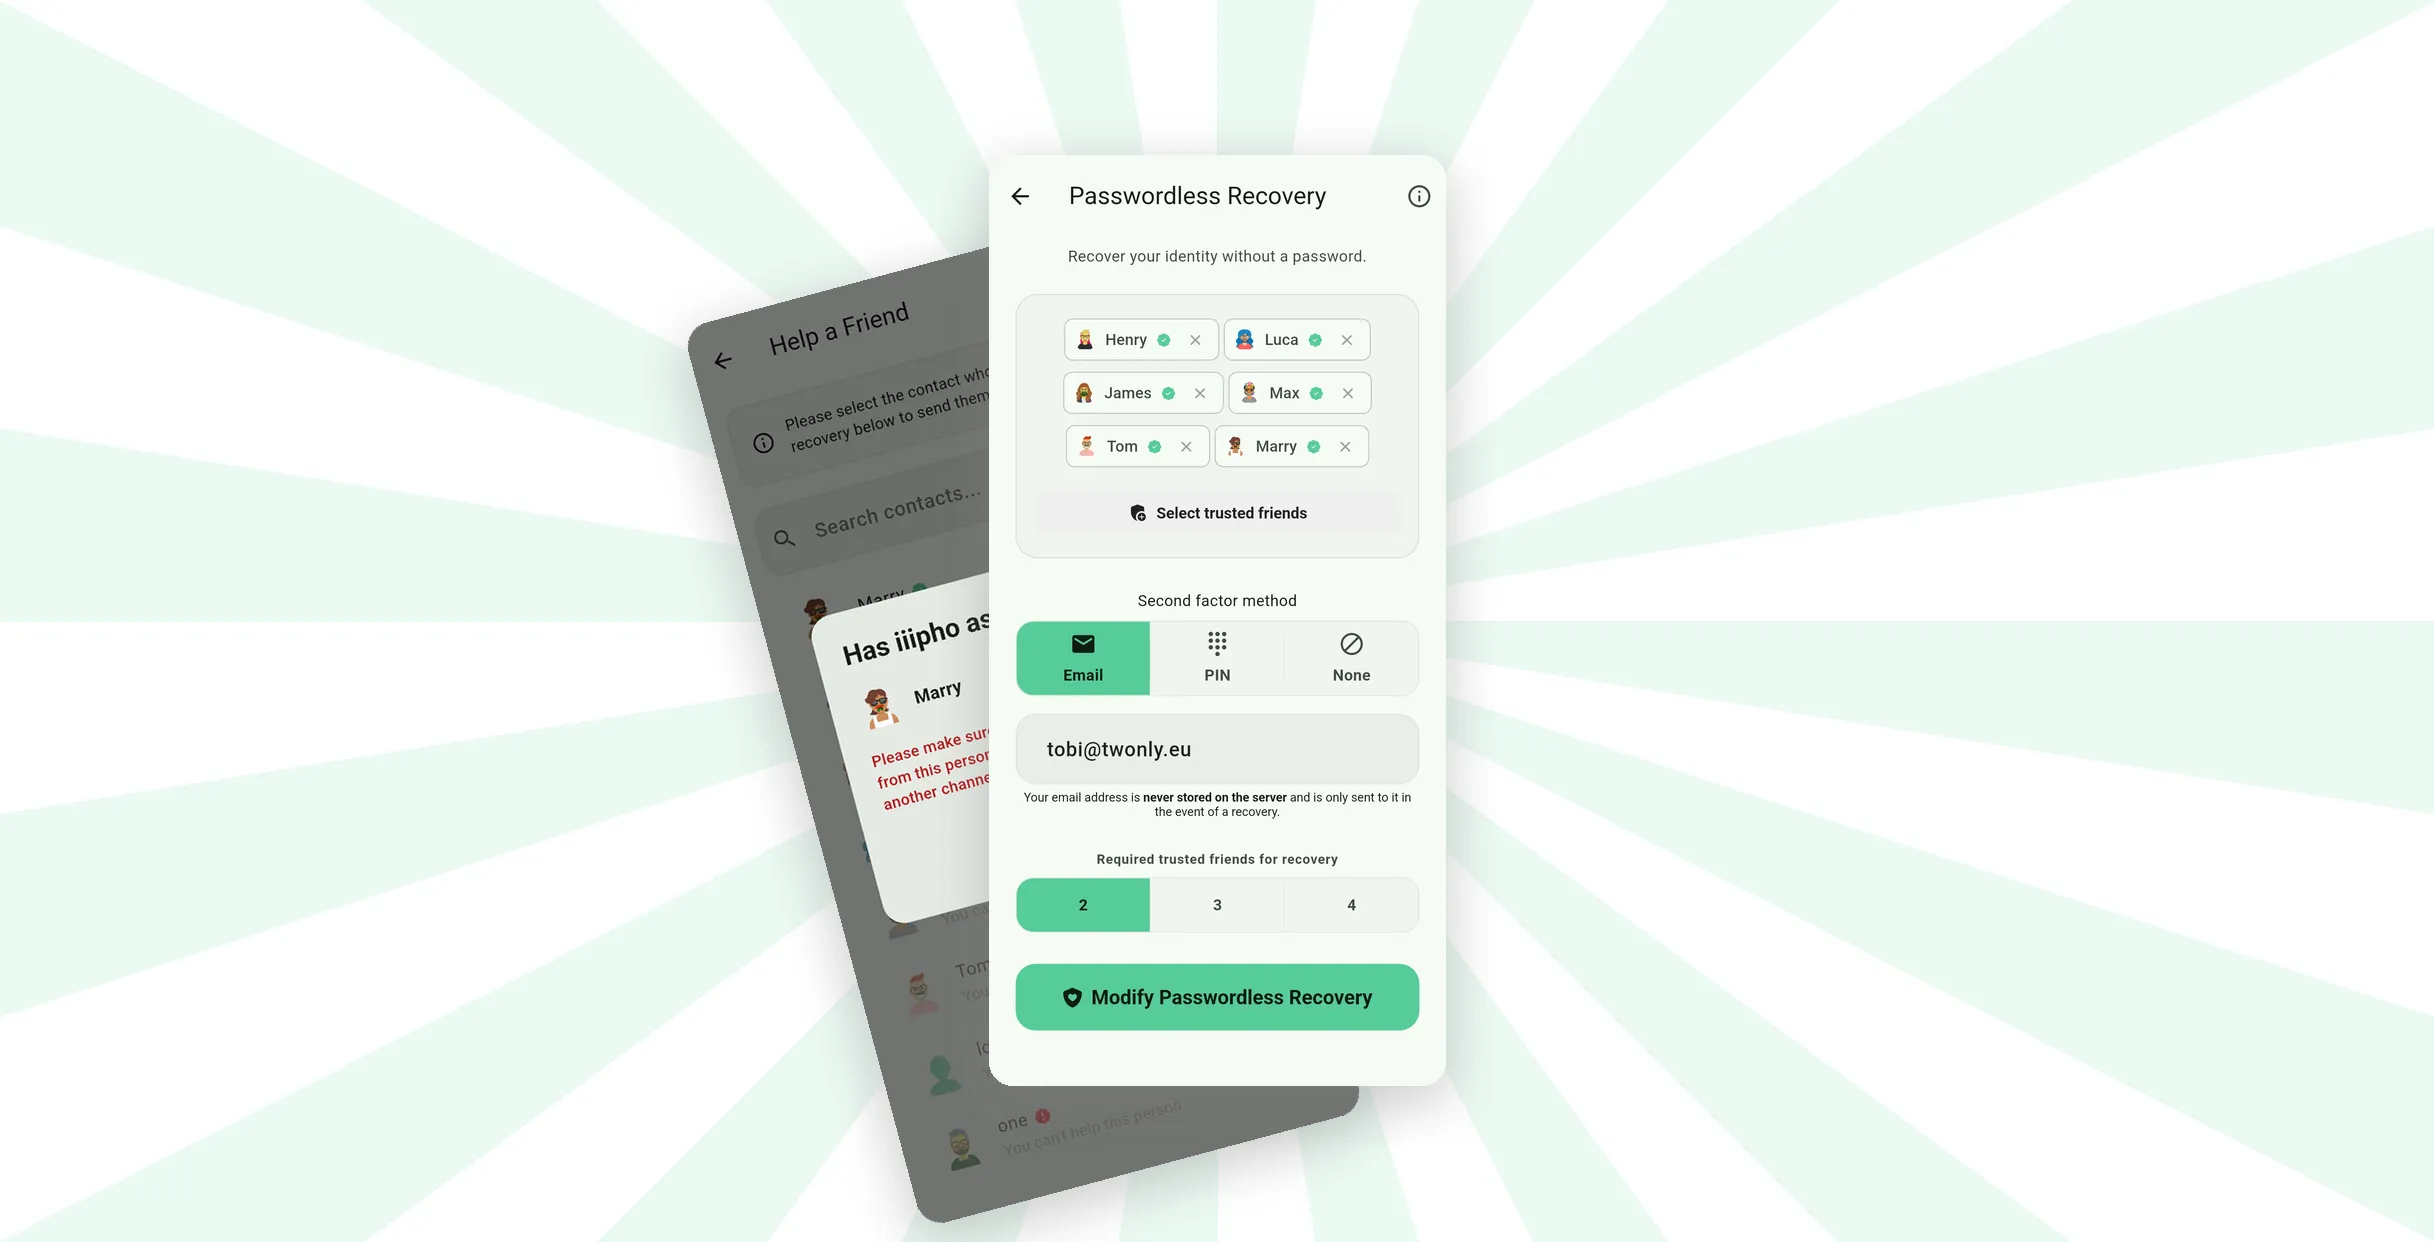
The upcoming update brings two major features preventing you from losing access to your memories 🎉

  1. Passwordless Backups: Never again lose access to your twonly account if you have forgotten your password. Just select friends you trust and choose a second factor. Read our blog post for more details [1].

  2. Encrypted Cloud Backups: More Details and additional features follow soon!

https://twonly.eu/en/blog/2026-passwordless-backup.html

#e2ee #privacy #snapchat #did

2
0
2
0
Replying to
It imagines a world where #E2EE is made illegal or at least a cause for suspicion. It turns the tables by saying, this thing that I am saying... not only am I not ashamed of saying it, but I am using my identity to validate that it is me saying it. A MAC-based identity/signing system is at the lower end of possibilities. If knowing that the signature matches a known identity gives assurances that this known identity is the source of the message, then why stop with a MAC? If I were to sign each packet with a string of the form "this packet is certified to come from the pen of and comes as part of a longer AONT message which is signed using the publicly-available PGP signature whose checksum is " #Muddle is also a political statement. It's a not-encryption scheme that's just too stupid to beat.
0
0
0
0
RE: https://mastodon.social/@HolosSocial/116937094959319831 While most of you know my main account for #Fedilab, months ago I wanted to work on something new. Being able to publish this code in production is an important step for me. Yes, it is possible to run an #ActivityPub server on your phone, with #E2EE DMs and a portable identity. And you are no longer tied to a single model like text, media or video. No need for separate apps: one account does it all, and you switch in one tap. Only your device owns the data, and the rules are on your side.
23
0
18
0