#cryptography
135 posts · Last used 4d
How to Hack Time, With C2PA https://lobste.rs/s/u8uvlr #cryptography #security
https://www.da.vidbuchanan.co.uk/blog/hacking-time.html
SequenceHash: multihashing for the rest of us https://lobste.rs/s/llnale #cryptography
https://blog.trailofbits.com/2026/10/02/sequencehash-multihashing-for-the-rest-of-us/
Another Look at Provable Security https://lobste.rs/s/vzqewa #cryptography
https://www.math.uwaterloo.ca/~ajmeneze/anotherlook/
Boosted by @welcome@friends.deko.cloud
Hello Mastodon! I'm into Computer #Security, #Programming, #ReverseEngineering, #Hacking, #Linux, #AmateurRadio, #Privacy, #OpenSource, #Cryptography and generally anything creative and interesting involving tech. Especially things that help people communicate and use computers more privately and securely. Lately I've been tinkering with mesh networks like #Meshtastic, #MeshCore and #Reticulum. Longtime #QubesOS and #GrapheneOS user.
I also enjoy touching grass like #Camping, #Backpacking and generally being in nature. Would recommend.
This is a personal/professional account so keep an eye out for various writeups and research, for work and for fun. Previous jobs ranged from #SoftwareEngineering to Computer Security #Research and #InfoSec, and I'm looking for more of the same.
#Introduction
wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.
#wolfSSL #wolfSSLVulnerabilities #TLS #AuthenticationBypass #EmbeddedSecurity #Cryptography #IoTSecurity #PatchNow
https://securityonline.info/wolfssl-5-9-4-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
Excellent research (and very useful FAQ) out on a new RSA attack: forging 1024-bit signatures in “nearly SNFS time” (not polynomial, but somewhat faster than previous number field sieve approaches by a few orders of magnitude). Real-world risk is low because most RSA implementations in practice do not meet one of the attack requirements; however … more ammunition on the need to transition away from RSA (and protocols like TLS moved to elliptic curve quite a while ago, or are moving to ML-KEM and #PQC). https://github.com/ucsd-hacc/NSNFSSSFSFN #cryptography
tip o’ the hat to Bruce Schneier’s blog for raising it to my attention
Replying to
@darkuncle@infosec.exchange
An interesting thing is this: While TLS does not expose a weak mode of using RSA, the majority of X.509 certs on the web are RSA (approx. 2/3). See below for a link to the source for this.
But certificates are also used for other things, e.g. code signing, token issuing, etc. And who knows whether any of those use cases will *always* be avoiding the classic RSA padding for signatures.
So a move to the more efficient and compact ECDSA or (even (better)) to EdDSA would be appreciated. This move will also more likely level the path towards allowing for better cryptographic agility to adopt hybrid #PQC ciphers in the future.
BTW, kudos to Let's Encrypt! There the entire chain is using ECDSA signed certs down to the web site using it.
https://ecdsa.com/research
#cryptography #RSA #ECC
MPC inside a Trusted Execution Environment (TEE) adds defense in depth, but the two make different bets on trust. MPC spreads trust across independent parties, while TEEs concentrate it in the hardware manufacturer and its attestation infrastructure. Our new post covers what TEE attestation can and can't fix in MPC deployments, the pitfalls we see most often in audits, and how to combine the two without undermining either.
https://blog.trailofbits.com/2026/09/25/dont-let-tees-break-your-mpc/
#infosec #cryptography #TEE
Forging 1024-bit RSA signatures in nearly SNFS time https://lobste.rs/s/ah5jnf #pdf #cryptography #security
https://eprint.iacr.org/2026/2131.pdf
Forging 1024-bit RSA signatures in nearly SNFS time
https://eprint.iacr.org/2026/2131.pdf
#Cryptography #Security #Research
Combining Machine Learning and Homomorphic Encryption in the Apple Ecosystem https://lobste.rs/s/7ekwll #ai #cryptography
https://machinelearning.apple.com/research/homomorphic-encryption
I want my mesh networks to be signed, not encrypted https://lobste.rs/s/r3ydgj #cryptography #networking
https://andanti.no/blog/SignedMesh.html
AMD's random number generator (RDSEED, RDRAND) cannot generate a 0.
https://board.flatassembler.net/topic.php?t=24261
#crypto #cryptography
Coinbase Prepares Post-Quantum Custody Defenses as Bitcoin Quantum Upgrade Remains Uncertain
Coinbase is building quantum-resistant custody infrastructure that can adapt to any post-quantum signature scheme Bitcoin may adopt, says Head of Cryptography Yehuda Lindell.
https://newisty.com/blog/coinbase-prepares-post-quantum-custody-defenses-as-bitcoin-quantum-upgrade-remains-uncertain?utm_source=social&utm_campaign=crypto_news
#bitcoin #cryptography #quantumcomputing
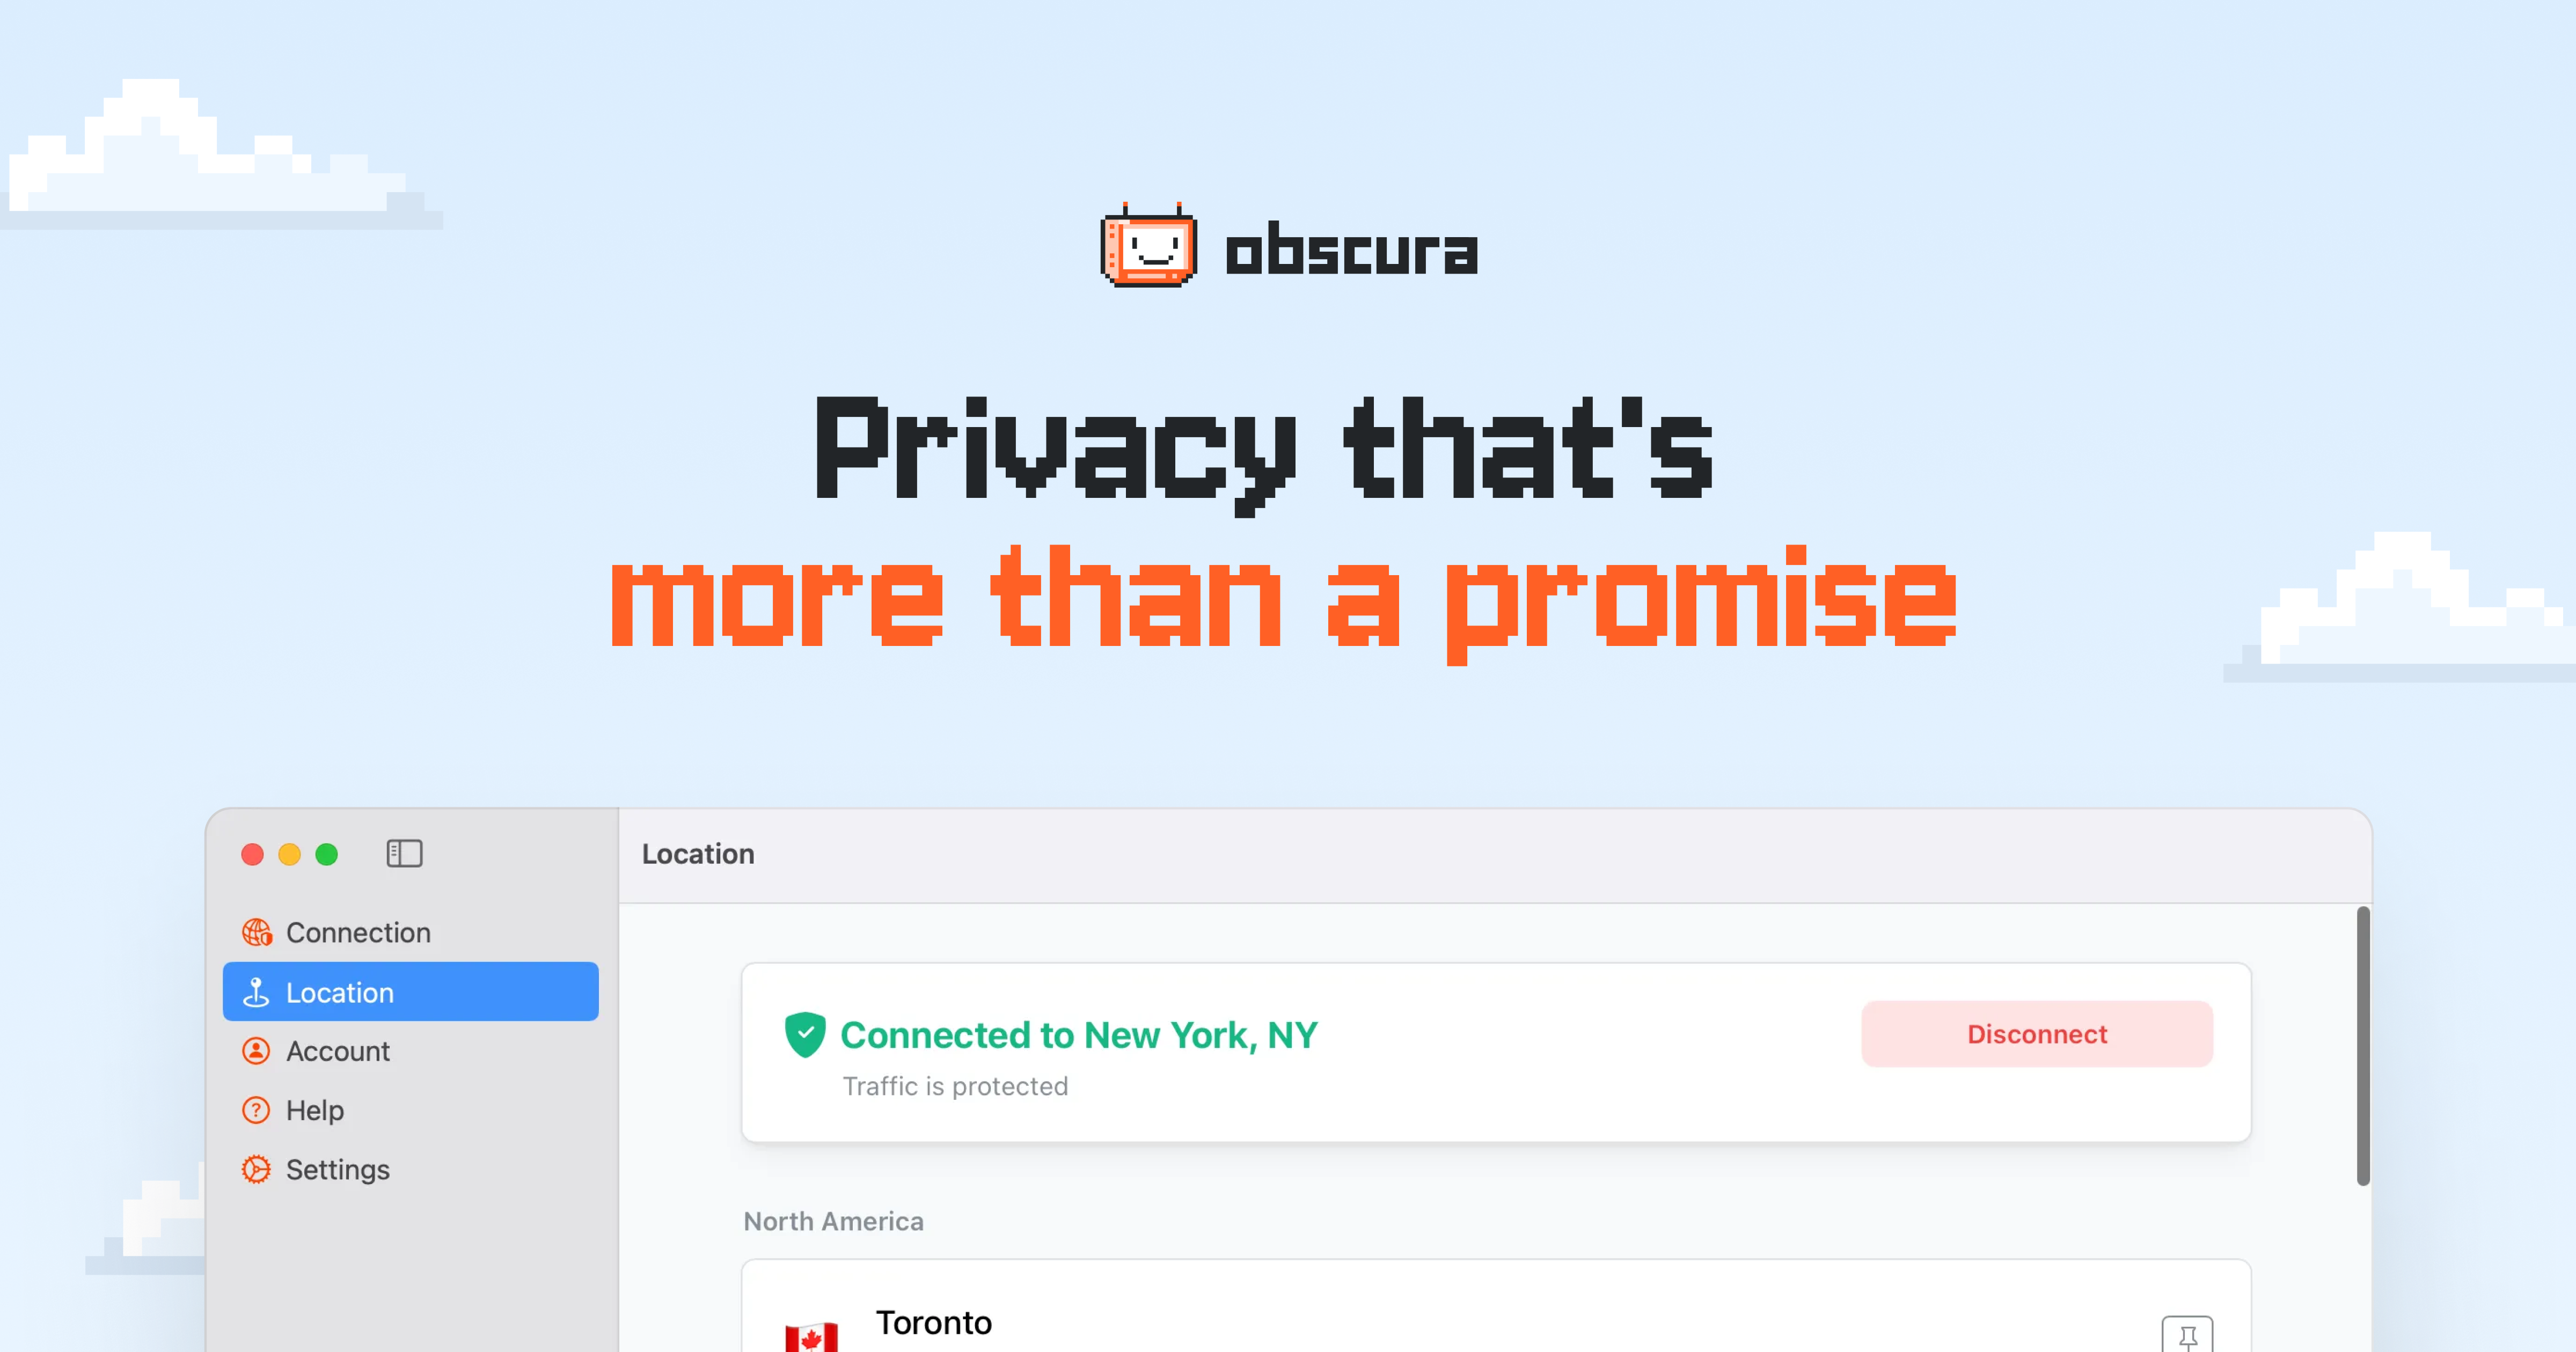
Obscura VPN, built by a team led by Bitcoin Core developer Carl Dong, uses a two-party relay architecture that splits a user's identity from their traffic across two independent operators: Obscura's own servers and an exit hop run by Mullvad. Connections run WireGuard tunneled over QUIC to Obscura's server, which relays the still-encrypted WireGuard packets to Mullvad without being able to decrypt them, while Mullvad never sees the user's real IP address. The design avoids account emails, offers WireGuard-compatible configs for non-native platforms, and accepts Bitcoin Lightning and Monero payments; the source code is published on GitHub.
https://obscura.com/#faq-technical
#InfoSec #Privacy #Cryptography #DigitalRights
35232 42728 29872 19649 63651 29225
#cryptography #rabbitwaves
GPT-6 Astra Solves a WWI German Radio Cipher https://lobste.rs/s/ywnsld #cryptography
https://www.prinzai.com/p/gpt-6-astra-solves-a-wwi-german-radio