Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Clemens

@neverpanic@chaos.social
mastodon 4.6.9
  • Open on chaos.social

MacPorts Developer, PPL/A, Works at Red Hat on Cryptography

searchable

444 Followers
145 Following
50 Posts
Joined November 04, 2022
Web:
https://neverpanic.de/
GitHub:
https://github.com/neverpanic
Open post
Clemens @neverpanic@chaos.social
· 5mo ago

So apparently #DEnic has messed up #DNSSEC records for .de, and essentially all resolutions of .de domains now randomly fail. For example, Google DNS just gave me "RRSIG with malformed signature found for 76b2e6birnkv6aekmcbtnl5i4qkbji6a.de/nsec3 (keytag=33834)" in a failure response. With caching, this is probably going to take a while.

I'm still not convinced DNSSEC is a net positive technology. The impact crater when somebody messes it up is just way too large.

chaos.social
23
3
14
0
Open post
Clemens @neverpanic@chaos.social
· 2mo ago
Replying to
@vowe@social.heise.de so weit daneben war das Meme gar nicht. Zumindest ist klar wo die Inspiration her ist und auch wo die Reise hin geht.
3
0
2
0
Open post
Clemens @neverpanic@chaos.social
· 3mo ago
Replying to
@katzenmann@c3d2.social These aren't independent sources, though, since they're written by @djb@mastodon.cr.yp.to, who has a strong opinion on this. For other views, see for example https://keymaterial.net/2025/11/27/ml-kem-mythbusting/ or https://words.filippo.io/crqc-timeline/ both from reputable crypto people.
ML-KEM Mythbusting
Key Material

ML-KEM Mythbusting

What is this? There have been some recent concerns about ML-KEM, NIST’s standard for encryption with Post-Quantum Cryptography, related standards of the IETF, and lots of conspiracy theories …

3
6
1
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@jwildeboer Meine persönliche Richtlinie ist ja immer "die gesichert rechtsextremistische AfD" zu benutzen. Führt zu herrlichen Beißreflexen.
8
2
1
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@filippo Couldn't agree more with "the bet is 'are you 100% sure a CRQC will NOT exist in 2030?'" — and I'd also add the operational perspective: "are you 100% sure you've found and replaced every Debian oldoldstable and RHEL 8 box that doesn't support PQC by 2030?"
8
2
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@mxk@hachyderm.io Where's the option for "yes, but I don't want to"?
5
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 3mo ago
Replying to
@sophieschmieg@infosec.exchange This would all be so funny if it weren't a colossal waste of time that could be spent getting stuff out of the door. I'm really hoping we're not going to see a repeat of this shit in, e.g., the SSH WG.
2
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago

RE: @molly0xfff@hachyderm.io

CAPS_WORD is best Caps Lock. I have this configured on all my keyboards, and it's why I'm really looking closely at which manufacturers actually provide source code for #QMK and which ones are violating the license.

hachyderm.io
6
0
3
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@sophieschmieg at this rate, we should come out with a blog post saying RHEL's target date for PQ auth is 2026 just so you have something to boost.
4
2
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@icing@chaos.social I think it's pretty clear that three letter agencies are already using LLM analysis to find vulnerabilities, so for organizations where those are part of the threat model, immediate full disclosure would allow better risk management. I'm not convinced many organizations could deal with the open firehose of reports, though. Certainly not those that treat CVE management as a checkbox exercise.
2
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@piratenpanda Kann mir vorstellen, das Carl Zeiss in Aalen Bedarf an diesem Profil hätte, und weil das jetzt keine große Stadt ist sind die Chancen da was zu finden auch nicht so schlecht. (edit: typos everywhere)
2
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 4mo ago
Replying to
@q@glauca.space @filippo@abyssdomain.expert the fact that he was only temporarily moderated shows the IETF's restraint in this matter, and yet that doesn't stop him from throwing around legal threats in response to said moderating action.
1
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@fluepke damals als ich noch für Automobiler gearbeitet habe war der Entwicklungsaufwand für Carsharing-Features einfach nicht wirtschaftlich sinnvoll. Glaube nicht, das sich das seitdem viel geändert hat.
2
5
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@swelljoe@mas.to @bagder@mastodon.social Agree on that. Blockchain is a solution looking for a problem, if not for cryptocurrencies, which have their own well-documented problems like enabling the ransomware industry.
1
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@swelljoe@mas.to I'm no fan of LF, but only one of the graphs cited here is clearly labeled to be about budget. The other one might also be by share of supported projects, number of contributors, or some other metric. Therefore it doesn't seem like this is a valid conclusion from the data in this PDF. And I honestly wouldn't have expected any better from the author of this website. Do look him up, and reconsider whether this is really somebody you want to boost. Cc @bagder@mastodon.social, who boosted.
1
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to

@ErikUden Yep, nothing you can do from your end.

If you're already running a local resolver, you can configure that to ignore DNSSEC for .de, e.g., for unbound:

server:
  domain-insecure: "de"

but that isn't something you can tell non-tech people.

1
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@vincent That's correct, but evidently getting DNSSEC key rollovers right is hard, i.e., deploying it increases the risk that you'll mess something up. They need to do all the existing DNS serving stuff anyway, doing DNSSEC correctly *in addition* is a net increase in risk of getting it wrong.
1
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@jwildeboer@social.wildeboer.net Considering my not DNSSEC-signed .de domain is also affected, this is at least partially incorrect. The problem seems to be with DNSSEC records at the .de level, where I have no control over whether they are signed or not.
1
3
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@letoams@defcon.social No, but there are mitigations using eBPF that don't require rebooting, e.g. https://github.com/atgreen/block-copyfail
github.com
1
2
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@minego Try https://redhat.wd5.myworkdayjobs.com/en-US/jobs/job/Raleigh/Senior-Product-Security-Engineer_R-053025-1 and https://redhat.wd5.myworkdayjobs.com/en-US/jobs/job/Raleigh/Principal-Software-Engineer_R-053026-1 and I believe we'll be opening a position around smart cards soon-ish, too. I know they say hybrid not remote, just apply anyway — if we can't find anybody locally (which is probably likely for cryptography people), they'll consider remote.
redhat.wd5.myworkdayjobs.com
1
2
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@darkuncle@infosec.exchange @hko@floss.social I believe a significant part of the problem is animosity between some of the people involved, and reservations against some algorithms such as AES-GCM (even though they are optional in OpenPGP at the request of GnuPG, iirc)
1
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@matthieu @Larvitz Can you deploy the diseases?
1
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@Techaltar Do you have a theory on what's going on with the mail votes going 90%/8% for FIDESZ/TISZA on https://vtr.valasztas.hu/ogy2026/orszagos-listak?tab=partlistak&filter=orszagos-eredmenyek That feels suspect given the rest of the results so far.
Országgyűlési képviselők választása 2026 – Nemzeti Választási Iroda
vtr.valasztas.hu

Országgyűlési képviselők választása 2026 – Nemzeti Választási Iroda

Választási szervek - Nemzeti Választási Iroda

1
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@filippo@abyssdomain.expert Unfortunately CNSA 2.0 also asks for SHA-512 over SHA-256, and that's in fact a major hassle and is wasting time, because we're looking at making the container ecosystem add support for that. Your point of the birthday problem and their target of 256bit security at least explains that (in a way that NSA's own documentation doesn't), but it's still a pity we're wasting time on this.
0
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to I respectfully decline to discuss with you. Calling that a tantrum is just the kind of style people have come to expect from you.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@icing@chaos.social agree with everything until "publish CVE information as soon as a patch is available for a vulnerable version" - if everybody can trivially find the same vulnerability, there's value in knowing whether updating to a newer version exposes you, and value in enabling others to develop a fix.
0
4
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@gregkh @mxk that sounds like a problem that https://mergiraf.org/ must have already solved, maybe you can steal their code to do something similar? I don't think they have an API for that, though.
mergiraf.org

Introduction - Mergiraf

A syntax-aware git merge driver for a growing collection of programming languages and file formats.

0
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@jwildeboer@social.wildeboer.net Google DNS still has a broken cache, for example:
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@icing@chaos.social Just to make this explicit: I don't speak for my employer. But yes, isn't that the logical consequence of your point? Avoids duplicate reports, and if there really is a very low bar to rediscover the vulnerabilities, this at least makes everybody aware, not just the "bad guys". My employer's customers won't like this, but it might just be the new reality we live in. OTOH, I would understand if you don't do that to avoid being bombarded with complaints why no fix is yet available.
0
2
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@young_ullrich @fluepke Ja, es gibt natürlich die Klasse an Features die der Vorstand oder der Designer halt will (oder "der Daimler hat das schon"), und dann wird das gemacht fast egal was es kostet (zB Display-Schlüssel mit Linux und ferngesteuert damit einparken). Dazu gehört Carsharing nicht. Vielleicht früher mal als Mercedes Carsharing noch selbst gemacht hat.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@stiiin@infosec.space well, if you consider buying illicit drugs and extortion through ransomware an application, there is a very good use case for it. @julsboo@mamot.fr @swelljoe@mas.to
0
2
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@fj Maybe not the best task for an intern, but good luck finding somebody.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@young_ullrich @fluepke Und selbst bei den Entwicklungskosten ist das kein free-for-all, auch da wurde vorher mit erwarteter "take rate" und einem Zielpreis für optionale Extras durchgerechnet ob die Entwicklung wirtschaftlich ist. Die minimale take rate für Carsharing killt diese Diskussion in der Regel sehr schnell, die Extrafeatures müssten für die wenigen Käufer sehr/zu teuer sein. Ein Auto für alle 10 Euro teurer zu machen um Carsharing zu finanzieren wäre niemals akzeptiert worden.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@utf_7 @protonprivacy ELI5 enough or do you want more details on how the math works?
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@bagder@mastodon.social I'm hearing similar things from both #OpenSSL and #GnuTLS.
0
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@ohir @filippo FN-DSA may be a solution for this class of devices. (Or LMS and XMSS, although those two are such a big footgun nobody should be using them, *especially* not for signing — verification is OK.)
0
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@0xKaishakunin @clt_news well, SLH-DSA, that isn't exactly fast on modern hardware either. 4 seconds for ML-DSA isn't all that bad.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@jschauma No, the PQ crypto algorithms are all open, the only discussions related to the crypto wars area are legislative. It is looking like we're heading towards a version of the crypto wars just with AI/LLM technology, though.
0
4
0
0
Open post
Clemens @neverpanic@chaos.social
· 3mo ago
Replying to
@frumble@chaos.social @jwildeboer@social.wildeboer.net Turns out a company as large as Red Hat has a few people that occasionally deal with video!
0
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to I'm not playing pigeon chess with you. Go away.
0
1
0
0
Open post
Clemens @neverpanic@chaos.social
· 6mo ago
Replying to
@arianvp @filippo There is movement in that area already, standards are being updated, and a few vendors seem to have development hardware tokens already, but it'll be a while until this becomes widely available.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@mgorny the developer works for Anthropic.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 2mo ago
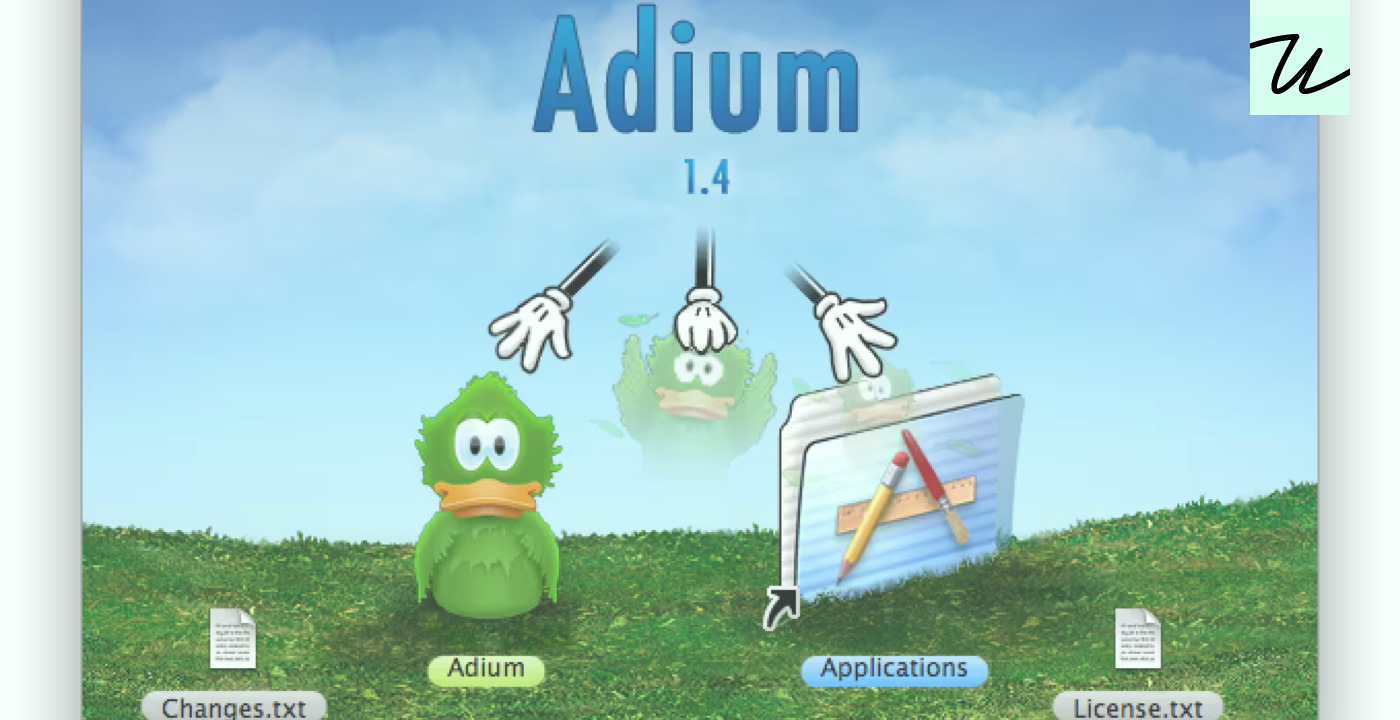
Gorgeous collection of macOS drag-to-applications-to-install Windows: https://unsung.aresluna.org/as-a-windows-user-its-a-very-surreal-way-to-install-a-program/
“As a Windows user, it’s a very surreal way to install a program.” – Unsung
Unsung

“As a Windows user, it’s a very surreal way to install a program.” – Unsung

A blog about software craft and quality

0
0
3
0
Open post
Clemens @neverpanic@chaos.social
· 2mo ago

My team is looking for a US-based person to work making #PQC #SmartCards work with open source software. Says Raleigh, but remote will be considered when nobody can be found locally, which is likely:

https://redhat.wd5.myworkdayjobs.com/Jobs/job/Raleigh/Senior-Software-Engineer-in-Crypto--Smart-Cards-_R-058584-1

#Crypto #cryptography #GetFediHired #FediHire

Note: don't complain to me if company decides to cancel the position in three days for reasons I don't understand.

chaos.social
0
0
1
0
Open post
Clemens @neverpanic@chaos.social
· 5mo ago
Replying to
@sungo@social.sungo.space @tek@freeradical.zone @c0debabe@masto.hackers.town Can't reproduce, most of the LLM bot traffic I see still comes from IPv4.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 4mo ago
Replying to
@mikemcquaid@mastodon.social @nor4@chaos.social only the latter is an option, the former makes no difference. This is due to the law on inventions this is based on - you could invent something at home in the shower, and the employer could still claim it. You can renegotiate though, I've done it before.
0
0
0
0
Open post
Clemens @neverpanic@chaos.social
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @katzenmann@c3d2.social The fact that you call what I linked "solo-PQ endorsement" when it says no such thing is a good example. Also, I have no interest in discussing this with you, you can keep that on the IETF mailing lists.
0
4
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 00:56:09 UTC