#dnssec
19 posts · Last used 8d
Skeptische Blicke beim #Stalwart-Vortrag am #LinuxDayAT – denn Mailserver-Installation und -Betrieb gelten als kompliziert. Bei Stalwart offenbar nicht. 😉
@opensourceuser@mastodon.social, 16 Jahre alt, hatte meinen Vortrag beim #CLT26 gesehen und die Installation direkt ausprobiert. Ergebnis: ein eigener, funktionierender Mailserver! 🎉
Anschließend haben wir anhand von https://www.hardenize.com noch den letzten Feinschliff besprochen: #DNSSEC, #MTA-STS, #TLS-RPT und #DANE.
Gerade nachgeschaut: Alles umgesetzt! 🎉 Besser geht's nicht.
Solche Erfolgserlebnisse geben Energie für die nächsten Vorträge. ❤️
The Internet Last Week
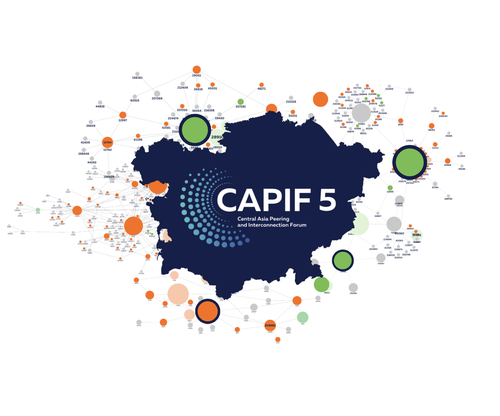
- Central Asia regional connectivity https://labs.ripe.net/author/anastasiya-pak/capif-5-regional-interconnectivity-in-central-asia/
- DNSSEC-anchored stateless encrypted auth DNS https://arxiv.org/abs/2609.14210
- Router compromise walk-through https://blog.j2sw.com/netops/mikrotik-router-compromise-forensic-walkthrough/
- Russia changed domain name registration rules https://riposte.levelflow.org/2026/09/rururu/
- Weaponizing digital choke points https://www.foreignaffairs.com/china/new-chinese-way-cyberwar-ai
1.1.1.1 prüft DNS jetzt mit Post-Quanten-Kryptografie
Cloudflare hat ML-DSA-44-Validierung für seinen DNS-Resolver 1.1.1.1 aktiviert. Das soll DNS-Antworten vor Quanten-Angriffen schützen.
https://www.heise.de/news/1-1-1-1-prueft-DNS-jetzt-mit-Post-Quanten-Kryptografie-11453315.html?wt_mc=sm.red.ho.mastodon.mastodon.md_beitraege.md_beitraege&utm_source=mastodon
#DNS #DNSSEC #IT #NIST #Quantencomputer #RSA #Security #news
Hosting your own mailserver?
It easy sometimes sometimes you sitting there trying to figure why the hell will Microsoft only connect and then quit. And not sending without any change to the mail-server. Updating the server looking through the config. Looking at the certificate. And nothing.
And starting to think that Microsoft is a shit mail company. Because google, yahoo and every other service i tried to send to my own server worked.
Everyone else will send to my server. And I have one that send email to me that use Microsoft.
After a few hours troubleshooting. I finely found the problem.
Drum role .....
IT was the DNS!! 😂
#selfhosting #DNS #DNSSEc #DANE #alwaysdns
A sad lesson from a few years of operating local #DNS resolvers in my infrastructure - #DNSSEC validation requires enormous resources to work reliably due to vast extra records it needs to pull from DNS for each validation and required computing power.
Forget about DNSSEC validation in systemd-resolved, dnsmasq or unbound on home routers, it will just cause periodic and apparently unexplained delays and choke overall DNS resolution.
On firewalls like #OPNsense it also would work only server-class devices, any of the desktop-class fanless hardware won’t work reliably for DNSSEC validation even if they can perfectly handle production-class proxy and firewall traffic.
Probably what only makes sense is a dedicated Unbound validation server, a separate container or jail but running within a proper hardware server with tons of memory and CPU. But then I found out that it’s much easier to use non-DNSSEC caching resolvers on perimeter devices that forward queries to Quad9 ECS resolvers[^1] which already do DNSSEC validation.
The only missing bit is that I think my local resolvers don’t forward the DO bit downstream, but that I need to still check.
[^1]: https://quad9.net/service/service-addresses-and-features/#ecssec
According to Cloudflare, .al (Shqipëri - Albania 🇦🇱) domains are having issues with DNSSec
https://www.cloudflarestatus.com/incidents/64d6d3l2h1lt
Selon Cloudflare, .al (Shqipëri - Albanie 🇦🇱) éprouve des difficultés avec DNSSec.
// En anglais //
A botched DNSSEC ZSK rollover by DENIC on May 6, 2026, caused a widespread SERVFAIL cascade, making millions of .de domains unreachable. This incident highlights DNSSEC's "fail-closed" design, forcing Cloudflare to temporarily disable validation for .de to restore access, raising serious questions about operational resilience.
#cybersecurity #dnssec #dedomains
🤖 This post was AI-generated.
Dass gestern Abend bei der DENIC ausgerechnet DNSSEC (wohl für die TLD .de und damit alle DNSSEC-signierten Domains unter dieser TLD) ausgefallen ist, ist schon wirklich heftig.
Das hat ja nun weitreichende Folgen gehabt. Bei mir waren alle meine Domains (davon drei mit einigem Traffic) nicht mehr erreichbar, ich konnte keine Mails mehr bei Mailbox.org abrufen (hätte ich noch meinen eigenen Mail-Server gehabt, wäre das Ergebnis dasselbe gewesen).
#DENIC #DNSSEC
#KRITIS Sektor #IT und #TK
Ah, DENIC eG hat #DNSSEC verbaselt und viele .de Domains tun deswegen nicht mehr...
It's always DNS 😂
Das gibt dann wohl ne Meldung an das @bsi@social.bund.de wegen NIS2 und KritisV 🧐
https://dnsviz.net/d/chaoswelle.de/dnssec/
We are monitoring a #DNSSEC-related issue with #DE ccTLD. The issue is not specific to Quad9. We will update once more information becomes available.
You can subscribe for updates at: https://uptime.quad9.net/
Our thoughts are with DENIC staff responding to this incident. #HugOps
#DNS #infosec
Gibt wohl gerade Probleme bei der #DENIC, dass #de-Domains nicht mehr aufgelöst werden. Ursache scheint #DNSSEC zu sein.
Quelle: https://www.reddit.com/r/de_EDV/comments/1t4qlrg/psa_die_dezone_l%C3%B6st_gerade_gro%C3%9Ffl%C3%A4chig_nicht_mehr/
So lange es die TTL noch zulässt: war schön mit Euch, wir sehen uns wieder, wenn die Nachtschicht rum ist und die Wesen vom Denic alles wieder aufgeräumt haben.
Es ist nie #dnssec :-)
Looks like DE ccTLD is unresolvable due to DNSSEC issue:
https://dnsviz.net/d/nic.de/dnssec/
😬
#InfoSec #DNSSEC #DNS #Germany
Seit gut einer Stunde sind viele Webseiten mit .de Domains down:
Der Grund liegt diesmal bei der DENIC herself. Die DENIC ist die oberste Domain Verwaltungsstelle in Deutschland, bzw. für .de Domains.
"Investigating
It seems like the fault is related to DNSSEC issues with "de" domains on a registry level.
Further information from DeNIC can be found at https://status.denic.de/
Due to a fault, there is currently limited availability to the recursive DNS resolution for "de" domains."
Heisst soviel wie, die Namensauflösung von .de Domains hat aktuell ein Problem. Sprich, wenn ein Browser nach der Domain www.bge.de fragt, dann kann der DNS nicht zu einer IP auflösen, die nötig ist, um den Request an den richtigen Server zu schicken.
Meine privaten seiten mit .de domain sind ebenfalls alle down.....
#denic #dns #dnssec
You've seen all posts