AfD und CDU stimmen Bürgerpatrouillen zu. Yay, ICE in Deutschland... 😓
Remote
13reak 
@13reak@infosec.exchange
 mastodon 4.8.0-alpha.3+glitch
Incident Responder interested in #DFIR #malware #reverseengineering #pentesting and #purpleteam . #fedora and #opensource fan
#GCFA #GCFR #CARTP
#ISO17024 IT forensics/IT security expert witness
Proud of #EU
187 Followers
318 Following
41 Posts
Joined January 31, 2023

Replying to
@jernej__s@infosec.exchange @meluzzy@woof.tech
Vivaldi is far worse than Brave. It's hyped as data protection but actually the opposite. It's partly closed source.
It sends part of your IP, screen resolution and CPU to Vivaldi servers. It's also assigning its users an identification number to track them better. Lastly, it's using Google services in the background, that's not data protection...
Brave is definitely not ideal but open source and the Google stuff can be turned off (as far as I know).
Replying to
@meluzzy@woof.tech
Any recommendations for a chromium based browser?
(Brave was my go-to when a website didn't support Firefox - try any video chat, hardly works...)
Replying to
@FuturisticRobert@infosec.exchange @chrissanders88@infosec.exchange
Also get the scheduled task and check it's content. Is there scripting code in the scheduled task?
Since there is more awareness of neurodiversity, my employer was thinking about a diversity statement on website/careers page that (among other things) addresses this and maybe change the interview process a bit.
It might be just a drop in the ocean and only help a little, but I think it's a step into the right direction and I'd like to support this and encourage it.
So, #askfedi : what would actually help you (neurodivergent folks) during job interviews or at work in general? What could an employer realistically do? And what would encourage you to apply?
E.g. would a buddy help? More time/pauses? Online/(partly) written interviews? Dim lit, quiet rooms?
Replying to
@chrissanders88@infosec.exchange
Since most of it is PowerShell or HTA, I'd first check Powershell logs and then check the file system for new HTA files: NTFS, Journal, sysmon, evidence of execution.
If there's Defender for Cloud, it's worth a look.
And ofc check RunMRU (commands of run dialog) for common lolbins.
#DFIR #analysis #incidentresponse #cybersecurity #infosec
Good that I use Firefox/LibreWolf...
Searching for an open source alternative to Jira. I tried Nextcloud Deck but it is a bit lacking.
Does anyone know a good open source kanban software that can do sub-tasks?
Replying to
@avuko@infosec.exchange
Problem with TOR is that the US authorities see it as fair game to attack anyone on TOR "cause it's just used by criminals".
Plus, it is not trivial to use. E.g. by default it covers TCP. UDP etc. packages are not automatically routed through it. So one small unintentional mistake (or an intentionally injected JavaScript?) de-anonymizes you.
It's possible to use it safely, yes, but it's not that easy.
PS: I am speaking from experience. I already got the real IP of an attacker using TOR to attack a customer. Also, once one of our pentesters was identified early due to a small TOR mistake.
@pheonix
I'm not surprised...
A simple cat on the command line can also compromise your system. If you're unsure, you should therefore use cat -v when I'm not mistaken.
Replying to
@QasimRashid
Yeah, we should give him a peace nobel for all the good deeds he did in Iran, Gaza, Lebanon, Venezuela, and the world. 🤦♂️
Replying to
@doctormo@floss.social
Apologies for reinterpreting the question a bit but I genuinely thought this might help:
I switched from LibreOffice to Grist. It has a python/plugin interface, so you can do anything you can imagine. Also, you find plugins on GitHub. Maybe it's worth a shot for you too.
Replying to
@r
Why should a website program microcontrollers or access the bootloader of my phone?
Rather sounds like a bad idea from security perspective...
Boosted by @ferrix@mastodon.online
For everyone who needs encrypted communication in crisis times: Briar has an offline mode and works via Bluetooth and WiFi.
It also works if someone turns off the Internet or cellphone connection. 😉
(Of course it only works over large areas if lots of people have it installed)
Spread the word!
#crisiscommunication #messaging #communication
Men cannot leave Germany any more without permission from the military? 🤦♂️ When do we fire Pistorius and SPD?
Replying to
@kajer
We already outsourced our useless notes to management 😉 they are far better at that
Or like engineers building bridges... How often did we hear about "one pillar" of a bridge collapsing vs "one directory" of a firewall being reachable.
Replying to
Can someone explain to me why AI companies are not being investigated for hacking other companies?
In the country I am living in, authorities HAVE TO investigate when they get to know about a crime - even without a criminal complaint (because generally people who were e.g. murdered cannot complain any more...).
Is the US justice system already so broken that this doesn't work any more?
Replying to
@superruserr@infosec.exchange
Switch job if you're in a dead end (it kills careers to stay) Certifications can open doors to better jobs that give better work experience it's worth even paying for certain certifications yourself if the company doesn't pay (especially for the first good course/certificate - SANS comes to mind) work experience can just be earned by working, preferably in a good job (bad jobs are just a waste of time and you don't learn much)
Replying to
@tobykurien@mastodon.social
What's the main difference to Matrix?
(I know lots of people at CCC use Matrix cause it's decentral. Delta chat is also decentral. So I was wondering which feature made you choose Delta chat)
Replying to
@girlgerms@infosec.exchange
You don't need to pay money for link shorteners here. All links count the same length within mastodon no matter how long they are 
Replying to
@Abelvicent@mastodon.social
Looks like an AI picture... Maybe not the best idea for an environmental message?
Shodan lifelong membership is currently only $5!
#shodanio #shodan #infosec #cybersecurity #vulnerability #vulnerabilityscanning #osint #dfir
Replying to
And the next nail in the coffin: Jens Spahn is using a surrogate mother while his own party forbids that in Germany.
"Some animals are more equal than others..."
#JensSpahnRuecktritt
Replying to on chaos.social
@netzpolitik_feed@chaos.social
Das ist krass und schade, vielen Dank für die Berichterstattung!
Boosted by @Ichinin@infosec.exchange
RE: https://eupolicy.social/@ilumium/117321075860995628
Amazing, well done!
Quoting
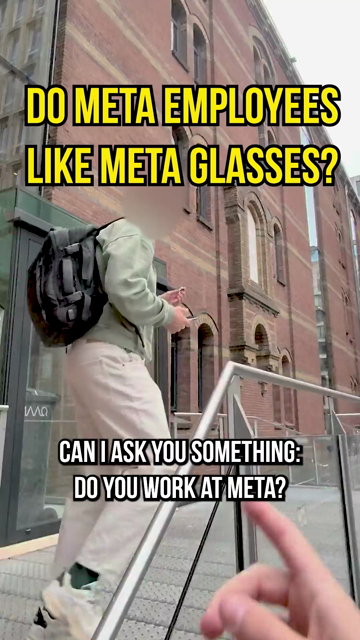
What an amazing campaign video about #Meta #SpyGlasses from @bitsoffreedom@chaos.social ❣️
Filmed in front of the Meta offices in #Amsterdam featuring real Meta employees. :)
I cannot remember the last time I was on time taking the train...
It's sad that DB nowadays has at minimum 1h delay. My last travels were: +1h, +1h, +3h, +1h 😮💨
#deutschebahn #DB_Bahn
Replying to
@ironicbadger@techhub.social
It's an online service that basically scans the entire global network and has a database on every device that is connected to it. Thus, you find hidden devices (also shadow IT or wrongfully connected printers etc) and vulnerabilities on shodan.
If you have an account, you can set up monitoring for your own IP range.
Replying to on mastodon.social
@adastra1930@mastodon.social
Why am I not surprised that pedophiles want to access baby cams?
Replying to
@newsguyusa@flipboard.social
There's an easier option to opt out: delete Instagram and use Pixelfed.
Replying to
@gildilinie@beige.party
How about Vivaldi website: 😆
https://vivaldi.com/we-respect-your-privacy/
=> IP tracking + location tracking and unique user ID
https://vivaldi.com/de/blog/decoding-network-activity-in-vivaldi/
=> Google requests
And the rest is from a German infosec expert who (among others) tested browsers:
https://www.kuketz-blog.de/vivaldi-datensendeverhalten-desktop-version-browser-check-teil5/
His (tech-only) recommendation is Brave and Firefox (https://www.kuketz-blog.de/browser-warum-firefox-und-brave-fuer-uns-derzeit-sinnvolle-empfehlungen-sind/) and I think he's using Librewolf as Firefox variant.
Replying to
@dee@grafana.social
Unfortunately, I strongly believe this is not the only project that looks like this. Companies only use open source and hardly support it. But when there's a vuln, the outcry to the maintainer is big.