Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Jerry on Mastodon

@Jerry@hear-me.social
mastodon 4.7.3
  • Open on hear-me.social

Admin/owner of this Mastodon server. I play around with Linux.

I also own:
Phanpy: https://phanpy.hear-me.social
Peertube: https://my-sunshine.video
Pixelfed: https://gr8.pics
Piefed: https://feddit.online
XMPP (Jabber): https://between-us.online
Matrix: https://secure-channel.net
Bluesky PDS: https://blue-ocean.social
Mobilizon: https://my-group.events

835 Followers
1475 Following
50 Posts
Joined December 19, 2022
verification:
https://hear-me.social/verifyme.html
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

Samsung pushed an update to their "smart" refrigerators

"... users ... on Samsung’s Korea Community forum report that their fridges completely stopped working, resulting in spoiled food. Other issues include the automatic door-opening function not working and the fridge’s internal lights not turning on."

#Samsung #IOT

https://www.androidauthority.com/samsung-accidentally-freezes-its-smart-fridges-with-a-software-update-3714472/

hear-me.social
5
0
4
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

Websites you should never visit because they are published by a conglomerate that creates the magazines using AI and nothing but AI.

I used to visit Space Daily every so often, but those days are now surely gone. I never heard of the others. It's quite a large list.

https://futurism.com/artificial-intelligence/every-brown-brothers-media-publication

#AI #AISlop

futurism.com
8
0
5
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

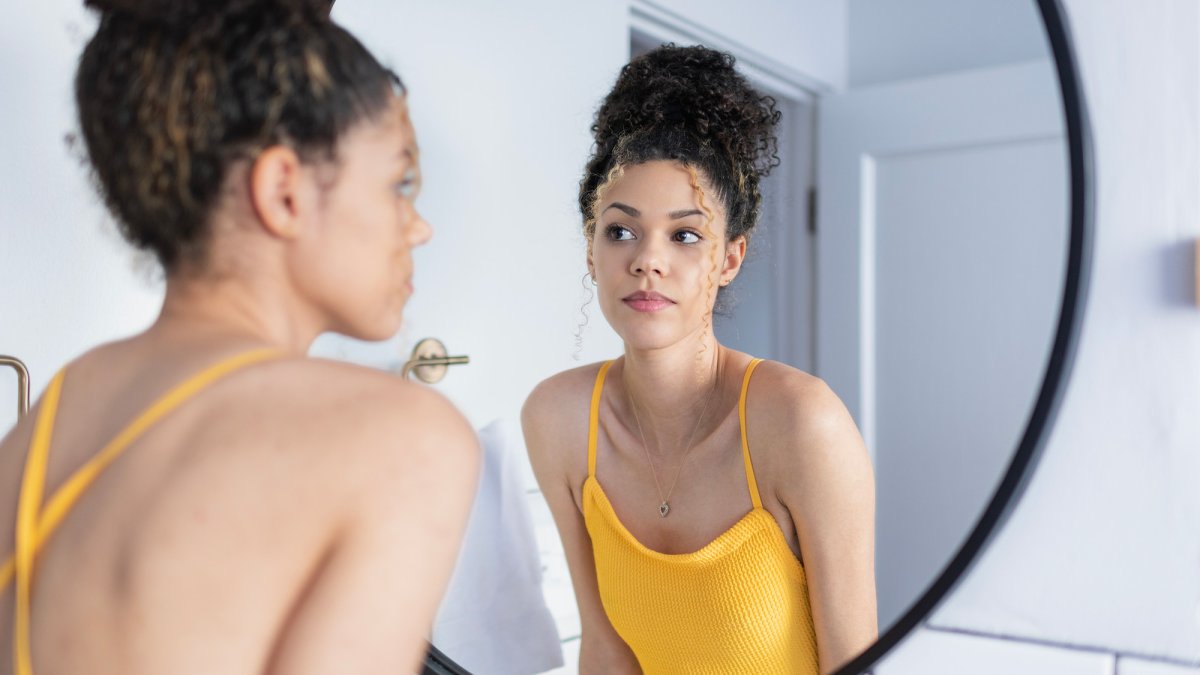
The reason your face looks wrong in photos. It's not you; it's mostly physics and some psychology.

https://www.popsci.com/science/why-look-different-in-mirror-photos/

#science #photography

The reason your face looks different in photos than a mirror
Popular Science

The reason your face looks different in photos than a mirror

It's not you, it's physics.

4
0
4
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

Did you know (few people do) that there is a Federated, decentralized, ethical alternative to #FacebookEvents and #Meetup for event-planning and group-management? Any alternative to Facebook is great, right?

It's called #Mobilizon. It's developed by the French non-profit organization Framasoft, which is the same group behind #Peertube.

Why Mobilizon stands out:

  1. It's Federated and Decentralized: It's made up of a network of independent websites that communicate with each other via ActivityPub, just like Mastodon, Pixelfed, PieFed, Peertube, etc.

  2. There are no Ads or trackers.

  3. Each instance is volunteer run.

It federates will ActivityPub applications, like Mastodon!

  1. You can follow Groups from mastodon via the group handle, like, @devon_football@my-group.events
  2. Events show in your Mastodon timeline
  3. If you reply to or comment in Mastodon, for example, about a Mobilizon event, your comment synchronizes back to the event page (and vice versa), bridging the conversation across both platforms.
  4. You don't need a separate account on a Mobilizon server just to keep tabs on a community's schedule.

If interested in exploring Mobilizon, in addition to running this Mastodon server, and other decentralized applications, I run the Mobilizon server, https://my-group.events

my-group.events

my-group.events - Mobilizon

6
3
5
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago

Important reminder, if you own a domain name and don't use it for sending email.

There is nothing to stop scammers from sending email claiming to be coming from your domain. And the older it gets, the more valuable it is for spoofing. It could eventually damage your domain's reputation and maybe get it blacklisted, unless you take the steps to notify email servers that any email received claiming to come from your domain should be trashed.

Just add these two TXT records to the DNS for your domain:
TXT v=spf1 -all
TXT v=DMARC1; p=reject;

The first says there is not a single SMTP server on earth authorized to send email on behalf of your domain. The second says that any email that says otherwise should be trashed.

If you do use your domain for sending email, be sure to add 3 records:
SPF record to indicate which SMTP server(s) are allowed to send your email.
DKIM records to add a digital signature to emails, allowing the receiving server to verify the sender and ensure message integrity.
DMARC record that tells the receiving email server how to handle email that fails either check.

You cannot stop scammers from sending email claiming to be from your domain, any more than you can prevent people from using your home address as a return address on a mailed letter. But, you can protect both your domain and intended scam victims by adding appropriate DNS records.

UPDATE: The spf and the dmarc records need to be appropriately named. The spf record should be named "@", and the dmarc record name should be "_dmarc".

Here's what I have for one domain.

One difference that I have is that I'm requesting that email providers email me a weekly aggregated report when they encounter a spoof. gmail and Microsoft send them, but most providers won't, but since most email goes to Gmail, it's enlightening when they come.

#cybersecurity #email #DomainSpoofing #EmailSecurity #phishing

hear-me.social
2245
60
1413
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

#Converse wants to apologize to you all for releasing a sneaker ad that looks like a #KKK lynching.

https://news.sky.com/story/converse-apologises-and-removes-ad-over-image-critics-said-evoked-racist-imagery-13590324

hear-me.social
2
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2mo ago

20% lower online prices if you use a local library computer? Another reason to hate retailers.

"Lora Kelley took a trip to the New York Public Library for us and compared prices against a personal iPhone. The results? A box of Apple Cinnamon Cheerios and a pack of toilet paper were nearly 20% cheaper on the library desktop."

https://www.mozillafoundation.org/en/nothing-personal/surveillance-dynamic-pricing-legal-groceries-tickets/

#OnlineShopping #Retail_sales #ConsumerProtection

mozillafoundation.org
7
4
4
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago
Boosted by @kagihq@mastodon.social
Paying for #Kagi search instead of using the "free" #Google search would now seem like a bargain for Elvira Schadlow, don't you think? It cost her $11,000 because she picked the first search result, the one Google was paid to prefer over the hotel's official site. Have you ever been fooled by a Google search result? https://www.nytimes.com/2026/04/09/travel/travel-scams-airlines-hotels.html?unlocked_article_code=1.aVA.hmRD.LzbZIcJU3rhu
nytimes.com
20
2
3
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2mo ago

On what planet would people not bother setting a simple switch to tell email servers to discard email claiming to be from their domains but aren't? You know to protect unsuspecting victims, protect the reputation of their domains, and prevent their domains from being shut down permanently for spam?

Apparently Earth.

People who leave the default option as it being OK to deliver spoofed email from their domain even if the email is screaming that it's a spoof, well, you know, deserve to lose their domain names, IMHO. What do you think?

https://ciphercue.com/blog/dmarc-enforcement-gap-rua-fragmentation-2026

#CyberSecurity #DMARC #SPF #DKIM #EmailSecurity

ciphercue.com
3
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 6mo ago
Replying to
@craig_patrick@mastodon.social @_elena@mastodon.social They aren't forthcoming about financing. So, as would be expected, they are not forthcoming about their monetization plans. These are 2 bad signs. Then add in the gaslighting about why major funding went unmentioned by both Bluesky and the VCs: "Everyone at Bluesky is just so gosh dang busy nobody had time to mention it." This is the gaslighting we see daily in the news. "I'll give you an obvious, nonsensical excuse, but still expect you to believe it because you all are gullible and emotion-driven."
17
0
7
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2mo ago
Replying to
@Hudson@kolektiva.social On what basis are you assuming their pricing is based on charitable parameters? This is never a corporate incentive for establishing pricing anywhere on this planet. Maybe it's just to encourage hooking new customers into opening an account so they get the higher prices later? I can assure you if it's a product that is essential to lower earners but optional to higher earners, they will start pricing the product higher once they learn the person is a lower earner.
1
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2mo ago
Replying to
@Sylocule@cyberplace.social Oh wow.
1
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago
Oh Wow! Since February 25th, mastodon.social, the massive mothership instance, has been having problems. I wasn't aware they were struggling so. #Mastodon
5
2
3
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago

I thought #Proton abandoned Mastodon. There was a big hoopla about it at the time on the Fediverse.

Then what is @protonprivacy@mastodon.social ?

I know Proton doesn't list this Mastodon account on their website, but it seems official and active, having just posted something 23 hours ago.

hear-me.social
4
3
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago

Just about the entire internet uses certificate authorities to establish trust. Here, a simple old-school social engineering trick broke this trust and allowed hackers to get signed certificates from DigiCert for their malware.

There is a better way to establish certificate trust that doesn't rely on a 3rd party, and it's free too. It's called DANE, which binds the trust directly to the Domain Name System by using DNSSEC. DANE is ideal for code signing certificates (and other uses), but is overlooked.

This attack is virtually impossible under DANE. A vulnerable support person is of no use. Hackers would need to directly compromise the target's DNS infrastructure, the registrar, and the top-level domain authority. All three. Nearly impossible compared to just finding some dupe at the CA in a public chat room.

https://hackread.com/hackers-digicert-issue-certificates-sign-malware/

#DANE #CertificateAuthorities #DigiCert

hackread.com
3
0
3
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago
Replying to
@Skwerlgyrl @TheZorse@protonprivacy is definitely official. #Proton never closed the account; they just stopped posting to it after their announcement to leave Mastodon, until recently. But they haven't made any official announcement that they are back. So who knows? As for not liking Mastodon, the reason they stopped posting was officially that they lacked the resources to have social accounts everywhere, although they seemed to keep their social accounts that are just about everywhere, except for Mastodon, even on platforms I never heard of. It may be because of people carrying on on Mastodon, as people tend to do on Mastodon, about a comment made by Proton CEO Andy Yen He wrote something that many interpreted as being MAGA supportive and others interpreted as his seeing something good in just one thing the Republicans did (maybe mistakenly) as it relates to controlling Big Tech. I won't get into it. But the most unbiased assessment of that mess is here: https://medium.com/@ovenplayer/does-proton-really-support-trump-a-deeper-analysis-and-surprising-findings-aed4fee4305e Spoiler: He and Proton put huge amounts of money into liberal causes and none into Trump or MAGA stuff. Nobody @ me about Yen and Proton being evil. I'm not going to respond
medium.com
3
1
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago
Replying to
@debby DDG is good, but they still use contextual ads powered through Microsoft. There was that controversy in the past where it was found that DDG had some ad-related agreements with Microsoft that were not disclosed. Still far better, IMHO, than Google and Bing. No ads in Kagi. Kagi allows me to down-rank results on my own terms. I don't want Reddit results or Pinterest results. I don't want NY Post or WSJ articles, etc. They filter out AI slop if you ask for it. I can rank certain sources as more desirable than others to control what is higher in the results. They have many extras. They have a private AI which has been useful. They have a private translation service. Many tuning options. They have their own spider, although they do supplement if necessary. I believe DDG uses Bing. If Bing falls victim to SEO Spam or they decide to manipulate results, that spam and those biases could inadvertently filter into the DDG results. The bottom line is that it shows me exactly what I want when I search and isn't open as much to manipulation. I think it's worth paying for.
3
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 4mo ago

For those who care, following yesterday's blowback on the sudden new rate limits imposed on #Gemini, Google has permanently reset the weekly quota for all paid plans and tripled the usage boundaries.

For those who don't care or who are upset about any #AI news, please don't AT me.

https://www.androidheadlines.com/2026/05/google-triples-gemini-paid-plans-usage-limits.html

hear-me.social
2
0
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago

Thank you, #Google.

Websites that hijack your back button must stop by June 15th or face consequences. Typically done by sites to get more clicks, force you to see advertising, or manipulate your experience. #LinkedIn, not surprisingly, is one of these offensive sites.

https://arstechnica.com/gadgets/2026/04/websites-that-hijack-your-back-button-must-stop-by-june-15-or-face-googles-wrath/

#webdev

hear-me.social
3
2
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 4mo ago
Replying to
@shanie@mastodon.tails.ch It's all controlled by the lawyers. They will decide what is necessary so Mastodon can continue owning their trademarked names. Companies must, by law, show they protect these assets vigorously. "Aspirin" was deemed not vigorously protected enough in the U.S. Bayer lost the right to this trademarked name, for example. It's called genericide; the name becomes generic. Other examples: Escalator, Thermos, Trampoline, and Videotape. I imagine that mastodon.world will get licensed, but many others will not if they are not considered well-run and well moderated by Mastodon gGmbH standards.
2
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 4mo ago

I never use the application names in any of my servers because I'm always worried about future trademark enforcement.

The Mastodon organization guidelines at https://joinmastodon.org/trademark say:

Do not use or register, in whole or in part, the Mastodon marks as part of your own or any other trademark, service mark, domain name, company name, trade name, product name, or service name.

When I search the database here for instances known to this server that contain "mastodon" in their domain names, I see over 1,800 server names. And it's unknown if they would consider "mstdn" to be a violation as well.

I wonder how far they will push this enforcement. A Mastodon server cannot change its domain name.

#MastoDev #MastoAdmin #Mastodon #TrunkAndTidbits

Trademark Policy of Mastodon
joinmastodon.org

Trademark Policy of Mastodon

2
2
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 6mo ago
Replying to
@_elena @Mastodon Maybe the painting should go on a T-shirt. You're right, the picture is the perfect background for you. Good luck with the Louvre.
3
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 30mo ago

Star Trek fans! :trekbadgetng:

7 of 9 (Jeri Ryan) has turned on Threads Federation and can now be followed on the Fediverse!

She once had an active Mastodon account but hasn't posted anything since last September. But, she's a prolific poster on #threads at @jerilryan@threads.net

Her inactive Mastodon account is @JeriLRyan@mastodon.world

#startrek #7of9 #SevenofNine @georgetakei@universeodon.com @GoodAaron@mastodon.social

hear-me.social
48
4
18
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 4mo ago

Seems like a good idea for #Bitwarden users to jump ship now.

https://www.osnews.com/story/145029/get-your-passwords-out-of-bitwarden-while-you-still-can/

hear-me.social
1
2
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago

#Letsencrypt is not living up to their name at the moment.

It seems the disruption in generating certificates is deliberate, related to some event:

May 8, 2026 18:37 UTC
INVESTIGATING

We have been made aware of a potential incident and are shutting down all issuance.

https://letsencrypt.status.io/

hear-me.social
1
0
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago

@ProtonDrive@mastodon.social Are there any special considerations using PQE with the email bridge?

1
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 24mo ago

This! This! So perfectly stated and well-written.

Beyond technical features: why we need to talk about the values of the Fediverse (part 1).

As users of the Fediverse, I think we'll all relate and understand.

https://blog.elenarossini.com/the-values-of-the-fediverse-ethical-social-media/?ref=the-future-is-federated-newsletter

@_elena@mastodon.social

#Fediverse

blog.elenarossini.com
14
2
10
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago

I am plagued by the problem described in this post.

My #Samsung monitor often goes black, sometimes just from standing from my office chair, not even touching anything. And when I stand, I'm always suddenly electrified and will give off a shock when I touch something grounded. If the Samsung monitor is near the shock event, it will go black.

I often need to disconnect and reconnect the monitor from the video port to get it back, but sometimes it won't, and I need to reboot.

I also have a #Dell monitor next to the Samsung, which has never been affected.

Does anyone else deal with this shocking situation?

BTW, this post blames it on the gas canister in the office chair giving off an EMI spike when I stand.

https://aalonso.dev/blog/2023/how-to-fix-monitor-that-goes-black-off-due-to-static-electricity-in-chair/

hear-me.social
1
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@pteryx I set up my own email server on DigitalOcean and instantly got blacklisted by Spamhaus because it was a new domain, and then by another company because the IP address belonged to DigitalOcean. Most mail servers also flagged it as spam because the domain was less than 60 days old and because it was a .online TLD. For a long time, some of my emails were immediately bounced back or went to spam folders because of all these reasons. I also believe that every home IP address is automatically blacklisted, which makes it worse for your roommate. You can eventually overcome it by letting the domain reputation slowly develop and then doing a direct appeal to the blacklist companies. But, it takes a long time. It's amazing any spam gets delivered.
8
3
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 10mo ago
Replying to
@Tutanota@mastodon.social Are these your nameservers? The ones in the huge AWS egg basket? The basket that had a global outage last month? Name Servers: ns-1138.awsdns-14.org ns-150.awsdns-18.com ns-1967.awsdns-53.co.uk ns-724.awsdns-26.net Domain: tuta.com Registered On: 1997-06-14
2
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 29mo ago

It's a legal conundrum

#Trump #PoliticalHumor #USPol #USPolitics

hear-me.social
7
1
4
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@mcnewton @simrob Thanks for this. I should have posted the record names. Thanks for adding this! Yep, "@" as the name of the spf record, and "_dmarc" for the name of the dmarc record.
3
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@dec23k @tychotithonus My DNS provider doesn't allow just a dot. Many don't. But saying nobody is allowed to send emails for me (SPF record) should cover it.
2
2
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@Aganim I'm not an expert on this (it's a career), but I know it's not that simple. If I get an unforwarded email, I definitely want both DKIM and SPF to pass. I want only email from an authorized server, and I want an email that is not modified and is properly signed. No exceptions. Both must pass. If I get email from a mailing list that is sending email to me on behalf of a different domain, I want SPF to pass in that I want to know that the mailing list provider's server is authorized to send email on behalf of the original domain. But, in this case, the original DKIM will fail because the mailing list provider will have changed the email. But, I expect the new DKIM to be correct, or I won't accept it. So, here, a failure on the original DKIM can be acceptable. If someone forwards an email to me, the original DKIM will fail. I will accept it. But, I want the SPF of the forwarding server to pass, and the new DKIM for the changed email to pass. There's also email redirection and forwards that happen at the server vs. the client and there can be separate rules for this. The records can get complicated if you truly want to control different scenarios. But, you don't always want to accept an email if only 1 check passes. At least, this is my understading of it all.
2
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@leoncowle Thanks, Leon!
1
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@momo Yep, people have mentioned it. I went back to try it and discovered my ISP does not allow a null MX record to be added. If it can be done, it's great, but an SPF that says nobody can send email should do the trick. If you could do, that's better.
1
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@amberage @pteryx Your points, I think, are very valid. And I live with the fear that I will end up with the same fate.
1
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 41mo ago
Replying to
@AbandonedAmerica@mastodon.social I agree with everything that you've written
1
2
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 46mo ago
Replying to
@atrupar @petercsoka I agree strongly with @extraface The instance that you are on matters tremendously. You need to be in an instance where moderation matches the world under which you want to exist. You don't want to be attacked or abused in your instance. You don't want other instances to de-federate yours. You don't want to be exposed to uncontrolled hatred and idiocy. And (rarely this is mentioned), but you want to make sure the instance is properly technically maintained. Make sure it's running the latest version. If it isn't, you are not getting the full experience, it may not be secure, and it may indicate that the owner is not inclined to maintain it, or is just not interested or capable. Your data may not be properly backed up, for example. Your experience may be sub-par. Make sure it's professionally deployed. A server running in someone's garage could one day disappear, become annoyingly unreliable, or lose your data. A cloud instance can be easily scaled out, won't burn out, and is probably using secure and reliable storage. And therefore there should be less downtime too. Jerry
1
3
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 5mo ago
Replying to
@codewizard Without using an OS other than Android, but otherwise Android=Google I would think
0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@Dero_10 @pteryx I had that issue a lot when I was running a Linux server in the cloud. It's why I stopped using my own Wireguard VPN server I hosted on Digital Ocean. So many sites would block it.
0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago
Replying to on fosstodon.org
@castaway@fosstodon.org Sure. I'm using the Docker version, and it comes broken. Mobilizon ships with paranoid privacy. Specifically, it uses: "Referrer-Policy: same-origin" which is not supported by *.tile.openstreetmap.org, the map provider they also choose as their default. openstreetmap wants a referrer so they have some control over abuse and scraping. It will accept a referrer that consists solely of the site's origin, in my case "https[:]//my-group.events/", which doesn't violate any user privacy. It doesn't forward slugs, paths, or query parameters, so privacy concerns should be addressed with this policy. So, you need to use "Referrer-Policy: strict-origin-when-cross-origin" instead to pass along the domain name. The default passes nothing. The problem is that it's not a good idea to modify the Docker containers directly and update the configuration files, as they get reset with each update. Instead, you can have Nginx discard and replace the Referrer-Policy before sending. For reference, here's my Nginx configuration, which uses "proxy_hide_header" to remove what is passed in by default. # Map block to handle WebSockets dynamically map $http_upgrade $connection_upgrade { default upgrade; '' close; } # Redirect HTTP to HTTPS server { listen 80; listen [::]:80; server_name my-group.events; return 301 https://$host$request_uri } # HTTPS Server server { listen 443 ssl http2; listen [::]:443 ssl http2; server_name my-group.events; # SSL Configuration ssl_certificate /etc/letsencrypt/live/my-group.events/fullchain.pem; ssl_certificate_key /etc/letsencrypt/live/my-group.events/privkey.pem; include /etc/letsencrypt/options-ssl-nginx.conf; ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; ssl_trusted_certificate /etc/letsencrypt/live/my-group.events/chain.pem; ssl_stapling on; ssl_stapling_verify on; ssl_ecdh_curve prime256v1; # Security Headers (Sent to Client) add_header Strict-Transport-Security "max-age=31536000; includeSubDomains" always; add_header Referrer-Policy "strict-origin-when-cross-origin" always; add_header X-Content-Type-Options "nosniff" always; add_header X-XSS-Protection "1; mode=block" always; # Strip upstream security headers from Mobilizon/Phoenix to eliminate duplicates proxy_hide_header Referrer-Policy; proxy_hide_header X-Content-Type-Options; proxy_hide_header X-XSS-Protection; # Gzip Compression gzip on; gzip_vary on; gzip_proxied any; gzip_comp_level 6; gzip_buffers 16 8k; gzip_http_version 1.1; gzip_types text/plain text/css application/json application/javascript text/xml application/xml application/xml+rss text/javascript application/activity+json application/atom+xml image/svg+xml; client_max_body_size 16m; # Global Proxy Settings proxy_http_version 1.1; proxy_set_header Host $host; proxy_set_header X-Real-IP $remote_addr; proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; proxy_set_header X-Forwarded-Proto $scheme; proxy_set_header X-Forwarded-Host $host; proxy_set_header X-Forwarded-Port $server_port; proxy_set_header Upgrade $http_upgrade; proxy_set_header Connection $connection_upgrade; # Main Application location / { proxy_pass http://127.0.0.1:4000 } # Static Media and Proxy Assets location ~ ^/(media|proxy) { etag off; access_log off; # Re-apply security headers due to Nginx block inheritance behavior add_header Strict-Transport-Security "max-age=31536000; includeSubDomains" always; add_header Referrer-Policy "strict-origin-when-cross-origin" always; add_header X-Content-Type-Options "nosniff" always; add_header X-XSS-Protection "1; mode=block" always; add_header Cache-Control "public, max-age=31536000, immutable"; proxy_pass http://127.0.0.1:4000 } } If you aren't using Docker, it's still the same concept.
$host$request_uri
0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@amyipdev @jernej__s What I learned is that every single home IP address from every single ISP provider is pre-blacklisted by spamhaus and several others I came across. It's not your ISP's fault.
0
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 3mo ago
Replying to
@_elena@mastodon.social Grateful for you too! Because your work has impact, and it's the impact we really need right now!
0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

More U.S. troops have died amid Iran war than Pentagon has disclosed publicly

https://wapo.st/3SPycmE

#Iran

wapo.st
0
0
1
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

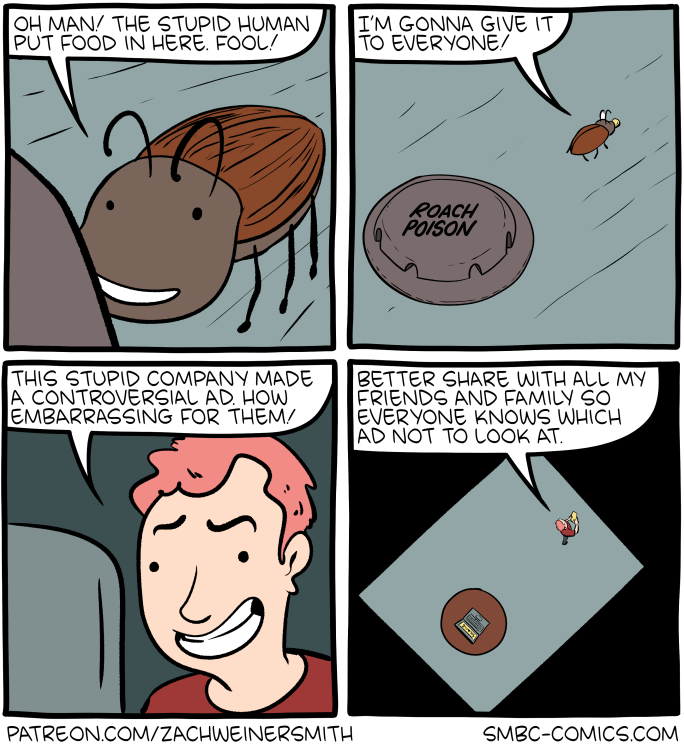
Well done

https://www.smbc-comics.com/comic/roach-2

#comics #SMBC_comics

Saturday Morning Breakfast Cereal - Roach
smbc-comics.com

Saturday Morning Breakfast Cereal - Roach

Saturday Morning Breakfast Cereal - Roach

0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@b3lt3r@mastodon.b3lt3r.com I'm far from an expert, but if your redirect is at the server, and your server adds a ".forward" to the email, and does not alter anything, you should be fine because your SPF and DKIM should pass. If your redirect is via an email client, or the server doesn't add a .forward, it may alter the email slightly, but in a way sufficient for DKIM to fail because the hash won't match any longer. But, I think in this case, if SPF passes, your email client would still accept it since the original DKIM passed before the forwarding. It gets really complicated. Suggest you try it. And this is based on my understanding, which, who knows?
0
1
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 46mo ago
Replying to
@petercsoka @atrupar @extraface I believe mastodon.online does, as well.
0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 2w ago

RE: @pixelfed@mastodon.social

https://gr8.pics was updated the same morning this update came out.

mastodon.social
0
0
0
0
Open post
Jerry on Mastodon @Jerry@hear-me.social
· 22mo ago
Replying to
@esplovago Yep. If you want to have different rules for subdomains, then the records get much more complicated. but "v=spf1 -all" pertains to the domain and subdomains.
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 22:37:32 UTC