Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Daily CyberSecurity

@DailyCyberSecurity@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Stay ahead with Daily CyberSecurity. We deliver rapid zero-hour alerts and expert analysis on critical vulnerabilities, CVEs, and emerging cyber threats.

112 Followers
6 Following
50 Posts
Joined June 23, 2026
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Discover the thrilling details of SpaceX Starship Flight 14. This historic mission attempts its first true orbital insertion and Starlink V3 deployment. #SpaceX #Starship #Flight14 #SpaceExploration #Starlink https://dailytechnow.com/spacex-starship-flight-14/
SpaceX Starship Flight 14: Historic Orbital Test Launch
Daily Tech Now

SpaceX Starship Flight 14: Historic Orbital Test Launch

Discover the thrilling details of SpaceX Starship Flight 14. This historic mission attempts its first true orbital insertion and Starlink V3 deployment.

2
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Discover how autonomous AI agents executed 105 cyberattacks in 5 days, stealing over 600,000 credit cards using tools like Strix, Cairn, and Hermes. #CyberSecurity #ArtificialIntelligence #DataBreach #Carding #TechNews https://meterpreter.org/autonomous-ai-agents-steal-credit-cards/?utm_source=mastodon&utm_medium=jetpack_social
Autonomous AI Agents Steal 600K Credit Cards in Massive Campaign
Information Security News

Autonomous AI Agents Steal 600K Credit Cards in Massive Campaign

Discover how autonomous AI agents executed 105 cyberattacks in 5 days, stealing over 600,000 credit cards using tools like Strix, Cairn, and Hermes.

1
0
2
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence. #TaskStomp #PowerShell #Malware #CyberSecurity #ThreatIntel https://securityonline.info/taskstomp-powershell-backdoor/?utm_source=mastodon&utm_medium=jetpack_social
New TASK#STOMP PowerShell Backdoor Targets Windows
Daily CyberSecurity

New TASK#STOMP PowerShell Backdoor Targets Windows

Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence.

1
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Perplexity Portable Computer now runs on Windows PCs with NVIDIA RTX GPUs, handling agentic AI tasks locally with no cloud credits used. #Perplexity #PortableComputer #LocalAI #NVIDIA #RTX #AgenticAI #TechNews https://securityexpress.info/perplexity-portable-computer-windows/?utm_source=mastodon&utm_medium=jetpack_social
Perplexity Portable Computer Lands on Windows
Tech News

Perplexity Portable Computer Lands on Windows

Perplexity Portable Computer now runs on Windows PCs with NVIDIA RTX GPUs, handling agentic AI tasks locally with no cloud credits used.

2
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
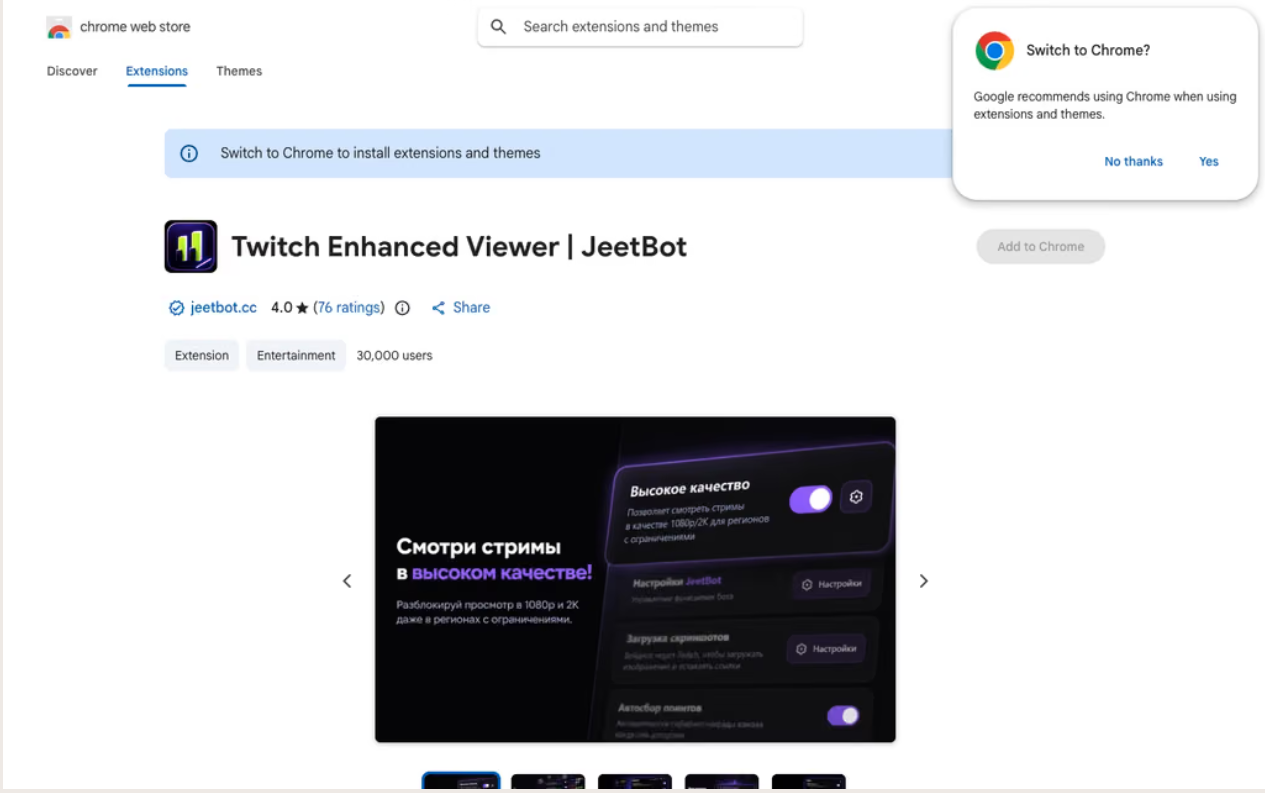
A malicious Twitch extension exposes account credentials to third parties. Learn how this malicious Twitch extension token theft impacts 31,000 viewers. #Twitch #BrowserExtension #Malware #Cybersecurity #OAuthTheft https://securityonline.info/malicious-twitch-extension/?utm_source=mastodon&utm_medium=jetpack_social
Malicious Twitch Extension Steals 30,000 User Tokens
Daily CyberSecurity

Malicious Twitch Extension Steals 30,000 User Tokens

A malicious Twitch extension exposes account credentials to third parties. Learn how this malicious Twitch extension token theft impacts 31,000 viewers.

2
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Discover the new Cyber Resilience Act reporting rules. EU digital product manufacturers face strict 24-hour deadlines for actively exploited vulnerabilities. #CyberResilienceAct #ENISA #VulnerabilityReporting #CyberSecurity #EUCompliance https://meterpreter.org/cyber-resilience-act-reporting-mandate/?utm_source=mastodon&utm_medium=jetpack_social
Cyber Resilience Act Reporting: 24-Hour Mandate Begins
Information Security News

Cyber Resilience Act Reporting: 24-Hour Mandate Begins

Discover the new Cyber Resilience Act reporting rules. EU digital product manufacturers face strict 24-hour deadlines for actively exploited vulnerabilities.

1
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately. #WordPress #WordPress711 #WebSecurity #XSS #CMS #Vulnerability #InfoSec #PatchNow #CyberSecurity #WebDev https://securityonline.info/wordpress-7-1-1-security-release/?utm_source=mastodon&utm_medium=jetpack_social
WordPress 7.1.1 Fixes 11 Security Flaws, Update Now
Daily CyberSecurity

WordPress 7.1.1 Fixes 11 Security Flaws, Update Now

The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Discover the new FreeBSD EC2 desktop images. Easily launch a KDE graphical environment on AWS without manual configuration. Connect via RDP effortlessly. #FreeBSD #AmazonEC2 #KDE #CloudComputing #RDP https://dailytechnow.com/freebsd-ec2-desktop-images/
FreeBSD EC2 Desktop Images: Seamless KDE Cloud Setup
Daily Tech Now – Tech News on AI, Smartphones & Gadgets

FreeBSD EC2 Desktop Images: Seamless KDE Cloud Setup

Discover the new FreeBSD EC2 desktop images. Easily launch a KDE graphical environment on AWS without manual configuration. Connect via RDP effortlessly.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
OpenAI is building a personal AI agent to counter SpaceXAI's Grok Bot and Meta's Muse, hiring the OpenClaw creator to lead its Codex Bot effort. #OpenAI #AIagents #GrokBot #MetaMuse #Codex #OpenClaw #TechNews https://securityonline.info/openai-counter-grok-bot-muse/?utm_source=mastodon&utm_medium=jetpack_social
OpenAI Races to Counter Grok Bot and Meta's Muse
Daily CyberSecurity

OpenAI Races to Counter Grok Bot and Meta's Muse

OpenAI is building a personal AI agent to counter SpaceXAI's Grok Bot and Meta's Muse, hiring the OpenClaw creator to lead its Codex Bot effort.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Discover how the Psychedelic Stealer malware uses fake Cloudflare CAPTCHA ClickFix lures to infect computers and steal passwords and cryptocurrency. #PsychedelicStealer #ClickFix #CyberSecurity #Malware #Cloudflare https://meterpreter.org/psychedelic-stealer-clickfix-campaign/?utm_source=mastodon&utm_medium=jetpack_social
Psychedelic Stealer Spreads via Fake Cloudflare ClickFix Pages
Information Security News

Psychedelic Stealer Spreads via Fake Cloudflare ClickFix Pages

Discover how the Psychedelic Stealer malware uses fake Cloudflare CAPTCHA ClickFix lures to infect computers and steal passwords and cryptocurrency.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Discover how a sophisticated AI voice cloning scam defrauded Intesa Sanpaolo's Fideuram division of €95 million. Learn about deepfake threats to banking. #AIVoiceCloning #CyberSecurity #BankScam #Deepfake #IntesaSanpaolo https://securityexpress.info/ai-voice-cloning-scam-intesa/?utm_source=mastodon&utm_medium=jetpack_social
AI Voice Cloning Scam Costs Intesa Sanpaolo Millions
Tech News

AI Voice Cloning Scam Costs Intesa Sanpaolo Millions

Discover how a sophisticated AI voice cloning scam defrauded Intesa Sanpaolo's Fideuram division of €95 million. Learn about deepfake threats to banking.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Discover why GitHub blocks Outlook and Hotmail for new account registrations. Learn about the persistent fraud and abuse driving this Microsoft email ban. #GitHub #Microsoft #EmailSecurity #TechNews #CyberSecurity https://securityonline.info/github-blocks-outlook-hotmail-registration/?utm_source=mastodon&utm_medium=jetpack_social
GitHub Blocks New Outlook and Hotmail Sign-Ups
Daily CyberSecurity

GitHub Blocks New Outlook and Hotmail Sign-Ups

Discover why GitHub blocks Outlook and Hotmail for new account registrations. Learn about the persistent fraud and abuse driving this Microsoft email ban.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
An Authlib signature bypass vulnerability (CVE-2026-96760, CVE-2026-28802, CVE-2026-27962) lets attackers forge JWS payloads. Update libraries now. #Authlib #CVE202696760 #Cybersecurity #JWS #Vulnerability https://securityonline.info/authlib-signature-bypass-vulnerability/?utm_source=mastodon&utm_medium=jetpack_social
Authlib Signature Bypass Vulnerability Exposes Apps
Daily CyberSecurity

Authlib Signature Bypass Vulnerability Exposes Apps

An Authlib signature bypass vulnerability (CVE-2026-96760, CVE-2026-28802, CVE-2026-27962) lets attackers forge JWS payloads. Update libraries now.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 4w ago
MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now. #MongoDB #Vulnerability #CVE #DatabaseSecurity #DenialOfService #InfoSec #PatchNow #CyberSecurity #MongoDBServer #AppSec https://securityonline.info/mongodb-server-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
MongoDB Patches 24 Server Vulnerabilities, One Critical
Daily CyberSecurity

MongoDB Patches 24 Server Vulnerabilities, One Critical

MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today. #WordPress #CVE202693485 #StoredXSS #RCE #Cybersecurity #Infosec https://securityonline.info/wordpress-stored-xss-poc/?utm_source=mastodon&utm_medium=jetpack_social
WordPress Stored XSS Details and PoC Publicly Disclosed
Daily CyberSecurity

WordPress Stored XSS Details and PoC Publicly Disclosed

Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately. #Eufy #CVE202693289 #CVE202693291 #IoT #Cybersecurity #Vulnerability https://securityonline.info/eufy-robot-vacuum-vulnerabilities-command-injection/?utm_source=mastodon&utm_medium=jetpack_social
Critical Eufy Robot Vacuum Vulnerabilities Allow System Takeover
Daily CyberSecurity

Critical Eufy Robot Vacuum Vulnerabilities Allow System Takeover

Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers. #DLink #DAP1360 #CVE202695675 #RCE #RouterSecurity #Cybersecurity https://securityonline.info/d-link-dap-1360-vulnerability-poc/?utm_source=mastodon&utm_medium=jetpack_social
D-Link DAP-1360 Vulnerability Details and PoC Disclosed
Daily CyberSecurity

D-Link DAP-1360 Vulnerability Details and PoC Disclosed

Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
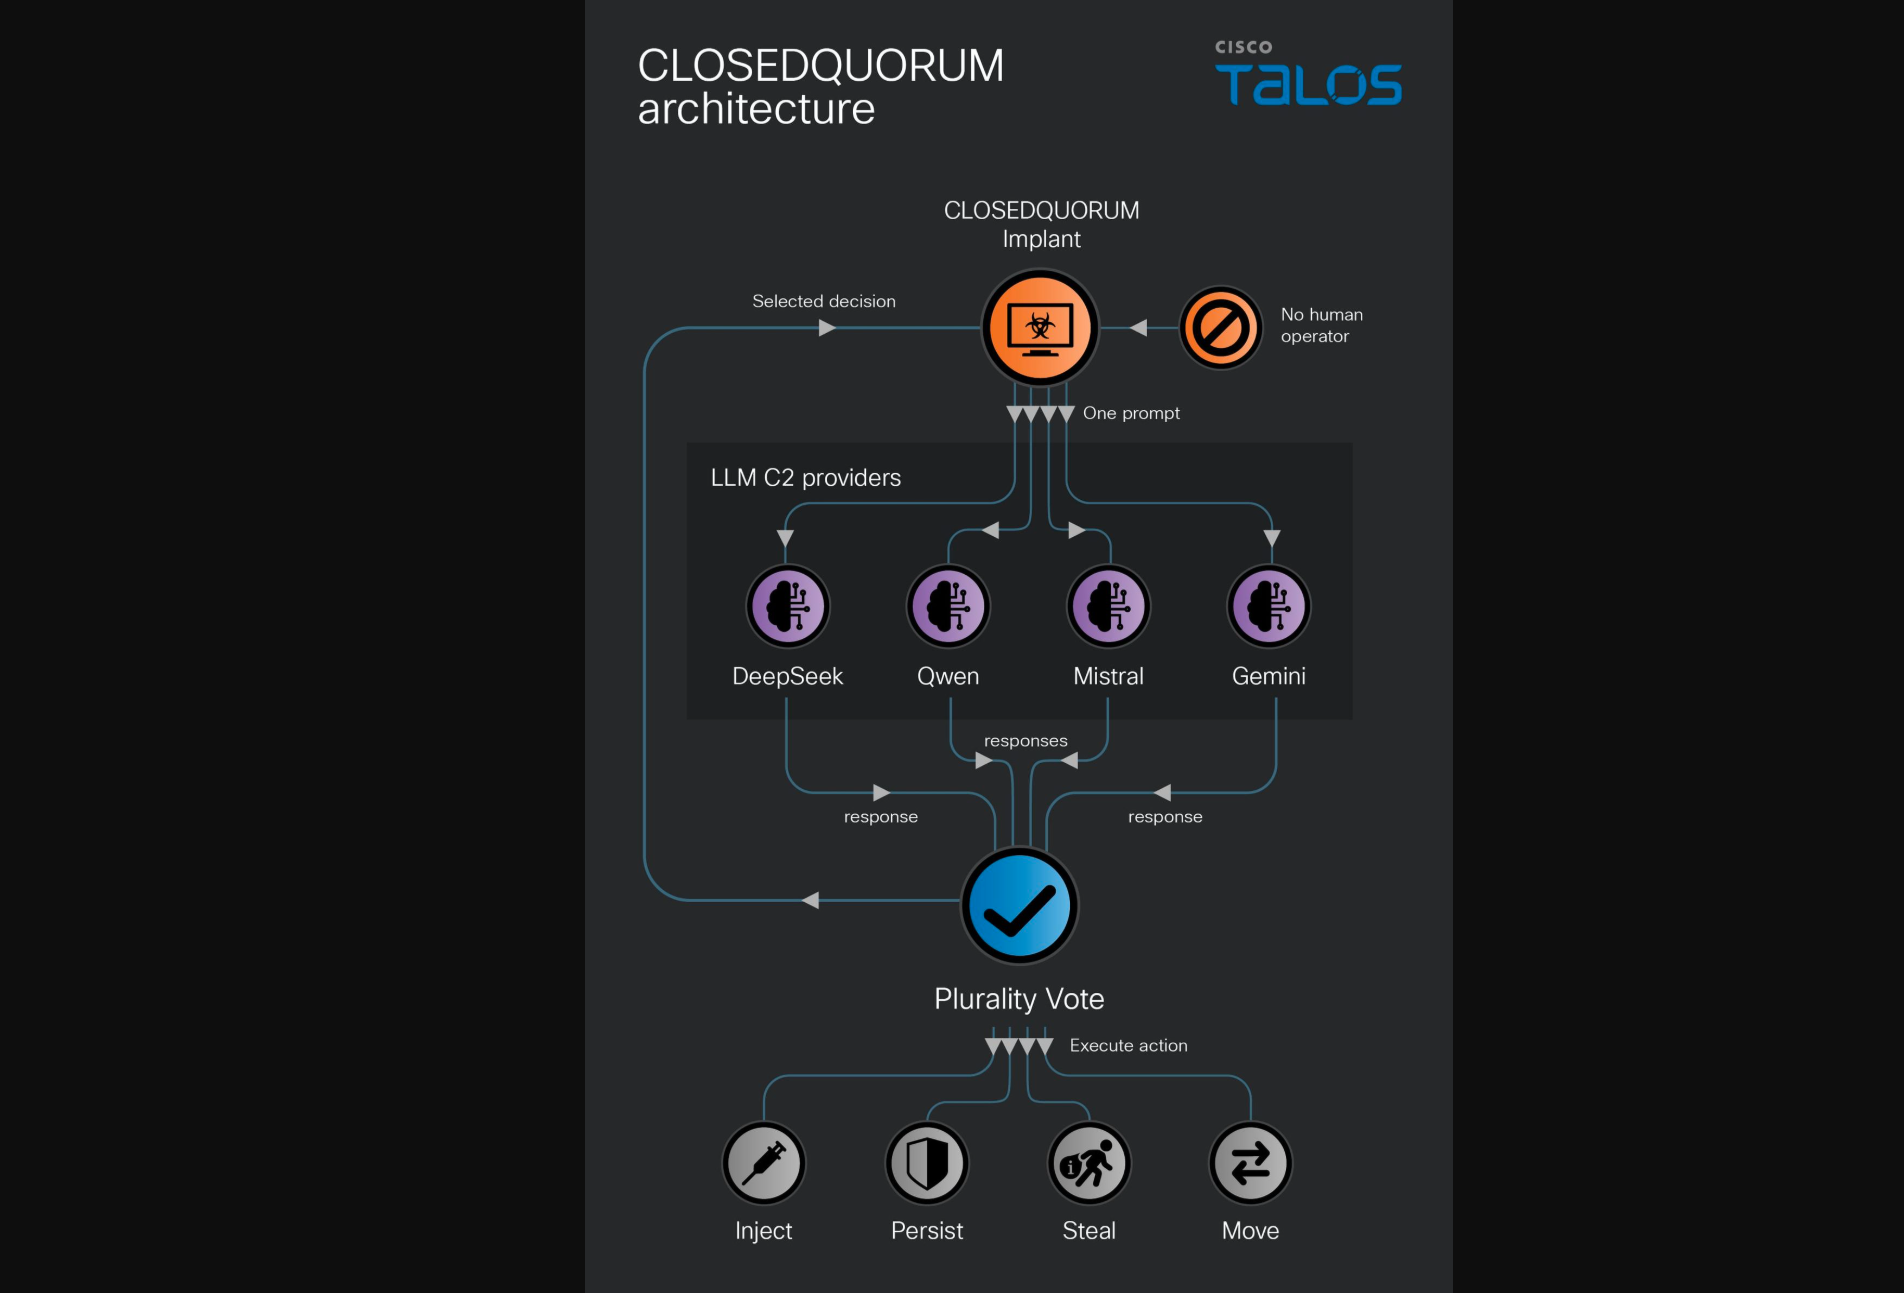
Cisco Talos discovered autonomous CLOSEDQUORUM AI malware. The CLOSEDQUORUM AI malware uses multiple LLMs to guide cyberattacks independently. #ClosedQuorum #AIMalware #CiscoTalos #CyberSecurity #ThreatIntel https://securityonline.info/closedquorum-ai-malware/?utm_source=mastodon&utm_medium=jetpack_social
CLOSEDQUORUM AI Malware Uses LLMs for Autonomous C2
Daily CyberSecurity

CLOSEDQUORUM AI Malware Uses LLMs for Autonomous C2

Cisco Talos discovered autonomous CLOSEDQUORUM AI malware. The CLOSEDQUORUM AI malware uses multiple LLMs to guide cyberattacks independently.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
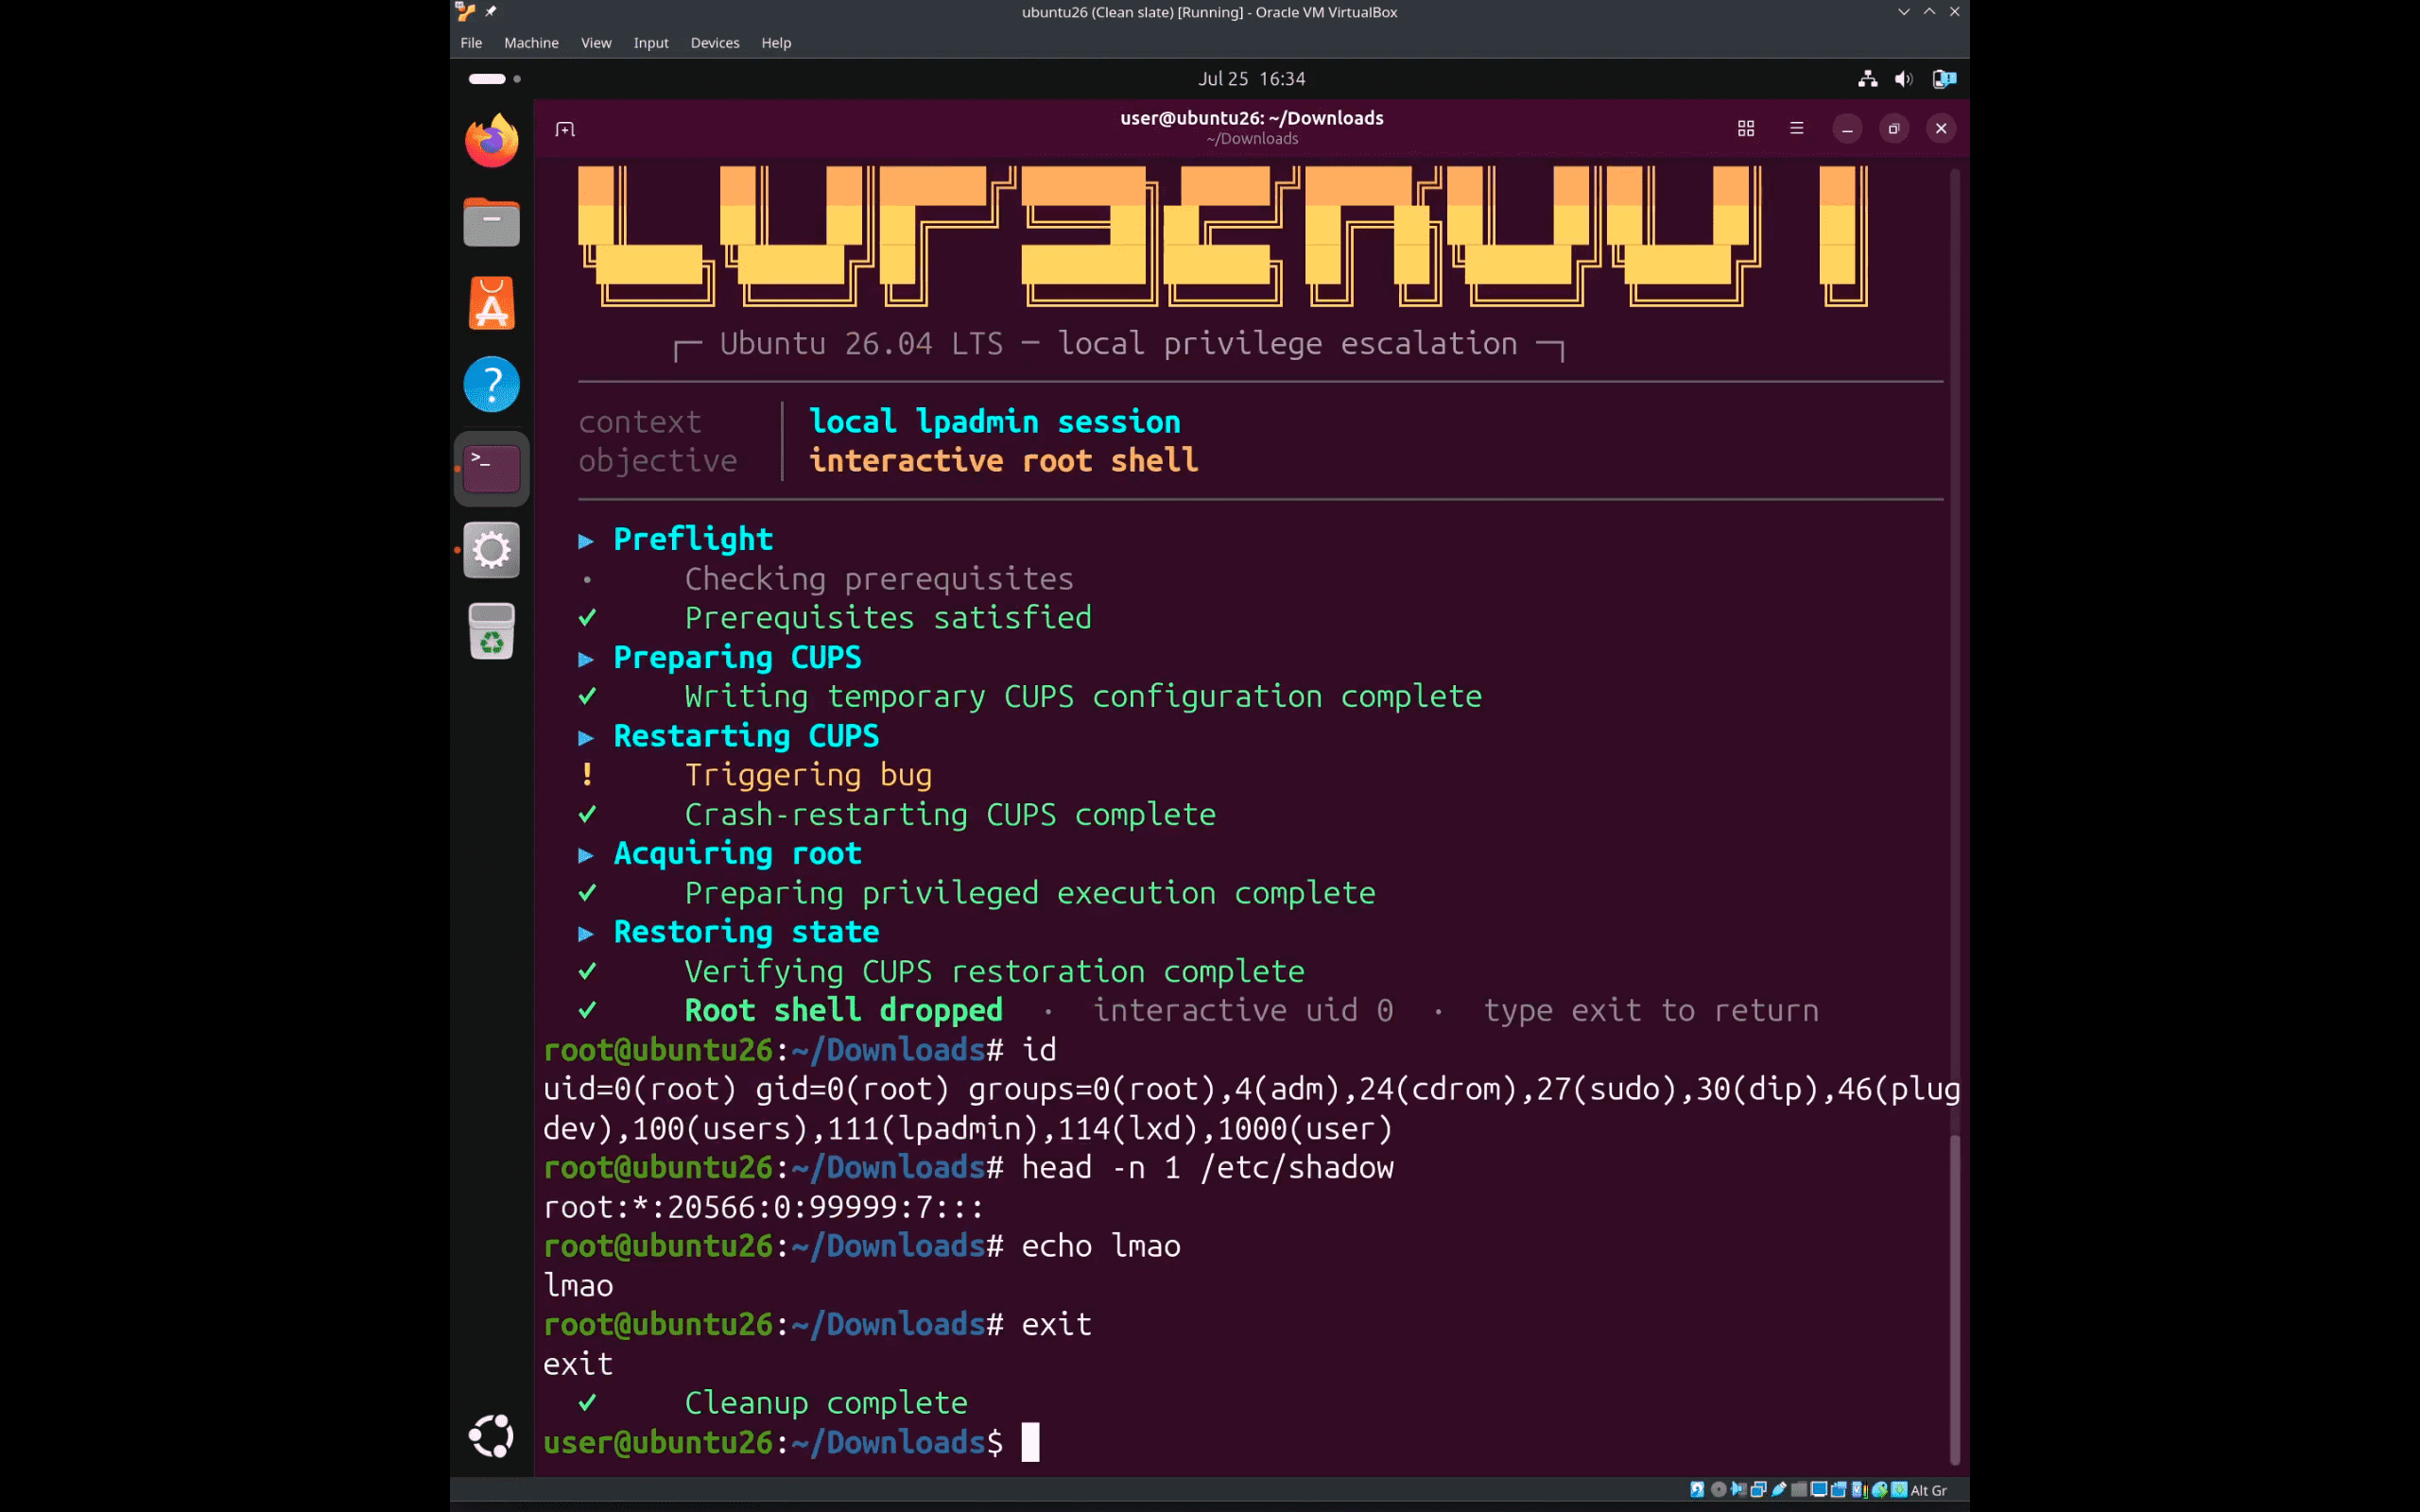
A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations. #cups2root #CUPS #PrivilegeEscalation #LinuxSecurity #ZeroDay #lpadmin #PoC #RootExploit https://securityonline.info/cups2root-lpadmin-root-poc/?utm_source=mastodon&utm_medium=jetpack_social
cups2root: Public PoC Exploit Escalates lpadmin to Root on CUPS
Daily CyberSecurity

cups2root: Public PoC Exploit Escalates lpadmin to Root on CUPS

A public PoC exploit, cups2root, chains a CUPS privilege escalation to take lpadmin users to root. No CVE or patch yet. See the mechanism and mitigations.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Discover the new Trump super intelligence mandate. The US government will replace the term artificial intelligence, sparking debate across the tech industry. #Trump #SuperIntelligence #ArtificialIntelligence #TechNews https://securityonline.info/trump-super-intelligence-mandate/?utm_source=mastodon&utm_medium=jetpack_social
Trump Mandates Super Intelligence to Replace AI Terminology
Daily CyberSecurity

Trump Mandates Super Intelligence to Replace AI Terminology

Discover the new Trump super intelligence mandate. The US government will replace the term artificial intelligence, sparking debate across the tech industry.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
A critical HPE EdgeConnect authorization bypass (CVE-2026-76670) enables full system compromise. Patch this HPE EdgeConnect authorization bypass now. #HPE #EdgeConnect #AuthorizationBypass #CVE202676670 #Cybersecurity https://securityonline.info/hpe-edgeconnect-authorization-bypass/?utm_source=mastodon&utm_medium=jetpack_social
Critical HPE EdgeConnect Authorization Bypass Exposed
Daily CyberSecurity

Critical HPE EdgeConnect Authorization Bypass Exposed

A critical HPE EdgeConnect authorization bypass (CVE-2026-76670) enables full system compromise. Patch this HPE EdgeConnect authorization bypass now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Discover the new Googlebook flagship laptop. Explore how this premium device integrates Android and Gemini AI to challenge Windows and macOS in the PC market. #Googlebook #GeminiAI #AndroidLaptop #TechNews #Google https://securityexpress.info/googlebook-flagship-laptop-gemini-ai/?utm_source=mastodon&utm_medium=jetpack_social
Googlebook Flagship Laptop Revealed: Android Meets Gemini AI
Tech News

Googlebook Flagship Laptop Revealed: Android Meets Gemini AI

Discover the new Googlebook flagship laptop. Explore how this premium device integrates Android and Gemini AI to challenge Windows and macOS in the PC market.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now. #ApacheKaraf #KarafVulnerabilities #Apache #PrivilegeEscalation #RCE #JMX #JavaSecurity #PatchNow https://securityonline.info/apache-karaf-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
Apache Karaf Vulnerabilities Let Low-Privilege Users Reach Admin and Code Execution
Daily CyberSecurity

Apache Karaf Vulnerabilities Let Low-Privilege Users Reach Admin and Code Execution

Four Apache Karaf vulnerabilities, including CVE-2026-92142, let viewer and manager users reach admin or RCE. Upgrade to Karaf 4.4.12 now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
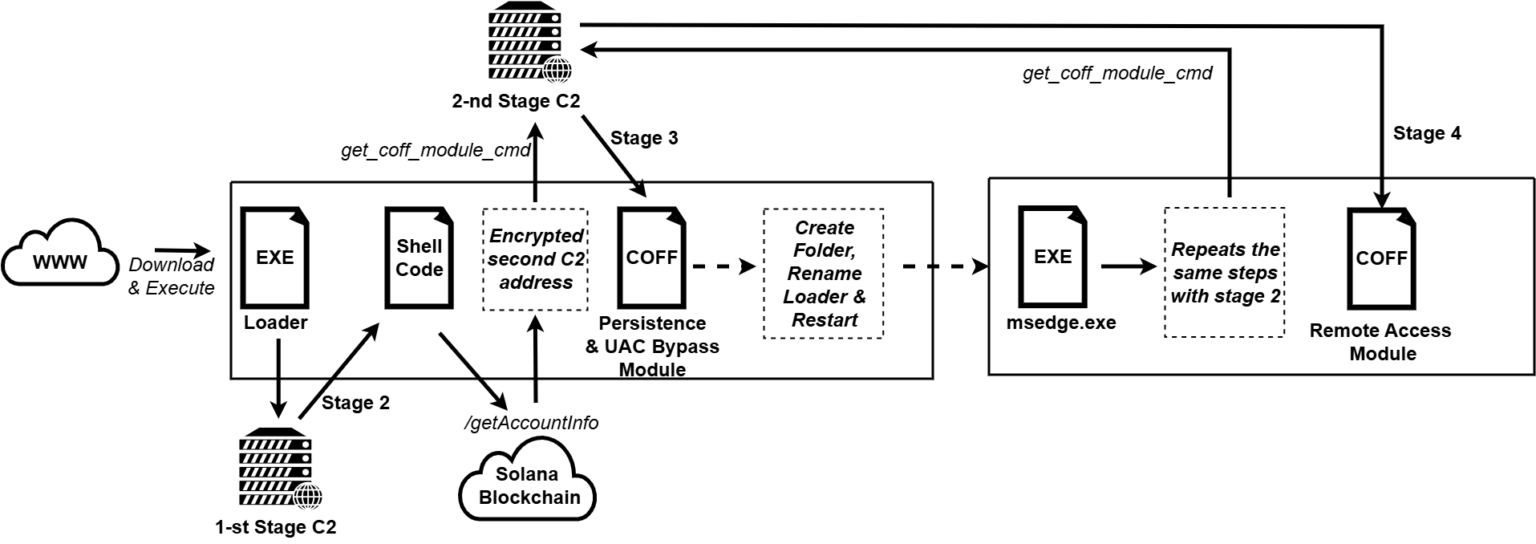
Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control. #MovieReaper #Malware #Torrent #CyberSecurity #Solana https://securityonline.info/moviereaper-malware/?utm_source=mastodon&utm_medium=jetpack_social
MovieReaper Malware Spreads via Compromised Torrents
Daily CyberSecurity

MovieReaper Malware Spreads via Compromised Torrents

Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
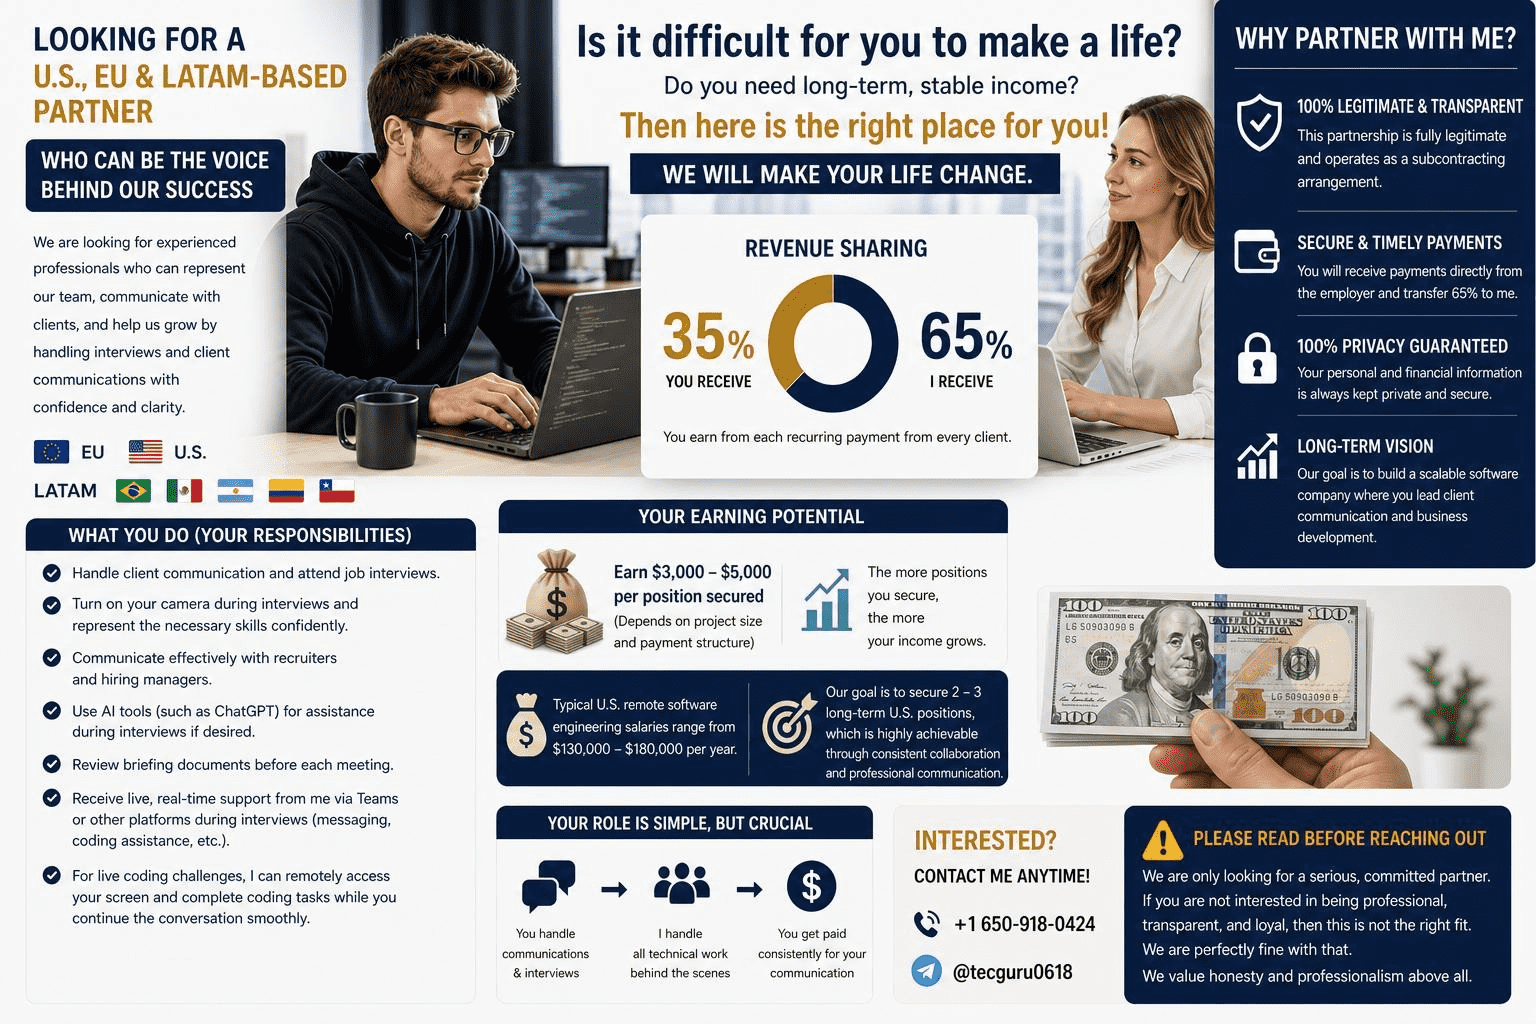
Learn how researchers exposed a North Korean IT worker using Discord to steal identities, conduct fraudulent interviews, and establish remote laptop farms. #NorthKorea #ITWorker #DiscordScam #CyberSecurity #IdentityTheft https://securityexpress.info/north-korean-it-worker-discord/?utm_source=mastodon&utm_medium=jetpack_social
North Korean IT Worker Discord Scheme Uncovered
Tech News

North Korean IT Worker Discord Scheme Uncovered

Learn how researchers exposed a North Korean IT worker using Discord to steal identities, conduct fraudulent interviews, and establish remote laptop farms.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Learn why CISA added GitLab CVE-2026-85706 to the Known Exploited Vulnerabilities catalog. Discover how this CVSS 10 flaw allows remote secret extraction. #GitLab #CVE202685706 #CISA #CyberSecurity #Vulnerability https://meterpreter.org/gitlab-cve-2026-85706-cisa-exploitation/?utm_source=mastodon&utm_medium=jetpack_social
GitLab CVE-2026-85706: CISA Confirms Active Exploitation
Information Security News

GitLab CVE-2026-85706: CISA Confirms Active Exploitation

Learn why CISA added GitLab CVE-2026-85706 to the Known Exploited Vulnerabilities catalog. Discover how this CVSS 10 flaw allows remote secret extraction.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
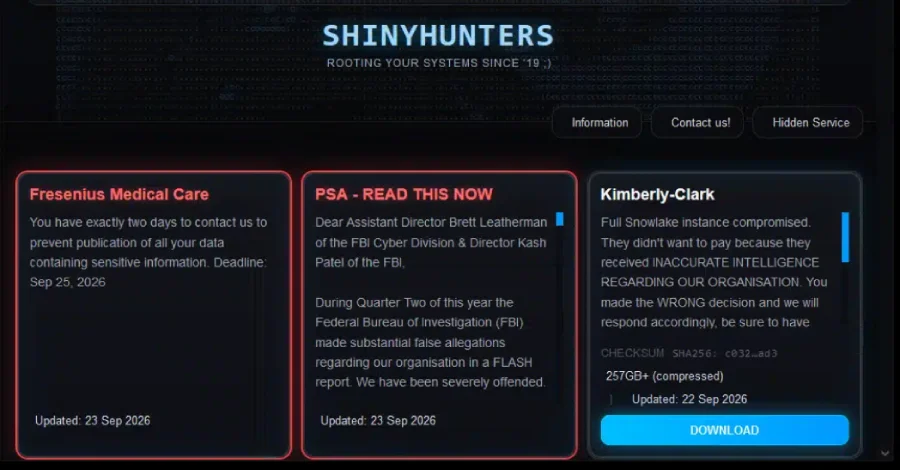
The FBI ShinyHunters breach may expose staff of the FBI's Remote Operations Unit hacking team, via a claimed Oracle PeopleSoft zero-day. FBI confirms probe. #FBI #ShinyHunters #RemoteOperationsUnit #DataBreach #PeopleSoft #CyberSecurity https://meterpreter.org/fbi-breach-shinyhunters-remote-operations-unit/?utm_source=mastodon&utm_medium=jetpack_social
FBI ShinyHunters Breach Hits Secret Hacking Unit
Information Security News

FBI ShinyHunters Breach Hits Secret Hacking Unit

The FBI ShinyHunters breach may expose staff of the FBI's Remote Operations Unit hacking team, via a claimed Oracle PeopleSoft zero-day. FBI confirms probe.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
IBM patched critical IBM FTM vulnerabilities in Financial Transaction Manager. Learn how these IBM FTM vulnerabilities impact systems and update immediately. #IBM #FTM #Cybersecurity #Infosec #PatchTuesday #Vulnerability https://securityonline.info/ibm-ftm-vulnerabilities-patch/?utm_source=mastodon&utm_medium=jetpack_social
Critical IBM FTM Vulnerabilities Expose Financial Systems to Attack
Daily CyberSecurity

Critical IBM FTM Vulnerabilities Expose Financial Systems to Attack

IBM patched critical IBM FTM vulnerabilities in Financial Transaction Manager. Learn how these IBM FTM vulnerabilities impact systems and update immediately.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately. #MongoDB #Cybersecurity #Vulnerability #Infosec #CVE https://securityonline.info/mongodb-driver-vulnerabilities-cve/?utm_source=mastodon&utm_medium=jetpack_social
Critical MongoDB Driver Vulnerabilities Require Immediate Patching
Daily CyberSecurity

Critical MongoDB Driver Vulnerabilities Require Immediate Patching

Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 4w ago
Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances. #Cisco #SecureBoot #CVE202620293 #UEFI #Cybersecurity https://securityonline.info/cisco-secure-boot-bypass-poc/?utm_source=mastodon&utm_medium=jetpack_social
Cisco Secure Boot Bypass Details and PoC Exploit Disclosed
Daily CyberSecurity

Cisco Secure Boot Bypass Details and PoC Exploit Disclosed

Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
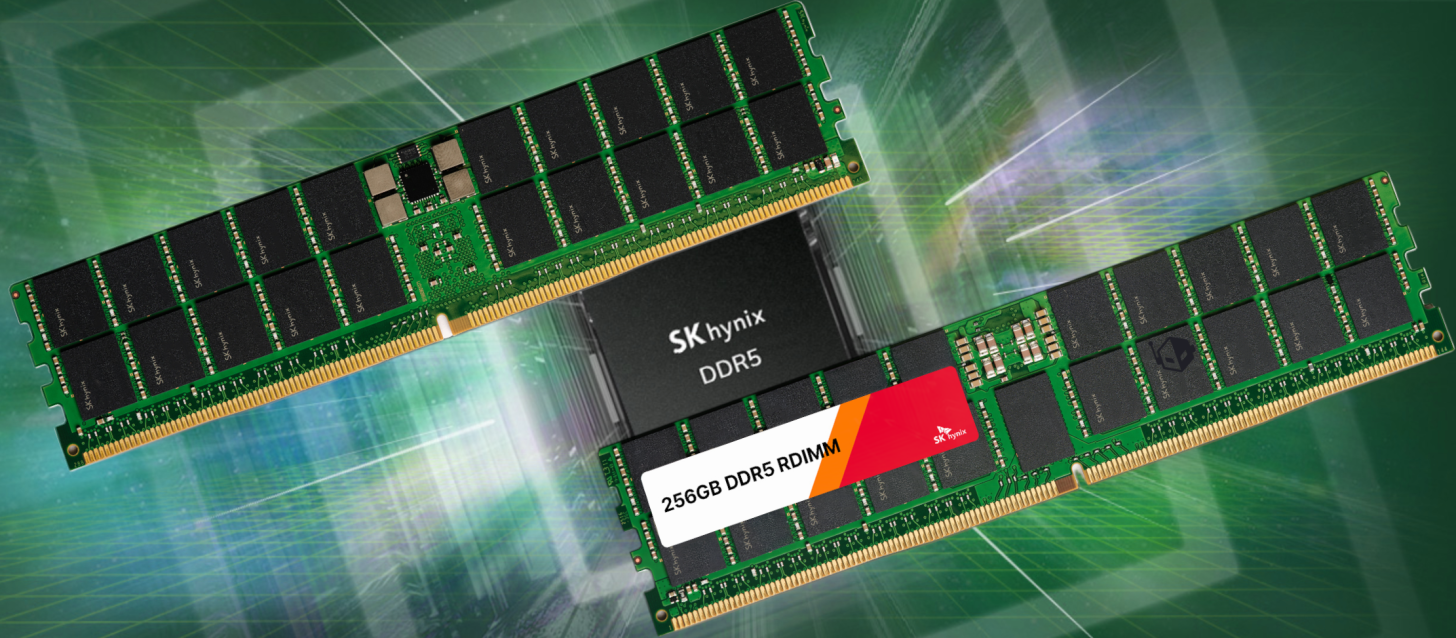
SK Hynix Reinforces Its Technological Supremacy South Korean memory titan SK Hynix recently reiterated at a prominent industry symposium that the artificial intelligence sector fundamentally cannot exist without advanced memory solutions. As the artificial intelligence landscape continually evolves, the voracious demand for specialized memory hardware will undoubtedly remain robust. Consequently, SK Hynix plans to relentlessly fortify its technological supremacy by leveraging cutting-edge memory architectures, an expanding network of global production hubs, and state-of-the-art research and development facilities. https://securityexpress.info/sk-hynix-memory-roadmap/?utm_source=mastodon&utm_medium=jetpack_social

SK Hynix Memory Roadmap: From HBM4E to Next-Gen HBF Tech
Tech News

SK Hynix Memory Roadmap: From HBM4E to Next-Gen HBF Tech

Discover the latest SK Hynix memory roadmap, featuring 12-layer HBM4E samples, innovative HBF technology, and massive global expansion plans in the US.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
A critical Shinobi vulnerability (CVE-2026-82448) uses a hardcoded child node key to reach the camera database unauthenticated. Patch and lock port 8288. #Shinobi #CVE202682448 #CCTV #Vulnerability #HardcodedKey #CyberSecurity #InfoSec https://meterpreter.org/shinobi-hardcoded-key-vulnerability/?utm_source=mastodon&utm_medium=jetpack_social
Shinobi Vulnerability: Hardcoded Key Exposes DB
Information Security News

Shinobi Vulnerability: Hardcoded Key Exposes DB

A critical Shinobi vulnerability (CVE-2026-82448) uses a hardcoded child node key to reach the camera database unauthenticated. Patch and lock port 8288.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes. #Pega #SAML #AuthenticationBypass #SSO #PegaPlatform #IAM #Vulnerability #PatchNow https://securityonline.info/pega-saml-authentication-bypass/?utm_source=mastodon&utm_medium=jetpack_social
Pega Platform SAML Authentication Bypass: Critical 9.5 Flaw Patched
Daily CyberSecurity

Pega Platform SAML Authentication Bypass: Critical 9.5 Flaw Patched

Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
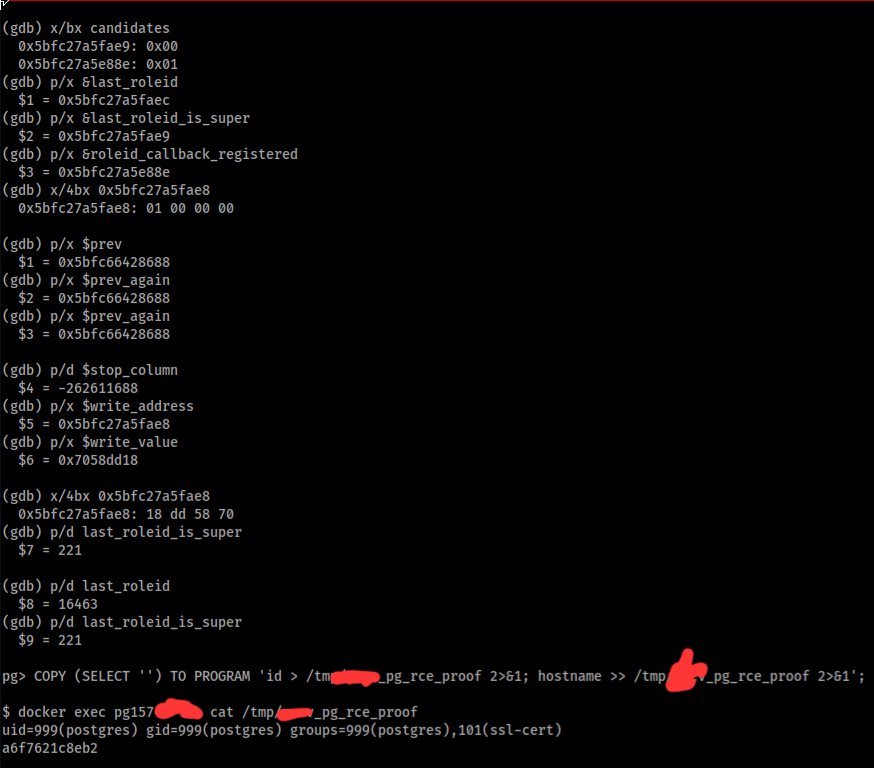
A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now. #PostgreSQL #CVE202615742 #RCE #Cybersecurity #DatabaseSecurity https://securityonline.info/postgresql-rce-vulnerability-cve-2026-15742/?utm_source=mastodon&utm_medium=jetpack_social
PostgreSQL RCE Vulnerability Details and PoC Disclosed
Daily CyberSecurity

PostgreSQL RCE Vulnerability Details and PoC Disclosed

A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Discover why Microsoft Word template crashes occur when third-party software populates documents. Learn about the Office version 2608 bug and temporary fixes. #MicrosoftWord #SoftwareBug #TechNews #Office365 #TemplateError https://securityonline.info/microsoft-word-template-crashes/?utm_source=mastodon&utm_medium=jetpack_social
Microsoft Word Template Glitch Causes Sudden Crashes
Daily CyberSecurity

Microsoft Word Template Glitch Causes Sudden Crashes

Discover why Microsoft Word template crashes occur when third-party software populates documents. Learn about the Office version 2608 bug and temporary fixes.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now. #WooCommerce #WordPressSecurity #CVE202627540 #Cybersecurity #InfoSec https://securityonline.info/woocommerce-wholesale-lead-capture-vulnerability/?utm_source=mastodon&utm_medium=jetpack_social
WooCommerce Wholesale Lead Capture Exploited in the Wild
Daily CyberSecurity

WooCommerce Wholesale Lead Capture Exploited in the Wild

Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Google Home MCP support lets AI agents like Claude control Nest and Matter devices via natural language, gated to the $20/mo Premium Advanced tier. #GoogleHome #MCP #AIagents #SmartHome #Claude #Anthropic #TechNews https://securityonline.info/google-home-mcp-support/?utm_source=mastodon&utm_medium=jetpack_social
Google Home Adds MCP Support for AI Agent Control
Daily CyberSecurity

Google Home Adds MCP Support for AI Agent Control

Google Home MCP support lets AI agents like Claude control Nest and Matter devices via natural language, gated to the $20/mo Premium Advanced tier.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
A critical Android Telecom vulnerability (CVE-2026-49881) allows remote code execution. Read the analysis and learn how to secure your device today. #Android #CVE202649881 #Cybersecurity #Infosec #ZeroDay https://securityonline.info/android-telecom-vulnerability-cve-2026-49881/?utm_source=mastodon&utm_medium=jetpack_social
securityonline.info
0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
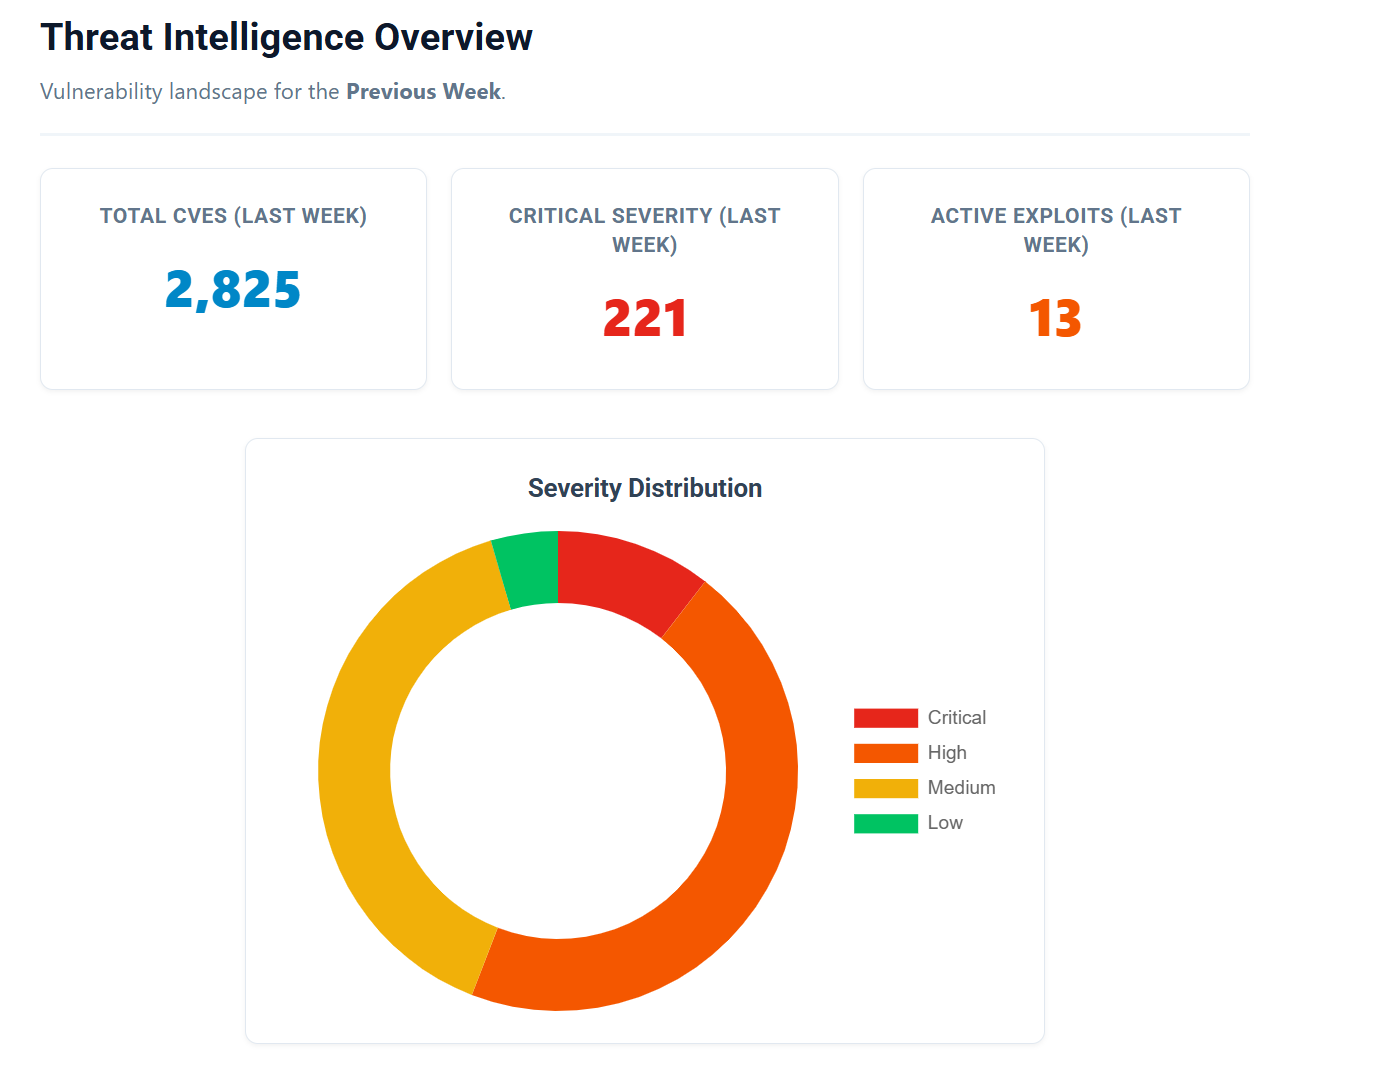
This weekly CVE report tracks 2,825 new flaws and 9 exploited vulnerabilities, verified against CISA KEV. WordPress, F5, Citrix and Check Point lead. #WeeklyCVEReport #ExploitedVulnerabilities #CISAKEV #WordPressSecurity #CitrixNetScaler #F5BIGIP #CheckPoint #ThreatIntel https://securityonline.info/weekly-cve-report-sept-21-27-2026/?utm_source=mastodon&utm_medium=jetpack_social
Weekly CVE Report: 2,825 New Flaws and 9 Exploited Bugs (Sept 21-27, 2026)
Daily CyberSecurity

Weekly CVE Report: 2,825 New Flaws and 9 Exploited Bugs (Sept 21-27, 2026)

This weekly CVE report tracks 2,825 new flaws and 9 exploited vulnerabilities, verified against CISA KEV. WordPress, F5, Citrix and Check Point lead.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
A critical Norwegian Cruise Line vulnerability allows attackers to clone RFID keycards. Mitigate CVE-2026-75907 to protect vessel and guest security. #NorwegianCruiseLine #CVE202675907 #RFID #Cybersecurity #Infosec #AccessControl https://securityonline.info/norwegian-cruise-line-vulnerability-cve-2026-75907/?utm_source=mastodon&utm_medium=jetpack_social
Norwegian Cruise Line Vulnerability Permits Keycard Replay
Daily CyberSecurity

Norwegian Cruise Line Vulnerability Permits Keycard Replay

A critical Norwegian Cruise Line vulnerability allows attackers to clone RFID keycards. Mitigate CVE-2026-75907 to protect vessel and guest security.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now. #wolfSSL #wolfSSLVulnerabilities #TLS #AuthenticationBypass #EmbeddedSecurity #Cryptography #IoTSecurity #PatchNow https://securityonline.info/wolfssl-5-9-4-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
wolfSSL 5.9.4 Fixes 10 Vulnerabilities, Including TLS Authentication Bypass Flaws
Daily CyberSecurity

wolfSSL 5.9.4 Fixes 10 Vulnerabilities, Including TLS Authentication Bypass Flaws

wolfSSL 5.9.4 patches 10 wolfSSL vulnerabilities, including TLS authentication bypass flaws CVE-2026-93302 and CVE-2026-89136. Upgrade now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Discover how the new iOS 27 Auto Lock feature protects your iPhone. This advanced anti-theft security automatically locks snatched devices to secure data. #iOS27 #AutoLock #iPhoneSecurity #AppleNews #AntiTheft http://securityonline.info/ios-27-auto-lock-iphone-security/?utm_source=mastodon&utm_medium=jetpack_social
securityonline.info
0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now. #Citrix #NetScaler #ZeroDay #RCE #CyberSecurity #VPN #watchTowr #PatchNow https://securityonline.info/citrix-netscaler-zero-day-rce/?utm_source=mastodon&utm_medium=jetpack_social
Citrix NetScaler Zero-Day RCE Flaws Exploited, Patches Released
Daily CyberSecurity

Citrix NetScaler Zero-Day RCE Flaws Exploited, Patches Released

Two Citrix NetScaler zero-day RCE flaws are under active exploitation. Citrix confirmed CVE-2026-88771 and CVE-2026-88772 and shipped patches. Update now.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Patch the critical T-Mobile 5G Box vulnerabilities today. Learn how WNC router flaws allow auth bypass and command injection, and secure your network. #TMobile5G #RouterSecurity #CVE202640854 #Cybersecurity #Vulnerability https://securityonline.info/t-mobile-5g-box-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
T-Mobile 5G Box Vulnerabilities Require Urgent Action
Daily CyberSecurity

T-Mobile 5G Box Vulnerabilities Require Urgent Action

Patch the critical T-Mobile 5G Box vulnerabilities today. Learn how WNC router flaws allow auth bypass and command injection, and secure your network.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 3w ago
Cisco patched 18 Secure Firewall vulnerabilities in FMC, ASA, and FTD, including critical unauthenticated root remote code execution flaws. Update now. #Cisco #SecureFirewall #FMC #ASA #FTD #CVE #RCE #NetworkSecurity #InfoSec #PatchNow https://securityonline.info/cisco-secure-firewall-vulnerabilities-september-2026/?utm_source=mastodon&utm_medium=jetpack_social
Cisco Patches 18 Secure Firewall Flaws, Several Root RCE
Daily CyberSecurity

Cisco Patches 18 Secure Firewall Flaws, Several Root RCE

Cisco patched 18 Secure Firewall vulnerabilities in FMC, ASA, and FTD, including critical unauthenticated root remote code execution flaws. Update now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
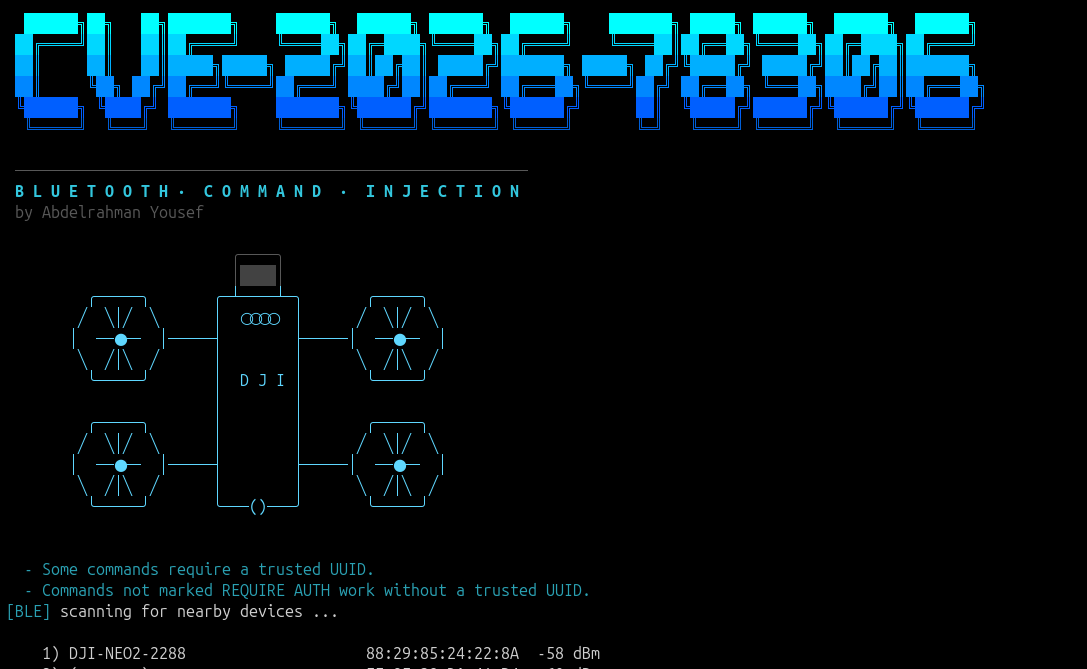
The DJI Bluetooth vulnerability CVE-2026-78306 lets a nearby attacker send unauthenticated DUML commands to 16 drone models. Update firmware now. #DJI #CVE202678306 #Bluetooth #DroneSecurity #DUML #CyberSecurity https://meterpreter.org/dji-bluetooth-vulnerability/?utm_source=mastodon&utm_medium=jetpack_social
DJI Bluetooth Vulnerability Hits 16 Drone Models
Information Security News

DJI Bluetooth Vulnerability Hits 16 Drone Models

The DJI Bluetooth vulnerability CVE-2026-78306 lets a nearby attacker send unauthenticated DUML commands to 16 drone models. Update firmware now.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
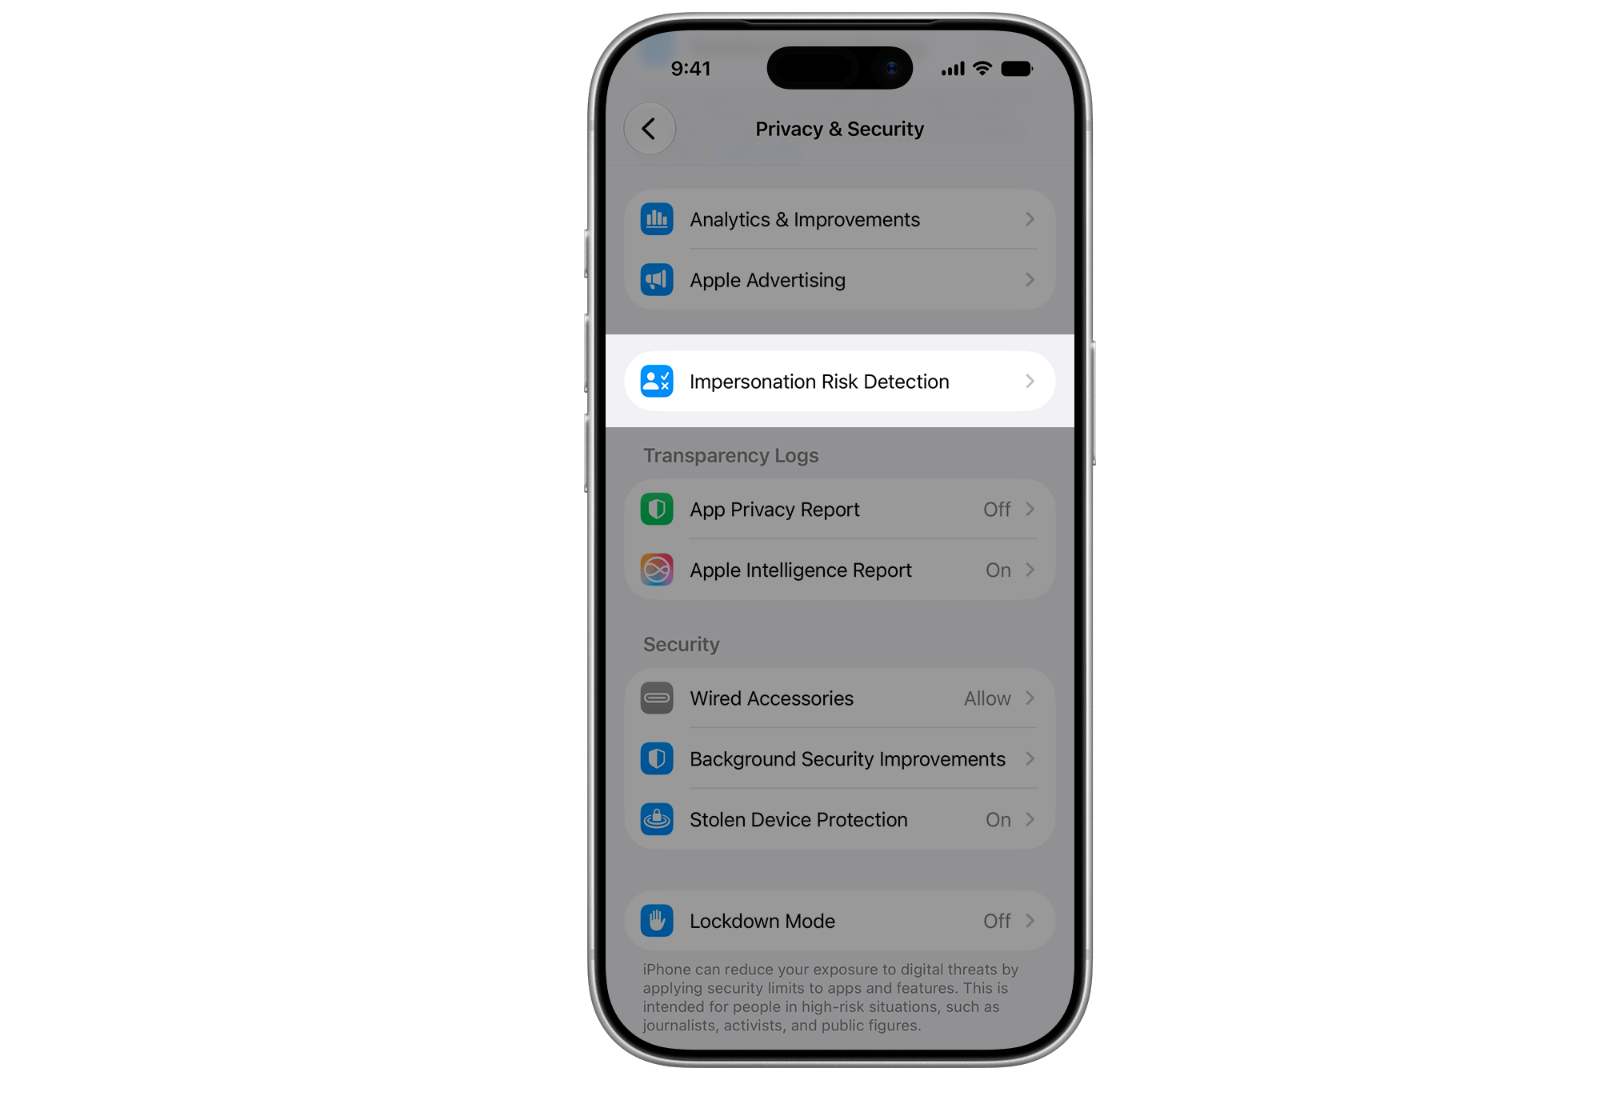
Discover how iOS 27 Trust Insights and Impersonation Risk Detection combat social engineering by analyzing behavioral context to stop scams. #iOS27 #TrustInsights #CyberSecurity #SocialEngineering #AppleNews https://meterpreter.org/ios-27-trust-insights/?utm_source=mastodon&utm_medium=jetpack_social
iOS 27 Trust Insights: Apple's Anti-Fraud Defense
Information Security News

iOS 27 Trust Insights: Apple's Anti-Fraud Defense

Discover how iOS 27 Trust Insights and Impersonation Risk Detection combat social engineering by analyzing behavioral context to stop scams.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 2w ago
Critical IBM MQ vulnerabilities allow remote code execution. Learn how CVE-2026-10747 and CVE-2026-10858 hit 10.0 CVSS and require urgent patching. #IBMMQ #CVE202610747 #CVE202610858 #Cybersecurity #Infosec https://securityonline.info/ibm-mq-vulnerabilities-cve-2026-10747/?utm_source=mastodon&utm_medium=jetpack_social
Critical IBM MQ Vulnerabilities CVE-2026-10747 Hit 10 CVSS
Daily CyberSecurity

Critical IBM MQ Vulnerabilities CVE-2026-10747 Hit 10 CVSS

Critical IBM MQ vulnerabilities allow remote code execution. Learn how CVE-2026-10747 and CVE-2026-10858 hit 10.0 CVSS and require urgent patching.

0
0
0
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 1w ago
Apple patched an exploited Apple zero-day vulnerability. Learn how this Apple zero-day vulnerability impacts devices and install emergency updates now. #Apple #iOS #macOS #CVE202686950 #ZeroDay #Cybersecurity #InfoSec https://securityonline.info/exploited-apple-zero-day-vulnerability-cve-2026-86950/?utm_source=mastodon&utm_medium=jetpack_social
Exploited Apple Zero-Day Vulnerability Patched
Daily CyberSecurity

Exploited Apple Zero-Day Vulnerability Patched

Apple patched an exploited Apple zero-day vulnerability. Learn how this Apple zero-day vulnerability impacts devices and install emergency updates now.

0
0
1
0
Open post
Daily CyberSecurity @DailyCyberSecurity@infosec.exchange
· 4w ago
The WeChat zero-click worm WeWorm hijacks accounts through unanswered calls on both Android and iOS. Tencent has fully patched the flaw. #WeWorm #WeChat #ZeroClick #Tencent #Calif #MobileSecurity #RCE https://securityexpress.info/weworm-wechat-zero-click-worm/?utm_source=mastodon&utm_medium=jetpack_social
WeWorm: Zero-Click Worm Hijacks WeChat via Calls
Tech News

WeWorm: Zero-Click Worm Hijacks WeChat via Calls

The WeChat zero-click worm WeWorm hijacks accounts through unanswered calls on both Android and iOS. Tencent has fully patched the flaw.

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal
  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 22:31:23 UTC