#wordpresssecurity

13 posts · Last used 9d

WordPress 6.7.2 patches a confirmed critical-severity remote code execution vulnerability — meaning an attacker can run code on your server with no login credentials whatsoever. In my view, this is not optional. If you have not updated yet, do it now. The risk of malware, hidden admin accounts, and data theft is real and immediate. #WordPress #Security #WebDev #WordPressSecurity #WPGuy https://wpguy.uk/blog/wordpress-672-critical-rce-patch-you-must-apply-now/
0
0
0
0
If your site runs Elementor Pro with a file upload field in any form, patch immediately. Versions 4.2.1 and below contain a critical flaw that allows complete site takeover — no account, no password, no interaction required. The upload field your visitors use daily is the attack vector. I recommend updating now without delay. #WordPress #Elementor #WebSecurity #WordPressSecurity #SecurityHardening https://wpguy.uk/blog/elementor-pro-file-upload-vulnerability-patch-now/
1
0
0
0
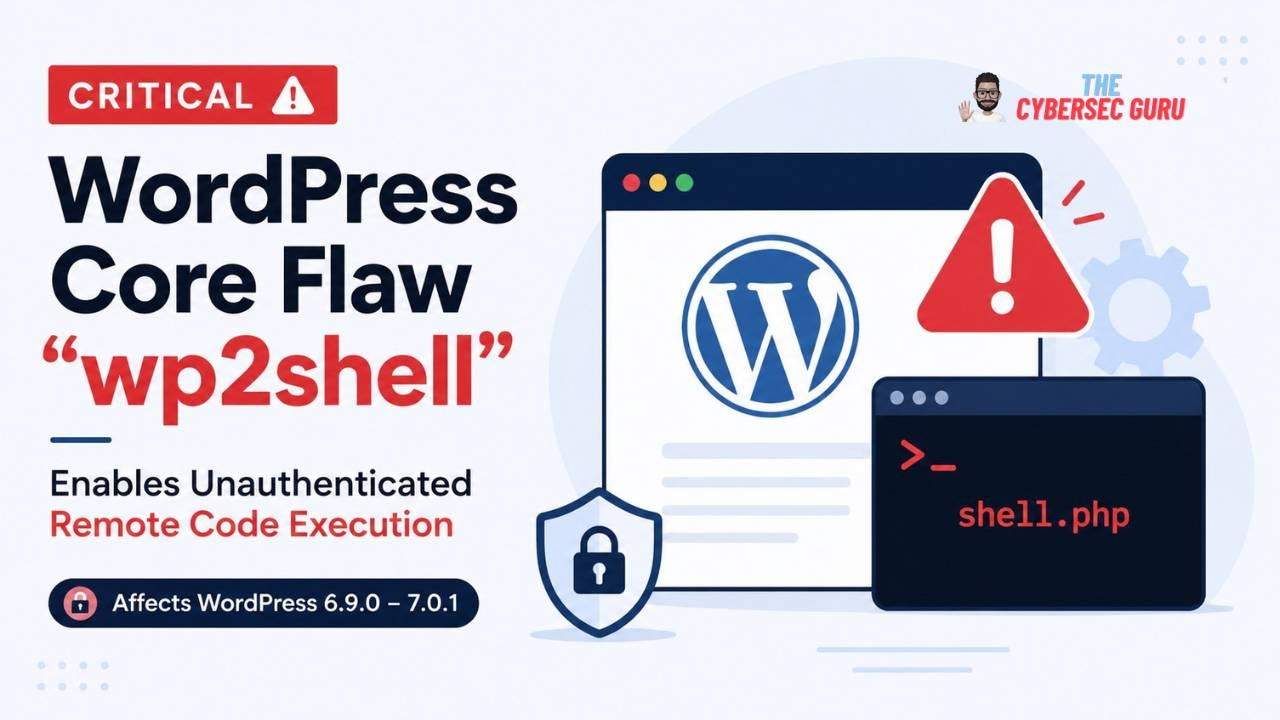
A critical WordPress RCE vulnerability, wp2shell, was disclosed on 17 July 2026. It chains a REST API route confusion flaw with an SQL injection in WP_Query — no login required, no plugin involved. If my site were unpatched, an attacker could take full control. Check your WordPress version now. #WordPress #Security #WordPressSecurity #WebSecurity #RCE https://wpguy.uk/blog/is-your-wordpress-site-exposed-to-the-wp2shell-remote-code-execution-flaw/
0
0
0
0
🚨 CRITICAL: WordPress Core "wp2shell" RCE A single anonymous HTTP request can lead to Remote Code Execution on vulnerable WordPress Core installations. ⚠️ No plugins. ⚠️ No themes. ⚠️ No authentication required. Tracked as: 🔴 CVE-2026-63030 (REST API Batch Route Confusion → RCE) 🔴 CVE-2026-60137 (Facilitated SQL Injection) Affected versions • WordPress 6.9.0–6.9.4 • WordPress 7.0.0–7.0.1 ✅ Update immediately to WordPress 6.9.5 or 7.0.2. Due to the severity, WordPress has enabled forced automatic security updates for affected installations. 🔗 Full technical analysis: https://thecybersecguru.com/news/wordpress-core-rce-wp2shell/ #WordPress #WordPressSecurity #wp2shell #CVE202663030 #CVE202660137 #RCE #RemoteCodeExecution #SQLInjection #RESTAPI #CyberSecurity #InfoSec #WebSecurity #WebsiteSecurity #PatchNow #ThreatIntelligence #BlueTeam #SOC #Linux #PHP #ZeroDay #SecurityResearch #SysAdmin #DevSecOps
35
4
57
0
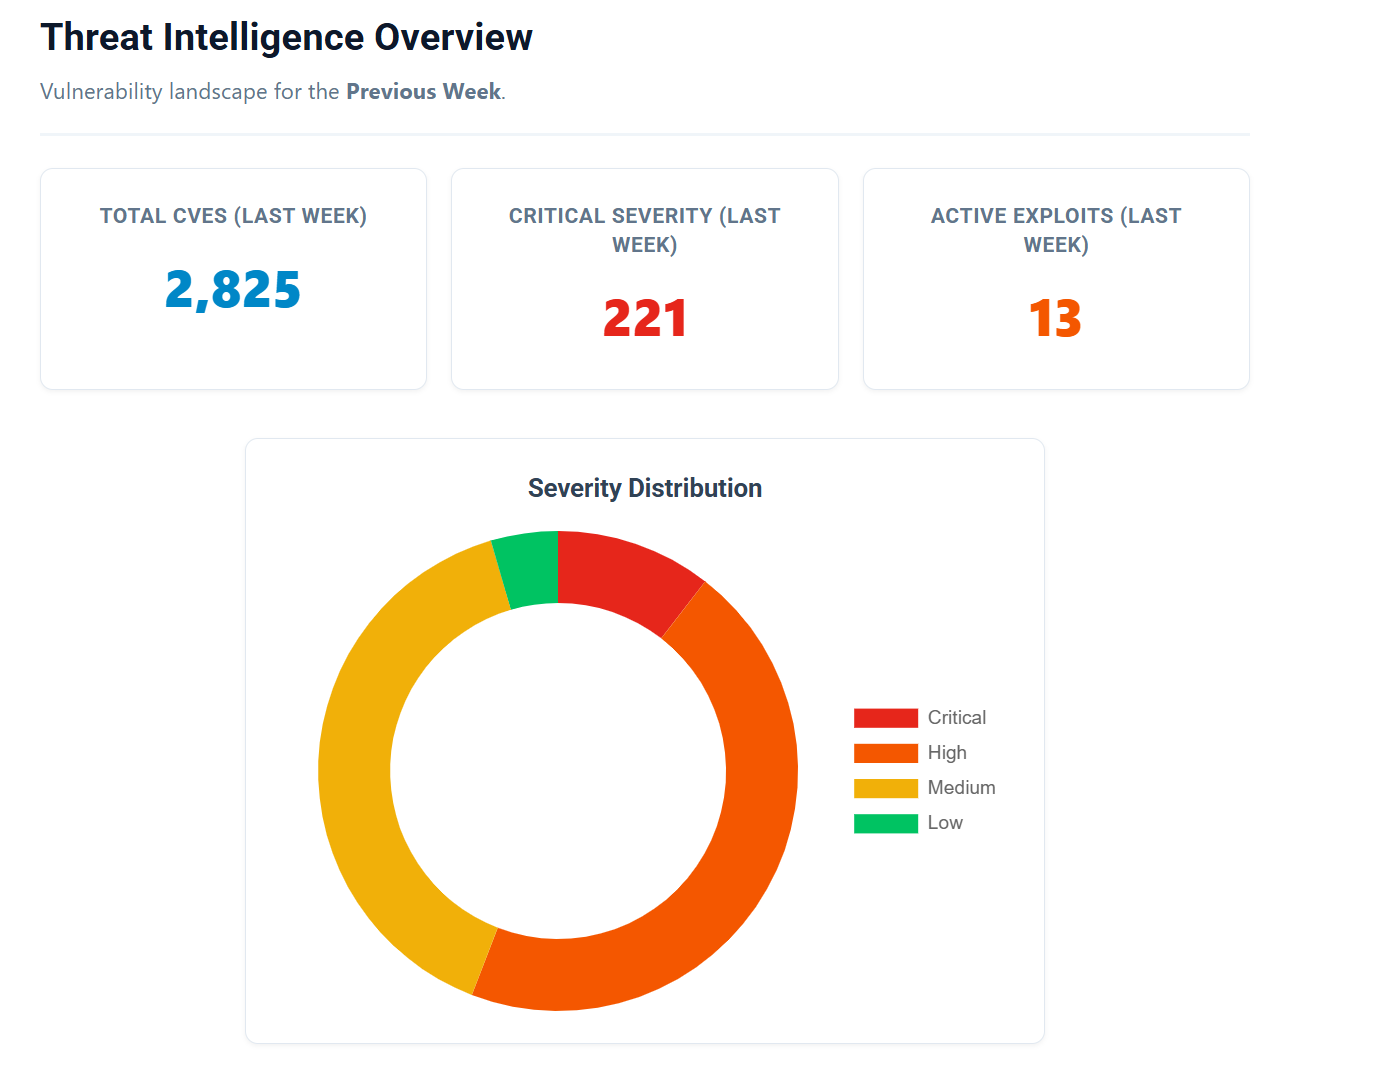
250+ WordPress plugin vulnerabilities are disclosed every week in 2026 — that is not a spike, it is the baseline. What concerns me most is that 43% require no login to exploit. Automated scanners find vulnerable sites before most owners even know a patch exists. This is the environment I work in daily, and it demands a serious approach to hardening. #WordPress #WebSecurity #WordPressSecurity #PluginSecurity https://wpguy.uk/blog/wordpress-plugin-vulnerabilities-are-rising-what-business-owners-must-know/
0
0
0
0
Three plugins I keep a close eye on — WPForms (6M+ sites), WPvivid, and Smart Slider 3 — all had vulnerabilities publicly disclosed in June 2026. Patches are available for all three. If you have not updated recently, your site is likely exposed. Worth checking your versions today. #WordPress #WordPressSecurity #WPForms #PluginUpdates #WebsiteSecurity https://wpguy.uk/blog/wordpress-plugin-vulnerabilities-in-june-2026-what-site-owners-must-know/
0
0
0
0
You've seen all posts