#cisco

50 posts · Last used 15d

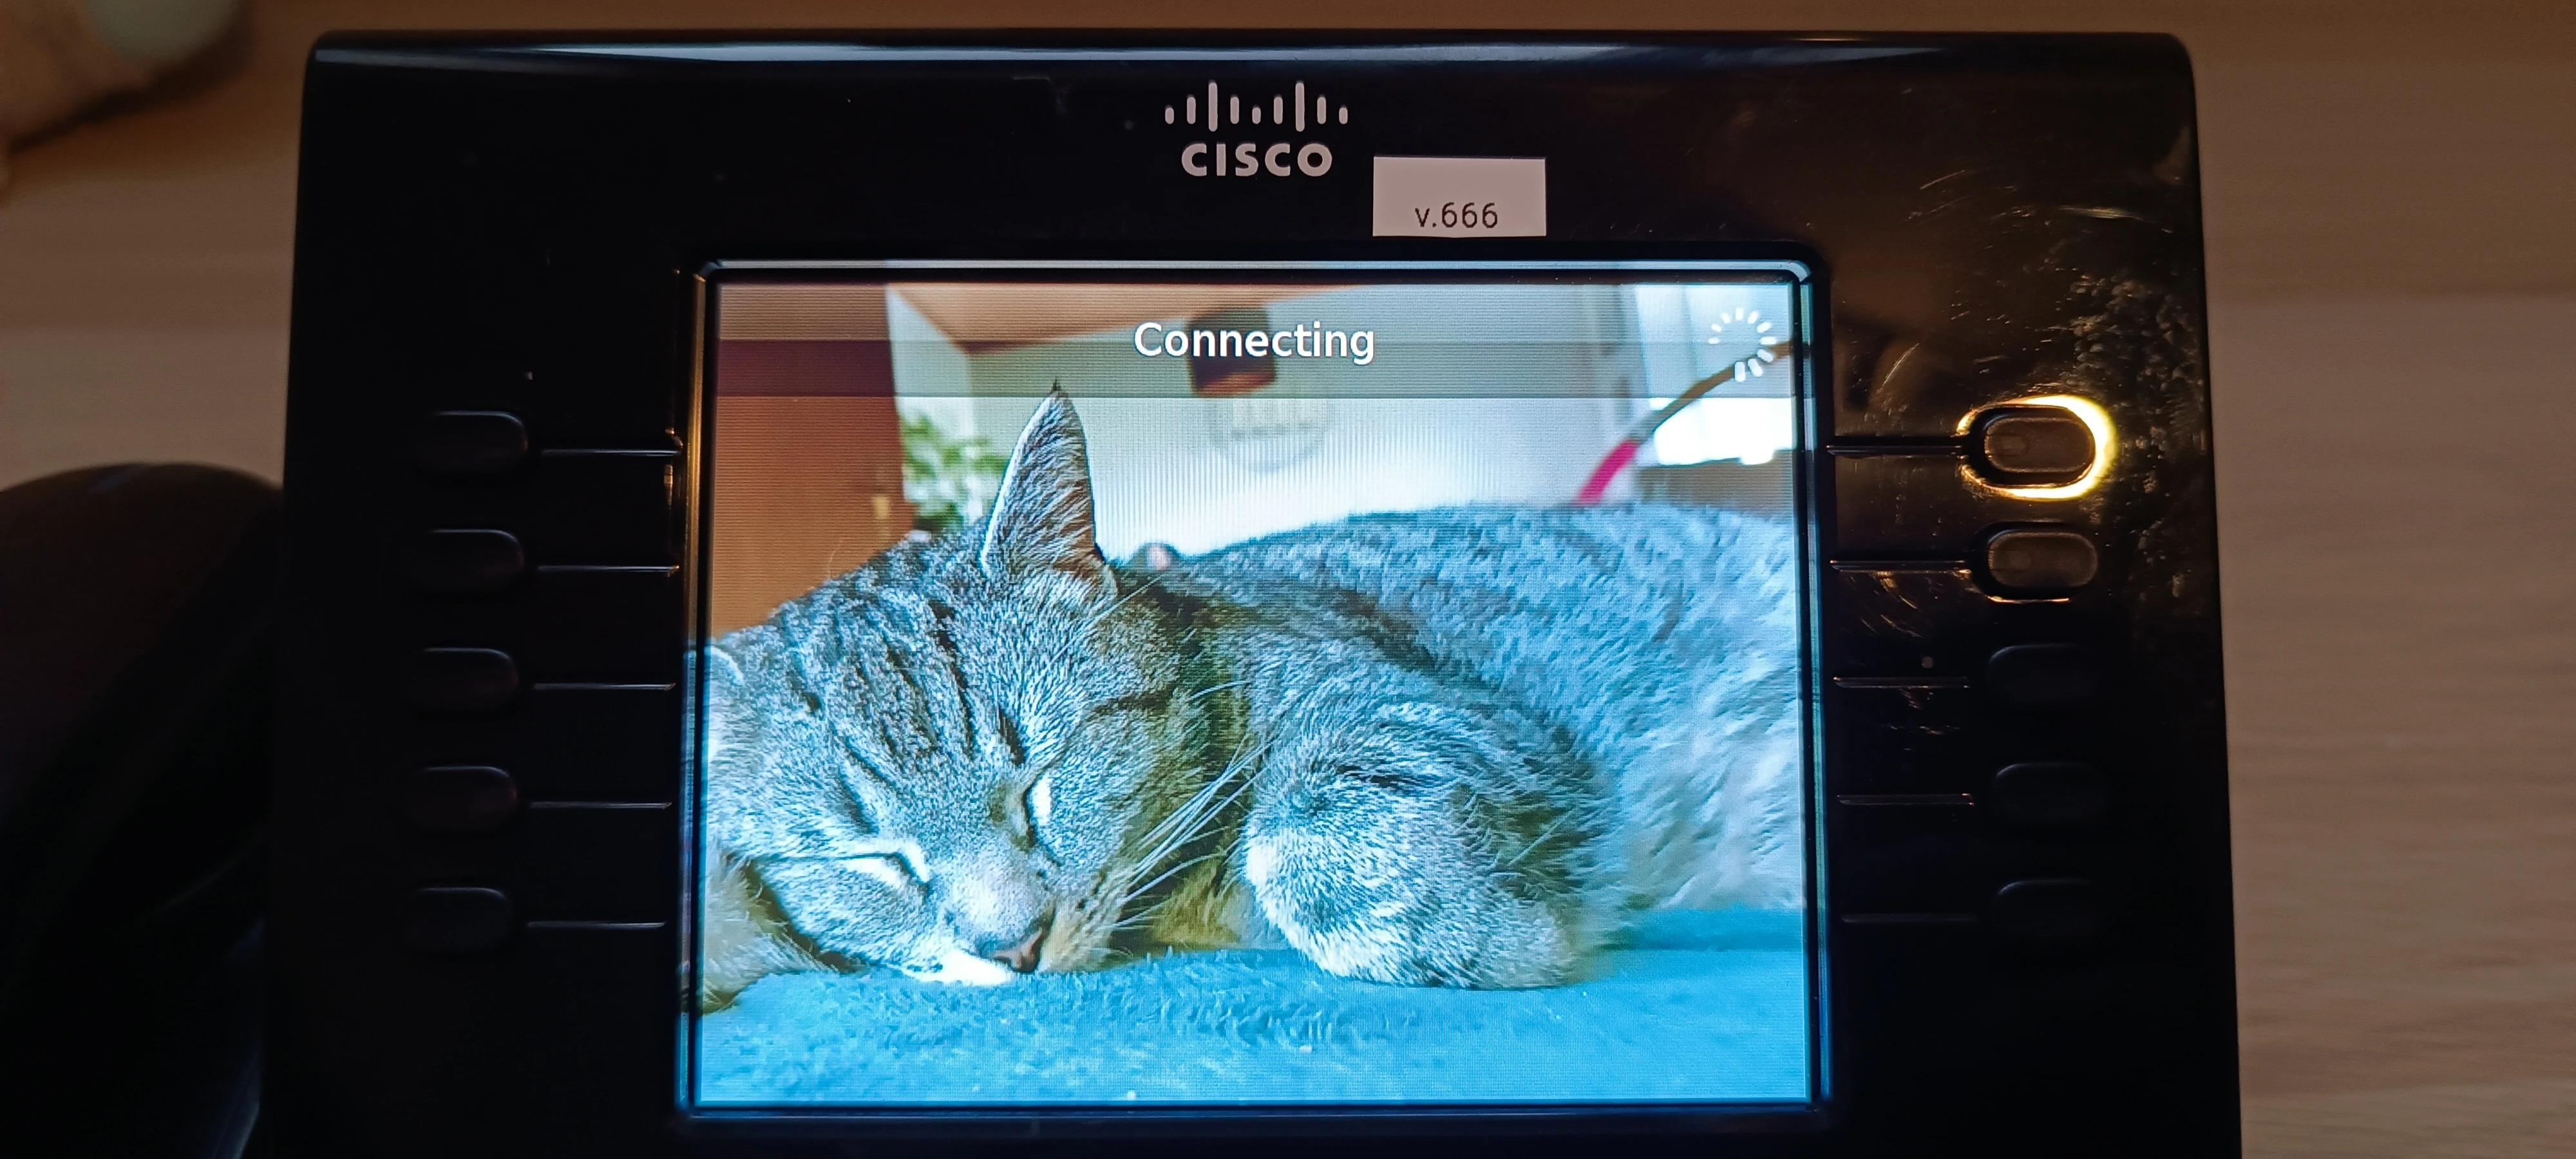
I bought a used Cisco CP-9951 for about €35. Three days later, it was running DOOM natively. :D ARMv6, MontaVista Linux, /dev/fb1, the real Cisco keypad, local sound, persistent under Applications → Doom — and after installation it even works with the Ethernet cable unplugged. https://www.dennishilk.com/museum/home-computing-lab/field-notes/field-note-7/ Source/Release: https://github.com/dennishilk/cisco9951-doom #DOOM #Linux #Retrocomputing #HardwareHacking #Homelab #Cisco “Three days later, it was running DOOM natively.” bleibt einfach herrlich. :DD
6
0
6
0
New. Cisco: “Keep going, bro. You’ve got this!” A data-driven look at how adversaries are weaponizing AI https://blog.talosintelligence.com/keep-going-bro-youve-got-this-a-data-driven-look-at-how-adversaries-are-weaponizing-ai/ @TalosSecurity@mstdn.social More: "Talos said guardrails 'did not provide much protection', and that it encountered no sophisticated encoding or evasion techniques. Where guardrails did engage, they achieved little, and the pattern held across models and platforms rather than affecting any single vendor." Infosecurity-Magazine: Cisco: Cybercriminals Bypass AI Safety Controls by Splitting Malicious Tasks Across Multiple Sessions https://www.infosecurity-magazine.com/news/talos-attackers-split-tasks-evade/ #infosec #Cisco #threatresearch #cybercrime
0
0
0
0
There are two new advisories from Cisco, one addressing a critical vulnerability that was first published on March 4: CRITICAL: CVE-2026-20079: Cisco Secure Firewall Management Center Software Authentication Bypass Vulnerability https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-onprem-fmc-authbypass-5JPp45V2 The second is a high-severity vulnerability that was first published yesterday: CVE-2026-20316: Cisco Secure Firewall Management Center Software Static Credential Vulnerability https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-static-cred-BET3Cjh @TalosSecurity@mstdn.social #infosec #vulnerability #Cisco
0
0
0
0
Could it be considered ironic that... an internet search for "Cisco china theft" doesn't show any results of the Chinese dictatorship stealing Cisco's hardware designs which gave the CCP regime a leg up to control the "cyberspace" and helped it develop its repressive "Great firewall of China" (and also aided CCP's foreign intrusive "intelligence" gathering...) and instead the search now brings up only lawsuits claiming Cisco aided the dictatorship in "jailing and torturing" its critics... 🤷🏻‍♂️ The wonders of "Free World" internet in this era! And Viva colaboración with hostile dictatorships! #cisco #ccp #china #ironyisntdead
0
0
0
0
🚨 BREAKING: If you manage Cisco firewalls, stop what you're doing and check this. Cisco has confirmed active exploitation of CVE-2026-20316, a hardcoded credentials flaw in Secure Firewall Management Center (FMC). ⚠️ No authentication required. ⚠️ No workaround available. ⚠️ Attackers can remotely log in using a built-in low-privileged account and potentially chain additional vulnerabilities for greater impact. Cisco has released hotfixes, and CISA has already added the flaw to its Known Exploited Vulnerabilities (KEV) Catalog. Full breakdown, affected versions, IoCs, and patch guidance👇 https://thecybersecguru.com/news/cisco-fmc-cve-2026-20316-hardcoded-credentials-active-exploitation/ #CyberSecurity #Cisco #CVE202620316 #Infosec #BlueTeam #Firewall #ZeroDay
0
0
2
0