#peoplesoft

3 posts · Last used 11d

Google reports active exploitation of CVE-2026-35273 in Oracle PeopleSoft PeopleTools by UNC6240, linked to ShinyHunters. Encoded requests evade WAF rules to deploy JSP webshells via the Environment Management Hub, enabling persistent access. Prioritize patching and compromise hunting. #OracleSecurity #PeopleSoft #ThreatIntel https://cyberworldops.eu/en/encoded-requests-let-shinyhunters-linked-attackers-breach-oracle

0
0
0
0
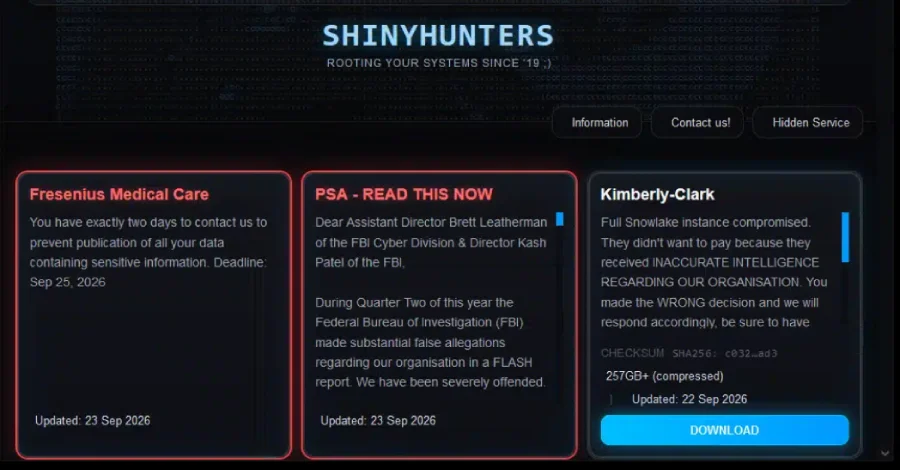
⚠️ ShinyHunters claims it hacked 100 orgs by exploiting an Oracle PeopleSoft 0-day 「 A spokesperson for the cybercrime crew on Thursday told The Register that they exploited CVE-2026-35273 to break into the university’s PeopleSoft system and steal 40 GB of personal data and billing records belonging to hundreds of thousands of current and former students 」 https://www.theregister.com/cyber-crime/2026/06/11/shinyhunters-claims-oracle-peoplesoft-0-day-hit-100-orgs/5254443 #ShinyHunters #PeopleSoft #oracle #CVE202635273
0
0
1
0
You've seen all posts