Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Andreas

@ePD5qRxX@mastodon.online
mastodon 4.8.0-nightly.2026-10-06
  • Open on mastodon.online

I'm here for / interested in: Physics, climate (crisis), astronomy / space, it / infosec, collapse of crypto scam, dogs, news, strange stuff in general, ... - or just everything 🤓

#fcknzs #fckafd #niewiederistjetzt
Slava Ukraini! 🇺🇦

77 Followers
416 Following
33 Posts
Joined October 26, 2022
Open post
Andreas @ePD5qRxX@mastodon.online
· 3mo ago
Replying to
@cstross@wandering.shop Aussie fans sing “We’re on a bender, Donald Trump is a sex offender” https://www.reddit.com/r/DanLeBatardShow/comments/1u5g0rq/aussie_fans_sing_were_on_a_bender_donald_trump_is/
reddit.com
63
1
40
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 3mo ago
Replying to
@helenasteinhaus@kolektiva.social Spätestens wenn sie feststellen, dass das Deutschlandticket mehr als 50€ kostet und die Betroffenen, auf dem Papier, damit mehr Geld bekommen als jetzt, wird das wieder eingestampft. Dann aber vermutlich ersetzt durch eine Bezahlkarte 2.0 für den ÖPNV 🤮
4
1
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 3mo ago
Replying to
@XR_Nuernberg_sunny2@mstdn.social https://media.ccc.de/v/tdf5-210-privacy-by-lying @evawolfangel@chaos.social
media.ccc.de
3
6
2
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 3mo ago
Replying to

@boll@norden.social

Kommentar auf der Spendenseite:

Sie steht der Familie sehr nahe und ist die Lebensgefährtin eines Bruders der Verstorbenen.

@FlippoFlip@norden.social

3
1
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 3mo ago
Replying to
@cwebber@social.coop And @adamw@fosstodon.org for the research.
4
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 3mo ago
Replying to

@helenasteinhaus@kolektiva.social

Der Generalverdacht, dass Bürgergeldempfänger alles auch Schwarzfahrer sind:

Außerdem argumentieren die Befürworter, dass die Justiz durch weniger Verfahren wegen Schwarzfahrens entlastet würde.

...passt perfekt ins Bild.

2
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 6mo ago
Replying to
@wrdlbrmpft@social.tchncs.de Wenn schon zahlen, dann direkt für das Original (und den Datenlieferanten für WetterOnline) -> WarnWetter von @DeutscherWetterdienst@social.bund.de
6
0
2
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to
@bkastl@mastodon.social Vielleicht weil Denic das DNSSEC kaputt gemacht hat? https://news.ycombinator.com/item?id=48027897 https://www.reddit.com/r/sysadmin/comments/1t4qr6h/dns_issues_for_de_tld_servfail/ https://status.denic.de/
reddit.com
4
7
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to

@anton

Federal Reserve notes are a blend of 25 percent linen and 75 percent cotton. Currency paper has tiny red and blue synthetic fibers of various lengths evenly distributed throughout the paper.

https://www.uscurrency.gov/about-us/currency-facts

@michael_w_busch

uscurrency.gov
4
2
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to
@samy_crypto@mastodon.social Da ging es um die "originale" Windows-Applikation KeePass. Die verschlüsselte Datenbank selbst war und ist sicher. Und zur erwähnten Lücke. Wenn ein Angreifer an einen Memory-Dump kommt/erstellen kann, habe ich ganz andere Probleme. Und langsam ist zumindest bei der genannten Lücke nicht korrekt. Die wurde Anfang/Mitte Mai bekannt und Anfang Juni gab es eine gefixte Version. Weniger als 30 Tage schaffen nicht viele - schon gar nicht bei einer Lücke mit so niedrigem Score (7.5)
4
2
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to
@kristoff Why do something that doesn't work, solves nothing, allows tracking and implements a system that is just one step away of the Chinese social score system - in an environment where Nazis/right wing parties are on the rise?
2
18
1
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 6mo ago
Replying to

@swelljoe

wcurl, curl-wrapper that comes bundled with curl since 8.14, does that https://curl.se/wcurl/manual.html

curl.se

wcurl - How To Use

2
4
1
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 7mo ago
Replying to
@iampytest1 I would call them a*sholes 🤷‍♂️ @ChristineMalec
2
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 4mo ago
Replying to
@sixtus@mastodon.social Und schafft allein damit ~$500 Millionen pro Jahr in die Stadtkasse https://www.youtube.com/watch?v=m4BIv5ebu_M&t=48
1
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to
@alexanderkjall https://infosec.exchange/@wdormann/116495106231293342
infosec.exchange

Will Dormann: "What went wrong with this case? Theori appear to…" - Infosec Exchange

1
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 6mo ago
Replying to
@Aglaia89@norden.social Das Web Archive hat im Januar das erste Mal dazu einen Snapshot: https://web.archive.org/web/20260105214829/https://www.gesetze-im-internet.de/wehrpflg/__2.html Davor gibt es noch einen am 30. November ohne Ergänzung: https://web.archive.org/web/20251130153859/https://www.gesetze-im-internet.de/wehrpflg/__2.html #Wehrpflicht #Freizügigkeit
web.archive.org

§ 2 WPflG - Einzelnorm

1
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 23mo ago
Replying to

@janboehm@edi.social

Just in case...

Er könne diese Fressen einfach nicht mehr sehen, soll Lindner gerufen haben.

Quelle (Zeit Online): https://archive.is/97FiD

archive.is
4
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 12mo ago
Replying to
@haubles@hachyderm.io There's also this thread with updates: https://mastodon.iftas.org/@iftas/115322867312262878 @iftas@mastodon.iftas.org
mastodon.iftas.org

IFTAS: "⚠️ SW-ISAC Advisory A Russian network creating h…" - IFTAS

1
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 30mo ago
Replying to
@AstroKatie https://astrodon.social/@ThomasConnor/112163114528873020
astrodon.social
1
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to

@bkastl@mastodon.social

Let's Encrypt has resumed issuance. Due to an issue with the cross-signed certificate from our Generation X root to our new Generation Y root, all issuance has been switched back to our Generation X root certificate. This affects our "tlsserver" and "shortlived" ACME certificate profiles.

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 7mo ago
Replying to
@xinit@mastodon.coffee This might actually be Dianna, but (currently) not active :/ @dianna@mas.to
0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 9mo ago
Replying to
@stux@mstdn.social And every time a different clan member of the orange war criminal gets the bounty...
0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 4mo ago
Replying to
@jedimb@mastodon.gamedev.place Most likely nothing. At least it is not an officially documented URL parameter https://duckduckgo.com/duckduckgo-help-pages/settings/params @eniko@mastodon.gamedev.place
How To Use URL Parameters To Change Your DuckDuckGo Search Settings - DuckDuckGo Help Pages
duckduckgo.com

How To Use URL Parameters To Change Your DuckDuckGo Search Settings - DuckDuckGo Help Pages

DuckDuckGo doesn’t track you. That’s the DuckDuckGo privacy policy in a nutshell.

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to

@holgerpatzelt@mastodon.world

...wurde gegen den Rat einschlägiger Expert*innen...

Aber ein Holger weiß das natürlich besser... 🤷‍♂️

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 7mo ago
@rebane2001 @bucketchallenge one more open S3 bucket ⬆️
0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 6mo ago
Replying to
@Reaverz3r0@mastodon.social It is explained in detail on the linked website -> "The Attack: How it works"
0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to

@jrp

Specifically, edit your grub (or whatever you use to load your kernel) configuration to have one of the following arguments: initcall_blacklist=algif_aead_init initcall_blacklist=af_alg_init initcall_blacklist=crypto_authenc_esn_module_init

https://infosec.exchange/users/wdormann/statuses/116496097678724677

#copyfail

infosec.exchange
0
2
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 4mo ago
Replying to

@GossiTheDog@cyberplace.social

Theoretically, we could leverage this design to leak ASLR by progressively overwriting pointers byte by byte. In this post, we discuss the exploitation technique assuming ASLR has already been bypassed.

Based on that ASLR is "just" a nuisance and not an actual show stopper 🤔

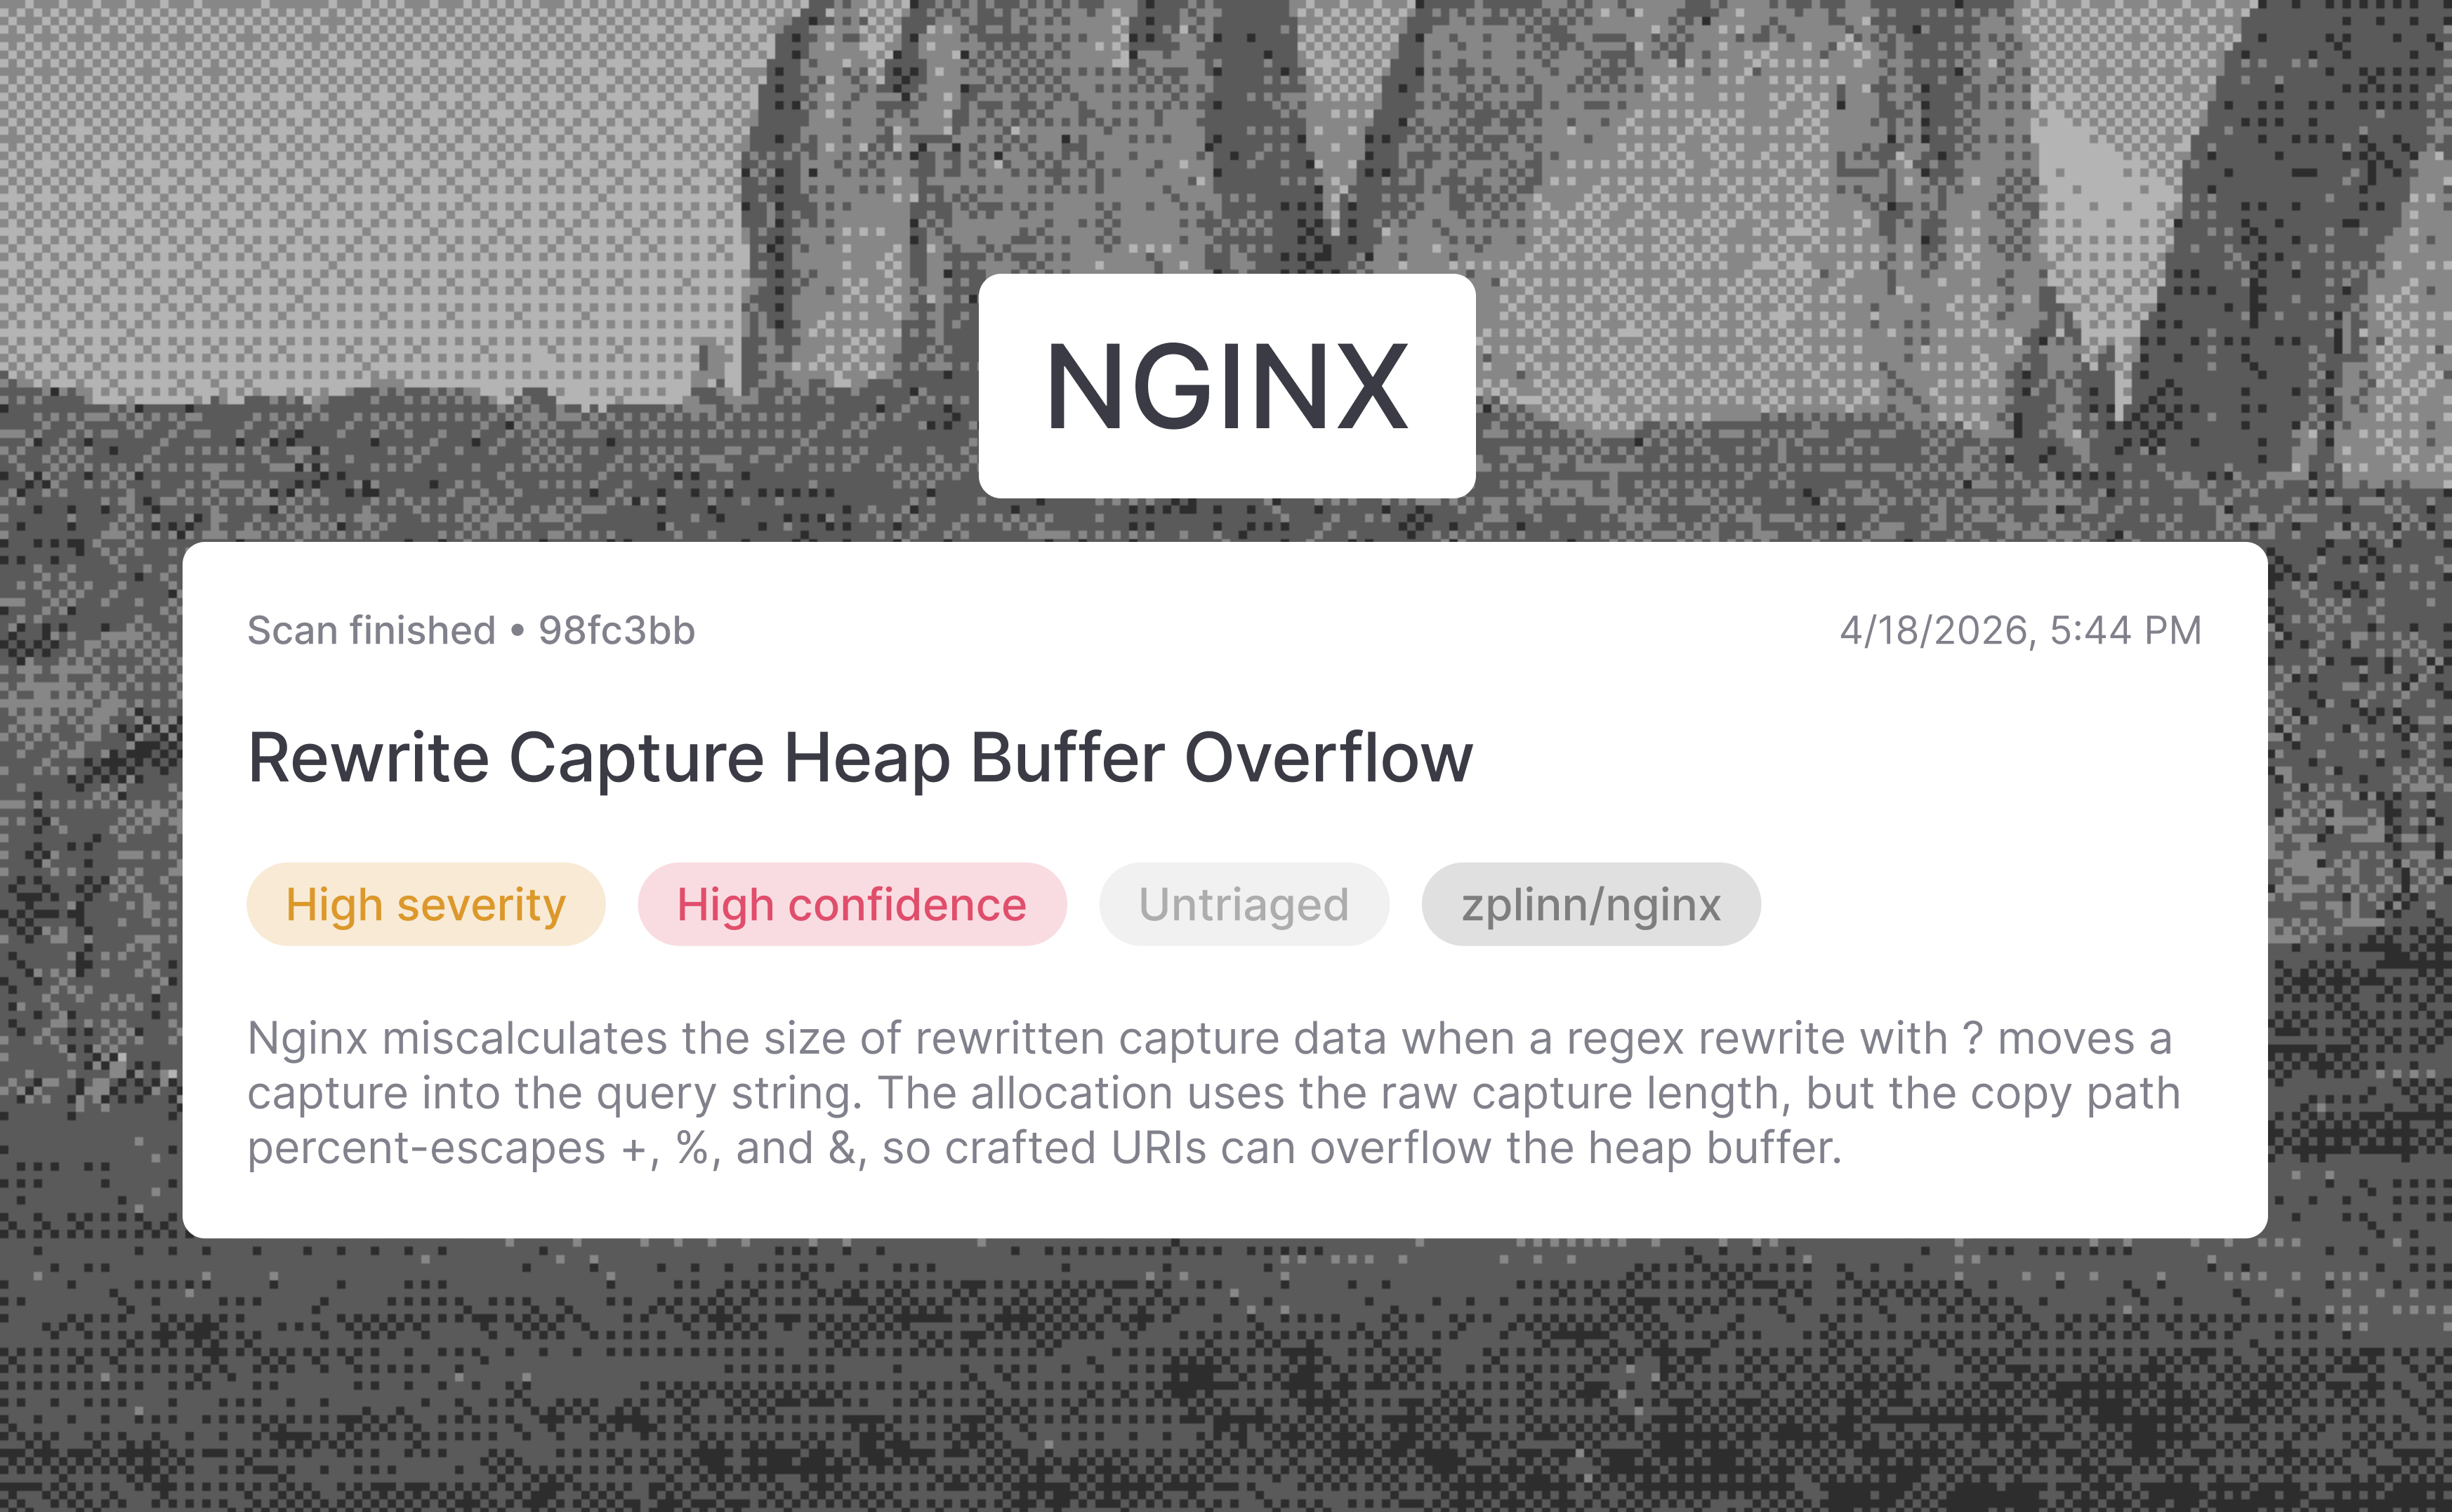
https://depthfirst.com/research/nginx-rift-achieving-nginx-rce-via-an-18-year-old-vulnerability

NGINX Rift: Achieving NGINX Remote Code Execution via an 18-Year-Old Vulnerability | depthfirst
depthfirst.com

NGINX Rift: Achieving NGINX Remote Code Execution via an 18-Year-Old Vulnerability | depthfirst

We used the depthfirst system to analyze the NGINX source code, and it autonomously discovered 4 remote memory corruption issues, including a critical heap buffer overflow introduced in 2008. We further investigated the exploitability of the issues, and developed a working proof of concept demonstrating RCE with ASLR off. If you use rewrite and set directives in your NGINX configuration, you

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 32mo ago
Replying to
@ipg@wetdry.world https://oisaur.com/@renchap/111948489205925124 @Gargron@mastodon.social
oisaur.com

Renaud Chaput: "@GossiTheDog@cyberplace.social here are my plans …" - Oisaur

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to

@bradr@infosec.exchange

Let's Encrypt has resumed issuance. Due to an issue with the cross-signed certificate from our Generation X root to our new Generation Y root, all issuance has been switched back to our Generation X root certificate. This affects our "tlsserver" and "shortlived" ACME certificate profiles.

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to

@hnapel

Are there different postmortems? 🤔

Our Trust Operations investigation found that the threat actor used the compromised analyst endpoint to access DigiCert's internal support portal

...which allowed them to request EV certificates.

Their CA was not affected.

https://bugzilla.mozilla.org/show_bug.cgi?id=2033170

bugzilla.mozilla.org

2033170 - DigiCert: Misissued code signing certificates

RESOLVED (dcbugzillaresponse) in CA Program - CA Certificate Compliance. Last updated 2026-07-20.

0
0
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 5mo ago
Replying to
@samy_crypto@mastodon.social Definiere "KeePass". Es gibt viele kompatible Apps die mit der Datenbank zurecht kommen.
0
1
0
0
Open post
Andreas @ePD5qRxX@mastodon.online
· 6mo ago
Replying to
@zyx And that response is why exactly useful for me, Joe or anyone else?
0
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 02:09:46 UTC