Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

alexanderkjall

@alexanderkjall@mastodon.social
mastodon 4.8.0-nightly.2026-10-06
  • Open on mastodon.social

Security Engineer by day
Crustacean by night

0 Followers
0 Following
9 Posts
Joined October 27, 2022
GitHub:
https://github.com/alexanderkjall/
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 5mo ago
Boosted by @ferrix@mastodon.online
Today I have spent way too much time handling the https://copy.fail situation #copyfail The persons who discovered it didn't notify the distribution security list, so no patched kernels was available for people to install when they released it. But they did have time to write an exploit, and thought it was a good idea to distribute that on day one, before vendors had time to provide patches. I'm not very impressed with xint.io, I guess it's the marketing department that runs the show.
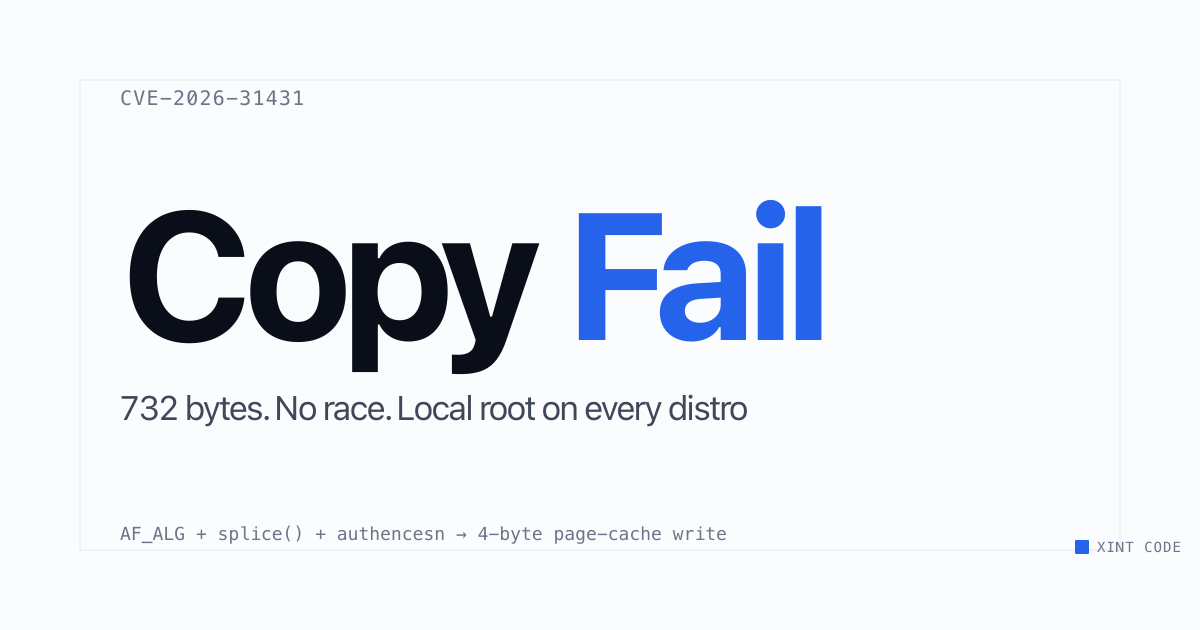
Copy Fail — 732 Bytes to Root
Xint

Copy Fail — 732 Bytes to Root

CVE-2026-31431. 100% Reliable Linux LPE — no race, no per-distro offsets, page-cache write that bypasses on-disk file-integrity tools and crosses containers. Found by Xint Code.

227
64
210
1
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 17mo ago

Today my #rust compiler told me "expected future, found a different future".

And I'm like: me too buddy, me too

mastodon.social

Mastodon

1517
21
832
0
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 5mo ago
Replying to
@fedops @penguin42 I'm not part of any distro security team, so I can't really speak for any of them. But Debian contains about 40000 source packages as of may 2026, it feels slightly unrealistic that the security team are supposed to track patches for all of those and understand which ones contain important security fixes. If you find a vulnerability, register a website and build an exploit, then notifying the vendors beforehand feels like a quite small thing in comparison.
5
1
0
0
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 5mo ago
Replying to
@penguin42 It did not, the process is somewhat described here: https://docs.kernel.org/process/security-bugs.html
docs.kernel.org

Security bugs — The Linux Kernel documentation

5
1
0
0
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 5mo ago
Replying to
@asltf Since the kernel have the policy "every bug gets a CVE" ( https://docs.kernel.org/process/cve.html ), that seems like a full time job for multiple people. They published 200 CVE's since 2026-04-24: https://lore.kernel.org/linux-cve-announce/topics_new.html I guess the security team of your favorite linux distribution would appreciate some support.
docs.kernel.org

CVEs — The Linux Kernel documentation

4
0
1
0
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 5mo ago
Replying to
@LabanSkoller @jmm They do not, the process is somewhat described here: https://docs.kernel.org/process/security-bugs.html
docs.kernel.org

Security bugs — The Linux Kernel documentation

3
2
0
0
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 7mo ago

Saw this on my way home from @hackeriet@chaos.social , the kids are all right

4
0
1
1
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 5mo ago
Replying to
@raven667 @OmegaPolice I agree that it would be great if the kernel security team had a process that made life simpler for downstream vendors. But since neither me or my employer contributes anything to make that happen I don't think it's my place to have public opinions about it. Personally I would love to see more effort focused on reducing the attack surface of the kernel.
2
0
0
0
Open post
alexanderkjall @alexanderkjall@mastodon.social
· 7mo ago

I love how easy rayon makes it to introduce a thread-pool to parallelize a problem over in #rust .

3-4 hours of work resulted in -84% running time on one of our benchmarks.

Now it feels stupid that I haven't done this before.

mastodon.social

Mastodon

2
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 03:25:31 UTC