Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

buherator

@buherator@infosec.place
akkoma 3.20.1-2-gbc62dd80
  • Open on infosec.place
"I'm interested in all kinds of astronomy."
1661 Followers
742 Following
50 Posts
Personal:
https://scrapco.de
GitHub:
https://github.com/v-p-b
Nudes:
https://infosex.exchange
Open post
buherator @buherator@infosec.place
· 2mo ago
Replying to
@HennaVirkkunen@ec.social-network.europa.eu You are an idiot.
3
0
1
0
Open post
buherator @buherator@infosec.place
· 2mo ago
LLM2Human Clinic https://llm2human.pages.dev/
llm2human.pages.dev
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
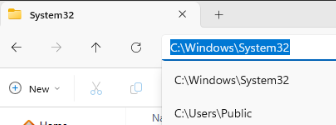
#Windows experts, can you answer this without trying: How many times do you need to press the down arrow to select C:\Users\Public? #UX #UI

#Windows experts, can you answer this without trying: How many times do you need to press the down arrow to select C:\Users\Public? #UX #UI

0
2
0
1
Open post
buherator @buherator@infosec.place
· 1w ago
Umm why does infosec.place "access my device"? /cc @jerry@infosec.exchange
0
2
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@jerry@infosec.exchange @dey@mastodon.social I count HTML as code...
0
0
0
0
Open post
buherator @buherator@infosec.place
· 3w ago
When you help out at a friends kitchen and take a nice looking knife they're usually like "it's shit, don't use that! use this." then hand you an old piece in seemingly questionable condition that was used to skin bears during The War and is still so sharp you need safety goggles just to look at it. Is this world-wide or just an Eastern-European thing? #cooking
0
1
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
[RSS] 4 jsoup vulnerabilities https://joshua.hu/4-jsoup-vulnerabilities
joshua.hu
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@jerry@infosec.exchange It *is* timeline dependent! I had to scroll back more than a day (I stupidly overwritten the original screenshot with the crop, but the timestamp helped). So far I could get this out from some vibe coded event handler in dev tools: "Local Network Access permission required: top-level site “https://infosec.place/” initiator “https://infosec.place/” attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
localhost
0
1
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
An old friend is ashamed of speaking English with people but want to practice. Any pro/cons of using an educational chatbot for this? At first I find this a pretty good use case for language models.
0
1
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
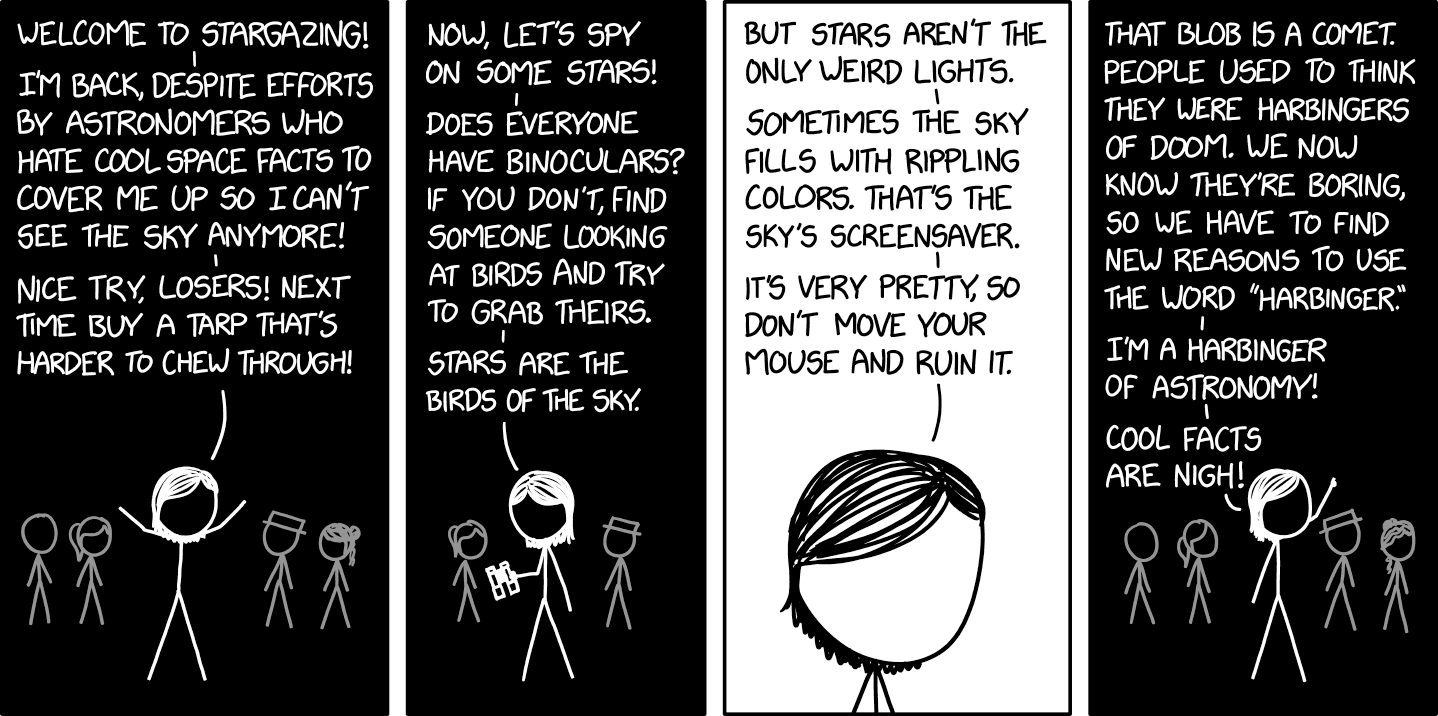
Today's xkcd is especially unhinged, love it! https://xkcd.com/3301/
Stargazing 5
xkcd

Stargazing 5

0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@jerry@infosec.exchange Original timestamp of the image: Wed Sep 23 09:14:13 PM CEST 2026 It's the first time I see such request ever (not just here).
0
2
0
0
Open post
buherator @buherator@infosec.place
· 3w ago
Some places of #Fedi literally require you to look up the Communist Manifesto. Un-fucking-believable.
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
Replying to
@dey@mastodon.social The cybersecurity awareness you spread to me starts to itch. It also hurts to pee. @briankrebs@infosec.exchange
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
Replying to
@VoltPaperScissors@chaos.social @inselchaos@chaos.social Still very cool, Pocket Encrypt already looks like a spy gadget (IMO that's really important when teaching cryptography :))!
0
1
0
0
Open post
buherator @buherator@infosec.place
· 3w ago
This IT Crowd episode predicted the AI boom (except instead of covering bad team dynamics we try to prevent $NVDA go down): https://www.youtube.com/watch?v=uyV0IVItlM4

The it crowd - Denholm Hello Computer

0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
Replying to
@VoltPaperScissors@chaos.social @inselchaos@chaos.social Pringles Enigma! Brilliant! Although as I understand the Enigma part is not delivering electricity (yet)?
0
2
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
[RSS] Advisory X41-2026-004: dm-verity can be bypassed in Debian live-boot https://x41-dsec.de/lab/advisories/x41-2026-004-debian-live-boot/
Advisory X41-2026-004: dm-verity can be bypassed in Debian live-boot
X41 D-Sec - Penetration Tests and Source Code Audits

Advisory X41-2026-004: dm-verity can be bypassed in Debian live-boot

X41 discovered that dm-verity can be bypassed in Debian live-boot

0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
[RSS] 22 CVEs in TeamDavid(R) a "secure" M365 alternative https://labs.infoguard.ch/posts/22-cves-in-david-a-secure-m365-alternative/
labs.infoguard.ch
0
0
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
[RSS] What Go Taught Us About Java Garbage Collection https://debugagent.com/what-go-taught-us-about-java-garbage-collection
What Go Taught Us About Java Garbage Collection
DebugAgent

What Go Taught Us About Java Garbage Collection

As Java developers, we take a lot of inspiration from HotSpot. It is the gold standard for many of us, and for good reason. But measuring ParparVM against Go recently sent me down a different path. Wh

0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
[RSS] Chamilo LMS... It's raining 0days, hallelujah, it's raining 0days http://blog.quarkslab.com/chamilo-lms-its-raining-0days-hallelujah-its-raining-0days.html
blog.quarkslab.com
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@dey@mastodon.social @jerry@infosec.exchange But I'm not using Mastodon, this is an Akkoma instance. And this only happens if I scroll back to the point in my timeline when I first got this notif. It'd be really weird if this behavior didn't trigger at around page load.
0
1
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
Replying to
@cR0w@infosec.exchange Exquisite meme, sir!
0
1
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
Dependency Cooldowns for different package ecosystems https://cooldowns.dev
cooldowns.dev

Dependency Cooldowns - Dependency Cooldowns

A guide to configuring dependency cooldowns across package managers to protect against supply chain attacks.

0
1
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
#music #reggae
96 degrees in the shaaaaade https://www.youtube.com/watch?v=hwE5gfZlMZY
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
[RSS] CVE-2026-43783: Repair Permissions - Get Root: LPE via DesktopServicesHelper in macOS 26.5 https://ptswarm.com/blog/cve-2026-43783-repair-permissions-get-root-lpe-via-desktopserviceshelper-in-macos-26-5/
ptswarm.com
0
0
0
0
Open post
buherator @buherator@infosec.place
· 3d ago
I recently learned to distinguish rabbits from hares (from a shitpost ofc) and now I feel slightly offended because my emoji keyboard shows a rabbit but it clearly renders as a hare in the app. 🐇
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Session timeouts[1] provide great examples of #compliance disconnects from reality: When booking for events it *always* takes *days* to get from registering for an event and getting there to show your QR or whatever. And while an attacker who hijacks your session has 0 benefit from accessing it for a prolonged time, somehow #security finds it crucial that users are auto logged-out after 30mins. It would take just a *tiny* bit of thinking to avoid making things worse for everyone. [1] https://wstg.owasp.org/latest/4-Web_Application_Security_Testing/06-Session_Management/07-Session_Timeout/ (congrats to #OWASP for breaking all your indexed links in search engines, also very helpful!)
WSTG - Latest
OWASP Web Security Testing Guide

WSTG - Latest

The premier cybersecurity testing resource for web application developers and security professionals.

0
0
0
0
Open post
buherator @buherator@infosec.place
· 3w ago
[RSS] Apple Reference Image: A New Approach for Verified Photography https://security.apple.com/blog/apple-reference-image
Apple Reference Image: A New Approach for Verified Photography - Apple Security Research

Apple Reference Image: A New Approach for Verified Photography - Apple Security Research

Introducing Apple Reference Image, a new solution for verifiable photography on iPhone. This new, opt-in camera mode lets a photographer create a securely timestamped reference image that accurately depicts what was captured by the iPhone's camera sensor. Apple Reference Image offers a trustworthy, scalable guarantee that a reference image is what it claims to be: a real photograph, captured by a real sensor in an iPhone camera, at a specific period in time.

0
0
0
0
Open post
buherator @buherator@infosec.place
· 3d ago
"This 3-day training focuses on macOS Vulnerability Research (VR) for beginner to intermediate students. While intermediate topics will be discussed, the course focuses on bringing security researchers up to speed with macOS’s unique protections and vulnerabilities"

Great content from my friends, now in Budapest:

https://macosvuln.training
macosvuln.training
0
0
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
[RSS] LLMs won't break symmetric crypto https://www.bfswa.blog/p/llms-wont-break-symmetric-crypto
bfswa.blog
0
0
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
Replying to
If you like this post, please consider supporting this GitHub issue: https://github.com/rust-lang/cargo/issues/16574 #Rust #Cargo
github.com
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
[RSS] The Binary Hiding in Your Registry: Cracking Windows UCPD's Dynamic Rules https://binary.ninja/2026/08/04/ucpd-dynamic-rules.html
binary.ninja
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@dey@mastodon.social @jerry@infosec.exchange More details pls, who is trying to figure out if I have SW X installed and how?
0
1
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
Seems like AI companies are not that easygoing when they are on the wrong end of hacking :P https://threadreaderapp.com/thread/2101252692635004997.html
Thread by @LiveOverflow on Thread Reader App
threadreaderapp.com

Thread by @LiveOverflow on Thread Reader App

@LiveOverflow: Here is how OpenAI’s CISO fumbled the situation (in my personal opinion) 🧵 1/X Right after the report we got into a shared Slack channel with OpenAI. First thing OpenAI’s CISO said: He was "pretty...…

0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@jerry@infosec.exchange FF
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
I thought I'm making up a conspiracy theory around NVIDIA architecting the AI bubble after the crypto bubble bursted. It seems @david_chisnall@infosec.exchange agrees (sort of): RE: https://infosec.exchange/@david_chisnall/117075838205635406
infosec.exchange
0
1
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
FlyDubai crew is pretty badass!
0
0
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
[RSS] KindaRails2Shell: arbitrary file read to RCE in Rails Active Storage via libvips (CVE-2026-66066) https://ethiack.com/info-hub/research/kindarails2shell-rails-rce-cve-2026-66066
KindaRails2Shell - Critical RCE in Rails via Active Storage (CVE-2026-66066) | Ethiack
Ethiack

KindaRails2Shell - Critical RCE in Rails via Active Storage (CVE-2026-66066) | Ethiack

Ethiack research team discovered KindaRails2Shell (CVE-2026-66066): a critical RCE in Ruby on Rails via Active Storage. 500,000+ sites affected. Find out if you are and how to mitigate.

0
0
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
Replying to
@codinghorror@infosec.exchange CEOs often work for minimal wage for tax reasons around here. But even that case is much better than simply asking your billionaire friends to push literal peanuts your way along with a job contract 2 years before you run for office.
0
2
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@jerry@infosec.exchange @dey@mastodon.social I can see the Initiator is an img, but I can't find anything seemingly related in inspector + network rectord don't tell me what code initiated a request. That's the status.
0
2
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
[RSS] Is This A Joke? In The Auth Header? (F5 BIG-IP UnAuth Heap-Overflow to RCE CVE-2026-94127) https://labs.watchtowr.com/is-this-a-joke-in-the-auth-header-f5-big-ip-unauth-heap-overflow-to-rce-cve-2026-94127/
Is This A Joke? In The Auth Header? (F5 BIG-IP UnAuth Heap-Overflow to RCE CVE-2026-94127)
watchTowr Labs

Is This A Joke? In The Auth Header? (F5 BIG-IP UnAuth Heap-Overflow to RCE CVE-2026-94127)

Well, well, well, well, well, well, well, well, well, well, well, well, well, well, well. We're back. Sorry. We've been watching the onslaught of vulnerabilities flood the internet. Every man, dog, and their grandmas (apparently?) are now using LLMs to find and reproduce vulnerabilities - it’s a free-

0
1
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
That's right, the right answer for this questions is: 3! By first pressing the down arrow you remove the selection (which you didn't put there) from the address bar text. The two downs are needed to reach C:\Users\Public. "2 or 3" would be also acceptable, because if you don't just click the address bar, but start to type in it, there is no selection to remove. https://infosec.place/objects/85dfac07-d1d6-412b-832c-897be5be860b
Open quoted post
Quoting
buherator
@buherator@infosec.place
#Windows experts, can you answer this without trying: How many times do you need to press the down arrow to select C:\Users\Public? #UX #UI
Open quoted post
infosec.place
0
0
0
0
Open post
buherator @buherator@infosec.place
· 3w ago
FFS Reddit is now using "protecting communities from scrapers" as an excuse to kill RSS. Great job everyone coming up with this BS! https://old.reddit.com/r/modnews/comments/1tq9vxo/protecting_communities_from_scrapers_and_platform/
old.reddit.com
0
0
0
0
Open post
buherator @buherator@infosec.place
· 2w ago
Replying to
@tychotithonus@infosec.exchange I miss OS diversity too, guess it'll be a future improvement? Prioritizing Linux instructions makes sense if you consider CI pipelines.
0
0
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
[RSS] Escaping Linux Sandboxes via PipeWire (CVE-2026-5674) https://embracethered.com/blog/posts/2026/pipewire-flatpak-linux-sandbox-escape-cve-2026-5674/
Embrace The Red

Escaping Linux Sandboxes via PipeWire (CVE-2026-5674) · Embrace The Red

This post walks through a sandbox escape from a Flatpak application via PipeWire. The vulnerability was discovered using my automated research pipeline with …

0
0
0
0
Open post
buherator @buherator@infosec.place
· 1w ago
Replying to
@jerry@infosec.exchange Based on this article and the previous error I assume this permission request is not coming from JS but someone trying to make me fetch an URL from localhost which now triggers additional warnings: https://support.mozilla.org/en-US/kb/control-personal-device-local-network-permissions-firefox At this point I'm not sure if it should be illegal for posts to contain references to localhost.
support.mozilla.org

Client Challenge

0
0
0
0
Open post
buherator @buherator@infosec.place
· 2mo ago
[RSS] XProtectRemediatorDubRobber infoleak on macOS (CVE-2024-40842) https://gergelykalman.com/CVE-2024-40842-xprotectremediatordubrobber-infoleak-on-macos.html
gergelykalman.com
0
0
0
0
Open post
buherator @buherator@infosec.place
· 1mo ago
Replying to
@VoltPaperScissors@chaos.social @inselchaos@chaos.social This looks amazing! Does the multi-rotor part actually work??
0
4
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 20:49:10 UTC