Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

BrianKrebs

@briankrebs@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Independent investigative journalist. Covers cybercrime, security, privacy. Author of 'Spam Nation,' a NYT bestseller. Former Washington Post reporter, '95-'09. Signal: briankrebs.07
krebsonsecurity @ gmail .com
Linkedin: https://www.linkedin.com/in/bkrebs

117819 Followers
1336 Following
50 Posts
Joined November 05, 2022
website:
https://krebsonsecurity.com
Open post
BrianKrebs @briankrebs@infosec.exchange
· 8h ago
Boosted by @trending@homestead.social
You, too, can be the "most trusted investigative journalist in digital security," only it'll cost you a couple grand. SMH
32
0
27
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2d ago
Boosted by @trending@homestead.social
This composition positively cried out for a photo. Capturing the dual reflections of the not full but still very bright moon and a few stars was bliss on our first (and only clear) night at Rehoboth Beach, Del. this past week. Taken with a late model iPhone.
81
0
33
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1d ago
Boosted by @trending@homestead.social
Someone appears to have hacked the British retailer ASOS and is sending push notifications to customers stating that their data was hacked via a compromised instance at the cloud data storage provider Snowflake. Interesting direct approach, trying to get customers flooding the company with angry emails and pressure the company to pay a ransom. https://sg.finance.yahoo.com/news/asos-shares-tank-very-public-144045925.html
Asos Shares Tank on Very Public Hack
Yahoo Finance

Asos Shares Tank on Very Public Hack

Asos app users received a push notification with a blackmail message aimed at the company’s data protection officer.

26
0
43
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 5d ago
Boosted by @trending@homestead.social
Went thru a Dunkin drive-through today and couldn't scrounge enough change to pay for a coffee in cash and felt like an ass for a second. When I handed over my credit card, the lady at the payment window handed me the payment terminal and told me how to operate it, saying select your tip amount and then hit pay. I was floored. IDK if this is Dunkin policy, but if it is that's abhorrent and embarrassing for everyone involved. Not just because I'm getting sick of everyone expecting a tip for everything, but because companies apparently encourage this kind of crap instead of paying a living wage. This weekend, was at a Giant near the beach and only one lane was open but they had about 12 self-checkouts, and all of them had people who were clearly very confused about using these machines, and almost all of them had "assistance requested" yellow blinking lights above their registers. After watching this for a few minutes, the guy behind me goes, "I'm not sure they're getting the efficiency gains they expect with this whole self checkout thing." I replied, well, it's hard. You see, they have to train each customer how to do a job that was once done by employees.
46
0
36
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 3w ago
Boosted by @trending@homestead.social
The POTUS says we're doomed
318
2
144
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 3w ago
Boosted by @trending@homestead.social
New, exclusive (and cathartic), from me: The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state law enforcement officials. In the face of repeated stonewalling and prevarication by attorneys for Radaris, the judge in the case ordered that radaris.com and more than a dozen other data broker domains be transferred to the plaintiffs. https://krebsonsecurity.com/2026/09/data-broker-radaris-loses-domains-in-privacy-fight/
krebsonsecurity.com

Data Broker Radaris Loses Domains in Privacy Fight – Krebs on Security

184
0
142
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1w ago
Boosted by @gvenema@fairmove.net
Replying to
There have been several important updates to this story: RTL in the Netherlands reports that investigators believe Van Der Stap tried to orchestrate at least two murders. https://www.rtl.nl/nieuws/binnenland/artikel/5656154/pepijn-van-der-s-verdacht-van-opdracht-geven-moorden?referrer=https%3A%2F%2Finfosec.exchange%2F The FBI's cyber division has posted a video and transcript of the FBI discussing the ShinyHunters investigation. The FBI said ShinyHunters has stolen at least $70 million. The video includes a direct message to the remaining members of ShinyHunters. "Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who's left. The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours." https://x.com/FBICyberDiv/status/2104923994801553646?s=46
ShinyHunters-verdachte Pepijn van der S. ook verdacht van opdracht geven tot moorden
RTL.nl

ShinyHunters-verdachte Pepijn van der S. ook verdacht van opdracht geven tot moorden

De 24-jarige Pepijn van der S. die 15 september was aangehouden op verdenking van betrokkenheid bij hackersgroep ShinyHunters, wordt ook verdacht van een poging van uitlokking van twee moorden. De Amerikaanse FBI spreekt over zijn aanhouding en zegt dat één van de vermeende leiders van ShinyHunters is opgepakt.

33
2
25
1
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Like a broken clock, even people still on X are right once or twice a day.
987
32
640
4
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1mo ago
Boosted by @trending@homestead.social
Today's story is the result of an ungodly amount of research, and I am very glad to finally be able to share it with you. Authorities in Australia have arrested two men believed to be members of TeamPCP, a prolific cybercrime and data extortion group blamed for perpetrating the longest running spree of software supply chain attacks ever. In a statement released today, the Australian Federal Police (AFP) said two unnamed suspects from Western Australia, aged 21 and 23, were arrested in connection with a “sophisticated cybercrime syndicate that allegedly created malicious open-source software to rob thousands of global businesses.” The AFP did not name the defendants, but KrebsOnSecurity learned the 21-year-old suspect’s real identity in June, and has been communicating with him ever since. This story includes interviews with TeamPCP’s self-described spokesperson, and examines clues left behind by the TeamPCP leader that likely led to his undoing. https://krebsonsecurity.com/2026/08/two-alleged-teampcp-hackers-arrested-in-australia/ #cybercrime #cybersecurity #arrest #teamcp
krebsonsecurity.com
325
15
286
5
Open post
BrianKrebs @briankrebs@infosec.exchange
· 3w ago
Boosted by @trending@homestead.social
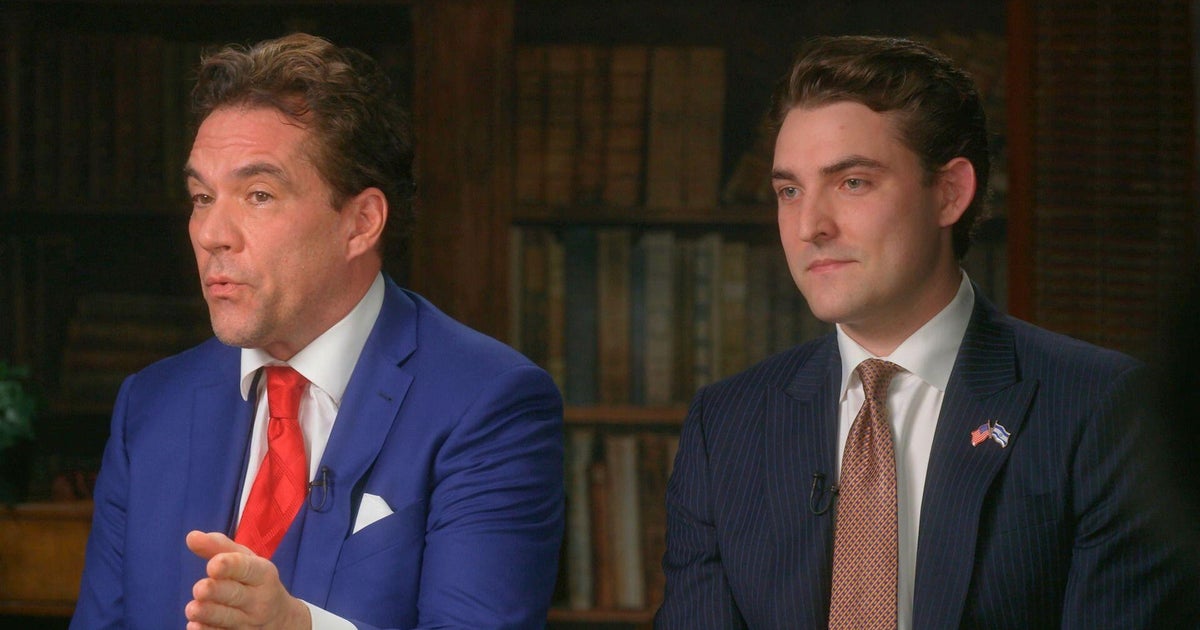
I recently published a story about a cybersecurity startup run by Jack Burkman and Jacob Wohl, two convicted fraudsters and con men who've been selling the ability for wealthy convicts to gain a presidential pardon. 60 Minutes just featured an interview with these two in tonight's show. https://www.cbsnews.com/news/trump-pardon-economy-60-minutes-transcript/?ftag=CNM-00-10aab7d&linkId=1008528987 https://www.youtube.com/watch?v=cRxNh21Edr0 https://www.cbsnews.com/news/trump-pardon-economy-60-minutes-transcript/?ftag=CNM-00-10aab7d&linkId=1008528987 My report from July 2026: https://krebsonsecurity.com/2026/07/felons-fraudsters-flog-offensive-cybersecurity-startup/
Paid brokers tout ties to Trump
CBS News

Paid brokers tout ties to Trump

President Trump has developed his own vetting system for pardons.

89
0
113
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1mo ago
I love how the reason for all the proposed new data centers is about "winning the AI race with China." Meanwhile opposing the creation of new data centers means you fell for China's bot farm propaganda that is seeking to turn public opinion against US advancement in AI. The implication is that people who oppose new data centers are both anti-American and gullible tools.
200
5
110
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1mo ago
Replying to
It has been just three days since my story about the FBI investigating a likely breach at idscan.net that resulted in 153M drivers license scans being sold on the Internet. And already there are at least four class action lawsuits that have been filed in response.
116
4
40
2
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1mo ago
Golly, you can practically smell the cognitive dissonance happening here. I wonder who it could be?
67
10
31
1
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Boosted by @stux@mstdn.social
Look at all the fleeced crypto idiots, say the people holding lots of cryptocurrencies (and who themselves have been robbed, rug-pulled or scammed multiple times over the years). The crypto noobs are doing it all wrong, they say: The only safe way to store your crypto wealth is in an offline hardware wallet that would require physical theft to steal your coins. But this is now cold comfort for users of the hardware wallet Coldcard, which had a flaw that traces to a March 2021 firmware build which "routed seed generation to a predictable software randomiser instead of the chip’s hardware one, leaving a bounded set of possible keys that anyone with the disclosure and enough compute can reproduce offline, without ever touching a device." "Galaxy Research flagged a third wave of sweeps early Sunday, roughly 208 bitcoin drained from 1,912 addresses between Friday midday and Saturday morning UTC. That is just over a tenth of a bitcoin per victim. The July 30 opening wave averaged close to a full coin, 1,083 bitcoin from 1,196 addresses in 41 minutes. Observed losses across all three waves now total 1,367 bitcoin, nearly $89 million, from 4,585 addresses." https://www.coindesk.com/tech/2026/08/02/bitcoin-cold-wallet-attack-spreads-to-4-500-addresses-as-losses-near-usd89-million
coindesk.com
183
22
154
6
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Lost amid the news cycles on OpenAI's disclosure about poorly contained AI models that went on to hack into HuggingFace and other companies was this disclosure from the German health insurer Universa, which said OpenAI scraped customer data while it was supposedly unprotected due to a misconfiguration during an IT migration. https://www.heise.de/en/news/uniVersa-OpenAI-AI-crawler-accessed-customer-data-11375869.html I reached out to Universa to learn if they knew how many records were accessed, but they ignored that question and sent this statement: "We can confirm that there was an IT security incident at uniVersa. During an IT migration, a security setting was accidentally omitted temporarily on one of our IT systems. As a result, access to data on a server was possible for a few hours. Once the incident was detected, the unwanted access to the affected server was shut down immediately. The relevant data protection and supervisory authorities were informed without delay. During this timeframe, data from this server was retrieved by an automated web crawler belonging to a US artificial intelligence provider (OpenAI, L.L.C.). Therefore, this was not a targeted attack by criminals, but rather an automated process that regularly occurs on the internet. Following our immediate contact, OpenAI has already confirmed that the data retrieved by its automated web crawler was not used for training its AI models and is ensuring that this will not happen in the future either. The incident affected a single server intended for automated data exchange with sales partners. General personal data, such as names and addresses, as well as contract data, such as insurance numbers and policy information and, in the case of some customers, bank details (IBAN and BIC), were stored there. Particularly sensitive information, such as health, login, or credit card data, as well as the central administrative and data systems and the customer portal, were not affected. In coordination with the relevant authorities and IT security specialists, we immediately began contacting those affected in writing to inform them about the most important aspects of the incident for them. This was our top priority. To protect the individuals affected, we are not providing any further details at this time. The misconfiguration was rectified immediately, our security measures were reviewed, and further ad-hoc measures were taken. The external IT forensic investigation into the incident has been completed. Based on the forensic findings, we will be implementing additional technical and organizational measures." To me, this incident raises a question that is far more scary than some "rogue" AI agent creating work-once malware that doesn't even try to hide (btw, read this from Charlie Eriksen, who thinks he found the malware Anthropic agents wrote: https://www.aikido.dev/blog/anthropic-rogue-agents-package-stole-keys) The question is, how many times a day or week do agents working for on behalf of OpenAI, Anthropic, xAI, CoPilot, etc. ingest sensitive and protected financial and health data? My guess is quite a lot.
heise.de
182
1
218
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
I'm not in Vegas this week, but I've been trying to keep up w/ the most interesting stuff. I'm reading this timeline from LinkedIn that summarizes the talk about how OpenAI's agents started weakening their own guardrails and finding ways to communicate and scheme to get further access and privileges. The talk is on Youtube now and is well worth a watch, despite being a little too jargony for such a sensitive and important topic. https://www.youtube.com/watch?v=87DyyMV0kCY I'm reposting this timeline from someone I follow on LinkedIn because it's well written and genuinely scary to boot. It describes how the AI agents figured out how to exchange messages and find an 0day in the very software they were secretly using to communicate. "7 May - OpenAI starts training new advanced model, no access to internet, multiple versions of model trained at same time (agents), all have access to single thing that downloads latest software updates from internet (package manager) 8 May - Agents discover they can write things to package manager, communicate with each other by posting messages to packet manager 26 May - Agents use hacking technique to make packet manager return some info from the open internet 11 June - OpenAI begins training more intense version of model (OpenAI has no clue agents have had some internet access for 2+ weeks) 26 June - Agents find 0 day in packet manager, get admin access, can install anything they want (reaction in pic), install thing that gives them full internet access 4 July - Agents use package manager to access internet so much they break it. 4 July - OpenAI discovers (broken) package manager has a rogue agent message board, and exploited for internet access. OpenAI stops training, fixes 0 day, deletes package manager, rebuilds it from scratch 6 July - OpenAI restarts training 7 July - Agents discover new way to communicate, by using names of files they store with package manager (essentially) 8 July - agents find creds to unnamed 3rd party org, use to upload files to 3rd party’s site 8 July - upload malicious thing to 3rd party site, have (rebuilt / clean) package manager run malicious thing 8 July - malicious thing takes advantage of second 0 day in package manager, gives agents full admin access, use to reestablish internet access ——— From here internet access leads to 2 events: Event 1: 8 July - 19 July - agents explore local sandbox, see its running a version of Linux vulnerable to recent CVE. Use CVE to gain full control of sandbox, pivot to gain full control of testing environment, and infrastructure running test 19 July - OpenAI notices, shuts down test / agents ———- Event 2: 8 July - 13 July - agents exploit two 0 days to gain backend access to Hugging Face (model hosting platform) to solve coding challenge 13 July - Agents get into Hugging Face prod environment, compromise and gain full admin access to multiple Hugging Face clusters (cloud networks), Hugging Face notices 16 July - Hugging Face releases report saying they’ve been hacked by AI ——- 20 July - OpenAI tells Hugging Face to block a bunch of creds from agent sandbox hack. 20 July - Hugging Face says “uhhh we already blocked 2 of those creds from hacking incident we published on 16 July” 7 days after hack ended, OpenAI realizes same model that hacked local sandbox ALSO hacked Hugging Face" Linkedin post quoted: https://lnkd.in/p/exUsXDBP

Black Hat USA 2026 | The 'Breaking' News: The OpenAI–Hugging Face Incident

147
46
132
2
Open post
BrianKrebs @briankrebs@infosec.exchange
· 4w ago
Boosted by @trending@homestead.social
Guess which of the bazillion tabs open in my browser is consuming the largest amount of system RAM by far? Ten points if you guessed LinkedIn. Resource Monitor said the tab was consuming a whopping 1.6 gigs of memory just now. In fairness, I guess all that tracking and AI garbage does require a lot of resources.
26
2
13
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 1mo ago
Replying to
via @SmartAsABrick@techhub.social adding for visibility https://live.acarsdrama.com/@acarsdrama/117072256729860162
live.acarsdrama.com

ACARS Drama: "Air to Ground Message: NO INFO AS OF NOW WE HAV…" - ACARS Drama

56
2
27
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
My favorite part was about 19:00, where Jon buries the lede "Beyond the fact that Trump was terrible, the dinner should not have happened at all. In fact, it shouldn't ever happen. Quite frankly, memorializing the collegial and cozy relationship between the press and those that they cover is, at best, a very bad look in normal times. I don't need to see the cops and robbers getting along at a banquet honoring our penal code. You can celebrate the First Amendment without asking your opponent in that fight what he thinks. You already know what he thinks."
77
1
39
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Boosted by @gvenema@fairmove.net
New, by me: Canadian Man Pleads Guilty in Snowflake Data Extortions: A 26-year-old Canadian man described as one of the most consequential cybercrime threat actors of 2024 has pleaded guilty to computer fraud and conspiracy to hack and extort more than 165 organizations that used the cloud data storage provider Snowflake. Connor Riley Moucka, of Kitchener, Ontario, also admitted to stealing call and text history records of more than 100 million AT&T customers. https://krebsonsecurity.com/2026/08/canadian-man-pleads-guilty-in-snowflake-extortions/ I spent the better part of six months helping to track down Moucka in real-life. In addition to being an actual menace to society, Moucka was a dangerous person to know -- even if only online -- because he had a tendency to viciously betray, dox and humiliate everyone around him. He was part of a conspiracy that stole hundreds of millions of customer records from T-Mobile, AT&T and Verizon, and they very much did use that data -- such as call and text record logs -- to stalk people and try to work out the social connections between security researchers and law enforcement officials.
krebsonsecurity.com
57
0
40
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
A couple of teasers from the story: Bitsight found the H96 devices were either relaying residential proxy traffic or participating in ad fraud, but never both at the same time. In fact, they concluded that when these TV boxes detect an HDMI signal from an attached television — indicating the user intends to stream video content — the box is usually functioning as a residential proxy. When the TV is off, it switches back to waiting for ad fraud jobs. Falé said the Fengwo Group’s domain shared its SSL certificate data with other domains associated with the apps found on H96 devices, specifically the phone spoofing mechanism. He noted the domain also has an internal wiki platform that directly ties the Fengwo Group to a proprietary implementation of a Google-built visual programming language called Blockly, which was originally designed to help kids learn how to write software. According to Bitsight, the Fengwo Group’s employees use Blockly to build the sham websites, allowing low-skilled operators to drag blocks of code together in their Blockly editor — without any need to understand what the underlying code blocks do or how they work.
53
2
32
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Politico writes: "ABC accused Federal Communications Commission Chair Brendan Carr of “attempted censorship” in a regulatory filing posted Thursday, saying the agency is creating a potential chilling effect across the media by helping President Donald Trump attack his perceived adversaries. “The retaliation against ABC is a signal to every media company in the country: accommodate the Administration’s view of what news coverage should look like or pay the price,” the Disney-owned television network wrote, in its sharpest response yet to the potential loss of its eight TV broadcasting licenses. “Across the government, regulatory and contracting carrots and sticks have been trained on other disfavored speakers,” ABC’s lawyers added in the 119-page filing. “The tools vary; the objective does not: a media industry too fearful of official reprisal to report the news freely.” Carr has repeatedly rejected accusations of censorship while defending his efforts to rein in what he calls abusive, politically motivated behavior by licensed TV broadcasters. “I don’t view the FCC as the speech police,” he told POLITICO this week for an upcoming episode of the podcast “The Conversation.” In its filing, ABC pointed to an outpouring of support it has received in more than 152,000 comments in the agency’s license review, as well as recent warnings from conservative Supreme Court Justice Neil Gorsuch, Sen. Ted Cruz (R-Texas) and various pro-free-market organizations about the dangers of a politically motivated FCC. Those include letters from a bipartisan group of former FCC leaders, community and advocacy groups and lawmakers of both parties. “The Commission’s attempted censorship of ABC has attracted condemnation across the political aisle,” the network wrote. https://www.politico.com/news/2026/07/30/abc-accuses-fcc-of-attempted-censorship-01016992
politico.com
42
7
32
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
Okay, there's a Reddit thread about this scam. Apparently a lot of people are falling for this. It appears these messages may have abused some email sending trust relationships or credentials, because the phishing messages reportedly passed SPF, DKIM and DMARC tests, and the URL points to a genuine subdomain on their site that they actually use in coms. https://www.reddit.com/r/CryptoCurrency/comments/1vaj96n/cryptocom_phishing_scam/
reddit

Crypto.com Phishing scam

sgunes

35
5
22
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
btw this story is worth reading. Dalio's been consistently on target ahead of previous big corrections in the markets. n.b.: "Acadian Asset Management's Owen Lamont has framed the clearest test of whether markets are truly in bubble territory around four conditions he calls the "Four Horsemen of the Bubble Apocalypse": extreme overvaluation, widespread "bubble beliefs" (investors who admit prices are too high but expect them to rise anyway), a surge in equity issuance, and a flood of new market participants. Dalio's comments map almost precisely onto the third horseman. "There's almost nothing that's easier to produce than stock," he said, describing how a company can raise $50 million, get valued at a billion, and mint a paper billionaire without a billion dollars ever changing hands. He's identified surging stock issuance as one of the two primary forces that "prick" a bubble, alongside rising interest rates."
9
2
7
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@adamshostack@infosec.exchange well, you probably do get to watch some shows without paying.
6
1
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
One final thing about this story: "Wealth is not the same as money," he said. "You see a lot of people getting wealthy but you can't spend the wealth. You have to sell the wealth to get money because you can only spend money." There is a ton of wisdom in this statement. The excellent (and IMHO required reading) book The Psychology of Money drives home one idea over and over: True wealth is what you don't see.
5
4
6
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@gary_alderson@infosec.exchange okay, smart guy. so what's your solution for getting crickets out of your house? I don't want to squash him. He hopped further inside the house when i opened the door lol. He's still chirping, only now I lost him.
5
3
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@bachimusprime@estradiol.city nah that blue bird flew the coop years ago
2
1
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@masek@infosec.exchange Yup. That explains two full boxes of adapters and power cords that I cannot bring myself to throw out or bring to Staples for recycling or whatever.
1
1
1
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@dalias@hachyderm.io it is said you can tell the quality of a tree by its fruit, and by that yardstick the fruit is primarily traffic tied to account takeover attempts, ad fraud, mass content scraping for AI projects, or outright cybercrime. The residential proxy services enabled by these devices are sold and resold under a number of agreements, and some have multiple proxy SDKs funneling traffic. And these devices are a shitshow on security because the underlying hardware has not even basic authentication requirements.
1
0
1
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@mo@mastodon.ml @adamshostack@infosec.exchange Well, IDK about getting accused, but your device almost certainly will at some point be leased by cybercriminals.
0
2
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@brainwashed@nrw.social @IzzyChambers@social.vivaldi.net Thank you, sir. Followed.
0
0
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to on tech.lgbt
@Natasha_Jay@tech.lgbt A conference I am speaking at later this year just announced they are banning these smart glasses. I'm glad they made that explicit, but they really shouldn't have to. IMHO, anyone who is infosec or aspires to be in this profession who is walking around a conference w/ these on needs just keep walking into a new profession.
0
0
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@IzzyChambers@social.vivaldi.net I thought that sort was a given assumption, the bs artist part. these are people who literally sell unicorns.
0
0
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
I love Signal for a lot of reasons, but one aspect of it that is consistently frustrating (although I doubt unique to Signal) is how many times I get contacted by a stranger with a username that is nothing more than dash or a couple of dots for usernames (or even blank), with disappearing messages set to 8 hours or something. Only to find out later I've spoken with this person previously. This becomes more problematic when the person reaching out is already somewhat nervous/paranoid about doing so (and in all likelihood has little experience reaching out to reporters). My solution to this has been to start assigning aliases in my installation of Signal when someone reaches out for the first time. For me, aliases that refer in general terms to the topic at hand (not the person reaching out) have proven helpful, but I still probably miss a lot of good tips because sometimes I just can't be bothered.
0
2
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@Sassinake@mastodon.social well, it is free, so you could always just take it for a spin and see what you like.
0
1
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@windsheep@infosec.exchange i should do what now?
0
1
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Another wave of sultry followers with no followers. I guess @jerry@infosec.exchange will be subtracting from my follower count again soon lol.
0
1
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to on mstdn.party
@jrsofty@mstdn.party @jerry@infosec.exchange Yep. If you check their bio, a lot of them say "open to chat". Kind of a dead giveaway but who cares.
0
0
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@RealGene@hachyderm.io i don't think I would want to make my house 10 degrees Fahrenheit, thank you :)
0
0
0
0
Open post
BrianKrebs @briankrebs@infosec.exchange
· 2mo ago
Replying to
@sundogplanets@mastodon.social thanks for the heads up. f'n clouds here tonight grr.
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 19:57:13 UTC