#owasp

32 posts · Last used 8d

#OWASP #Ottawa is pleased to announce that Alexander Rudolph, PhD will be speaking at OWASP Ottawa Day 2026 with his presentation: “Canadian Digital Sovereignty in a Zero-Trust World: Unpacking Socio-Economic Dimensions of Digital Sovereignty” Digital sovereignty is no longer just about where data is hosted. Alexander will examine how foreign legal, technological, and economic dependencies affect Canada’s sovereignty, including the implications of the U.S. CLOUD Act, Microsoft’s GDID, and Canada’s reliance on U.S.-based technology providers. Alexander is a Ph.D. researcher at Carleton University focused on Canadian cyber defence policy and conflict in cyberspace, and the creator of Canadian Cyber in Context. 📅 October 17, 2026 ℹ️ Information: https://lnkd.in/geydKX5N 🎟️ Tickets (free): https://lnkd.in/gc5W7DBe #DigitalSovereignty #CyberSecurity #CyberDefence #Canada #OWASPOttawa2026 #AppSec
3
1
5
0
Replying to
REGISTER NOW: https://appsecil.org/registration Code: AppSecIL2026 (10% off) #AppSecIL #OWASP
0
0
0
0
Session timeouts[1] provide great examples of #compliance disconnects from reality: When booking for events it *always* takes *days* to get from registering for an event and getting there to show your QR or whatever. And while an attacker who hijacks your session has 0 benefit from accessing it for a prolonged time, somehow #security finds it crucial that users are auto logged-out after 30mins. It would take just a *tiny* bit of thinking to avoid making things worse for everyone. [1] https://wstg.owasp.org/latest/4-Web_Application_Security_Testing/06-Session_Management/07-Session_Timeout/ (congrats to #OWASP for breaking all your indexed links in search engines, also very helpful!)
0
0
0
0
POST 1/2 SESSION SPOTLIGHT Beyond the Bomb: Securing AI Applications and Agents through Security Steerability Itay Hazan Meet ASTRA: a framework that puts tool-using agents through 140 attacks to measure their security steerability. POST 2/2 https://appsecdayisrael2026.sched.com/event/2WQZI/beyond-the-bomb-securing-ai-applications-and-agents-through-security-steerability REGISTER NOW: https://appsecil.org/registration Code: AppSecIL2026 (10% off) #AppSecIL #OWASP
0
0
0
0
Save the date: Saturday October 17th. #OWASP #Ottawa is pleased to announce a day of learning, community, and mentorship to celebrate the 25th Anniversary of the OWASP Foundation and the OWASP Ottawa Chapter’s selection of one of the top chapters in a constellation of over 130 Chapters. This will be a free _and_ ticketed event. Details on tickets, speakers, and other details will be made available soon. For the community. By the community. #OWASPOttawaDay2026 #Security hashtag#appsec #Itsec #Cyber #Cybersecurity
2
0
2
0
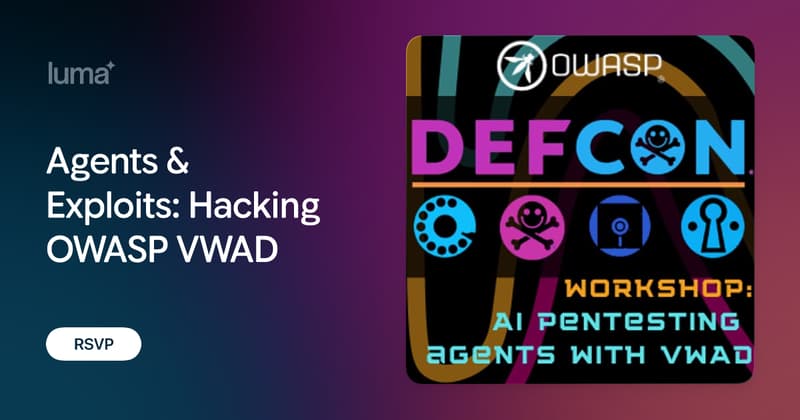
🤖 Give an AI agent shell access, a browser & an OWASP vulnerable app - then teach it to hack. Build a security agent, find exploits, analyze what it misses & iteratively improve it at #DEFCON34. 📍OWASP Community Village, LVCC, W4/1415 🎟️ https://luma.com/yw0xkarr #OWASP #AISecurity
1
0
0
0
what I've experienced at OWASP Global AppSec EU 2026 and why I wouldn't have been there in the first place if it weren't for @m1r314@infosec.exchange | A Tester's Journey: OWASP Global AppSec EU 2026 - Achievement Unlocked https://www.lisihocke.com/2026/07/owasp-global-appsec-eu-2026-achievement-unlocked.html #OWASPVienna26 #OWASP #GlobalAppSec #AchievementUnlocked
4
2
2
1

Moin!

Wie vorangekündigt: 28.7. ist das nächste OWASP-Treffen, bei dem ein bisschen Hamburger Lokalpariotismus mitschwingt 😉

Wie vielleicht vermutet, ist die Rede vom OWASP Juice Shop, a.k.a. "probably the most modern and sophisticated insecure web application". Das ist ein sog. OWASP-Flagship-Projekt, dass vor Kurzem sein 20. Release hatte.

Eckdaten:
  • Lokation: Baumwall 7, New Work SE (danke, New Work, vor allen Dingen: Gerrit)

  • Vortrag: Freshly Squeezed: Prompt-Injecting Juice Shops New AI Brain

  • Sprecher: Björn Kimminich und Jannik Hollenbach

  • Datum: 28.7.2026

  • Start: 18:00

  • Anmeldung: Wäre hilfreich für die Getränke, die unser Host bestellt. Entweder per Mail oder: https://www.meetup.com/owasp-hamburg-stammtisch/events/315684286

  • Presentation Language: TBD. (if you plan to come and English is better for you, let us know)

Abstract

OWASP Juice Shop's chatbot now runs on real LLM backends, either local models or the major providers' APIs.

And we're not just going to show you the new LLM challenges: we'll solve them with you, live on stage. You call out the payloads, we fire them at the bot: coaxing it into leaking data it shouldn't, hijacking its behavior with well-placed prompts, and finding out on the spot which attacks land and which ones it shrugs off. Bring your nastiest prompt-injection ideas!

We maintainers also had a "fun" year fielding large quantities of AI bot contributions of wildly differing quality. The talk covers how running a popular open-source project has changed since the boom of AI coding agents.

Beyond LLMs, 2026 kept MultiJuicer, the project for managing multiple Juice Shop instances across local or remote hackathons and trainings, busy too. It now ships with a new CTF / wargames scoreboard for tracking participant scores, which we'll show off along the way.

Nachbereitung

Das Portugiesenviertel könnte uns danach weiter verwöhnen. Wenn du zur Nachbereitung dabei bist, sag mir Bescheid. Dann würde ich für dich mit reservieren.

Sonstiges

Falls du selbst Lust auf einen Vortrag hast, oder du generell Vorträgen ein werbefreies Dach über dem Kopf bieten kannst, melde dich gerne!

Generelles zum OWASP-Treffen

Bei unseren für alle offenen Treffen geht es um Software und deren Sicherheit im Internet und/oder #Infosec allgemein. Hier treffen sich Menschen, die sich beruflich oder privat mit IT-Sicherheit beschäftigen: Entwickler, Manager, Pentester und alle an (Web)sicherheit interessierte. Die Atmosphäre ist offen und locker. Uns geht's um den Erfahrungsaustausch, Technikschnack und um's Netzwerken. Wer Produkte oder Dienstleistungen verkaufen will, ist hier falsch. Ihr seid herzlich willkommen, euren Kollegen oder Bekannten einen Hinweis auf unsere Treffen weiterzuleiten. Alle Treffen sind frei, für jeden Menschen offen und kostenlos, mit oder ohne #OWASP-Mitgliedschaft.

0
0
0
1