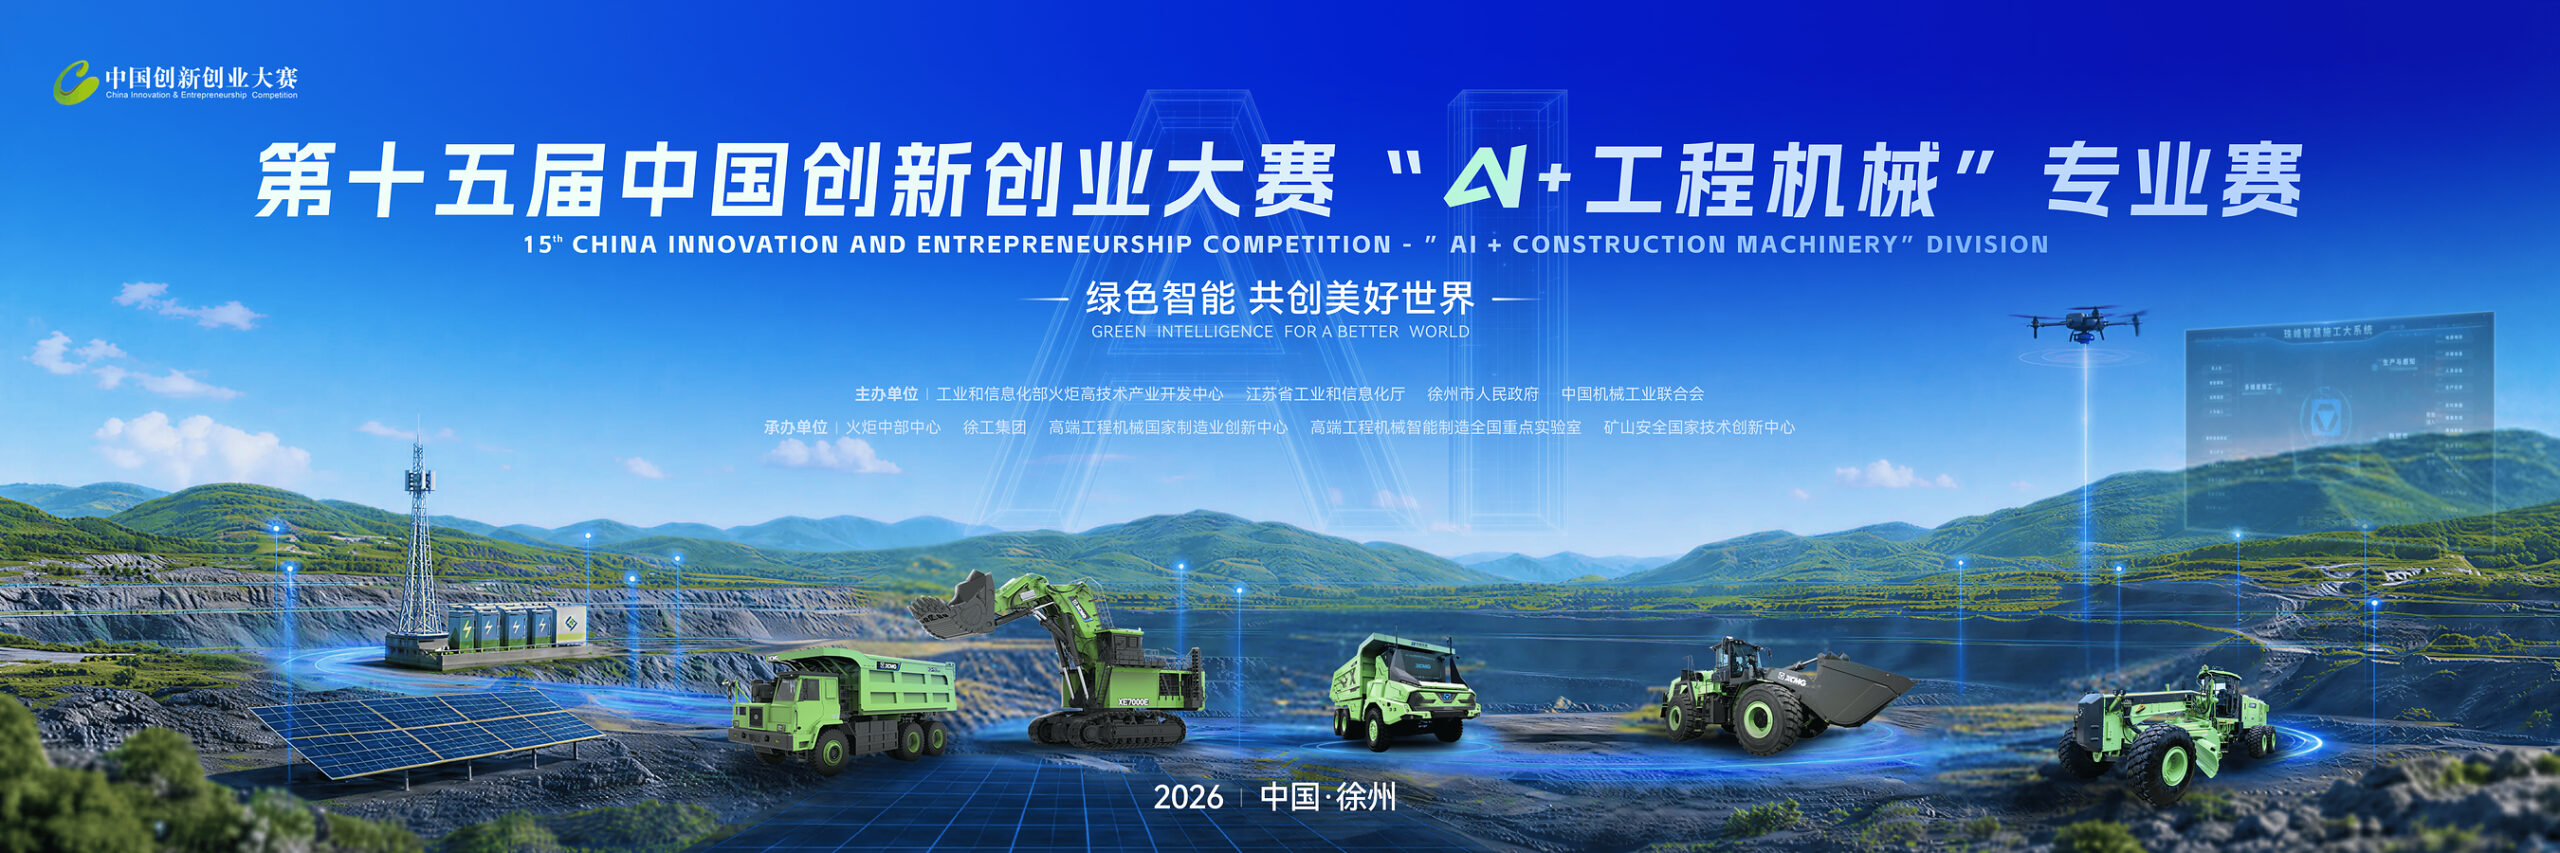
The 15th #China #Innovation & #Entrepreneurship #Competition has opened #registration for its “#AI + #Construction #Machinery” division, running from Aug 13 to Sep 15, with project submissions due by September 25 (Beijing Time). Co-organized by #XCMG, a leading #Chinese construction machinery #manufacturer, the competition focuses on advancing #intelligent and #green #technologies for the #industry under the theme “Green Intelligence for a #Better #World.” https://cnbusinessforum.com/china-launches-ai-construction-machinery-competition-with-xcmg/
#registration
7 posts · Last used 13d
The 15th #China #Innovation & #Entrepreneurship #Competition has opened #registration for its “#AI + #Construction #Machinery” division, running from Aug 13 to Sep 15, with project submissions due by September 25 (Beijing Time). Co-organized by #XCMG, a leading #Chinese construction machinery #manufacturer, the competition focuses on advancing #intelligent and #green #technologies for the #industry under the theme “Green Intelligence for a #Better #World.” https://cnbusinessforum.com/china-launches-ai-construction-machinery-competition-with-xcmg/
Boosted by @fedicat@pc.cafe
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
limit_except GET {
deny all;
}
try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
Boosted by @fedicat@pc.cafe
Dear #Fediverse and #Mastodon admins
currently there is a massive wave of spam registrations everywhere in the fediverse.
For mastodon, I have a solution that works for me:
Create new file /etc/nginx/conf.d/lsbt-registration-spam.conf:
map "$request_method:$uri:$http_user_agent" $block_lsbt_registration_spam {
default 0;
~^POST:/api/v1/accounts:Python/3\.[0-9]+\ aiohttp/ 1;
}
Add to the server block in /etc/nginx/sites-available/mastodon:
location = /api/v1/accounts {
if ($block_lsbt_registration_spam) {
return 403;
}
try_files $uri @proxy;
}
@michaela@lsbt.me @njakob@lsbt.me @MikeGorden@lsbt.me#fediverse #mastodon #registrationspam #spam #registration #Automatedprotocoldeliverabilityprobe #lsbt
Boosted by @GroupNebula563@mastodon.social
does anyone have experience with these free sms receiver sites? the few i found are rejected. or any recommendation for very cheap european throw-away esims?
#privacy #registration #account
Replying to
@Em0nM4stodon@infosec.exchange in fact, many places from #Kenya to #Germany banned the #WorldCoin #Shitcoin #Scam for being a #privacy invasion and/or illegal #Shitcoin without proper #PrivacyPolicy, #ConsumerProtection, ToS and
(allegedly!) in case with German financial regulator @BaFin@social.bund.de:Refusal to comply with mandatory #registration as a #security, Violation of #KYC, #AML & #CTF laws,Operating an illegal #CryptocurrencyExchange,Offering it to #minors,Not documenting #Risks in writing.
https://www.nytimes.com/2026/04/09/us/us-military-draft-automatic-registration-war.html
U.S. Government Moves Toward Automatic Registration for Military Draft
The Selective Service System, an executive branch agency that is separate from the Defense Department, has required men ages 18 to 25 who are eligible to be drafted to register with the government since 1980.
But government officials, bracing for what experts say are potential confrontations with China or Russia while military recruiting has slumped, plan to comb other federal databases to bolster the list.
#militarydraft #registration #resist
You've seen all posts