Seen on FB:
Remote
Dissent Doe 
@PogoWasRight@infosec.exchange
 mastodon 4.8.0-alpha.3+glitch
Blogger/journalist at databreaches.net and pogowasright.org. As a retired healthcare professional, breaches in the healthcare sector are my priority.
The header pic is Indy, a Siberian husky we rescued in 2016 after I read how nobody wanted her because she was so difficult. She is now living her best life and is a mushball with me.
3227 Followers
1447 Following
50 Posts
Joined November 07, 2022
#DataBreaches:
#Privacy:
Have a news tip?:
Signal: Dissent.73
Email:
Breaches@DataBreaches.net
Email:
Breaches@protonmail.ch
Pronouns:
She/Her
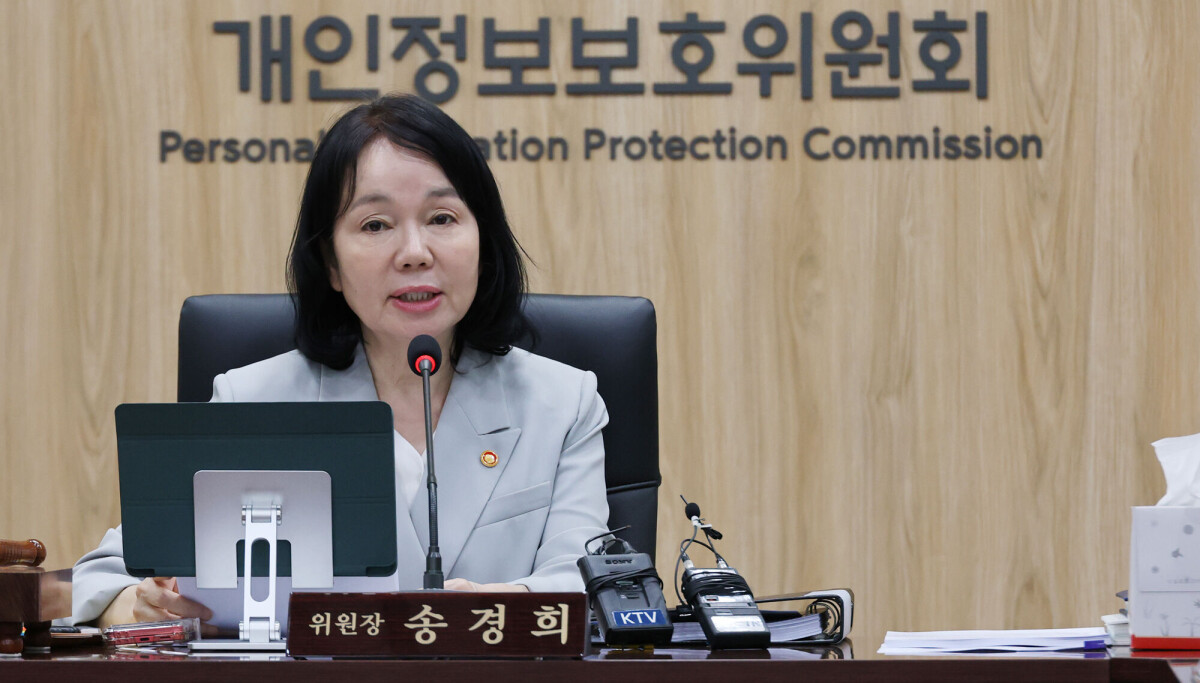
South Korea is cracking down on companies with major data breaches to push them to be more proactive. As seen in Korea JoongAng Daily:
"Starting Friday, companies found to have leaked the personal data of 10 million or more people through intent or gross negligence can be fined up to 10 percent of their total revenue as part of a broader overhaul under the revised Personal Information Protection Act that is set to take effect the same day. Even if a leak hasn’t been confirmed, companies must notify users within 72 hours if the risk of exposure is high.
[…]
Under the enforcement decree, the cap applies to companies that repeatedly commit intentional or grossly negligent violations within three years, or that fail to comply with a corrective order and go on to suffer a breach as a result. Fines are calculated based on the nature and severity of the violation, the circumstances involved and the scale of the damage.
Link: https://www.koreajoongangdaily.com/business/korea-raises-data-breach-fines-to-10-of-revenue/12869899
In the past, South Korea's financial regulators have also fined executives and prohibited some card issuers and banks from signing up any new customers for months as a consequence of big breaches.
I wonder if their efforts/consequences are actually effective in getting more entities to take infosecurity and cybersecurity more seriously.
And I bet we can all think of U.S. companies that might qualify to get hit with such huge penalties.
#databreach #accountability #legislation #SouthKorea #infosecurity #cybersecurity
NEW by me:
The U.S. military leaked more than 93,000 tips via insecure P3 Global Intel. Has anyone been notified?
I had reported on the school-related tips in the Navigate360 breach, and then the Crime Stoppers tips. In this post, I looked at the tips to the U.S. military.
#Navigate360 #P3GlobalIntel #databreach #cybersecurity #incidentresponse
NEW by me:
ShinyHunters escalates dispute with FBI; claims to have seized job applicants' site and acquired data
First, they threatened Clop this week, and now the FBI.
Some will disagree with me strongly, but I actually agree with ShinyHunters on some of their objections to a May 2026 FBI bulletin about them. That still doesn't excuse them hacking and extorting them, of course.
https://databreaches.net/2026/09/22/shinyhunters-escalates-dispute-with-fbi-claims-to-have-seized-job-applicants-site-and-acquired-data/
#databreach #govsec #cybersecurity #extortion #ShinyHunters #FBI #Cl0p
What's going on with ShinyHunters? First they accuse Clop of stealing their zero-day for Oracle, then they start hitting medical sector, then they deface and threaten Clop, and now we learn they ratted out TeamPCP?
Something's very different.
RE: https://cyberplace.social/@GossiTheDog/117313751385768529
I emailed Elsevier to ask whether there was any risk to any patient/healthcare data at all. They sent me a statement:
"On September 21, Elsevier identified that visitors to select platforms were being redirected to a third-party page. Our cybersecurity team responded immediately, resolving the issue and restoring normal service.
Our investigation indicates that this was a narrowly scoped, limited-duration event involving the temporary redirection of traffic for certain web properties. There is no indication that core platforms, customer data, research content, or operational systems were compromised."
Quoting

Elsevier got hacked and their website replaced with a LAPSUS$ ransomware group portal.

NEW, by me:
Silent Ransom Group Hacked Greenberg Traurig; Who notifies the 126k Affected?
GT says they notified a small number of affected clients. But more than 126,000 clients were affected.
We dug into the data tranche, obtained exclusive details from the threat actors, and asked Yelisey Bohuslavskiy for his thoughts on the group and attempts to prevent their attacks.
#databreach #infosec #cybersecurity #hack #extortion #SilentRansomGroup #SRG #GreenbergTraurig
I'm always curious to see what cyber insurers are doing on coverage for different scenarios. The Revolut incident reportedly has some insurers re-thinking. Matthew Sellers reports:
"Most social engineering endorsements are triggered by a transfer of funds, not a transfer of data. A scam where nothing is paid out but a large volume of identity and biometric data leaves the building can fall between a crime policy, built for financial loss, and a data breach policy, often built around unauthorised access rather than a fraudulent-but-convincing request. Brokers reviewing fintech and financial services clients’ wording may want to check whether “fraudulent instruction” definitions extend to information requests, not just payment instructions."
Source: Insurance Business Magazine: https://www.insurancebusinessmag.com/uk/news/cyber/revoluts-paperwork-breach-shows-why-insurers-are-rethinking-what-counts-as-a-cyber-attack-589775.aspx
#databreach #cyberinsurance #Revolut

RE: @josephcox@infosec.exchange
This may be the most horrifying and infuriating piece I've ever read about the dangers of ChatGPT. Great reporting, as always, by @josephcox@infosec.exchange and @404mediaco@mastodon.social
In January 2025, the WA attorney general sued T-Mobile over a data breach that affected 2M residents (this was the 79M T-Mobile breach). One of the issues in the litigation was that T-Mobile didn't properly notify those affected of the breach -- it omitted telling them in SMS notifications that their SSN had been acquired.
For background, see https://www.atg.wa.gov/news/news-releases/ag-ferguson-files-lawsuit-against-t-mobile-massive-data-breach
Now a court has agreed with the state that the text message notifications did not comply with the state's breach notification law:
https://www.seattletimes.com/business/t-mobile-violated-wa-data-breach-notification-law-judge-rules/
T-Mobile says it will appeal.
#databreach #incidentresponse #notifications #TMobile
NEW by me:
Navigate360 may soon release a public notice about its horrific breach, but will any individuals be notified?
#databreach #infosec #cybersecurity #incidentresponse #notification #Navigate360 #P3GlobalIntel
RE: https://mastodon.social/@brianhonan/117275280843738578
Ooh. Interesting thought, thanks. Have you come across situations in which insurers denied coverage for regulator fines but paid other incident response costs from data breaches?
Quoting
@PogoWasRight@infosec.exchange They may also want to check if the policies cover fines from regulators resulting from data breaches
Open quoted postReplying to
@realhackhistory@chaos.social Well, the threats against Nixon and Larsen really caused chaos, and leaking some USgov info. After Jubair and Flowers were arrested and detained, things calmed down a bit, but still not a good look.
Replying to
@realhackhistory@chaos.social Yeah... but I do distinguish between ShinyHunters and Scattered and Lapsus$ even though they collaborated. And if you were watching them, you may remember times when Shiny showed up and deleted a lot of their stuff or told them to knock it off. It was like herding cats or misbehaving children. And I do think that Shiny announcing they were all one was a huge mistake for ShinyHunters. He even acknowledged that to me months later.
It has been four months since a hacktivist obtained 8.3 million tips submitted to organizations such as Crime Stoppers and Sandy Hook Promise. What the hacktivist found in terms of lack of security was appalling.
In the four months since Navigate360 (the parent company for P3 Global Intel and P3 Campus) learned of the breach, they have made zero public statements after the first day when they said they were investigating. Their wall of silence, and the conspiracy of silence involving programs like Safe2Say, Safe2Tell, SilentWitness, and Crime Stoppers has been unacceptable. No one has been notified, it seems. And we cannot find any state regulator that has been notified, either.
DataBreaches wrote about the disgraceful lack of transparency in a new post this week:
Broken Promises of Anonymity: Four Months Later, Still No Transparency. Now We’re Seeking Accountability.
https://databreaches.net/2026/07/20/broken-promises-of-anonymity-four-months-later-still-no-transparency-now-were-seeking-accountability/
In conjunction with that post, I filed a formal FTC complaint against Navigate360 under Section 5 of the FTC Act and also notified the National Association of Attorneys General, saying that states should be protecting their residents by investigating the breach and incident response.
And that's not all. Today, I have filed a complaint with one state attorney general's office and will be filing with others.
I will also be publishing a post this week about the Crime Stoppers data in the dataset and the ridiculous response by legal counsel for Crime Stoppers USA to inquiries by DataBreaches about what was being done to improve security.
I have not written up anything specific to all of the Canadian data in the dataset, but yes, Canadian crime stoppers and police organizations are in there, too.
Take Action:
If you know anyone in a state attorney general's office, encourage them to read up on the breach on my site, where I have also published tables with data for easy reference.
If you know anyone in the FTC, encourage them to read the complaint I filed and to act on it.
If you know any personal injury lawyer who should be handling a massive lawsuit alleging privacy harms, point them to my coverage.
Children and adults who tried to be good citizens and relied on promises of anonymity have been put in harm's way. We cannot allow this to be minimized or covered up.
@zackwhittaker@mastodon.social @nytimes@mediastodon.com @caparsons@mastodon.social @douglevin@infosec.exchange#databreach #infosec #Navigate360 #CrimeStoppers #Safe2Tell #Safe2Say #SilentWitness #SandyHookPromise #transparency #notification #NAAG #FTC
The city manager of the City of Coweta is refusing to even contact unnamed threat actors and says the city will not pay any ransom in response to a recent ransomware attack.
Why? Because the city manager was with another city that was attacked; even though that city paid the ransom, it was reinfected two weeks later. So now she is very anti-paying.
Read more at KTUL:
https://ktul.com/news/local/city-of-coweta-refuses-to-pay-ransom-after-system-wide-cyberattack-08-08-2026
And as I previously reported on this incident, the city has an offsite backup they say they can use to restore all city files after they clean the servers of ransomware.
Good for her and the city.

"Marco Rubio says the US will deny visas to foreign nationals involved in cybercrime and may extend the restrictions to their immediate families.......... Marco Rubio says the US will deny visas to foreign nationals involved in cybercrime and may extend the restrictions to their immediate families." (see on The Register)
Why not allow the suspected criminals to get visas, allow them to fly over here, and then arrest them and prosecute them?
Replying to
I wish this wasn't being handled in a partisan way. Surely Democrat and Republican state attorneys general can agree that questions need answers about this incident. I really wish they had collaborated on this one.
TFW you finish entering all your new appointments for this week, only to realize you entered them in last week's calendar and now mucked everything up. 😭 🤦♀️
One of the dozens of new #ransomware groups this year is a group calling itself #Orova. Since early May, they appear to have dozens of victims in about half a dozen countries.
Three of the listings are U.S. medical entities, so, of course, I reached out to them to find out more.
My new report:
Cardiology Associates of Port Huron remains silent although they were allegedly hacked and had patient data stolen in June.
#databreach #healthsec #cybersecurity #extortion #encryption
GovTech reoorts on the ITRC's H1 report:
"[ITRC]found that 1,029 data compromises generated 471 million breach notices in the first half of the year, with one incident — the breach involving Instructure’s Canvas platform — accounting for 275 million of those notices, or about 58 percent of the total."
More than 30 Minnesota water systems targeted in cyberattack:
https://www.fox9.com/news/30-minnesota-water-systems-targeted-cyber-attack
I haven't seen Handala or any group claim responsibility yet, but it's noteworthy that the quality of drinking water does not appear to have been tampered with.
#cyberwar #Handala #criticalinfrastructure #water
Developing: AnMed reports phone and internet outage impacting all 4 hospital locations in South Carolina and Georgia. Emergency rooms remain open.
No group has claimed responsibility as yet.
#cyberattack #healthsec
NEW by me: more analysis of the Navigate360 data breach, this one focusing on Crime Stoppers and crime-oriented tip lines using P3 Global Intel:
Crime Stoppers assured people their tips would be anonymous. Then more than 1 million tips leaked:
https://databreaches.net/2026/07/24/crime-stoppers-assured-people-their-tips-would-be-anonymous-then-more-than-1-million-tips-leaked/
If anyone has a connection in their state attorney general's office, encourage them to read this and open an investigation. A table in the article shows how many tips were submitted for each chapter of Crime Stoppers that appeared in the dataset.
#databreach #cybersecurity #infosec #Navigate360 #CrimeStoppers@zackwhittaker@mastodon.social @campuscodi@mastodon.social @jgreig@ioc.exchange @douglevin@infosec.exchange @ajvicens@mastodon.socialspill.com
RE: https://infosec.exchange/@chum1ng0/117044228483502361
You weren't alone, @chum1ng0@infosec.exchange . Their misclassification reportedly affected thousands of blogs:
https://cybersecuritynews.com/google-blogger-locked-legitimate-websites/
But this is a good time for you to think about backups and alternatives. :)
Milford, New Hampshire seems to be dealing with a cyberattack since July 15, but they don’t call it that and haven’t revealed many detail details. A resident wonders whether the breach was caused by a vulnerability he reported to them in May that they did not address. My post about it all:
https://databreaches.net/2026/07/21/milford-new-hampshire-confirms-unauthorized-activity-withholds-details-of-suspected-cyberattack/
#govsec #cybersecurity
Replying to
@sawaba@infosec.exchange @adamshostack@infosec.exchange Ah. Well, this is on YOU, then, of course. :)
It's fantastic that you had the foresight to start this years ago and that you maintain it. It really is a great resource for any journalist or researcher who wants to fact-check claims about the consequences of breaches.
Replying to
@sawaba@infosec.exchange @adamshostack@infosec.exchange That was my sense, too. Chapter 11 equivalence.
Maybe you should have a Chapter 11/insolvency/wounded but not dead sheet. Because how do we know that a company ever successfully bounces back and doesn't wind up dead after all?
New York State Department of Financial Services announced on August 5 that Order Express, Inc., a licensed money transmitter, will pay a $250,000 penalty for violations of DFS’s cybersecurity regulation (23 NYCRR Part 500).
Order Express suffered a ransomware attack in 2022, which they reported appropriately. But then the DFS's investigation revealed that the entity did not have adequate cybersecurity risk assessment or plan.
Read more at: https://www.dfs.ny.gov/reports_and_publications/press_releases/pr20260805
#NYSDFS #OrderExpress #databreach #cybersecurity #FinSec #ransomware #riskassessment
Replying to
@hnapel@mastodon.social That's somewhat lost on me... I never really watched that show more than once or twice. All I remember about it was that there was something about apple pie?
Replying to
@chum1ng0@infosec.exchange Yes, Chu, you need to appeal and say there is NOTHING in your blog posts that is malware or any malicious content. Tell them to have an informed human being read the posts and they'll confirm that.
@javilopezg@mastodon.social
Replying to
@chum1ng0@infosec.exchange Those complaints/reports show that Blogger has a false positive problem/issue.
Add your report to it and appeal the blocking.
Replying to
@chum1ng0@infosec.exchange I think they made a mistake. And if they don't undo the block, maybe look at this page to get free help:
https://www.trust.org/our-services/legal-services-for-media/
Replying to
@chum1ng0@infosec.exchange Not necessarily. Might be a script looking for certain words type of thing.
Replying to
@chum1ng0@infosec.exchange I responded to your message on Signal, but let's keep this here because it may be a press freedom/ free speech issue.
What blog/platform banned your blog? And what reason did they give?
And do you have a complete backup that you can upload elsewhere?
As I mentioned the other day, there are free legal resources and help for independent media, but first explain more about what happened and why.
#pressfreedom @freespeech #censorship
(For those of you who don't know, Chu used to report LatAm breaches on DataBreaches.net. It's hard for me to imagine how he would get banned for the kind of reporting he does, but... let's find out. )
Replying to
@chum1ng0@infosec.exchange OK, so you clearly should file an appeal and tell them that although you report about data security incidents, you never include malware or malicious content and to please re-read your posts.
Replying to
@husjon@fosstodon.org I dunno, but I wouldn't be surprised if Trump sued OpenAI for 43 billion dollars or something....
Replying to
@fuzzyfuzzyfungus@cyberplace.social From what I am reading, Democrat attorneys general were not asked to participate or even review the letter. This was apparently intended to be partisan.
Replying to
ShinyHunters says the May attack wasn't them or SLH, so I corrected my post on that point.
@bobdahacker@infosec.exchange @campuscodi@mastodon.social
Replying to
@douglevin@infosec.exchange @funnymonkey@freeradical.zone
Instructure's most recent update even tells schools that if they discover notifications need to be sent, to contact them and Instructure will make the notifications via Kroll, so yes, it looks like not all notifications have been made. I wonder if ITRC used the "275 million" number from ShinyHunter's leak site claims or some other source.
Replying to
@adamshostack@infosec.exchange @sawaba@infosec.exchange My fault. I probably should have mentioned him at the top instead of the bottom.
Replying to
@octothorpe@mastodon.online (1) if they're employees for tax records, (2) for customers who want to finance a phone and they'll do a credit check, and (3) to verify identity if people call with a support request.
4).... ??? I dunno.
Replying to
@amvinfe@infosec.exchange I have no idea what to make of all that. Do you believe any of it?
Replying to
@cwbussard@ioc.exchange are you having trouble with the RSS feed? Email me your IP address address and I’ll whitelist it. Unfortunately, the. CF remains necessary because I continue to get DDoS attacks when I drop it.
Replying to
RE: https://chaos.social/@realhackhistory/117300415989405928
@realhackhistory@chaos.social So the shift in behavior I notice with ShinyHunters has also been seen in other groups. It seems to me that we should be paying more attention to this to figure out how to use it to aid in disruption, and not just write it off as so many kids being "nuts."
Quoting

@PogoWasRight@infosec.exchange I’d also say this needs to be viewed against the backdrop of increased rivalry in the ransomware / extortion scene, less victims are paying and the groups are at each others throats. DragonForce has defaced other groups extortion blog sites in the past for instance, and Russian groups have threatened each other publicly of late in ways they would not previously have.
Open quoted postReplying to
@realhackhistory@chaos.social Did you see the 2020 - 2023 ShinyHunters as "nuts?"
Replying to
@realhackhistory@chaos.social In them, no. Monitoring them, yes. And of course, they ultimately claimed it was all a big disinformation and distraction ruse.