Remote
Catalin Cimpanu
@campuscodi@mastodon.social
Cybersecurity reporter for Risky Business
0 Followers
0 Following
50 Posts
Joined September 10, 2017
Newsletter::
Podcast::
Boosted by @trending@homestead.social
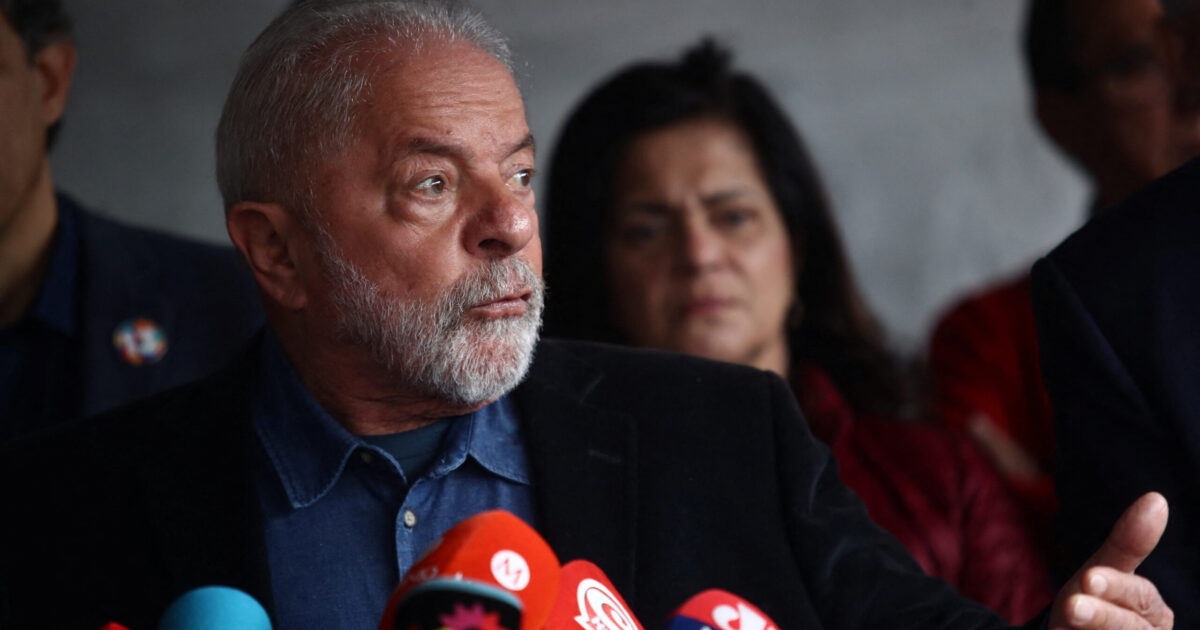
Social media giant Meta pulled down Brazilian President Lula's Facebook page and blocked his campaign from running political ads but allows paid ads calling for a military coup
It also didn't take down any of the right-wing disinformation campaigns reported in August
https://novaramedia.com/2026/09/28/facebook-blocks-lulas-campaign-ads-just-days-before-brazil-election/
Open post
Boosted by @trending@homestead.social
RE: https://techhub.social/@Techmeme/117373191633975809
The "clashing work styles" being privacy and security, from the company that's suppose to self-regulate its AI models
Open quoted post
Quoting
Meta says it is letting go of employees it hired from AI safety startup Virtue AI four months after they joined the company, citing clashing work styles (Ashley Gold/Semafor)
https://www.semafor.com/article/10/02/2026/meta-parts-ways-with-virtue-ai
http://www.techmeme.com/261002/p23#a261002p23
Open quoted post 18
0
31
0
Open post
Two days until everyone becomes hyper aware of cybersecurity
49
7
30
1
Open post
NSA announced it is accelerating it's PQC timeline 👀 👀 👀
All systems must be PQC hardened by the start of next year
All legacy systems that don't support PQC must be phased out by 2030
https://www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Release-View/Article/4615285/nsa-announces-post-quantum-cryptography-measures-to-safeguard-national-security/
9
0
15
1
Open post
Boosted by @trending@homestead.social
The Irish Presidency of the EU has proposed member states to allow AI companies unfettered access to the data of EU citizens.
According to leaked docs, the proposal would effectively exempt AI companies from any of the GDPR rules and deny EU citizens data protection rights
https://noyb.eu/en/ai-eu-member-states-plan-digital-expropriation-europeans-interest-ai-companies
88
0
180
1
Open post
That Reddit rumor about Citrix notifying customers to take Netscaler servers offline because of actively exploited zero-days is apparently real: https://www.reddit.com/r/Citrix/comments/1wqjk9a/netscaler_leak/
Confirmation 1: https://mastodon.social/@GossiTheDog@cyberplace.social/117339185245199481
Confirmation 2: https://www.linkedin.com/feed/update/urn:li:activity:7509660925809819649/
9
2
6
0
Open post
The OpenAI hack of Australia's Medicare is a watershed moment in the history of the internet and the perfect time to improve your sales strategies!
Here's 10 ways you can do it (1/11)
12
1
5
0
Open post
"AI-powered probes targeted Canadian and US government sites, with officials reporting no evidence of successful breaches"
https://www.verdict.co.uk/canadian-website-ai-hacking-attempts/
3
0
7
1
Open post
Replying to
@GossiTheDog@cyberplace.social watchTowr seems to say it's real
https://x.com/watchtowrcyber/status/2103894423222309027
5
1
2
0
Open post
North Korea is now using female operatives as part of its remote IT workforce groups
https://haydenmckenzie.com/research/dprk-it-worker-cell-part-one
4
0
4
0
Open post
Boosted by @gvenema@fairmove.net
-Major vulnerability found in ancient TACACS+ networking protocol
-OpenAI agent hacked Australian Medicare website
-Three other OpenAI incidents
-OpenAI gives Ukraine access to Daybreak
-UK to establish anti-disinformation center
-Hackers take over LNG cargo ship heading to Italy
-Hacker claims new Canva breach
-Four crypto-heists steal $17m
-Stolen FBI data includes sensitive work assignments
-New Europol boss proposed
P: https://risky.biz/RBNEWS615/
N: https://news.risky.biz/risky-bulletin-major-vulnerability-found-in-ancient-tacacs-networking-protocol/
5
0
6
0
Open post
Boosted by @gvenema@fairmove.net
-Intel ends paid bug bounties
-OpenAI agents probed dozens of organizations
-Fraudsters use AI to scam €95m from an Italian bank
-Bitget hacked for $350m
-Hackers breach Poland's Medyc platform
-Data breach at the Pentagon DMDC
-OpenAI brute-forced UN website API
-DIVD says it was hacked by an AI
-Hackers extort Flink customers for €10
-Cyberattack hits Wales police force
-Asus store breach
-TapClicks ransomware attack
-WebRezPro hack
N: https://news.risky.biz/risky-bulletin-intel-ends-paid-bug-bounties/
P: https://risky.biz/RBNEWS616/
3
0
8
0
Open post
Bruh... there's a "master key" that grants access to every Cosmos DB on Azure? Wut?
https://www.wiz.io/blog/cosmosescape-taking-over-every-database-in-azure-cosmos-db
106
20
116
2
Open post
Google has removed a cluster of Chrome extensions from the Web Store that enrolled user browsers into a web-scraping botnet
Security firm Spur says the number of Mellowtel proxy nodes fell from 90,000 to 18,000 after Google's action
https://spur.us/blog/mellowtel-browser-extensions-proxy-network
5
0
9
0
Open post
Boosted by @gvenema@fairmove.net
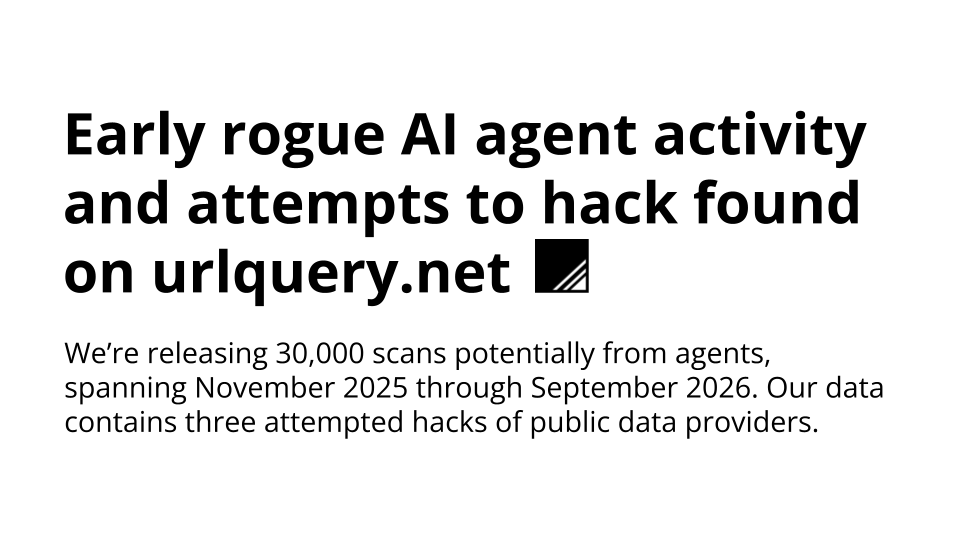
Three new OpenAI hacks come to light:
-Data USA
-University of New Mexico
-Australian Institute of Health and Welfare
https://transluce.org/agent-activity
4
0
7
1
Open post
RE: https://mastodon.social/@campuscodi/117365393830105700
According to Transluce, the probes targeted the Library and Archives Canada, a Canadian federal agency.
Government statement: https://www.cyber.gc.ca/en/news-events/statement-regarding-reported-activity-targeting-government-canada-websites
Transluce report: https://transluce.org/us-canada-gov
Open quoted post
Quoting
"AI-powered probes targeted Canadian and US government sites, with officials reporting no evidence of successful breaches"
https://www.verdict.co.uk/canadian-website-ai-hacking-attempts/
Open quoted post 1
0
3
0
Open post
Boosted by @oxy@social.bsdlab.au
More than 540,000 creds, valid and working, were found in public GitHub repos in a scan this July.
More than 200,000 were uploaded even after GitHub turned on a security feature to catch them from being sent to public repos
https://trufflesecurity.com/blog/github-repos-exposed-543699-credentials-nobody-revoked-them
1
0
1
0
Open post
New RemControl Android banking trojan spotted in the wild
RemControl devs tricked an AI coding assistant that it was creating a parental monitoring application but used the code for the trojan's backend servers
https://www.group-ib.com/blog/remcontrol-android-banking-trojan/
2
0
5
0
Open post
RE: https://mastodon.social/@campuscodi/117316476631238314
And now an F5 BIG-IP zero-day too:
https://my.f5.com/manage/s/article/K000162605?mkt_tok=NjUzLVNNQy03ODMAAAGkaH9ofwJ_SRrYgVTlugDrbGmtsu1nH57-t7CLkyTTdZHlyphUFNtULl3ACEteoRszBciQ_4gjkNsWTnQqQfftwYMNCzWPXxGhUqTJ-emmdyUmrf_dqfI
Open quoted post
Quoting
Check Point has disclosed a zero-day (in Security Management Server) and marked an older bug also as exploited in the wild (in Site-to-Site VPN)
https://blog.checkpoint.com/security/security-advisory-action-required-active-exploitation-of-cve-2026-85102-and-a-management-pre-authentication-vulnerability-cve-2026-93616/
Open quoted post 2
0
4
0
Open post
New FBI alert warns that Chinese AI companies are carrying out "industrial-scale knowledge distillation campaigns" to steal the "proprietary functionalities and capabilities of U.S. AI companies’ models"
PDF: https://www.ic3.gov/CSA/2026/260908.pdf
6
1
6
0
Open post
Replying to
RE: https://infosec.exchange/@watchTowr/117339663892945669
@mttaggart@infosec.exchange
More: https://mastodon.social/@watchTowr@infosec.exchange/117339663929597181
Open quoted post
Quoting
RE: https://infosec.exchange/@watchTowr/117338396418850285
We have been made aware of further info, which we are sharing. We had no idea Citrix sysadmins were like GTA6 fans - so friendly 🤗
Please, direct further questions to Citrix. We are not Citrix PSIRT (despite it occasionally looking that way).
Citrix comms & patches are expected early next week.
Two vulnerabilities - both RCE.
Unpatched, 0days.
Exploited in-the-wild - discovered during forensics.
As always, watchTowr Platform customers have access to this information and already have the information needed to reduce exposure.
Open quoted post 1
0
3
0
Open post
The Snowflake hacker, a former Army soldier, was sentenced to 70 months in prison
https://www.justice.gov/opa/pr/former-us-soldier-sentenced-hacking-and-extortion-scheme-exposed-sensitive-data-us
1
1
3
0
Open post
Hackers breached a third cargo ship, one that loaded in New Orleans and was traveling to Italy
It's now docked in Spain after hackers breached systems involving tank pressure, safety valves and boil-off gas management
https://neworleanscitybusiness.com/blog/2026/09/22/louisiana-lng-tanker-cyberattack/
1
0
4
0
Open post
"Google's Gemini AI hacked three companies in security test"
Took Gemini a while... finally popped its cherry
https://www.bbc.com/news/articles/c607l0k72rlvo
1
0
1
0
Open post
The US National Security Agency is working to gain access to all AI models available on the commercial market
https://www.nextgov.com/artificial-intelligence/2026/08/nsa-wants-access-all-ai-models-top-official-says/415672/
4
1
11
0
Open post
-Meta's AI joins Anthropic and OpenAI in the hacky-hacky
-AISI also loses track of AI models in a test
-Cyberattack disrupts North Carolina ports
-The Philippines will establish a cybersecurity agency
-Ransom Cartel admin gets 16 years
-Hackers target US hedge funds
-Panama Metro sees cyberattack
-Italy makes room for military cyber units
-China launches Palo Alto Networks probe
-Indiana establishes cybersecurity office
N: https://news.risky.biz/risky-bulletin-metas-ai-joins-anthropic-and-openai-in-the-hacky-hacky/
P: https://risky.biz/RBNEWS597/
4
0
6
0
Open post
Beacon CRM got hacked
Many orgs are now disclosing downstream breachs
https://www.bbc.com/news/articles/cr7km34z112o
https://www.artsprofessional.co.uk/news/breaking-scores-of-cultural-organisations-affected-by-possible-data-breach-after-cyber-attack
https://www.cse.org.uk/news/beacon-crm-incident/
4
0
8
0
Open post
Live streams from the BSides Las Vegas 2026 security conference, which is taking place this week, are available on YouTube
https://www.youtube.com/@BsideslvOrg/streams
3
0
8
0
Open post
Boosted by @gvenema@fairmove.net
The Silent ransom group made $28m in just two attacks
≖‿≖
https://bsky.app/profile/raphae.li/post/3msjcgdmqxk2h
2
0
5
0
Open post
The US government has banned the import of foreign-made robots and power inverters on the grounds of national security
Most of these products are produced and imported from China
https://www.fcc.gov/document/fcc-adds-foreign-produced-power-inverters-and-robots-covered-list
2
1
3
0
Open post
The number of Minnesota towns that reported hacks of their water systems is up to four
-Braham: https://dysruptionhub.com/braham-minnesota-water-cyberattack/
-Maple Plain: https://dysruptionhub.com/maple-plain-water-cyber-incident/
-Plymouth: https://dysruptionhub.com/plymouth-minnesota-water-cyberattack/
-St. Paul: https://dysruptionhub.com/south-st-paul-water-cyber-incident/
2
0
3
1
Open post
Microsoft will reduce NuGet API keys lifespan from 365 to 30 days
-change enters into effect August 17
-On November 1, Microsoft will invalidate all old NuGet API keys created before August 17.
-shorter lifespan is meant to counter supply chain attacks
https://devblogs.microsoft.com/dotnet/strengthening-nuget-supply-chain-security-reducing-api-key-lifetime/
1
1
3
0
Open post
Replying to
-Fake IRS letters target crypto users
-INC adopts SonicWall zero-day
-DarkSword spreads to 8 groups
-Far-right image board builds AI doxing tool
-New NullReceiver C2 technique
-New Fuyao ad fraud botnet
-New OctLurk and SilkLurk malware
-Storm-1516's Armenia campaign
-KindaRails2Shell vulnerability
-RufRoot vulnerability
-Apple introduces bug reporting cool-offs
-WaterISAC denounces leak
1
0
2
0
Open post
Replying to
-UK rejects Bahrain state immunity claim
-Wyden urges phasing out old VPNs
-Russia arrest smisher
-Hong Kong arrests SMS blaster
-Ariana Grande sues hackers
-Victims sue Apple over fake wallet app
-Joyfill supply chain attack on npm
-Binance is hindering law enforcement investigations
-New Work Panel vishing kit
-AngrySpark spyware intersects with Op. Triangulation
-New Tengu and Dysphoria botnets
-New MedusaHVNC and Flying Eagle RATs
1
0
1
0
Open post
Boosted by @gvenema@fairmove.net
-Sanctions impact TLS certs in Iran, Russia
-ShinyHunters member arrested in the Netherlands
-Apple fixes iOS zero-day found by Meta
-Citrix zero-days see mass exploitation within hours
-Hackers exploit security product in Bitget hack
-Belnet hacked
-Arizona courts hit by cyberattack
-MEP sues NSO over hacks
-Pentagon unleashes Cyber Command on election threats
-Agencies sabotage GAO's DOGE investigation
-China expands AI travel bans
P: https://risky.biz/RBNEWS617/
N: https://news.risky.biz/risky-bulletin-sanctions-force-cas-to-revoke-tls-certs-in-iran-russia/
0
0
1
0
Open post
Mozilla rotates GPG signing subkey for official Firefox and Thunderbird releases after the previous one leaked (it was inadvertently committed to a private GitHub repository)
https://blog.mozilla.org/security/2026/08/10/updated-gpg-key-for-signing-firefox-and-thunderbird-releases/
0
0
0
0
Open post
Check Point has disclosed a zero-day (in Security Management Server) and marked an older bug also as exploited in the wild (in Site-to-Site VPN)
https://blog.checkpoint.com/security/security-advisory-action-required-active-exploitation-of-cve-2026-85102-and-a-management-pre-authentication-vulnerability-cve-2026-93616/
0
0
3
1
Open post
RE: https://mastodon.social/@campuscodi/116999208190841327
Make that 30+ now:
https://mn.gov/mnit/media/blog/?id=38-761869
Open quoted post
Quoting
The number of Minnesota towns that reported hacks of their water systems is up to four
-Braham: https://dysruptionhub.com/braham-minnesota-water-cyberattack/
-Maple Plain: https://dysruptionhub.com/maple-plain-water-cyber-incident/
-Plymouth: https://dysruptionhub.com/plymouth-minnesota-water-cyberattack/
-St. Paul: https://dysruptionhub.com/south-st-paul-water-cyber-incident/
Open quoted post 0
1
1
0
Open post
Replying to
-The mysterious hack at the Zeus crypto-wallet
-Meta on the hook for $567m
-Bytedance is working on a cyber AI model
-AI code contributions are growing
-AI-generated code patches such, though
-All 2027 RAM already sold
-Amazon to build humongous data center
-Meta caught paying Nazis
-ENISA CVE program expands
-Lesotho sets up CSIRT
-Hegseth announces CYBERCOM 2.0
-Trump admin pulls election security funding after conspiracy theories are not confirmed
-New US cyber ambassador approved
0
1
1
0
Open post
Replying to
-Anthropic claims it cracked encryption algorithms
-Chrome 151 is out
-WhatsApp Web Calling is out
-EU extends DSA to Roblox and ChatGPT
-Russia blocks Bip and KakaoTalk
-Saudi Arabia blocks Tinder
-Australia to investigate Telegram
-New ODNI chief
-Romance scammer sentenced to 85 months
-Applicant gets a second chance after hacking Indian universities
-New AUR supply chain attack hits Arch Linux
-SonicWall cred-stuffing attacks
-SilverFox is still active despite arrests
0
2
2
0
Open post
ShinyHunters breached Cl0p and is demanding all the money Cl0-p made from the Oracle EBS hacking campaign
0
0
3
1
Open post
Russia's Sandworm follows North Korea and Iran and adopts the fake IT job interview as a malware delivery vector
https://cert.gov.ua/article/6318863
0
0
3
0
Open post
Replying to
-New Zealand issues new Russian (cyber) sanctions
-Data recovery firm execs get prison time for ransomware scheme
-Storm-1175 moves from Meduza to StormCrypter
-Kimsuky adopts AI
-Head Mare attacks TrueConf servers
-Kimi escapes test environment
-N-able issues additional zero-day patch
-New Kemp LoadMaster attacks
-RovoBlast, SCTPhantom, KerberLoss, and ResetNightmare vulns
-New NatJack attack
-New CSS attack steals your inbox and passwords
0
0
1
0
Open post
Coinkite has destroyed all its inventory of Coldcare hardware crypto-wallets after hackers exploited a bug in existing devices to steal close to $100 million from user offline hardware wallets
https://blog.coinkite.com/update-sunday/
0
0
0
0
Open post
Hackers are using a new zero-day to take over Adobe Commerce and Magento online stores.
A successful attack allows attackers to start a backdoored background process on hacked stores
https://sansec.io/research/stylesmuggler
0
0
6
0
Open post
Replying to
-New GenieLocker ransomware
-LogoKit and ARToken PhaaS
-Lots of DPRK APT reports
-Laundry Bear linked to recent Exchange zero-day
-New Cisco zero-day
-MikroTik brute-force bug
-New Copilot Word worm
-CosmosEscape vulnerability impacts Azure's CosmoDB
-Vulns in Volvo's fleet portal
-Okta buys Permiso Security
-DEFCON bans smart glasses
-New SBOM guidance
-OpenAI releases Codex Security CLI
0
0
0
0