Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Lee Holmes :donor:

@Lee_Holmes@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Partner Security Architect, Azure Security. Co-author of Threat Driven Software Development (https://www.amazon.com/Threat-Driven-Software-Development-Defending-services/dp/0135567386) and author of the PowerShell Cookbook (https://www.amazon.com/PowerShell-Cookbook-Scripting-Ubiquitous-Object-Based/dp/109810160X). OG PowerShell developer, and fanatical hobbyist.

108 Followers
341 Following
50 Posts
Joined November 08, 2022
Blog:
https://www.leeholmes.com
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 1w ago
Learned about this the other day - game changer! A locking trucker's hitch is basically a rachet strap made out of cord. You can use this for tying up packages neatly, tarps, whatever you want. Amaze! https://www.youtube.com/watch?v=oNsuvZOI-0U

Automatic Trucker's Hitch (Tension Locking)

2
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 1w ago
Replying to
@ajn142@infosec.exchange Yeah, I think the innovative uses come from places where you're not lashing down a load. For example, tying a package or other scenarios where people tend to use a shoelace knot.
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to
@catsalad I did this in stone :)
79
0
16
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2w ago
Replying to
@winterknight1337@infosec.exchange A pen testing organization out of Brazil eh? Certainly seems like it 🤔
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
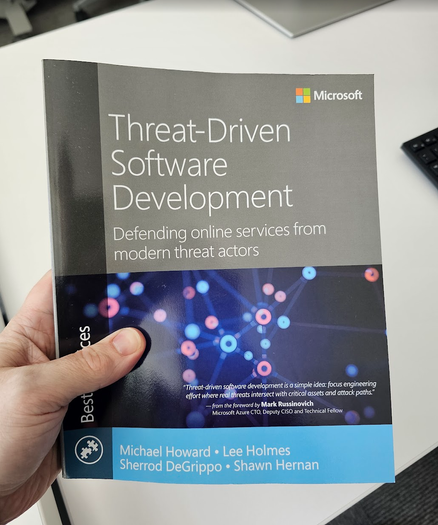
It's here! Super proud of this - it is such a perfect package of how to navigate operational security in the services world.
14
1
4
1
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Got to fly with the Blue Angels today :)
8
2
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3w ago
Replying to
@adamshostack@infosec.exchange Hope you like TDSD! One part I think you'll really dig is the concept of the Security Weakness Bug Bar to help target lines of questioning (and ranking of risks) during Threat Modeling.
1
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Ok, finally captured some thoughts about our new book, Threat Driven Software Development here: https://www.leeholmes.com/threat-driven-software-development/ If you are a Blue Teamer working on developing or securing online services - this is your jam and I hope you enjoy it.
leeholmes.com

Lee Holmes | Threat Driven Software Development

4
2
3
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3mo ago

Saw Disclosure Day yesterday - it's now solidly in the list of top films of all time to use PowerShell 🥳🥳🎉🎉🎉!

8
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to on social.scriptjunkie.us
@sj@social.scriptjunkie.us Gross. They also invented renting your car's features to you. And this is just the visible money grubbing... If they're doing this, they're probably selling every bit of customer data and car telemetry they have to the lowest bidder too.
3
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Shout out to my homies that still remember the track numbers on the CDs for their favorite songs.
16
0
4
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
RE: https://infosec.exchange/@Lee_Holmes/116925875891679749 Woohoo! Now available at your favorite retailers! https://www.amazon.com/Threat-Driven-Software-Development-Defending-services/dp/0135567386
Open quoted post
Quoting
Lee Holmes :donor:
@Lee_Holmes@infosec.exchange
It's here! Super proud of this - it is such a perfect package of how to navigate operational security in the services world.
Open quoted post
infosec.exchange

Lee Holmes :donor:: "It's here! Super proud of this - it is such a per…" - Infosec Exchange

4
3
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
You've probably been in the situation of weighing the difference between buying something commercially or making it yourself -- and then stumbling on a YouTube of somebody where this is clearly their passion. They've got dozens of videos of how to use these things. Make these things. Perfect these things. This is all they think about, and they also have a little store or Etsy where they sell what they make. The more I think about it, the more I realize: this is exactly the time to Support the Maker. For a small cost over what it would take to do this yourself, you can help somebody pursue their passion. Consider it a thank you. Consider it payment-in-kind for all those videos you just binged. But the world needs more of these people, and this is how you can support them.
3
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
I know it was fashionable for a while for infosec to mock people that use VPNs (ala "Hello, it's 2026. Everything worth securing is transmitted over TLS anyways") but I still think it's an immature absolutist take. TLS doesn't save you when Russia hacks the routers in your hotel to send you to phishing sites rather than actual login pages: https://www.bleepingcomputer.com/news/security/authorities-disrupt-dns-hijacks-used-to-steal-microsoft-365-logins/
bleepingcomputer.com
3
4
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Application Security is an investment. Operational Security is a commitment. This quote comes from Threat Driven Software Development: I think it perfectly captures the difference between application security and operational security when it comes to services.
3
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to

@malwaretech One of the things I love about this investigation is that it actually imposed cost:

  • Found malware: reported to AV vendors
  • Saw abuse of Cursor: reported to Cursor, got the accounts suspended
  • Saw abuse of ChatGPT: reported to OpenAI
  • Saw that a front website was implemented / hosted on Anima: reported to Anima, got the account suspended

Props on engaging like that.

12
1
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Ok, here's the answer to the question that's always on your mind: what treats should you buy when you visit Canada? https://www.leeholmes.com/what-treats-to-buy-in-canada/
leeholmes.com

Lee Holmes | What Treats to Buy in Canada

2
5
2
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@lcamtuf@infosec.exchange I think we're going to find some interesting social norms coming out of this. I just finished writing a book: zero AI for exactly the point you made. But I also just generated an architecture / design doc and fully used AI for it because -- let's be honest -- nobody cares about the prose in those as long as it's correct. People will send transactional email at work that was clearly AI-assisted and I'm not sure how I feel about that.
3
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@Sempf@infosec.exchange Don't forget the chai!
1
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@mkb@mastodon.social It doesn't look like Amazon is offering it on Kindle yet, but the MS Press store does have eBook.
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@culturednyc@mastodon.social Oooh, great catch. Thank you!
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@Sempf@infosec.exchange Hell yes. It's on the list.
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3mo ago
Replying to
@lcamtuf@infosec.exchange I learned about a YouTube niche for AI-generated "hard done by" revenge stories the other day... many of them with hundreds of thousands of views and a replies section that apparently thinks it's all true. WTF. Like https://www.youtube.com/watch?v=cJ9-PFcbfro
2
2
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3mo ago

I've never liked Schneier's phrasing of this: "Anyone, from the most clueless amateur to the best cryptographer, can create an algorithm that he himself can’t break.". You can't repeat it to somebody that you think it applies to when you want to use it for advice. It's really only good for dunking.

But the advice itself is super solid. Here's a rephrasing that I was actually able to use with somebody and not feel guilty: “Anyone, from beginner to expert, can create an algorithm that they themselves cannot break."

2
0
2
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@ajn142@infosec.exchange The latter.
1
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago

Was on the Microsoft Threat Intel Podcast recently with Sherrod, Michael, and Shawn about our new Threat Driven Software Development book. It was really great to have the chance to talk about the whole book end-to-end - https://thecyberwire.com/podcasts/microsoft-threat-intelligence/73/notes

Behind the Book: Threat-Driven Software Development
N2K CyberWire

Behind the Book: Threat-Driven Software Development

In this episode of the Microsoft Threat Intelligence Podcast, host⁠ ⁠⁠⁠Sherrod DeGrippo⁠ is joined by co-authors Michael Howard, Lee Holmes, and Shawn Hernan for a discussion on their new book, ⁠Threat-Driven Software Development: Defending Online Services from Modern Threat Actors.⁠ Together, they explore how security teams and software developers can build more resilient systems by understanding how real-world threat actors operate. From threat modeling and operational security to the evolv

1
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@spacerog@mastodon.social You're forgetting some other important history - https://www.microsoft.com/en-us/msrc/blog/2010/07/coordinated-vulnerability-disclosure-bringing-balance-to-the-force
microsoft.com

Coordinated Vulnerability Disclosure: Bringing Balance to the Force

1
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

RE: @malwaretech@infosec.exchange

One of the things I love about this investigation is that it actually imposed cost:

- Found malware: reported to AV vendors
- Saw abuse of Cursor: reported to Cursor, got the accounts suspended
- Saw abuse of ChatGPT: reported to OpenAI
- Saw that a front website was implemented / hosted on Anima: reported to Anima, got the account suspended

We don't have to just report on the bad guys. We can actually fight them.

infosec.exchange
4
0
2
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@medwds@infosec.exchange I really love the heavy blue influence (Blue Team) as well as the graph symbolism (= the way that attackers and defenders should think of systems).
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to
@agreenberg@infosec.exchange Auto-buy. Can I just give you my credit card and you automatically send me every book you write?
4
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Just had an internal web application break, and when I dug in through DevTools there was some dependent fetch running into a server error. The server error message provided the internal DRI contact to reach out to for how to engage and report.

This is so. smart. If you've figured out the DRI contact by going through DevTools, you clearly don't need any central helpdesk support on basic troubleshooting like checking your adblocker.

Makes me think of @shanselman@hachyderm.io 's "FizzBin" - https://www.hanselman.com/blog/fizzbin-the-technical-support-secret-handshake

FizzBin - The Technical Support Secret Handshake
hanselman.com

FizzBin - The Technical Support Secret Handshake

This is a short post, but I think it's important. Let's make it a movement. ...

4
0
2
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

LOL, you think reading it takes a lot of effort - try writing it 🤣

3
1
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to
@adamshostack I think the answer should be "Defensive Design Patterns." Good security architects have built up a bank of these in their head: "It looks like you're writing an updater! Here are some best practices around that." Once somebody makes that connection that they are writing an updater, they can always search the internet (or ask AI) for the best practices part - but having that lightbulb moment is not guaranteed.
3
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3mo ago
There's a famous joke: "I took one of those rapid-reading courses, and was able to read “War and Peace” in 20 minutes! It’s about Russia. Beyond that, I’m vague.” I thought it'd be funny to write a map-reduce algorithm to have LLM summarize the book into 10 words. OpenAI refused to play along 🤣
1
4
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to
@Aaron@front-end.social This is smart. Browsers should do this by default! I had discussions with one browser manufacturer at one time, and they were like "But the edge cases!" and it was clear that they didn't care about users enough.
3
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Where the hell did irm-iex-ing come from? As in "irm | iex"

Invoke-RestMethod in PowerShell has ALWAYS been a way to get objects out a website that exposes content as JSON, XML, etc.

Invoke-WebRequest is the one that gives you raw text back.

The fact that tools using irm-iex work at all is just a magic accident that converting an object (that's a string) into a string doesn't introduce any artifacts.

3
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Startup: Look at how agile we are! How quickly we can pivot!

2
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Here's one thing AdTech could do to instantly change the content dynamics of the internet: "Unvisit."

Landed on an AI slop page laden with ads and referral links? Click "Unvisit" and they'll never see a penny from your impression.

Got ambushed by a page full of taboola ads and auto-play videos? Unvisit. Can't use the back button? Unvisit.

Unvisit, Unvisit, Unvisit, and punish them where it hurts.

2
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Love this compilation of "The Defender's Mindset" from John Lambert. John does a lot of hiking and clearly occupies that time figuring out how to phrase things perfectly: @johnlatwc@medium.com

medium.com
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago

Holy smokes! Upgraded to a GAN speed cube with magnetic registration, and it knocked 30 seconds off of my solve time (~ 2 minutes to 1:30) compared to the classic Rubik's Cube model. It's also more fun to use!

1
0
1
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to
@lcamtuf@infosec.exchange Congrats!
1
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@azonenberg@ioc.exchange OOOOH, make two of the traces output oscillofun
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3mo ago

@campuscodi@mastodon.social The article is saying that it wasn't digital dynamite, it was something else unspecified (dormant cyber pathogens rearing their ugly head again?) to be used at a later time 🤣
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@Blueteamsherpa@infosec.exchange By flying a drone :) I'm pretty sure they were stoked about flying formation with me. It was hard to tell for sure though because I was 5 miles away out of the restricted airspace, but I could have sworn I saw a glint in somebody's eye.
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Replying to
@gvwilson@mastodon.social Answered - hope it helps some folks. There are quite a few "it depends" answers in this. If the goal is to compare responses with what is known as being empirically correct, most of these do not have an empirical answer.
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 5mo ago
Replying to
Hi Ava!
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2w ago
Replying to on fosstodon.org
@jborean@fosstodon.org There was definitely a lot of great discussion around folks adapting to an AI world: devs cranking out code faster than they ever have, phishing that no longer has the tells of bad grammar and typos, etc. Unlike most cons that depress you with how the sky is falling, people were coming with offerings of what's worked for them and how they are approaching it.
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 2mo ago
Working on a simple online CMS for my Hugo blog - a WYSIWYG Markdown editor based on Quill, and some basic management around that. It still stores the raw backing Markdown files in OneDrive like I was using with Hugo directly. Hooboy is it nerve wracking! 20 years of content that exercises apparently every edge case in Markdown! Thankfully Commonmark has an excellent test suite that I've been able to bootstrap a massive unit test infrastructure with.
0
0
0
0
Open post
Lee Holmes :donor: @Lee_Holmes@infosec.exchange
· 3mo ago
Replying to
@scottgal@hachyderm.io Agree with the points in your post. Also, there's definitely a lot of subtlety to what a 'summary' really means. I was mostly doing the naive approach you called out for a laugh. Would be interested to see what your better pipeline returns for a 10 (and 1) word summary of War and Peace :) https://raw.githubusercontent.com/mmcky/nyu-econ-370/refs/heads/master/notebooks/data/book-war-and-peace.txt
raw.githubusercontent.com
0
2
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 06:55:41 UTC