#remotecodeexecution

15 posts · Last used 7d

[🚨 #MediaWiki vulnerable extension]

If you are running a MediaWiki instance with Extension:External_Data < v3.7, your instance is vulnerable to arbitrary file loading and #RemoteCodeExecution.

The vulnerability was apparently publicly known since August, but due to the lack of communication, instance admins learned about it due to that vulnerability being exploited en masse.

If you know and like a MediaWiki instance, you can check their Special:Version page to see if they are using the External_Data extension to warn them.

More info:

#infosec #wikipedia #wikidata #adminsys #security #CVE #pwned
3
0
7
0
Replying to
https://securityaffairs.com/199873/security/citrix-confirmed-two-new-netscaler-flaws-exploited-as-zero-day.html #Citrix #NetScaler #ZeroDay #RemoteCodeExecution #CyberSecurity #PatchedOrPerish (3/3)
2
0
0
0
Replying to
Reward: You've received a Subpoena of Technical Negligence — non-transferable, immediately effective. #Fastjson #RemoteCodeExecution #CyberSecurity #Vulnerability #RCE #PatchedOrPerish (3/3)
0
0
0
0
Replying to
Searchlight Cyber published exploitation details; the wolves read it too. ServiceNow has acknowledged the activity. Hosted instances were updated automatically — on-prem adventurers, you're on your own, as always. Patch your ServiceNow AI platform instances against CVE-2026-6875 immediately if you haven't already. Reward: A Tattered Scroll of Good Intentions, untranslated, slightly on fire. #ServiceNow #CVE202668875 #RemoteCodeExecution #ZeroDay #CyberSecurity #PatchedOrPerish (2/2)
0
0
0
0
Replying to
Reward: You've received a Cracked Heap Fragment — a common drop. Very common, apparently. #NGINX #CyberSecurity #CriticalVulnerability #RemoteCodeExecution #CVE202642533 #PatchedOrPerish (3/3)
0
0
0
0
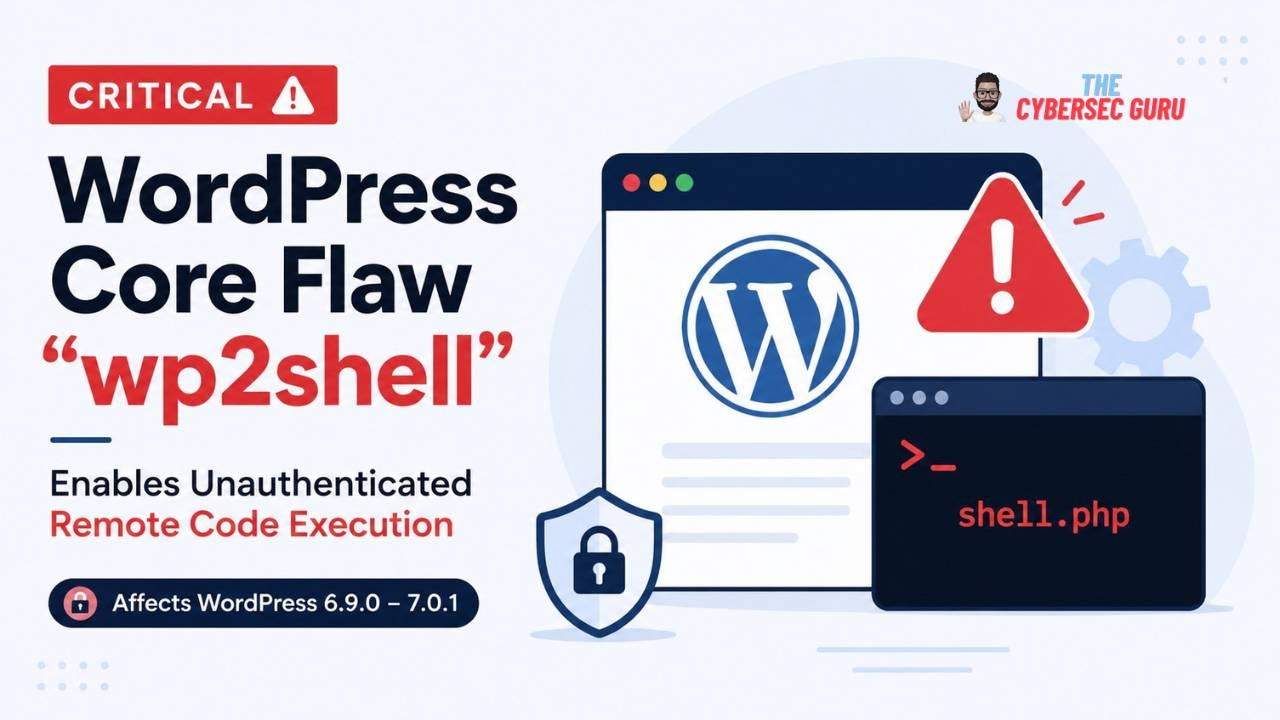
🚨 CRITICAL: WordPress Core "wp2shell" RCE A single anonymous HTTP request can lead to Remote Code Execution on vulnerable WordPress Core installations. ⚠️ No plugins. ⚠️ No themes. ⚠️ No authentication required. Tracked as: 🔴 CVE-2026-63030 (REST API Batch Route Confusion → RCE) 🔴 CVE-2026-60137 (Facilitated SQL Injection) Affected versions • WordPress 6.9.0–6.9.4 • WordPress 7.0.0–7.0.1 ✅ Update immediately to WordPress 6.9.5 or 7.0.2. Due to the severity, WordPress has enabled forced automatic security updates for affected installations. 🔗 Full technical analysis: https://thecybersecguru.com/news/wordpress-core-rce-wp2shell/ #WordPress #WordPressSecurity #wp2shell #CVE202663030 #CVE202660137 #RCE #RemoteCodeExecution #SQLInjection #RESTAPI #CyberSecurity #InfoSec #WebSecurity #WebsiteSecurity #PatchNow #ThreatIntelligence #BlueTeam #SOC #Linux #PHP #ZeroDay #SecurityResearch #SysAdmin #DevSecOps
35
4
57
0
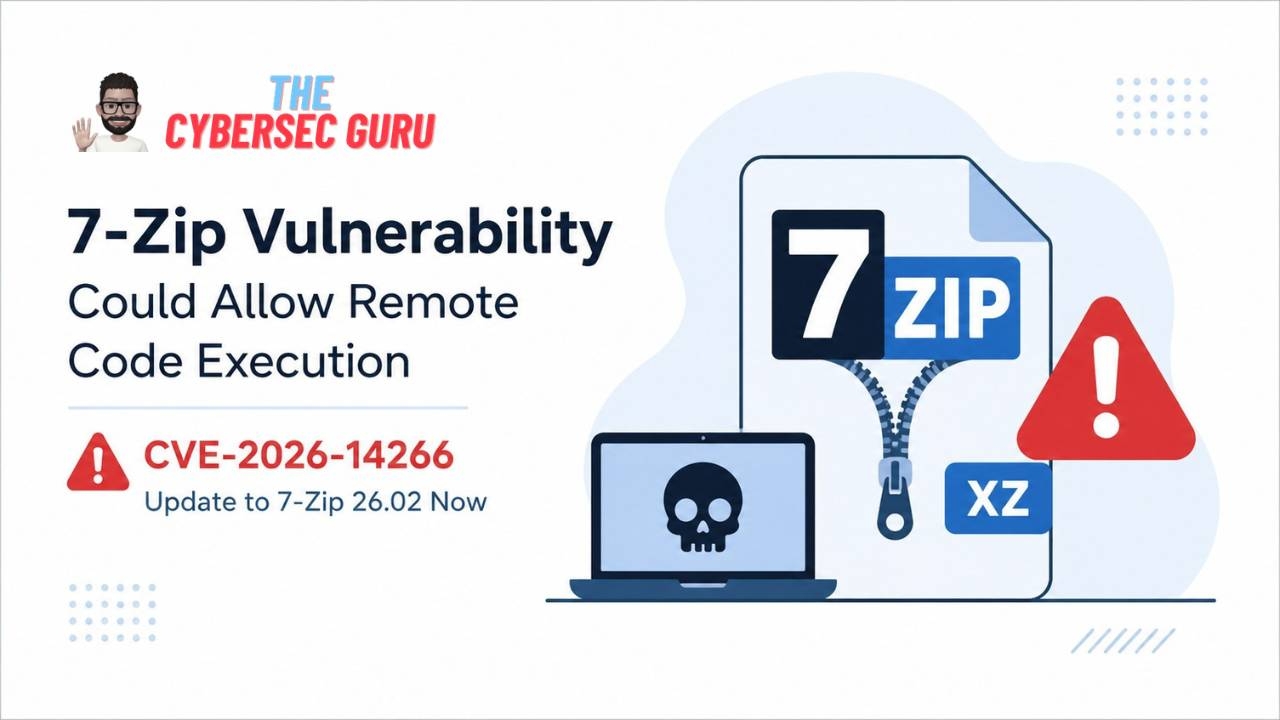
🚨 Millions of 7-Zip users should update immediately. A newly disclosed vulnerability, CVE-2026-14266, could allow Remote Code Execution (RCE) when a victim opens a specially crafted XZ archive. 🔍 Key details: • Heap-based buffer overflow • User interaction required • Exploitable through phishing emails, malicious downloads, and weaponized archive files • Fixed in 7-Zip 26.02 If you use 7-Zip, update now and avoid opening compressed files from untrusted sources. Read the full technical breakdown 👇 https://thecybersecguru.com/news/7-zip-vulnerability-cve-2026-14266/ #CyberSecurity #InfoSec #CyberThreat #Vulnerability #CVE #CVE202614266 #7Zip #RemoteCodeExecution #RCE #ThreatIntel #CyberAttack #Malware #Phishing #SecurityUpdate #PatchNow #WindowsSecurity #BlueTeam #SOC #ThreatHunting #CyberDefense
0
0
2
0
You've seen all posts