#reverseengineering
59 posts · Last used 5d
Boosted by @welcome@friends.deko.cloud
Hello Mastodon! I'm into Computer #Security, #Programming, #ReverseEngineering, #Hacking, #Linux, #AmateurRadio, #Privacy, #OpenSource, #Cryptography and generally anything creative and interesting involving tech. Especially things that help people communicate and use computers more privately and securely. Lately I've been tinkering with mesh networks like #Meshtastic, #MeshCore and #Reticulum. Longtime #QubesOS and #GrapheneOS user.
I also enjoy touching grass like #Camping, #Backpacking and generally being in nature. Would recommend.
This is a personal/professional account so keep an eye out for various writeups and research, for work and for fun. Previous jobs ranged from #SoftwareEngineering to Computer Security #Research and #InfoSec, and I'm looking for more of the same.
#Introduction
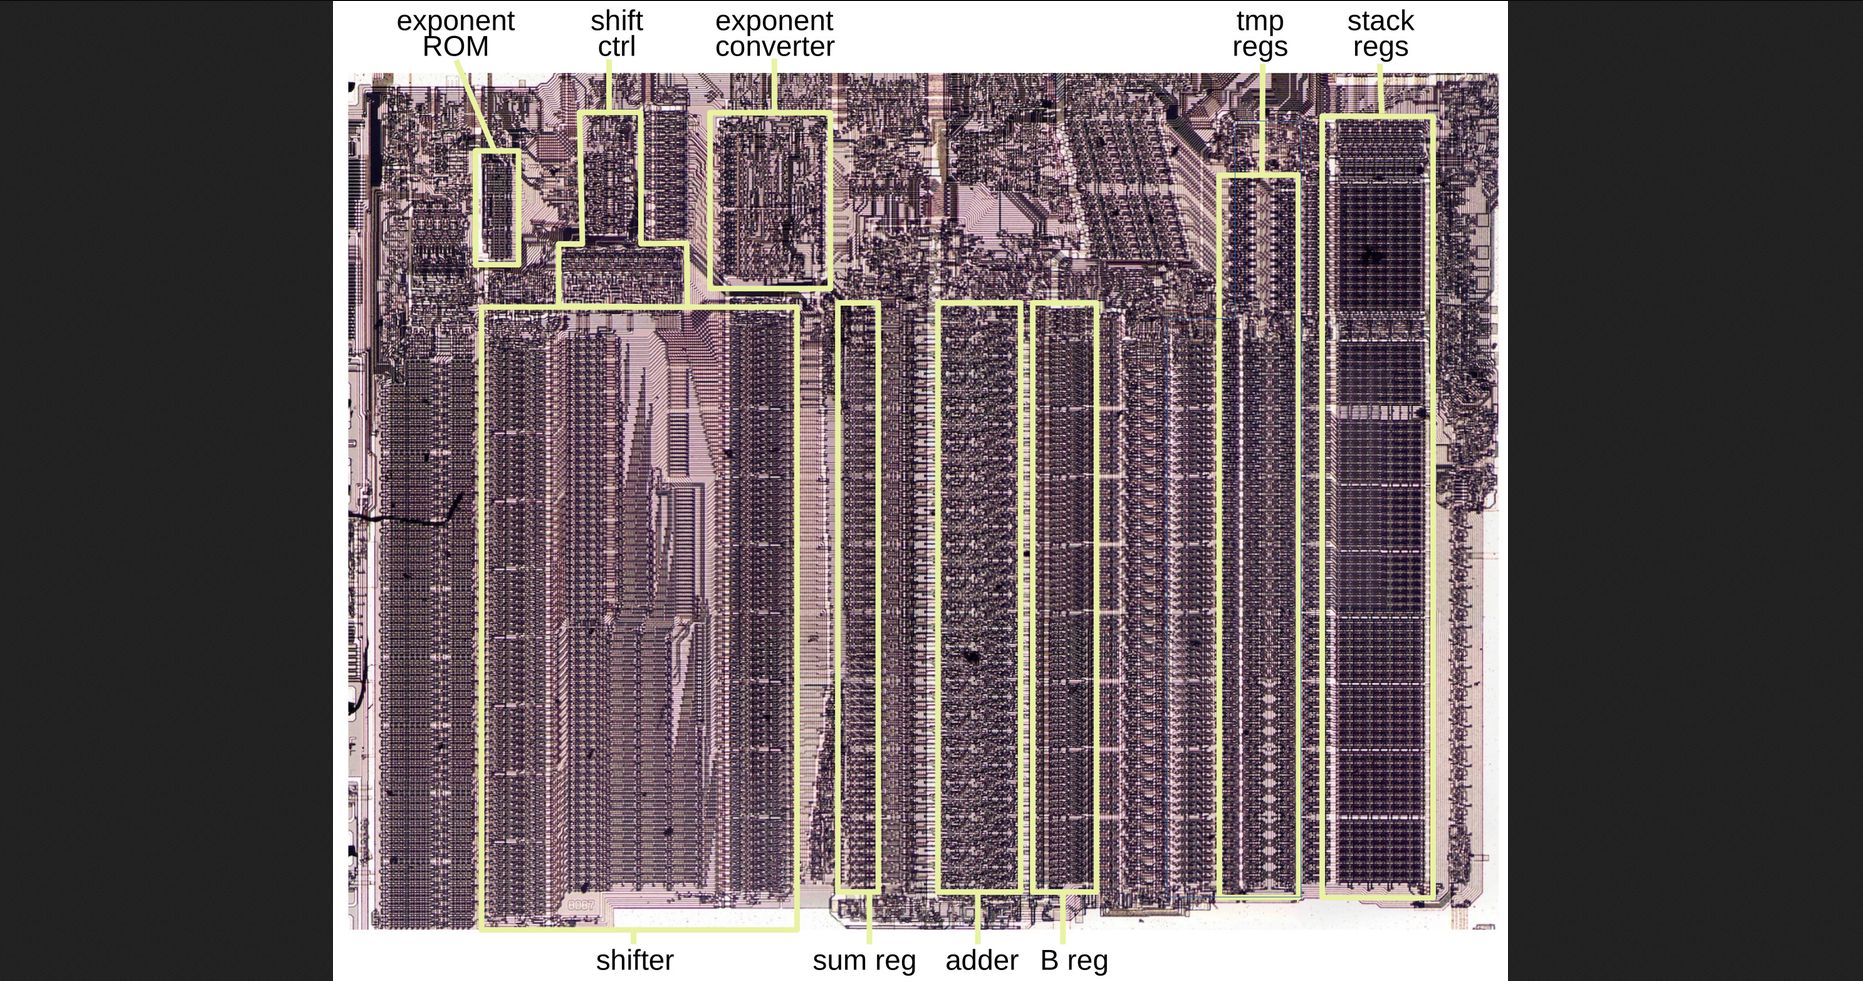
Going on a Tangent with the Intel 8087’s Hybrid CORDIC Algorithm https://hackaday.com/2026/09/27/going-on-a-tangent-with-the-intel-8087s-hybrid-cordic-algorithm/
#ReverseEngineering #Intel8087 #Trigonometry
----------------
🦠 Malware Analysis
===================
Settra is a ransomware operation first identified in June 2026 that has already claimed 50-70+ enterprise victims across technology, manufacturing, financial services, healthcare, and retail sectors. The group operates double-extortion: data exfiltration followed by encryption and ransom negotiation via Tox and darknet portals.
🔹 Intrusion Methodology
Human-operated intrusions begin through compromised VPNs or valid accounts. Credential dumping uses Mimikatz and ProcDump. Lateral movement relies on dual-use tools including PAExec and NetExec. Durable remote access is established via Mesh Agent.
Before encryption, operators abuse signed STProcessMonitor drivers via BYOVD to blind endpoint defenses.
🔹 Encryptor Architecture
The encryptor is a two-stage design recovered through offline static reverse engineering by Cynet Research Labs.
Outer loader (win64.exe):
• Password-gated entry
• PEB export hashing for API resolution
• Anti-debugging gates
• ~200,000-round SHA-256 KDF for key derivation
• AES-256-CTR decryption of inner payload
• Custom LP77 decompression
• Process hollowing into a suspended self-copy
Inner PE payload executes systematic anti-forensics:
• Wipes 12 targeted event logs via wevtutil
• Purges Windows Prefetch
• Deletes PowerShell command history
• Wipes USN change journals
• Disables Windows Recovery (reagentc, bcdedit, wbadmin, Disable-ComputerRestore)
• Resizes VSS shadow storage stealthily
• Powers down Hyper-V VMs via WMI (ROOT\virtualization\v2) to release .vhdx file locks
🔹 Cryptography
Files encrypted using Windows CNG (BCryptGenRandom, BCryptEncrypt) with unique symmetric keys wrapped by an embedded 4096-bit RSA-1 public key. Files renamed to .locked (preceded by temporary .locked_wip). The RSA private key is never present on the victim host. The encryptor contains zero C2 network communication stacks, making it fully offline.
🔹 Detection Claims
Cynet claims proactive interception within 1 second of detonation via kernel-level driver decoy traps. This is a vendor claim from the same organization that performed the analysis, so treat with appropriate skepticism.
🔹 Key Takeaways
The encryptor design is notable for its complete lack of network communication, heavy anti-forensics targeting recovery infrastructure, and deliberate Hyper-V shutdown to access locked virtual disks. The BYOVD approach using signed STProcessMonitor drivers is increasingly common in ransomware operations.
🔹 ransomware #malware #threatintelligence #BYOVD #reverseengineering
🔗 Source: https://www.cynet.com/settra-ransomware-inside-a-new-enterprise-grade-extortion-threat/
#NakedDieFriday restarts after operator error! Sorry about that. And I didn't even drink anything yet. :D
Today we have a C1034AH-J by Agere. This is apparently a sigma-delta codec sitting in front of a modem DSP.
Many thanks to @RueNahcMohr@infosec.exchange for supplying the sample!
Full-res map: http://infosecdj.net/map/agere/1034ah-j/infosecdj_mz_nikpa40x/
#electronics #reverseengineering
New Pwndbg release!
We now disassemble code backwards in context and nearpc, display indirect jumps, nearpc -f works without debug syms, added stack-vis command to visualize stack frames, improved v2p, p2w and pageinfo kernel debugging commands & more!
See https://github.com/pwndbg/pwndbg/releases/tag/2026.09.15
Please sponsor us: https://github.com/sponsors/pwndbg !
#pwndbg #gdb #lldb #reverseengineering #security #lowlevel #exploitation #pwning
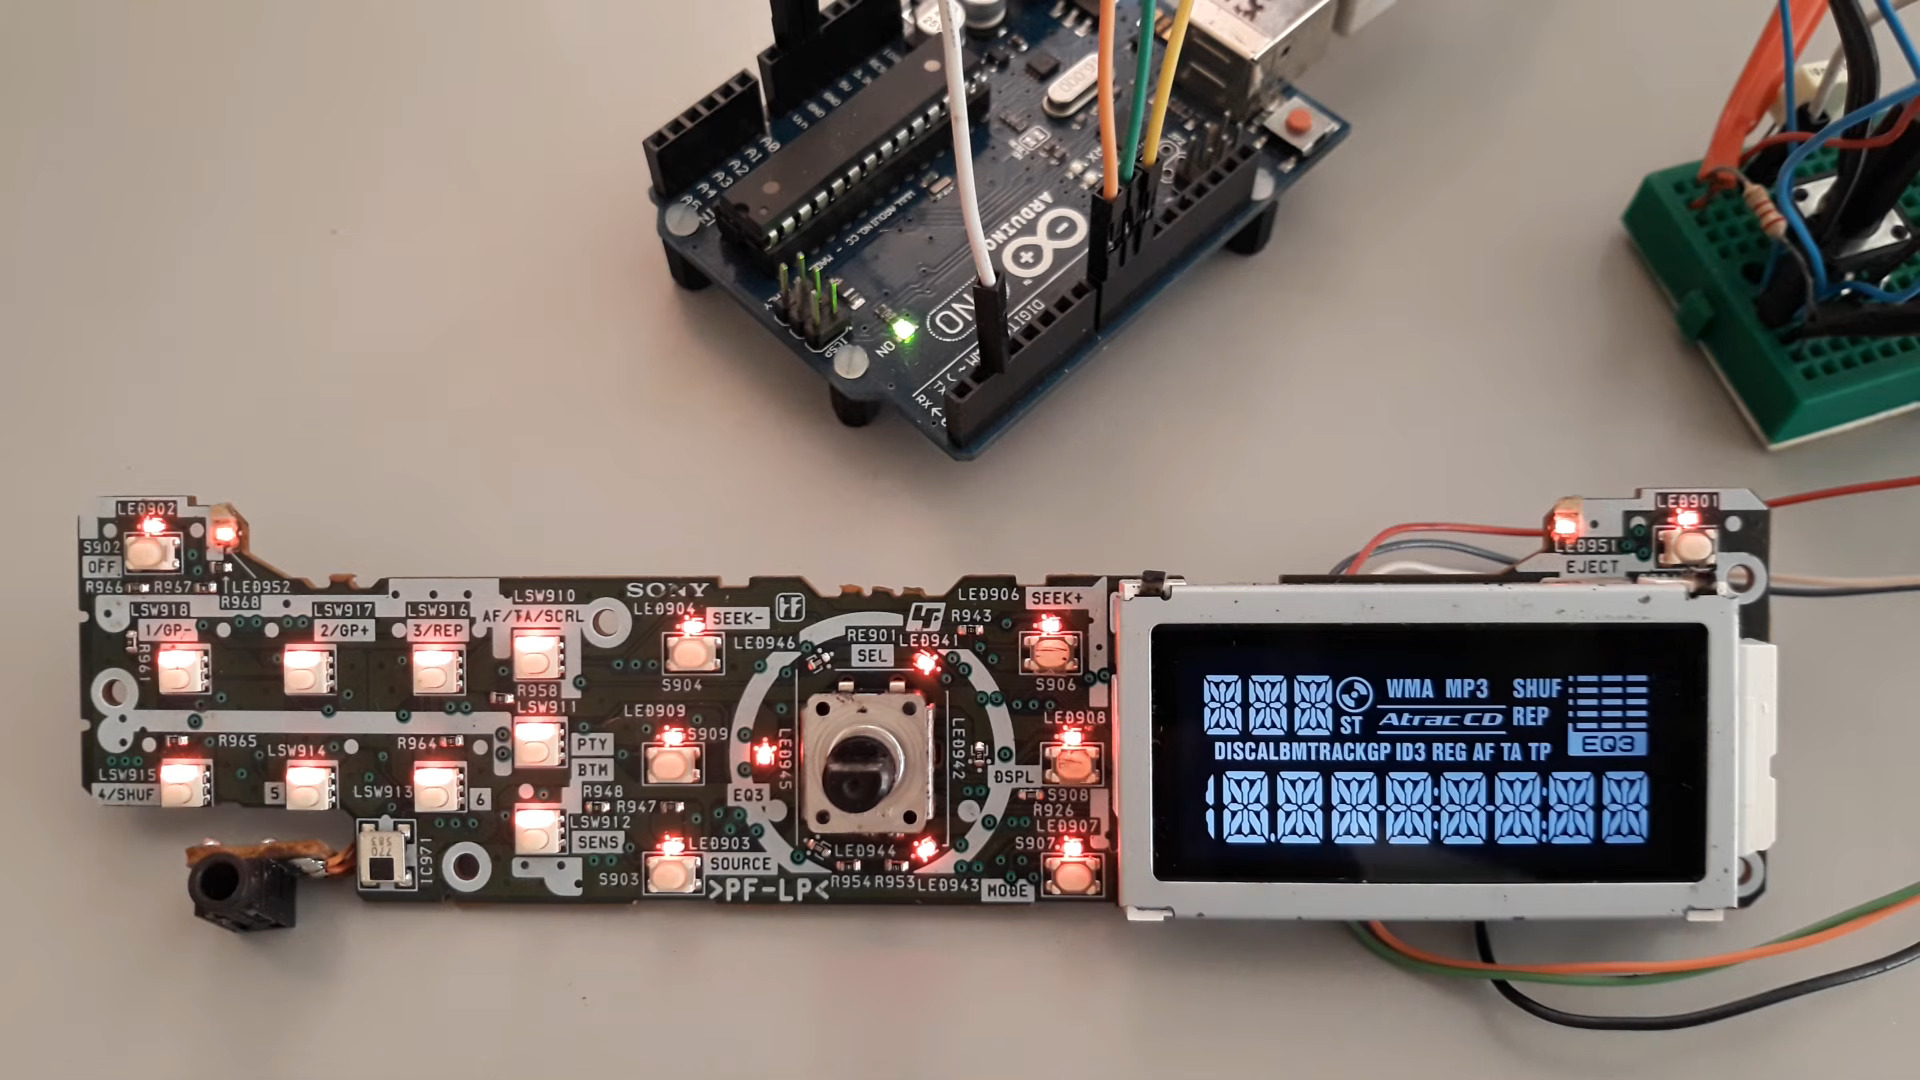
Reverse Engineering A Sony Car Stereo LCD https://hackaday.com/2026/09/20/reverse-engineering-a-sony-car-stereo-lcd/
#ReverseEngineering #Carstereo #LC75826W #Lcd #Reverseengineering #Sony
Laser Your Way into Debug Mode on the RP2350 https://hackaday.com/2026/09/19/laser-your-way-into-debug-mode-on-the-rp2350/
#Microcontrollers #SecurityHacks #Chipdecap #Laserfaultinjection #Reverseengineering #Rp2350
RE: https://infosec.exchange/@0x00string/117275795886211723
#hacking #reverseEngineering #faultInjection #glitching #crowdsupply #tools #cybersecurity
Quoting
@maehw@infosec.exchange check mine out, it mounts on a 3d printer instead of your human hand: https://www.crowdsupply.com/diffused-tactics/glitchcaster
Open quoted postMy attempt to read flash memory failed. I may want to try a side channel attack next. Challenge: I don't have experience here and don't want to spend too much for equipment. Any recommendations where to start? Voltage glitching? Clock glitching? EM fault injection? Is there "affordable" HW other than ChipWhisperer and ChipShouter? Or can anyone recommend them?
#hacking #reverseEngineering #faultInjection #glitching #embeddedSystems
Hacking a Tenda AC1200 Wi-Fi Router with a CVE Combo https://hackaday.com/2026/08/05/hacking-a-tenda-ac1200-wi-fi-router-with-a-cve-combo/
#ReverseEngineering #SecurityHacks #Routerhacking #Telnet #Tenda #Uart
Oh hey. Just wanted to let you know today that I am open to hobby/public IC decapping and imaging projects. Boosts and other sharing are always appreciated!
More info here: https://siliconpr0n.org/archive/doku.php?id=infosecdj:start#commissioning_work
#microscopy #reverseengineering #electronics
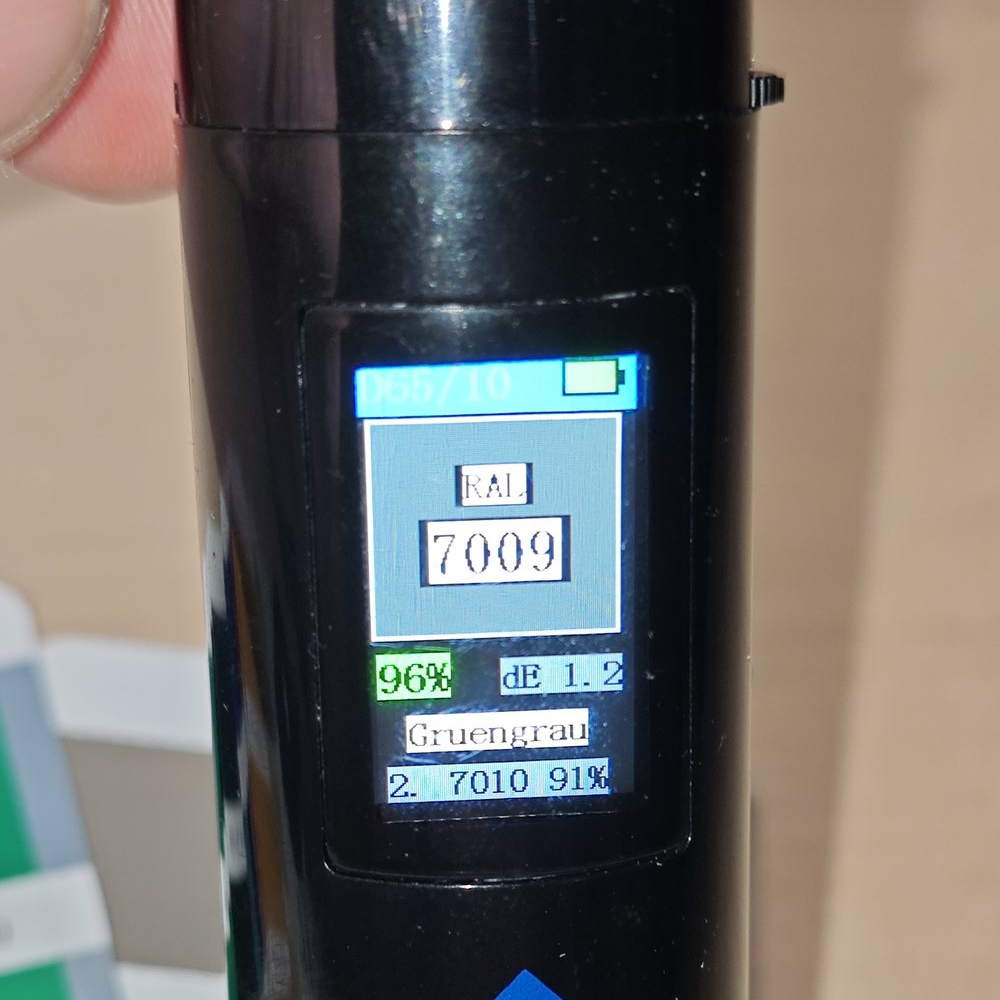
Hacking a Commercial Colorimeter to add RAL Color Code Support https://hackaday.com/2026/07/31/hacking-a-commercial-colorimeter-to-add-ral-color-code-support/
#ToolHacks #Colorimiter #Reverseengineering
AI is woke, stop using it.
AI believes in climate change, stop using it.
AI told me to get COVID vaccine, stop using it.
#reverseengineering
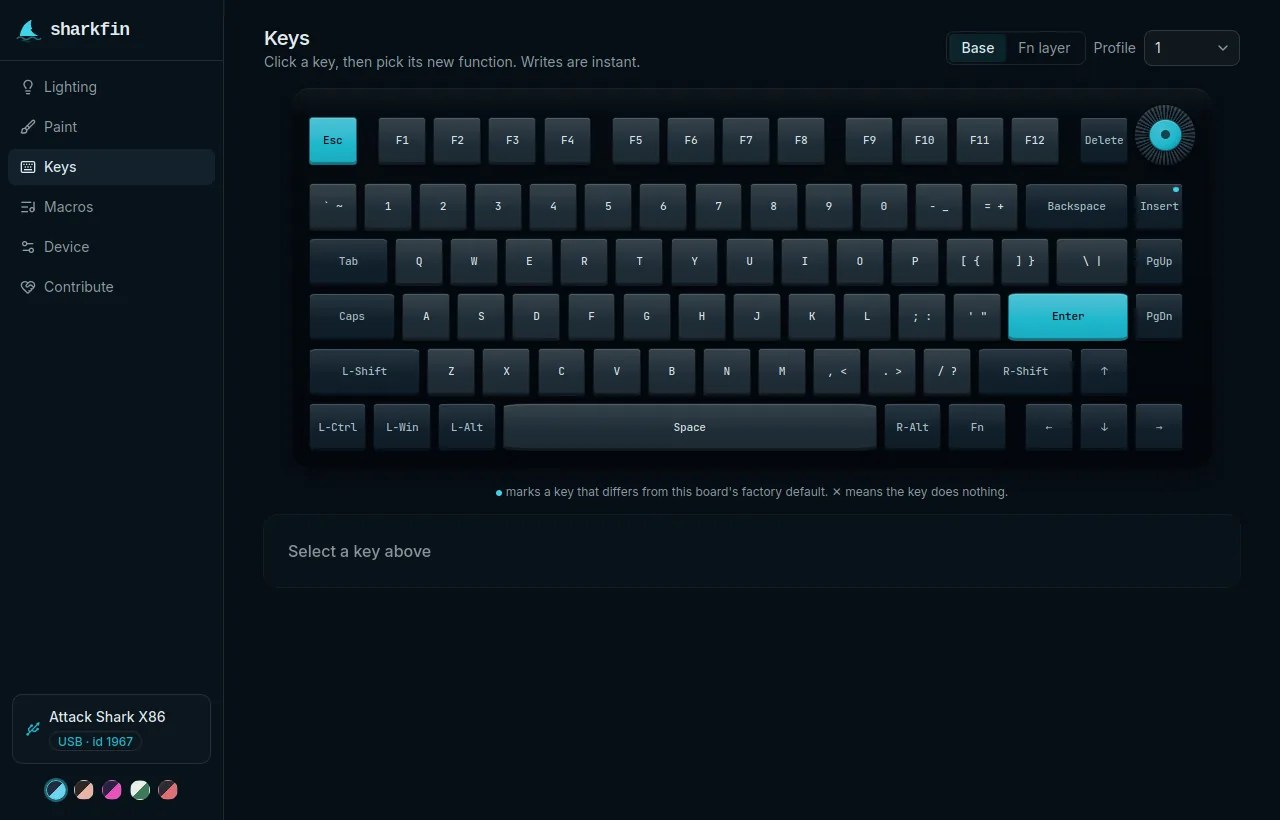
Sharkfin Bites Attack Shark https://hackaday.com/2026/07/28/sharkfin-bites-attack-shark/
#Classichacks #PeripheralsHacks #Configuration #Keyboard #Reverseengineering
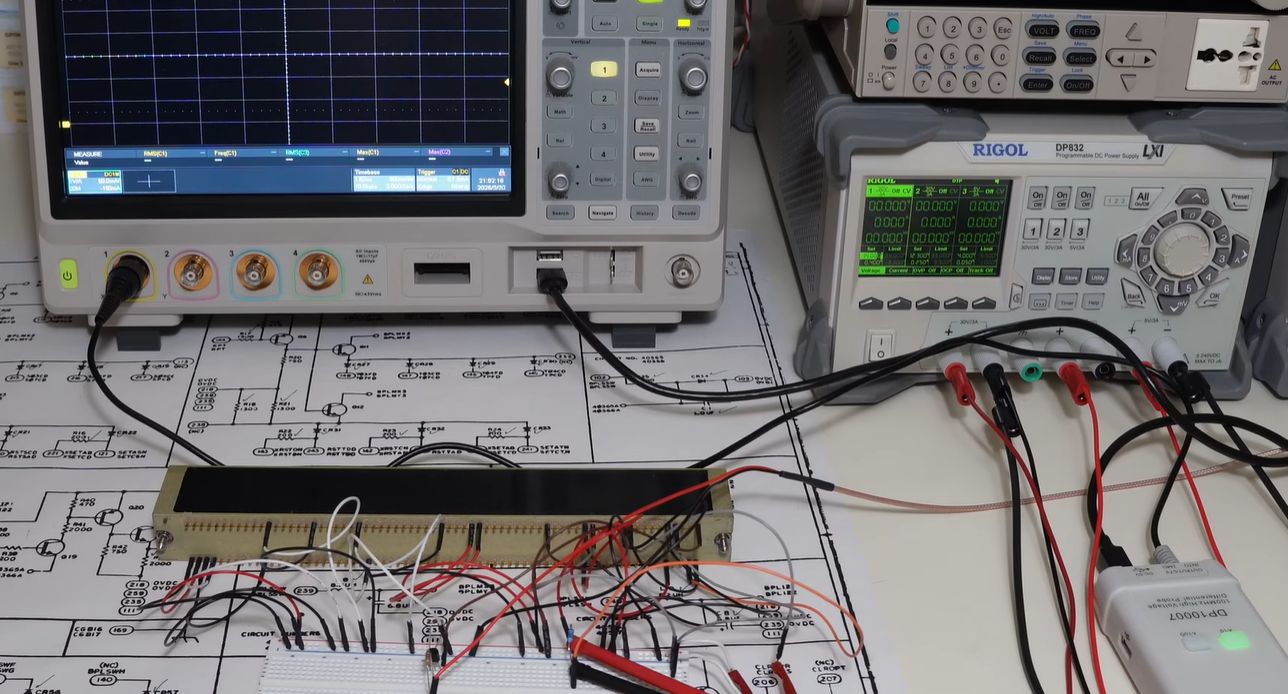
Re-Testing an Apollo Guidance Computer Module that Failed Certification Testing https://hackaday.com/2026/07/27/re-testing-an-apollo-guidance-computer-module-that-failed-certification-testing/
#History #Retrocomputing #ReverseEngineering #ApolloGuidanceComputer #Nasa #Space
rc-servers v1.3.0 (and v1.3.1, whoops) are out. They bring the initial federation-like abilities to servers, vehicle exporting, and many other improvements.
Full patch notes:
https://git.ngram.ca/OpenJam/rc-servers/releases/tag/v1.3.0
#Robocraft #ReverseEngineering #Openjam
🤖 Cruciferra Crypter: China-linked cybercrime groups use BYOVD (Bring Your Own Vulnerable Driver) and Process Ghosting to deliver malware via tax-themed phishing targeting Indian taxpayers. The crypter deploys RATs and info-stealers while evading EDR.
🔗 https://thehackernews.com/2026/07/cruciferra-crypter-uses-byovd-and.html
#Malware #BYOVD #CyberSec #Windows #ReverseEngineering
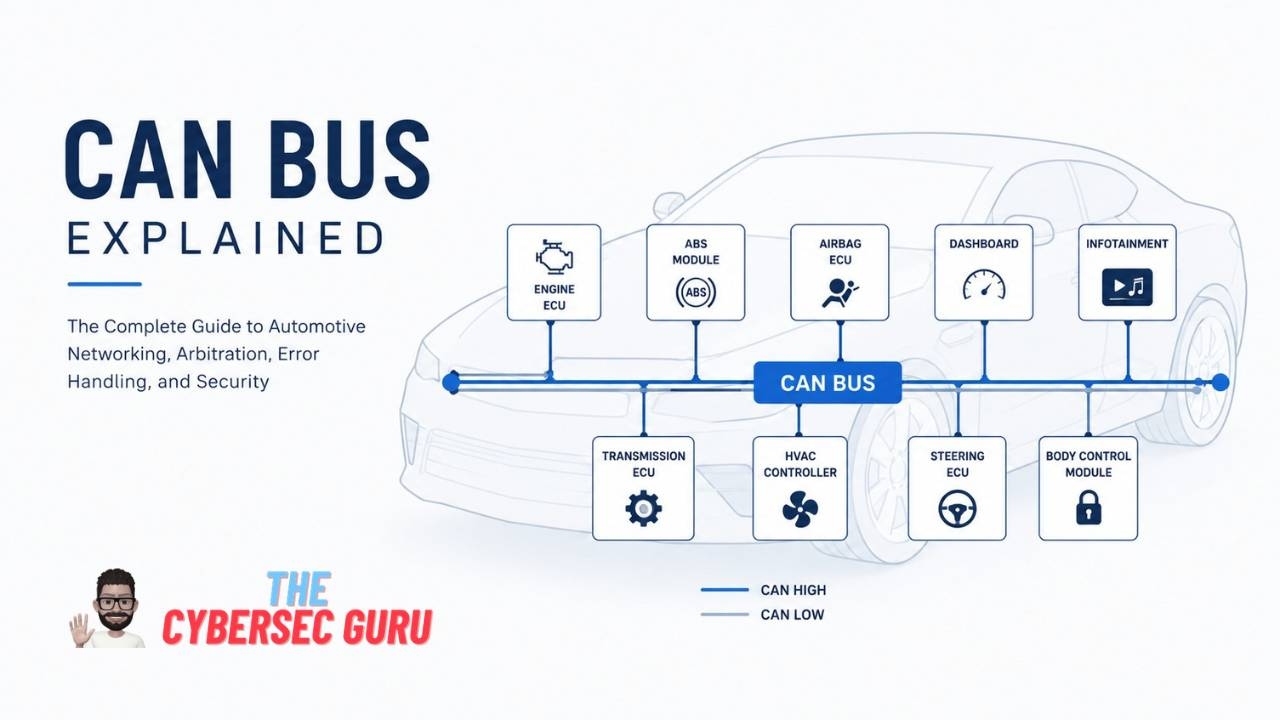
🚗 Every modern car is a network on wheels.
Behind every brake press, gear shift, and steering input, dozens of ECUs exchange thousands of messages over CAN Bus.
If you're learning: • Automotive Cybersecurity • CAN Bus • ECU Hacking • Reverse Engineering • Embedded Systems • OBD-II • CAN FD • Automotive Ethernet
This is the guide you need.
Read the complete guide 👇 https://thecybersecguru.com/glossary/can-bus-explained/
#Cybersecurity #CANBus #AutomotiveCybersecurity #ReverseEngineering #EmbeddedSystems #ECU #Automotive #IoT #CANFD #Engineering
Ahoy there, #NakedDieFriday is late in the day but still happening!
Today I got a Motorola part for you, one named SC541097. This looks like a special run of MC68HC05JP, which is a HC05-based microcontroller.
Many thanks to @RueNahcMohr@infosec.exchange for supplying this sample!
Full-res map: http://infosecdj.net/map/motorola/sc541097-j53w/infosecdj_mz_nikpa40x/
#electronics #reverseengineering #microscopy