#kvm
16 posts · Last used 10d
Krytyczna luka w Linux KVM na ARM64. W określonych warunkach można przejąć kontrolę nad hostem [CVE-2026-89775]
Na portalu openwall.com badacz bezpieczeństwa Hyunwoo Kim opublikował wpis zawierający szczegóły krytycznej podatności w podsystemie KVM (Kernel-based Virtual Machine) dla architektury ARM64 w jądrze Linuxa. Luka oznaczona identyfikatorem CVE-2026-89775 umożliwia ucieczkę z maszyny wirtualnej i uzyskanie dostępu do pamięci hosta. Może to prowadzić do przejęcia kontroli nad systemem (hypervisorem). TLDR:...
#Aktualności #Cve #Kvm #Linux #Rce
https://sekurak.pl/krytyczna-luka-w-linux-kvm-na-arm64-w-okreslonych-warunkach-mozna-przejac-kontrole-nad-hostem-cve-2026-89775/
Krytyczna luka w Linux KVM na ARM64. W określonych warunkach można przejąć kontrolę nad hostem [CVE-2026-89775] https://sekurak.pl/krytyczna-luka-w-linux-kvm-na-arm64-w-okreslonych-warunkach-mozna-przejac-kontrole-nad-hostem-cve-2026-89775/ #Aktualnoci #Cve #Kvm #Linux #Rce
Last week's IncusOS post listed Proxmox, XCP-ng and ESXi and skipped the hypervisor we have run and installed since 2007: KVM, in the Linux kernel since 2.6.20, on Ubuntu. Proxmox and Incus both run their VMs on it, so the choice is a management layer. New post: why Ubuntu plus KVM is our default, why we skip libvirt and talk to QEMU directly, and eVirt, our YAML-per-machine framework. https://blog.eracks.com/2026/09/kvm-on-ubuntu-since-2007/ #KVM #Ubuntu #Linux #SelfHosted
Is anyone aware of an existing KVM-type switch that would support sharing a single non-ADB keyboard/mouse between a #NeXT Cube (‘040 w/Dimension Board) and a NeXT Turbo slab?
I have one of each on my desk and already have a mechanical VGA switcher for the display side of things, but I’d love to use a single NeXT keyboard/mouse from a desk space perspective (and not have to unplug/replug it between the machines).
I guess I need to factor in the SoundBox as well.
#retrocomputing #kvm
Zapscape (CVE-2026-64561) is another reminder that the hypervisor boundary is only as strong as the code implementing it.
The vulnerability is a guest-to-host escape in Linux KVM's x86 Shadow MMU. The root cause is a stale-root validation ordering bug that allows the page fault handler to continue using an invalidated shadow MMU root after quota reclaim, ultimately leading to a use-after-free primitive. Public research demonstrates a complete guest-to-host escape chain, although exploitation requires privileged code execution inside an L1 guest and nested virtualization exposure.
I put together a deep technical analysis covering the Shadow MMU internals, nested virtualization, exploitation stages, cross-cache reallocation, KASLR bypass, AMD vs. Intel trigger conditions, the upstream fix, and why simply moving a stale-root check eliminates the entire exploitation chain.
Interested to hear how others assess the practical risk for multi-tenant KVM deployments where nested virtualization is enabled.
https://thecybersecguru.com/news/zapscape-cve-2026-64561-kvm-guest-host-escape/
#Linux #KVM #Virtualization #KernelSecurity #CloudSecurity #CVE202664561
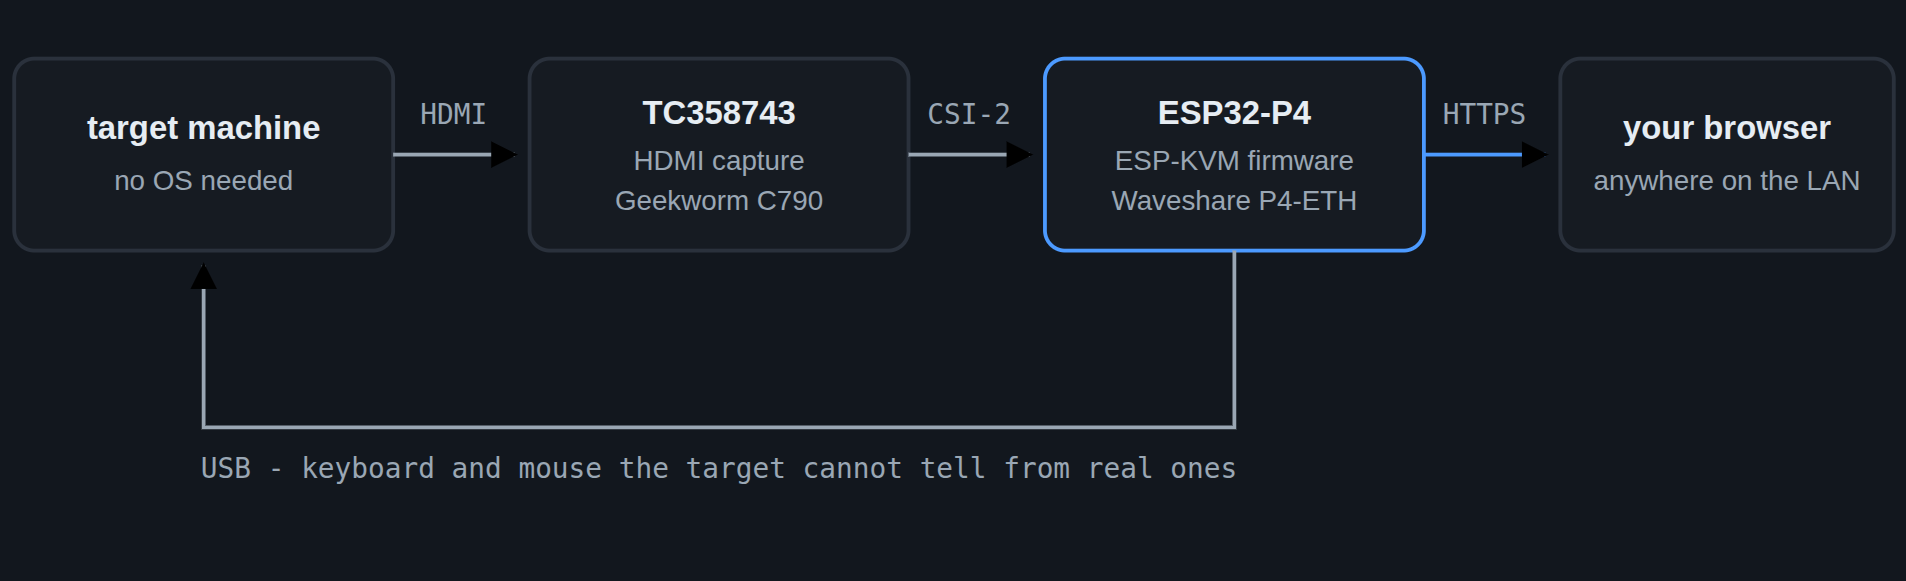
A Capable KVM Built With The ESP32 https://hackaday.com/2026/07/30/a-capable-kvm-built-with-the-esp32/
#Computerhacks #PeripheralsHacks #Csi #Hdmi #Kvm
OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.
#OVHcloud #CVE202653359 #KVM #LinuxKernel #CloudSecurity
https://securityonline.info/ovh-cve-2026-53359-kvm-patch/?utm_source=mastodon&utm_medium=jetpack_social
Most nodes at @BoxyBSD@mastodon.bsd.cafe are now operated by #bhyve on #FreeBSD via #Sylve again! Thanks to @hayzam@mastodon.bsd.cafe for his incredible work by crafting #Sylve! As it’s not that easy to drain nodes to be reinstalled with FreeBSD, there’re still nodes serving VPS instances via #Proxmox / #KVM.
#RUNBSD #VPS #freevps #opensource #community
KVM Januscape Bug: CVE-2026-53359 in Linux Kernel
🔗 https://cybersecurefox.com/en/kvm-cve-2026-53359-januscape-shadow-mmu-bug
#CVE-2026-53359 #KVM #Januscape #Linux #kernel #vulnerability #shadow #MMU
I am doing cloud security. A use after free can kill the MMU memory in KVM.
All Hyperscaler relying on KVM are affected.
GitHub - V4bel/Januscape · GitHub
https://github.com/V4bel/Januscape
#kvm #cloud #gcp #azure #aws #security #januscape
Januscape: Guest-to-Host Escape in KVM/x86
https://github.com/V4bel/Januscape
#Security #Virtualization #KVM
Today I realized that my Linux Contabo VPS has a built-in script in /etc/cron.hourly that drops the cache every hour. I found it when I checked dmesg; there are so many "drop_caches: 1" lines.
I guess the memory is not dedicated, but shared via KVM memory ballooning.
It seems Contabo tries so hard to reclaim physical memory from its customers by dropping page caches every hour. I feel like Contabo is somewhat notorious for aggressive overprovisioning.
I will delete the free script.
Just went through and did a fresh VM install of Windows 11 using kvm. That Windows install process is absolutely horrible, the ads, the multiple attempts at selling me a product during install.. I felt so validated for ditching Windows years ago while running this install
#winblows #kvm #vm #ubuntu #linux #windows
O Melhor KVM Open Source que Existe?
https://youtube.com/watch?v=uUo4tyiOXhc&si=UXJXmF2z0uURvPqi
#opensourcehardware #kvm #agpl3
O Melhor KVM Open Source que Existe?
Voisko IT- ja kotitoimistotietäjät kertoa, että mitä mun kannattaa hankkia, kun kotona mulla on pöytäkone, kaksi näyttöä + muut tilpehöörit. Sitten työkone on läppäri.
Haluaisin lähinnä käyttää työpöydän kahta näyttöä, enkä vain yhtä, joka on HDMI-piuhalla kiinni.
Käsitykseni mukaan en oikeastaan halua mitään telakkaa, koska lähtökohtaisesti käytän kuitenkin pöytäkonetta muutoin, enkä saa sitä järkeävästi telakkaan kiinni.
Onko tähän sitten järkevin ratkaisu KVM-kytkin? Siitä sitten piuha pöytäkoneeseen ja läppäriin ja tarpeen mukaan vaihtelen?
Vai onko jotain muuta ratkaisua?
#tietokoneet #apuaFedi #IT #ITkysymykset #työelämä #työt #KVM #telakka
You've seen all posts
![Krytyczna luka w Linux KVM na ARM64. W określonych warunkach można przejąć kontrolę nad hostem [CVE-2026-89775]](https://sekurak.pl/wp-content/uploads/2023/08/hackerzzz.jpeg)