Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

rsalz

@rsalz@ioc.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on ioc.exchange

Akamai, IETF, QuicTLS.
Previously DataPower->IBM, OpenSSL.

745 Followers
519 Following
50 Posts
Joined November 18, 2022
Spokeperson:
No
Pronouns:
he/his/him
(Skimpy) Website:
richsalz.com
Open post
rsalz @rsalz@ioc.exchange
· 4mo ago

And now we can say it publicly https://www.akamai.com/blog/security/akamai-anthropic-collective-defense-project-glasswing
akamai.com
3
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @djb@mastodon.cr.yp.to @letoams@defcon.social again, nothing is being removed. Nothing. In fact what is being added is explicitly not recommended.
1
4
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to

@djb @darkuncle

Everything I wrote is simple and consistent and, if you look at the context of when they were made, easy to follow. For those just jumping in.

  1. As a long-time person involved with the IETF I have not seen any hidden/coercive NSA involvement.

  2. I accept that the EFF budget piece is accurate.

  3. The term "crazy conspiracy thinking" referred to your blog posts on this topic.

I do not argue with NSA/NIST and pointed out why they could do that in the past. I find it amusing that ISO refused to standardize NSA's Simon and Speck. Perhaps they're not as good at influence as they used to be.

3
10
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
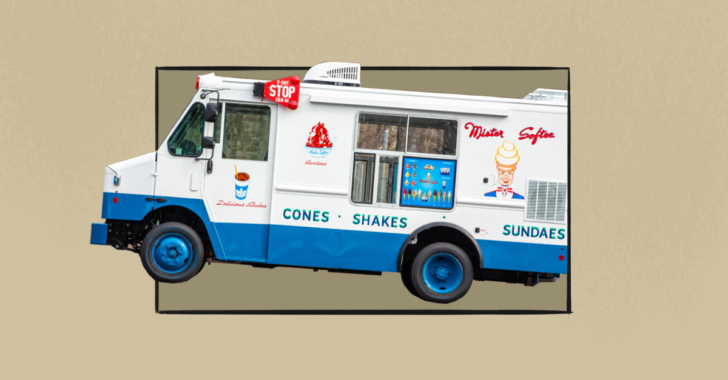
@mattblaze fascinating, thanks. On a lighter note, Service Request #1: What Happens When I Call 311? - 99% Invisible https://99percentinvisible.org/episode/service-request-01-311/
Service Request #1: What Happens When I Call 311? - 99% Invisible
99% Invisible

Service Request #1: What Happens When I Call 311? - 99% Invisible

During the early days of the pandemic lockdowns, 99% Invisible producer Christopher Johnson found himself trapped in a high-rise apartment in Washington Heights, tormented by the relentless, looping jingle of idling Mr. Softee ice cream trucks. Armed with the knowledge that local noise ordinances required the trucks to silence their music while parked, he dialed

2
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@djb @darkuncle I didn't dispute the RSA thing. I don't know about the other things you claimed.
2
4
0
0
Open post
rsalz @rsalz@ioc.exchange
· 4mo ago

We're building out a bunch of tools and such for our customers to use. Any recommendations for good dev-rel sites we can look at, life advice from, etc?

1
0
3
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago

"90% of women leave tech within 10 years," according to an Akamai study. https://www.computerweekly.com/news/366642319/Almost-90-of-women-leave-tech-industry-within-10-years

computerweekly.com
1
1
1
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@argv_minus_one "Do you have another explanation for the inexplicable push for the IETF to specify non-hybrid ML-KEM?" I don't know why you see it as inexplicable. Some people want it for various reasons, and not because they are NSA fronts. I can see various places where the size differential (time, bits on the wire, CPU cost) are not negligible to the environment, or where the cost of eventually transitioning off hybrid are not practical (subs, satellites, zillions of telephone poles, etc).
1
3
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@djb@mastodon.cr.yp.to @darkuncle@infosec.exchange no I do not, but that does not mean that the NSA is corrupting the IETF.
1
66
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@darkuncle as an active participant in many of the working groups, and colleagues with NSA and others, I do not believe there is any covert influence happening. His arguments have devolved to little more than ad hominem attacks. Kind of sad. I've known him for 30 years.
1
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@darkuncle I don't recall Dan suspecting dual EC but I may just be forgetting that. NIST, however did learn their lesson and sponsored global contests for AES post quantum etc. Not NSA.
1
4
0
0
Open post
rsalz @rsalz@ioc.exchange
· 2mo ago
What's next for PQ crypto? https://www.akamai.com/blog/security/post-quantum-cryptography-whats-next-edge-security Wherein I name-check many people smarter than I am.
akamai.com
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social has money prevented you from participating Dan?
0
5
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@djb@mastodon.cr.yp.to @darkuncle@infosec.exchange I presumed nothing. Read what I wrote. Twisting words to win an argument. Your better than this Dan.
0
61
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social you clearly are pretending not to know what community means
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@darkuncle Yes, erring on the side of extreme caution is right. But you completely discount Bas Westerban, Sophie Schmeig, etc?
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@huitema@social.secret-wg.org You think it will be published? I'm not sure sure it has consensus.
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@encthenet@flyovercountry.social didn't know about tcpenc. Disagree with you on the pq draft.
0
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@argv_minus_one Well, I don't presume to know all the operating environments. Are you sure you do? :)
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to

@jzb To answer your questions:

  1. If it were only the NSA, sure, be suspicious. But it's not (IEEE, Ericsson I believe, others) and I do not believe they were all cofrupted.

  2. Sure, the IETF is having that discussion. See what you think of https://github.com/tlswg/draft-ietf-tls-mlkem/pull/14/changes for example.
github.com
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@hal_pomeranz@infosec.exchange at least the George Michael donated the profits.
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@huitema@social.secret-wg.org @pedromj@mastodon.social I'll assume you read the draft and the PR with the revised security considerations. You also know that pushing on social media doesn't much impact IETF, unless you're trying to do brigading which I do not think you are.
0
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social Giving people template text and encouraging them to take a stand where they have never participated before is not participation. I've noticed that this kind of blind literalism is often seen in untrained people playing lawyer, or perhaps US Supreme Court justices. Also not uncommon with people "on the spectrum." I do not think you are stupid, nor are you a Justice and I am not qualified to diagnose. Therefore, I still believe you are therefore just acting in bad faith to get what you want, no matter how justified you think the end result is.
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@djb I have no idea who NSA paid. I do not dispute that the IETF approved an RFC that standardized their Dual EC. Again, what I have said multiple times is that I have seen no involvement *since Dual EC* that the NSA influenced IETF decisions. This is tiresome. I'm done.
0
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 2mo ago
Replying to
@gsuberland@chaos.social quoth the raven: nerxvtrvbv
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@djb I am glad your work on cryptography is better than your comprehension of what I write. "you presume this doesn't include the IETF since the document doesn't _specifically_ name the IETF." Ye gods man, read it again.
0
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @letoams@defcon.social @djb@mastodon.cr.yp.to if you let vendors sell you things you think are insecure sounds like you are responsible.
0
7
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to on mastodon.cr.yp.to
@djb@mastodon.cr.yp.to @letoams@defcon.social I am not inventing new rules Dan. We disagree over the meaning of participation, and you are changing the subject rather than trying to convince me that you are right. More bad faith from you, sadly. I have no idea what the NSA told its vendors. Do you have links or proof? All I know is Scott F from Cisco mentioned the government wants this. I thought doing a new WGLC made sense. And I am not surprised some long-time participants spoke up given the heated feelings about it. Can you explain why what you're doing is encouraging participation? If you;re upset about Jenkins email, do you feel any remorse about what you're doing?
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @djb@mastodon.cr.yp.to @letoams@defcon.social nobody is stopping you from implementing hybrid key exchange. In fact pure post quantum key exchange is not recommended. So what, exactly, is the problem here?
0
6
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Apropos of nothing, I just got this in a private email: Captain Appeal and his DoS attacks. I wonder who they are thinking of?
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to on mastodon.cr.yp.to
@djb@mastodon.cr.yp.to @damienmiller@hachyderm.io I treat any kind of praise, as opposed to a withering negative comment, is high praise from you indeed.
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social the chairs asked the working group, not generic people. You know this, why mislead? Because you're in the minority?
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 2mo ago
Replying to
@paulehoffman@infosec.exchange probably safest course of action
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social and you Dan are trying to redefine participate as participate in a sock puppet drive by comment without ever actually participating.
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @letoams@defcon.social @pluralistic@mamot.fr @eff@mastodon.social i suggest you learn more about how the IETF operates.
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social again you try to twist the meaning of participate to include those who do one drive by email.
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 2mo ago
Replying to
@adamshostack@infosec.exchange I thought it was under half an hour, although it did seem like almost 90 minutes...
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@darkuncle At the time of Dual_EC, NIST was required by law to take NSA's advice. They no longer are. But what history of seeing conspiracy where it did exist are you thinking of?
0
6
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @letoams@defcon.social @djb@mastodon.cr.yp.to @eff@mastodon.social @pluralistic@mamot.fr you presented no math.
0
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @djb@mastodon.cr.yp.to @letoams@defcon.social it is only summer in half the world. The ietf meets your round. We have another face-to-face meeting in July, we have it every july. It's not a vote . From your post, I can only assume you are not at a regular ietf participant.
0
10
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@djb@mastodon.cr.yp.to @letoams@defcon.social anyone can JOIN the IETF. Not the same as what you are doing.
0
2
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago
Replying to
@paulehoffman Very funny. :). And sad :(
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@darkuncle@infosec.exchange @encthenet@flyovercountry.social I have known him for about 30 years. Back in the Usenet days. Lately, he will twist and cherry pick people's words to reinforce his point. Sorry, I admit that this may be on me, but I no longer think he is operating in good faith and I do not trust him or what he says anymore. He did it with me, here on this platform, so I am speaking from experience.
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 5mo ago

Sad and very very funny. https://www.nytimes.com/2026/05/05/us/pope-leo-xiv-bank-customer-service.html?unlocked_article_code=1.gVA.-90Z.eWMDB6xhD-x7&smid=url-share

nytimes.com
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@grumpybozo@toad.social yeah it is really overboard. Everything goes through the template library. If all you have is a hammer...
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@mikalai@privacysafe.social @letoams@defcon.social @djb@mastodon.cr.yp.to @eff@mastodon.social and one random person getting vehement on social media doesn't make much of an impact on me, sorry.
0
4
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to on mastodon.cr.yp.to
@djb@mastodon.cr.yp.to @letoams@defcon.social Boy, you'll throw anything to see what sticks. Your attempt to engender guilt doesn't work because I know you're deceptive, misleading, and a liar.
0
0
0
0
Open post
rsalz @rsalz@ioc.exchange
· 3mo ago
Replying to
@encthenet@flyovercountry.social that's a rather strong word. Mistakes were made
0
1
0
0
Open post
rsalz @rsalz@ioc.exchange
· 2mo ago
Akamai latest state of the internet/security report is out. Unsurprisingly, the focus is on risks of AI to enterprises. https://www.akamai.com/resources/state-of-the-internet/enterprise-ai-risk-report Looking at the takeaways on the first screen, most people here will not be surprised, but maybe some bosses could stand to learn.
akamai.com
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:07:25 UTC