Linus Gasser
mastodon 4.5.7Hobby cryptographer with a tendency to prefer decentralized stuff like the internet, email, Mastodon, and of course blockchains in a way or another.
#Rust #Mutex #Deadlocks I didn't know that we know how to solve deadlocks since the seventies! The problem seems to be that there is no convenient interface available in most languages...
https://notes.brooklynzelenka.com/Blog/Surelock
Tries to give a template how to use mutexes in a way that all deadlocks (with one exception) are detected at runtime.
A very nice step-by-step explanation of the copy.fail vulnerability in the #linux kernel:
https://github.com/fraynal/articles/tree/main/copy.fail
Really nice because it shows how choosing something strange at one time might be abused some years in the future...
We had this long running joke of my friend starting to program in the 80s, and his first program was:
```
10 REM Maennchen laeuft ueber die Strasse
```
Which translates to: "guy walks across the street". My friend was very disappointed, when the "run" command didn't produce anything. After all, the programs in the magazines show things? Perhaps the lines after the REM were useful after all?
Nobody's laughing anymore now:
Ok, I think now is not a good time to debug my wife's computer...
#LLM #Security A very nice follow-up article about "We hold back 'Mythos' because it's so powerful". This company tests various models and finds that with the correct framework, even small models are very powerful at detecting security bugs:
https://aisle.com/blog/ai-cybersecurity-after-mythos-the-jagged-frontier
> A thousand adequate detectives searching everywhere will find more bugs than one brilliant detective who has to guess where to look.
-> using many small models is often better than using one big model...
If you have an iOS device, now is a good time to make sure updates are applied automatically, and get the latest software version. Somebody posted an exploit on GitHub that gives hackers full control of any iOS device not updated since September 2025. These exploits are usually well-kept secrets, as they are very valuable, and used only on high value targets. In this case, just visiting a website is enough to get your iPhone infected. Now everybody can be targeted!
So - is this #Mythos, or just people looking at the right places now?
Time to disable some more modules on your linux servers - one more privilege escalation because somebody allowed writing arbitrary 4 bytes to be written to any page cache:
https://github.com/V4bel/dirtyfrag
Twice in a couple of days - I should make it automatic to update the servers...
@paul@m.pcgt.link OK, let me see if my math is still good:
10↑↑3 m = 10 ** 10 ** 10 m
Now in quetta m, or Qm, or 10 ** 30 m:
10 ** 10 ** 10 / 10 ** 30 = 10 ** ( 10 ** 10 - 30 ) = 9'999'970 Qm
At least Claude has the same result (I asked it afterwards).
So a hectoknuthmeter is 9'999'970 quetta meters.
https://kirancodes.me/posts/log-who-watches-the-watchers.html
#formalverification #bug very nice finding: the actually formal verified code was really correct! But the underlying library was not. Nor was the code responsible for reading the file.
So: who verifies the verifiers? LLMs, of course :)
#Nextcloud #Preview Happy to say that my beta tester (aka my wife) just found out that if you have 100 PDFs in a folder, and open it in Nextcloud for the first time, it will
block
your
nextcloud
for
the
forseable
future!
Luckily Claude found the configurations in config.php:
```php
'preview_concurrency_all' => 4, // max parallel preview processes total
'preview_concurrency_new' => 2, // max parallel processes for *new* previews
```
Much nicer - slower previews, but works!
#Server #Hetzner Yay - I love being a sysadmin! Specifically in a professional network like Hetzner.
They seem to take security quite serious, so for a poor weekend sysadmin like me, forgetting to block requests to private addresses means they send angry emails.
But the "I hereby confirm that I have written the statement myself and not generated it by using AI." was too funny to not share it...
TIL the adoption dates of the SI prefixes:
1795: deca, hecto, kilo (10**3)
1873: mega (10**6)
1960: giga, tera (10**12)
1975: exa, peta (10**18)
1991: zetta, yotta (10**24)
2022: ronna, quetta (10**30)
So between 1960 and 1991 it was nearly two powers of 2 per year, then it dropped to one power of 2 per year.
So we might have to wait until 2050 or so for the 10**36 prefixes :)
I ignored the negative prefixes, which are symmetric.
#CRA - Cyber Resilience Act in the EU explained quickly with bikes:
https://fosdem.org/2026/schedule/event/BFMWKT-cybersecurity-risk-assessment-for-cra/
And now I also need to watch this one to understand how this works together with Open Source Software, and when you need to follow CRA...
Surprise - the nice #LLM overlords are not specifically suited in education - at least not for now:
It looks at one of the most cited meta-study on using ChatGPT in schools, which showed improvements. But a closer look at the papers used in the meta-study showed a lot of low-quality papers...
@paul@m.pcgt.link OK, you nerd-sniped me. After spending a long time on
https://en.wikipedia.org/wiki/Knuth%27s_up-arrow_notation#Computing_10_%E2%86%91n_b
and my mind exploding, I asked Claude to give me the number of digits, and its prediction was:
The digit count is not just astronomically large — it can't be written down in any normal sense.
So I suppose that even a kiloknuthmeter is larger than our universe.
Or did you mean "stacked" in the sense of H_3?
@bascule@mas.to OK, it's nitpicking. But in order to correctly compare comparable values, I think we should get used to follow a common way of defining what is happening:
- Power, [W], as the instantaneous delivery, like litre/s for a waterhose
- Capacity, Energy, [Ws], [Wh], [Jules], as the reserve in the system, like litres of water
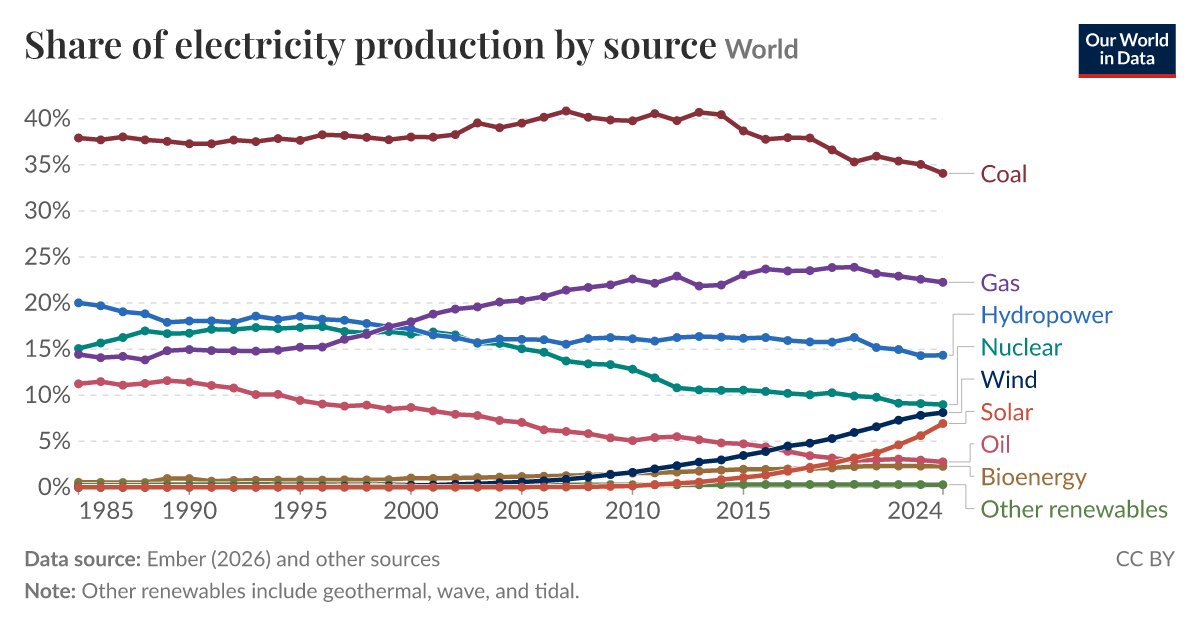
Both are important - one to fulfil the instantaneous need, one to hold to it as long as possible. And I hope both will increase so we can ditch non-renewables!
More than 90 per cent of California’s battery fleet has been built in the last five years, lifting total capacity to more than 17 GW from just 1.3 GW in 2020, according to Ember analyst Nicolas Fulghum.
Anyway, definitely no nuke bro here. Just a smartass with some solar panels on top of his roof and who calculates twice a year if batteries are finally worth it... So I prefer my capacity in Jules and not watts :)
@GossiTheDog@cyberplace.social @malwaretech@infosec.exchange I really liked this article here:
https://aisle.com/blog/ai-cybersecurity-after-mythos-the-jagged-frontier
Their TLDR is: yes, it's impressive, but with a good framework you can already do it for much cheaper. Also, depending on the vulnerability, some of the cheapest models are sometimes better than the most expensive ones.
And, yes, it's a looong ad for their company. But I think they deserve it :)