#apt
103 posts · Last used 8d
Improved indicators: Formbook (+1), RemcosRAT (+2), NetSupportManager RAT (+1), Coinminer (+1), ClickFix (+1), Chaos (+1) and Bashlite (+1). https://vuldb.com/actor #apt #cti #ioc
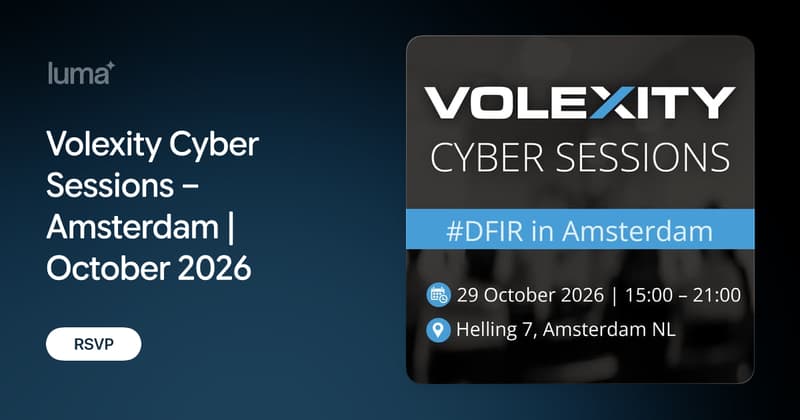
State-aligned threat actors continue to evolve their operations and infrastructure tactics. Feike Hacquebord will be speaking at our upcoming Volexity Cyber Sessions in Amsterdam (October 29) about APT campaigns by Russia-, China-, and DPRK-aligned actors targeting Europe in 2026.
Feike will examine China-aligned residential proxy networks built on compromised IoT devices, DPRK-aligned operations run from static Russian IP addresses and hundreds of VPS servers, and a decade of Pawn Storm (APT28/Fancy Bear) activity. He will also explain how domestic Chinese AI capabilities have reduced China-aligned actors' dependence on frontier Western models.
Seating is limited. Register now to secure your spot: https://luma.com/0qtkw49c
#dfir #threatintel #apt
Replying to
Reward: You've received a laminated Storm-2570 Awareness Certificate. It does not stop ransomware.
https://www.microsoft.com/en-us/security/blog/2026/09/24/beyond-ransomware-tracking-storm-2570-consistent-tradecraft-across-deployments
#Ransomware #ThreatIntelligence #Storm2570 #CyberSecurity #APT #FollowTheTrail (3/3)
New indicators for: Ghost RAT (+1), Quasar RAT (+1), Remus (+1), AsyncRAT (+2), Havoc (+1), Hook (+1) and AdaptixC2 (+5). https://vuldb.com/actor #apt #cti #ioc
Replying to
Known issue: the group demonstrates rapid customization across multiple platforms simultaneously, which is a feature for them and a bug for you. Patch Google Chrome and Microsoft Windows immediately.
Reward: You've received a Changelog of Regret. It ships with no hotfix.
https://osintsights.com/china-aligned-group-exploits-chrome-microsoft-zero-days?utm_source=mastodon&utm_medium=social
#ZeroDay #CyberSecurity #Chrome #Windows #APT #ExploitChainUnlocked (2/2)
🤖 North Korean APT group "WaterPlum" compromised at least 30,000 devices worldwide (Dec 2025–Jul 2026) and moved over $10.7M in stolen cryptocurrency to North Korea, per a joint law enforcement advisory.
🔗 https://www.bleepingcomputer.com/news/security/north-korean-waterplum-hackers-infected-30-000-devices-worldwide/
#DataBreach #APT #InfoSec #CyberSec
Replying to
Reward: You've received a complimentary Pending Ticket — estimated resolution time is never.
https://thehackernews.com/2026/09/china-linked-hackers-exploit-chrome.html
#CyberSecurity #ZeroDay #Chrome #Windows #APT #Malware (3/3)
Cyberattack on #UK #Airport Operator MAG Exposes Data of 8.7 Million Customers Across Three Airports
https://securityaffairs.com/197966/data-breach/cyberattack-on-uk-airport-operator-mag-exposes-data-of-8-7-million-customers-across-three-airports.html
#securityaffairs #hacking #APT
Added some more indicators for: GuLoader (+1), AgentTesla (+1), Kimwolf (+9), DeimosC2 (+1), DanaBot (+1), Chaos (+1) and AdaptixC2 (+2). https://vuldb.com/actor #apt #cti #ioc
Alert. Masowo hackują sieci WiFi w hotelach / kawiarniach / na konferencjach na całym świecie. Cel: podróżujący pracownicy korporacji.
O akcji ostrzega Microsoft, pisząc: zidentyfikowaliśmy w kilku krajach powszechne naruszenia bezpieczeństwa sieci WiFi w organizacjach z branży hotelarsko-gastronomicznej oraz w innych sieciach obsługiwanych przez urządzenia wspierające captive portal.Najpierw przejmowane są routerki dające dostęp do sieci WiFi. Umówmy się, często jedynym zabezpieczeniem w hotelu jest nieaktualizowany od 5 lat TP-Link...
#Aktualności #Apt #Cyberawareness #Hotele #Rosja #Wifi
https://sekurak.pl/alert-masowo-hackuja-sieci-wifi-w-hotelach-kawiarniach-na-konferencjach-na-calym-swiecie-cel-podrozujacy-pracownicy-korporacji/
Mitra 5.8.0 now available on Docker Hub and on my APT repository!
https://hub.docker.com/r/fjox/mitra
https://apt.hostnetwork.xyz/README.txt
#mitra #apt #docker #container
🇮🇷 Iran Cyberattacks Against Minnesota Water Systems
📝 Attribution is preliminary , and so far it seems no real damage. And it seems like this is a cam...
https://www.schneier.com/blog/archives/2026/08/iran-cyberattacks-against-minnesota-water-systems.html
📰 Schneier on Security
#APT #AI
We have improved indicators: Formbook (+1), BianLian (+1), XWorm (+3), SVCStealer (+1), Overlord RAT (+1), PureLogs Stealer (+3) and Sliver (+1). https://vuldb.com/actor #apt #cti #ioc
We have added indicators: Quasar RAT (+1), Eye Pyramid (+1), Havoc (+1), Evilginx (+2), Vidar (+32), Atomic Stealer (+1) and NetSupport (+1). https://vuldb.com/actor #apt #cti #ioc
#apt
7d35283f975f9d7a2ff335706527771bf3d7e75f8b6c8762f6165adcfe8d2cf5
ASEAN Semiconductor Roadmap 2026_2030_Draft v0 (For Input)_for ATF-JCC.docx
web-api.nrilsnalnrlne.workers[.]dev
Improved indicators: Tsundere (+1), Meterpreter (+1), Cobalt Strike (+10), ValleyRAT (+1), Remcos (+1), STRRAT (+1) and AsyncRAT (+10). https://vuldb.com/actor #apt #cti #ioc
Iranian APT Nimbus Manticore Deploys NightLedger Backdoor
🔗 https://cybersecurefox.com/en/nimbus-manticore-nightledger-bridgehead-arcbridge
#Nimbus #Manticore #NightLedger #BridgeHead #ArcBridge #Iranian #APT
Replying to
Reward: You've received the Gilded Pitfall — a decorative tile that is also a pit.
#AISecurityBreach #HuggingFace #CyberSecurity #ZeroDay #APT #AchievementUnlocked (3/3)
🤖 Laundry Bear (Void Blizzard), Russian state-sponsored group, exploits Exchange OWA zero-day to deliver OWAReaper backdoor. Targets orgs in Europe and US for long-term mailbox persistence. CISA notified.
🔗 https://www.bleepingcomputer.com/news/security/russian-hackers-exploit-exchange-owa-zero-day-for-long-term-mailbox-access/
#0day #RCE #CyberSec #Exchange #APT
🇮🇷 Iran-linked CyberAv3ngers suspected in attacks on Minnesota water systems
📝 Security researchers at Te...
https://www.theregister.com/security/2026/07/29/iran-linked-cyberav3ngers-suspected-in-attacks-on-minnesota-water-systems/5280357
📰 www.theregister.com - Articles
#APT #DataBreach