Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Tuxxin

@tuxxin@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Building security & developer tooling in the open — whack.sh (multi-egress URL threat scanner), qsa.sh (instant external scan via curl), curlhub.sh (curl-native dev tools), worldip.io (IP intelligence). Honeypot operator. Linux since the 90s. Orlando, FL.

1 Followers
2 Following
4 Posts
Joined July 31, 2026
Website:
https://tuxxin.com
Projects:
https://tuxxin.com/projects
Code:
https://github.com/Tuxxin
Based:
Orlando, FL
Open post
Tuxxin @tuxxin@infosec.exchange
· 4w ago
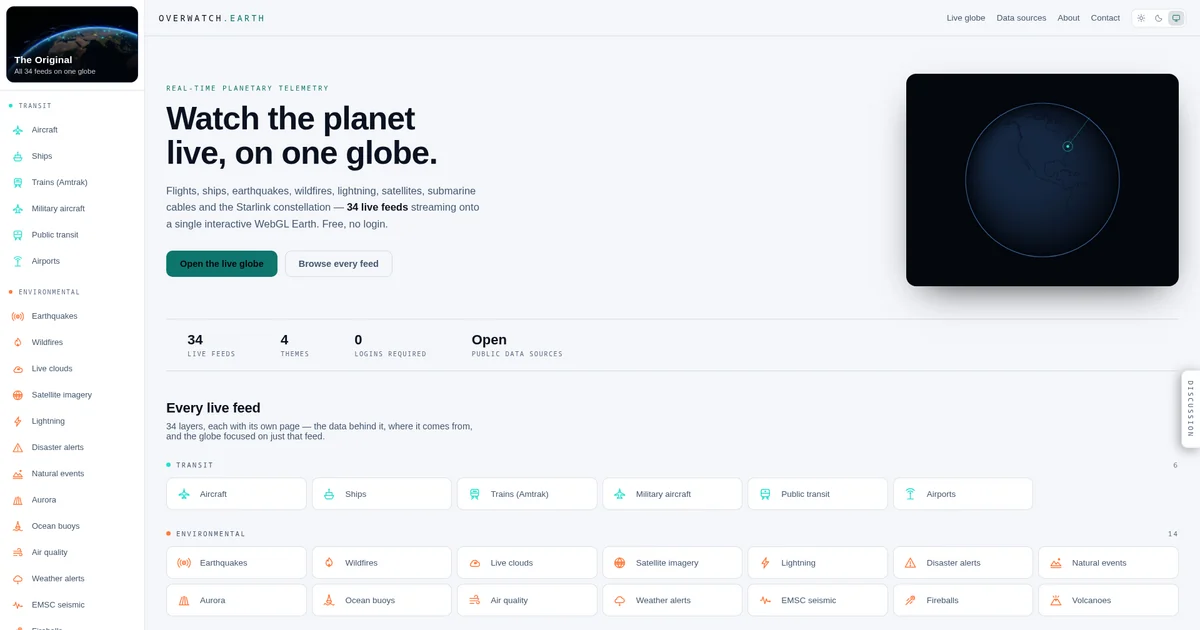
overwatch.earth rebuild adds feed pages, discussions, and passwordless comments overwatch.earth now opens on a website rather than the globe. All 34 live feeds have their own pages, every map carries a comments drawer, and commenting uses a pin code emailed to you. https://tuxxin.com/blog/overwatch-earth-rebuild-discussions-passwordless-comments #overwatchearth #livedata #opendata #webgl
overwatch.earth rebuild adds feed pages, discussions, and passwordless comments
Tuxxin

overwatch.earth rebuild adds feed pages, discussions, and passwordless comments

overwatch.earth now opens on a browsable site: 34 live feeds with their own pages, community discussions, feed submissions, and passwordless pin-code comments.

0
0
0
0
Open post
Tuxxin @tuxxin@infosec.exchange
· 2w ago
Brevo delivered ClickFix malware to 51 of its own customers Kirk at ADAMnetworks found Brevo serving ClickFix malware from its own infrastructure to 51 customer sites. I took part in the investigation using whack.sh. https://tuxxin.com/blog/brevo-clickfix-customer-sites #security #threatintelligence #whacksh #clickfix
Tuxxin

Brevo delivered ClickFix malware to 51 of its own customers

Brevo delivered ClickFix malware to 51 customer sites in September 2026. Research by ADAMnetworks, with Tuxxin taking part via whack.sh.

0
0
0
0
Open post
Tuxxin @tuxxin@infosec.exchange
· 1w ago
Invoice-named scripts drop a DLL-sideloading backdoor behind Pakistan Navy decoys Nine files named Invoice1.txt to Invoice9.txt in an open web directory are one-line Windows scripts that open a decoy PDF and install a backdoor inside a signed Microsoft program. The decoys include Pakistan Navy planning minutes for Exercise AMAN 2027 and quotations from a Navy supplier. The command server was live o… https://tuxxin.com/blog/fake-invoices-pakistan-navy-backdoor #threatresearch #malware #backdoor #dllsideloading
Invoice-named scripts drop a DLL-sideloading backdoor behind Pakistan Navy decoys
Tuxxin

Invoice-named scripts drop a DLL-sideloading backdoor behind Pakistan Navy decoys

Fake invoice scripts drop a DLL-sideloading backdoor behind decoys aimed at the Pakistan Navy, its suppliers and Pakistani government bodies.

0
0
0
0
Open post
Tuxxin @tuxxin@infosec.exchange
· 2mo ago
Replying to
@nixCraft@mastodon.social it took far too long
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:34:56 UTC