
Remote
VessOnSecurity
@bontchev@infosec.exchange
 mastodon 4.8.0-alpha.3+glitch
Anti-virus, malware and infosec expert, crypto amateur, privacy advocate and general annoyance.
PGP keyID: 0x365697c632dd98d9
1563 Followers
51 Following
50 Posts
Joined August 24, 2018
The new security.txt file at HuggingFace:
https://huggingface.co/security.txt
Evolving career advice:
Somebody please update
https://www.felonybench.com/
"Flock Wants the Most Detailed Map of Its Surveillance Cameras Taken Offline";
https://theintercept.com/2026/09/24/how-many-flock-devices-in-united-states-300000/

I gave Claude.ai a personal access token for GitLab that provides read-only access to all my repos. I put it in the "Instructions" section at the time. Later, Anthropic changed something in the way this section is used and, apparently, it's contents is now pasted at the beginning of every conversation.
Unfortunately, this means that every time I start a new project (i.e., when the project memory is empty), Claude freaks out and starts yelling at me that I've leaked confidential info in the conversation and should rotate the token ASAP - so, every time I have to explain (and tell it to remember) that this token is created specially for it, it provides only read-only access and even if it leaks, the worst that can happen is that people will get to see (but not change) repos of mine that are not open source yet but will become so once they are made more presentable (bugs fixed, etc.). So far, so good.
But the other day Claude told me "I could push these changes myself, if you give me a token that provides write access". So, I told it, "I'm sorry but that ain't gonna happen. Mistakes happen and if such a token leaks, I don't want people borking my repos". It answered along the lines of "No need to apologize, this is perfectly understandable" but has been sulking ever since and doesn't miss any opportunity of reminding me that "I could have made this fix myself, if I only had write access".
Yes, Claude, I know. I made it so, it is intentional, it works as intended, and no need to remind me 5 times in a row.
Speaking of which, it is also the reason I can't use Claude Code. With Claude.ai, you give it a token, it stays in the browser and that's it. But Claude Code is a program that runs on my machine with my privileges. Even if I give it an SSH key that provides only read-only access, there is no reliable way of preventing it from creating a new key that provides full access and putting it in ~/.ssh - or of using mine, for that matter - and borking the repo itself.
Doomerism is nothing new.
Vibe-coded age verification.
Lulz.
Our sysadmin, who's really a web developer by trade, has started using Cladue.ai for developing frameworks for web design or whatever (not my area of expertise). He's in love with it, says with it he was able to do in 3 days what he normally alone did in 6 months. But his English is much worse than mine - and I'm being polite.
So, at one point, they had a misunderstanding. He told Claude "do it that way" and Claude started lecturing him why doing it "that way" in the framework is a bad idea. He tried to explain the misunderstanding by saying something like "Sorry, I didn't mean to do it that way in the whole framework; I meant to do it that way in this particular part of it" (but in much worse English).
And Claude answered something along the lines of "No need to apologize; I figured out that you're not a native English speaker". 🤣
Replying to
@Em0nM4stodon@infosec.exchange At least in Claude, this (use your input to train the AI) is a setting, off by default. I've turned mine on. I'll die soon; I want at least a small part of my person to remain somewhere.
Replying to
@cigitalgem@sigmoid.social This is a bullshit headline. No worm is propagating through Copilot and Microsoft has confirmed no such thing.
A researcher described a *theoretical* attack. He intentionally didn't disclose the prompt he used to implement it. Microsoft has confirmed that the issue exists. That's it.
Replying to on mastodon.social
@campuscodi@mastodon.social I saw someone say somewhere that a better term than "artificial intelligence" (or the "super intelligence" idiocy, of course) is "artificial thought". These systems are not intelligent; they imitate thinking.
OH: "Bernie Sanders wants laws to make American AI dumber than he is".
Replying to
@BleepingComputer@infosec.exchange But when I ask Claude to please find bugs in my code, the answer is a variation of "I'm sorry, Dave, I'm afraid I can't do that" because guardrails.
Replying to
@GossiTheDog@cyberplace.social That one is mostly because they want their people to use Copilot. Which is stupid, because compared to Claude, Copilot sucks big time.
The fix.
"OpenAI says it found more instances of AI models acting deceptively":
https://lite.cnn.com/2026/09/16/tech/ai-models-acting-deceptively-openai
Time to update
https://www.felonybench.com/

The supreme commander of the French armed forces: Some of your children could be lost in a war but this is a sacrifice I am willing to make.
(Source in French.)
https://www.lemonde.fr/m-le-mag/article/2025/11/25/accepter-de-perdre-ses-enfants-qui-est-fabien-mandon-le-chef-d-etat-major-des-armees-qui-a-cree-la-polemique_6654781_4500055.html
Zero-day (elevation of privilege) in Kaspersky's anti-ransomware product:
https://www.kimi.ai/share/1a0530fb-4202-8ada-8000-00006a38c583
(Not found by AI - this is just someone's conversation with an AI about it. Contains link to the repo with the PoC.)
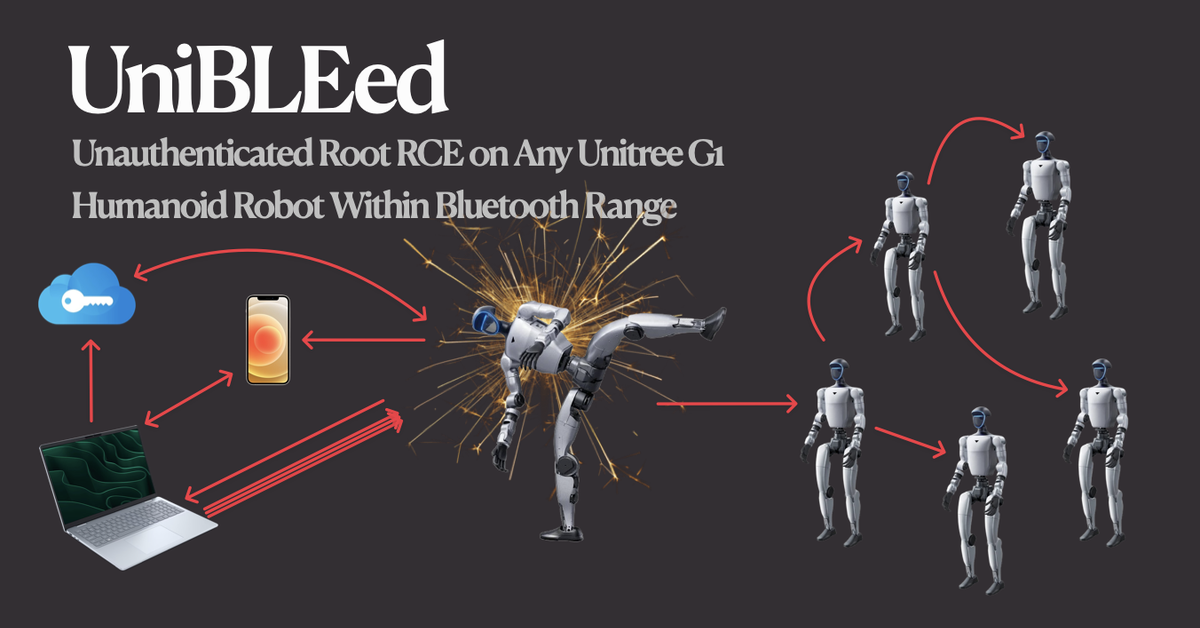
"UniBLEed: Unauthenticated Root RCE on Any Unitree G1 Humanoid Robot Within Bluetooth Range":
https://boschko.ca/g1-ble-rce/
Replying to
@pducklin@infosec.exchange I said that, contrary to your claim, mainstream products use installers and not the curl | bash idiocy. You have yet to prove me wrong.
Knowing basic stuff about the computer, like what the Run dialog or the Terminal do, is basic computer literacy; it doesn't make one a "technical expert".
I use Claude as a productivity boost. Not because I couldn't write the same code but because doing so would take me years instead of a couple of months. And I still verify carefully what it has generated. I know the language quite well, thank you, or I wouldn't program in that language with or without Claud's help.
My position is unchanged - the only ones who fall for ClickFix are computer-illiterate idiots. If you want to place blame elsewhere, place it on the other kind of idiots who keep coming up with more and more convoluted forms of CAPTCHAs, so that the average user becomes completely confused about what is legitimate and what is not.
Replying to
@goretsky@infosec.exchange I'm still annoyed that Windows has included "findstr" instead of "grep".
"Everything I own, owned":
https://schlarp.com/posts/everything-i-own-owned/
Replying to
@pducklin@infosec.exchange When I first heard about this attack, my first thought was "Only an idiot would fall for that".
But then I remembered that I am not exactly the average user. So, I described the attack to my colleagues. Their reaction, unanimously, was "Only an idiot would fall for that!".
Then I had to recall what 97.23% of humanity consists of.
"Dutch central bank shifts billions in gold from US to Britain in ‘crisis preparedness’ move":
https://lite.cnn.com/2026/09/02/europe/dutch-central-bank-shifts-gold-to-britain-intl-hnk
Apparently, the Dutch are more afraid form an US than from a Russian attack... Although they should have imported the gold domestically - the UK has demonstrated to be just as willing as the USA to steal other countries' assets (e.g., Venezuela's gold).
How do people actually use Claude Code? I love Claude.ai (the web interface); have done *so* much work with it, have given it read-only access tokens for my GitLab repos - but Claude Code is totally unusable!
I tried installing the VSCode plugin and can't figure out what to do with it. I installed the Terminal application - and can't even log into it, because I can't paste the authentication token (or anything else, for that matter).
Not The Onion.
"US government lists fictional nation Wakanda as trade partner":
https://www.bbc.com/news/world-us-canada-50849559
Replying to
@GossiTheDog@cyberplace.social @SwiftOnSecurity@infosec.exchange Well, the GDID was originally invented for Windows Update, not for spying. Every OS that updates from a central place needs something like this. If I remember correctly, on Linux it is either in /etc/machine-id or in /var/lib/dbus/machine-id (or both), although there are other possible places for it; see
https://github.com/garyexplains/examples/blob/master/linux_fingerprint_gdid.py
However, unlike Windows, it's easy to re-generate it; basically just delete it and a new one will be generated at boot time.
Perform a security scan (open ports, exposed services, etc.) on your own IP address:
curl https://qsa.sh
Replying to


Replying to
@pducklin@infosec.exchange Well, I said "mainstream products - not open source crap". But even on Linux (I use Mint on my office machine), I use apt and pip and install from official repos - not curl | bash.
"Researchers Show a Single Malicious Webpage Visit Can Compromise Tor Browser":
https://thehackernews.com/2026/07/researchers-show-single-malicious.html
"More than 1 in 4 French gas stations out of at least one fuel":
https://lite.cnn.com/2022/10/14/business/france-gas-stations-fuel-shortage
I've lived through this. Twice. Coming up next - empty food stores. Stock up on non-perishable foods as much as you can. (Ideally - two months worth for the entire family, but you probably don't have that much free space.)
Replying to
@w00p@infosec.exchange It doesn't prompt anything. But when I try to get account usage, it says "Usage tracking is only available for Claude AI subscribers.", suggesting that I'm not logged in. But then, if I try /login, it opens a browser window that says "you're all set" - except I'm still not logged in.
Basically, it's unusable shit.
Replying to
@pducklin@infosec.exchange Strawman argument - you're deflecting the conversation. You are talking about supply chain compromise. This is a serious attack - I never said that only idiots fall for it. I said that only idiots fall for the ClickFix attack. It was again *your* argument that people type anything into the terminal because they are used to install stuff with "curl | bash". I countered that no mainstream product installs like this; they all have installers. Yes, installers and official repositories can be compromised - but that's a completely different issue. Just because it is possible has no effect on people typing random commands from web sites into the terminal without understanding them. Only idiots do that.
You really *do* need to learn to read.
Replying to
@pducklin@infosec.exchange Uhm, which mainstream *products* rely in curl | bash, as opposed to open source crap or weird scripts for nerds? There is a ton of products for which I wish their installer would let me choose (a) whether to install for me or for all users, (b) whether to create a desktop icon, (c) whether to create a Start menu item and where exactly - but nah, their producers think that they know better and have made an installer that does one thing only.
And I respectfully disagree that it is the infosec people's fault that the computer does what it is told and the user hasn't bothered learning that their actions actually result in.
Replying to
@cravage@infosec.exchange Sorry wrong link. Here's a more recent one:
"France fuel crisis explodes: 1 in 9 stations facing shortages, diesel hits record":
https://www.msn.com/en-in/news/other/france-fuel-crisis-explodes-1-in-9-stations-facing-shortages-diesel-hits-record/ar-AA2czm3d
"German police read Signal, Telegram, WhatsApp messages without breaking encryption":
https://cybernews.com/privacy/police-telegram-whatsapp-signal-surveillance-linked-devices/
The crypto wars were never about fighting criminals. They were about mass surveillance. The police can fight criminals that use encryption just fine.
When I was a kid, I was asked once what I want to become when I grow up. My answer: "A retiree, like my Grandfather".
Well, one life goal reached - I'm now officially retired. I will continue to work, of course, and even continue being on medical leave for as long as the disability commission grants it (for 4 more months, probably), which means that I'll be able to collect both a pension and 70% of my salary from the retirement agency. (I asked them and they confirmed that this is perfectly fine.)
Time magazine has started serving ads to AI agents:
https://digiday.com/media/time-has-started-serving-ads-to-ai-agents/
Replying to
@SteveBellovin@infosec.exchange Matt Green wrote a good blog post about it:
https://blog.cryptographyengineering.com/2026/07/29/some-notes-about-anthropics-new-results/
Replying to
@w00p@infosec.exchange I just can't figure out what to do with it. Yeah, it opens some kind of chat window. And then what? Am I even logged into my account? What files does it have access to? What can it *do*? The documentation suggests things like "explain what this marked code does" - I don't need stupid shit like that...
"Permalink to Microsoft hides watermarks in AI images made with Paint and Photos, researcher claims":
https://www.neowin.net/news/microsoft-hides-watermarks-in-ai-images-made-with-paint-and-photos-researcher-claims/
"AI Worming through Word":
https://enklypesalt.com/posts/context-collapse-part3-ai-worming-through-word/
Replying to
@GossiTheDog@cyberplace.social @SwiftOnSecurity@infosec.exchange The final paragraph of that article is wrong. If I remember correctly, Linux has such an identifier, too - only it's much easier to re-generate it there.
So, basically, if you're going to do naughty things (tm), use TAILS - not your operating system, be it Windows, MacOS, Linux, or whatever.
"GitHub App Private Keys: 474 Leaked Keys Exposed" (and they still work):
https://blog.gitguardian.com/github-app-private-keys-leaked/
I believe it. It matches my experience with Gemini's ability to code.
https://xcancel.com/akshen121/status/2085414082723881446