Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Paul Ducklin

@pducklin@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

I’m Paul Ducklin, but everyone calls me Duck.

I’ve been in cybersecurity since the early days of computer viruses, right at the pointy end - reversing, coding, analysing, responding, and supporting the community. (You may know me as one of the names behind the legendary EICAR test file.)

I’m an accomplished, award-winning technical writer well-known for explaining even super-complex technical stuff in plain English, from esoteric cryptographic bugs to wacky security exploits.

I’m an experienced and entertaining speaker who consistently gets glowing feedback for the quality and impact of my talks, live malware demos, and webinars.

Readers and audiences love my material and enjoy coming back for more,

If you have any writing, speaking or presenting you’d like me to do for you, or if you’re a journalist looking for informed and eminently quotable content, please get in touch via my ABOUT ME link.

93 Followers
87 Following
50 Posts
Joined March 20, 2026
ABOUT ME:
https://pducklin.com/about
Open post
Paul Ducklin @pducklin@infosec.exchange
· 1w ago
RE: https://infosec.exchange/@bontchev/117314994533181052 Ah, I forgot you are a Windows user, where installers are a differently interesting risk,given that it’s old-school “click link, download file, run MSI or EXE.” Being zoomed in on Windows does tend to narrow your viewpoint and your experience a lot, given that other OSes are available, and used by a majority of server-style systems and a significant minority of laptop users. (I’m ignoring iOS and Android, which are Mach/BSD and Linux at their core respectively, because of their strongly regulated installation ecosystems.) There are certainly mainstream products - by any reasonable definition of mainstream - that officially document curlbash copy-and-paste operations for installation. My own system has Rust and Julia installed in just that way, though I downloaded the script first, for what that’s worth, examined it briefly, and then ran it later instead of piping the download filelessly into a command prompt. I guess it’s sad that age hasn’t mellowed you into being respectful (or gentle) enough not to call people “idiots” because they don’t know Windows like you do. People aren’t stupid just because their knowledge and experience are different from yours. Sometimes, bad learning comes from bad students. But surprisingly often it’s as much or more the result of bad, or unsympathetic, or unthoughtful, or hypocritical teachers. As others have said before, with humour but also in seriousness…. Vesselin, you need to get out more.
Open quoted post
Quoting
VessOnSecurity
@bontchev@infosec.exchange
@pducklin@infosec.exchange I said that, contrary to your claim, mainstream products use installers and not the curl | bash idiocy. You have yet to prove me wrong. Knowing basic stuff about the computer, like what the Run dialog or the Terminal do, is basic computer literacy; it doesn't make one a "technical expert". I use Claude as a productivity boost. Not because I couldn't write the same code but because doing so would take me years instead of a couple of months. And I still verify carefully what it has generated. I know the language quite well, thank you, or I wouldn't program in that language with or without Claud's help. My position is unchanged - the only ones who fall for ClickFix are computer-illiterate idiots. If you want to place blame elsewhere, place it on the other kind of idiots who keep coming up with more and more convoluted forms of CAPTCHAs, so that the average user becomes completely confused about what is legitimate and what is not.
Open quoted post
infosec.exchange

VessOnSecurity: "@pducklin I said that, contrary to your claim, ma…" - Infosec Exchange

2
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 1w ago
RE: https://infosec.exchange/@bontchev/117337322796120995 Hahahaha. So the official download repositories of Julia and Rust are “open source crap,” but somehow the entire supply chain of dependencies that you invite into your world when running pip to grab some new packages is trustworthy? But, of course, “you know what you are doing,” because everyone else is some kind of idiot while you are not. Somehow you expect pip install to be safer than curlbash… when they are much more similar in terms of risk than they are different - basically, download a chain of stuff from the internet, unpack it into memory or onto disk or both, run what you get out, rinse, repeat until dependencies satisfied. Well, good luck with that. (To be clear, you really *do* need to get out more.)
Open quoted post
Quoting
VessOnSecurity
@bontchev@infosec.exchange
@pducklin@infosec.exchange Well, I said "mainstream products - not open source crap". But even on Linux (I use Mint on my office machine), I use apt and pip and install from official repos - not curl | bash.
Open quoted post
infosec.exchange

VessOnSecurity: "@pducklin Well, I said "mainstream products - not…" - Infosec Exchange

1
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2w ago
𝕋𝔸𝕃𝔼𝕊 𝔽ℝ𝕆𝕄 𝕋ℍ𝔼 𝕊𝕆ℂ: "MFA - The what, the how, and the why." Join me and David Emerson for a delightfully jargon-free, plain-English discussion of multi-factor authentication. We explain how and why the main forms of MFA work, while at the same time reminding you of the cybersecurity risks that MFA can't solve. (Side-story. In this episode, David mentioned in passing that he needed to buy a new laptop. I couldn't resist asking him what he felt about the price of RAM these days, but probably shouldn't have 😬) LISTEN NOW! Search "Tales From The SOC" in your favorite podcast feed, or download the MP3 directly. (Full links to feeds and files in comments below.) https://podcasts.apple.com/us/podcast/mfa-the-what-the-how-and-the-why-s1-ep028/id1755463306?i=1000791349911
MFA - The what, the how, and the why | S1 Ep028
Apple Podcasts

MFA - The what, the how, and the why | S1 Ep028

Podcast Episode · Tales From The SOC · September 23 · 23m

1
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
Replying to
Apple: https://podcasts.apple.com/us/podcast/ai-enterprise-best-practices-s1-ep026/id1755463306?i=1000778561277 Open Spotify: https://open.spotify.com/episode/6MsZjJCobjBdlJykVdeE7c?si=m7ou14RnQ1mGNVvmTcmL7A Podbean: https://tales-from-the-soc.podbean.com/e/ai-enterprise-best-practices-s1-ep026/ Audible: https://www.audible.co.uk/pd/B0HBR8CX8J
podcasts.apple.com
2
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago

New podcast: AI - ENTERPRISE BEST PRACTICES

Duck (🦆 yes, that is I!) and @d@merveilles.town (David Emerson) of ☀️SolCyber give you a well-informed guide to using AI safely, all in plain English.

Straight talk, good humour, no FUD, and zero hype - this is a short, digestible, and very instructive episode.

Listen now 🔈, or read 📖 a cleanly-edited transcript (curated by me - free of AI guesswork and speculation 😬):
https://solcyber.com/tales-from-the-soc-ai-enterprise-best-practices-s1-ep026/

(More links in the comments for a variety of podcast feeds.)

merveilles.town

David Emerson (@d@merveilles.town) - Merveilles

1
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 3mo ago

TALES FROM THE SOC: Exploits versus Entropy - are the shiniest new threats worse than the disruptive disorder of history? Join me and David Emerson (@d@merveilles.town) for another thoughtfully outspoken but infectiously good-humored episode 😬

Find this awesome ☀️SolCyber podcast on your favorite podcast feed, or listen directly here:

https://tales-from-the-soc.podbean.com/e/exploits-versus-entropy-s1-ep-025/

Exploits versus Entropy | S1 Ep025 | Tales From The SOC
tales-from-the-soc.podbean.com

Exploits versus Entropy | S1 Ep025 | Tales From The SOC

Are the shiniest new threats worse than the disruptive disorder of history?  Paul Ducklin and David Emerson are in great form, as always - thoughtfully outspoken but infectiously good humored at the same time.

1
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 3mo ago
𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: Some secret software strings are so cool that they're now paradoxically part of public programming practice. (Try connecting to Google's Gmail service via IMAP and sending it the command XYZZY :-) Find heaps of facts, fun, and plain-English explainers on the ☀️SolCyber blog: https://solcyber.com/amoss-almanac-like-a-dictionary-only-cooler/ #AmosArmadillo
solcyber.com
1
0
1
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

Hasbro, the games company, today made a non-April-Fool’s admission to the SEC that it was breached.

Sites are “undergoing maintenance,” and the biz says that disruption “may continue for several weeks.”

Often, that level of disruption turns out to mean “company-wide ransomware crisis,” but at this point, Hasbro probably only knows what it doesn’t yet know, if you know what I mean.

The company says it spotted the intrusion on 2026-03-28, but that’s not necessarily when the crooks first got in.

3
0
2
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: Ever mistyped or misread an obvious word? It's easily done...

Follow me, and Amos's cool Almanac, and lots more community-centered cybersecurity content, on the not-a-sales-schpiel cybersecurity site I write for called the ☀️SolCyber blog:
https://solcyber.com/blog
#AmosArmadillo

SolCyber

MSSP Blog | SolCyber the Modern Managed Security Program

SolCyber provides the latest information on how to tackle cyberthreats and immediately boost your security posture.

3
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 5mo ago

Join me and co-host David Emerson (@d@merveilles.town) - some strong words in this episode, but it's entertaining, educational, and good-humoured nevertheless!

Please give us a listen, like, boost, comment, subscribe, etc. (And message us if you have any funky topics you think we should cover in future!)

Search TALES FROM THE SOC in your favourite podcast feed, or find a human-curated, readable transcript plus tightly-edited audio on the ☀️SolCyber blog here:
https://solcyber.com/tales-from-the-soc-back-to-basics-s1-ep022/

solcyber.com
2
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 5mo ago

Online accommodation giant booking dot com has been breached, but seems to be rather coy about it so far.

The business is owned by a multibillion-dollar US company that owns numerous other online accommodation services, but so far only booking dot com seems to have been infiltrated in this attack.

As often happens, the biz has been quick to emphasise what was *not* stolen (financial data, apparently), but doesn’t yet seem to know, or to have said, exactly how many of its many millions of users were affected, or exactly what data *was* stolen.

The BBC reports that the breach “could include” victims’ booking details, names, addresses, emails, phone numbers, plus “anything you may have shared with the accommodation,” which one imagines might cover all sorts of information about children travelling with you, your vehicle, related travel plans and expected arrival times, and more.

Historical data - in other words, bookings already done and dusted - are apparently affected, not merely currently active bookings, but there’s no indication of how far back the breach goes.

Advice on “what to do” is hard to give in cases like this, where the business that has let you down still doesn’t know just how badly or how extensively.

Whatever you do, be careful of crooks who know or guess that you’re a booking dot com customer (and who may sound surprisingly believable through data acquired via this very breach) trying to conduct a follow-up scam, especially if they’re offering to “help” you recover in some way.

2
0
1
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

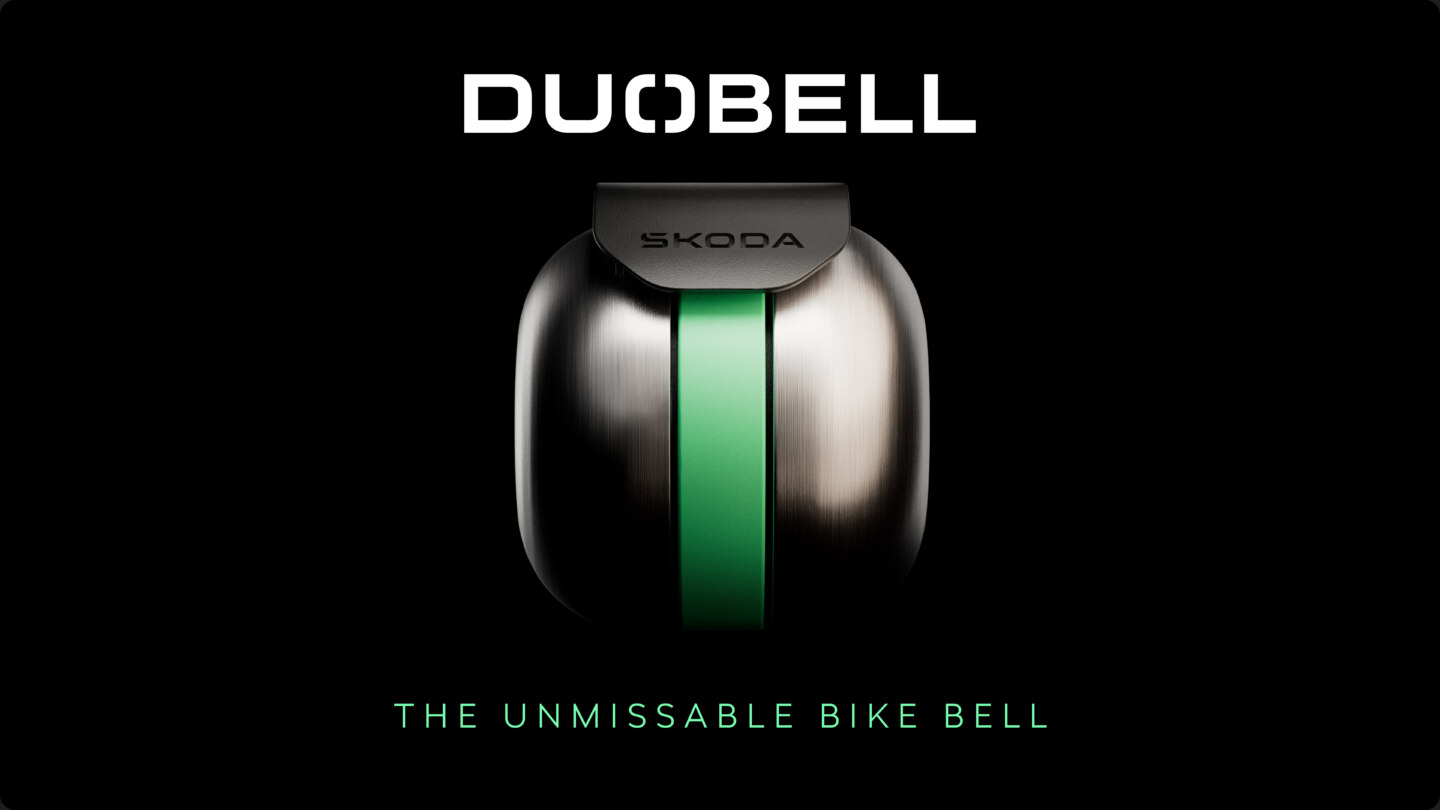
Funky audio science (or great marketing - time will tell :-) as automotive biz Škoda announces a new bicycle bell…

Old becomes new again with a product called “duobell” that aims to defeat the hazard of digital noise-cancelling headphones, using a 100% analogue, battery-free, finger-operated bell much like the one (or your parents, or grandparents) had back in 1979.

Anyone who rides a bicycle as their primary urban transport will know just how futile most bike bells are against distracted pedestrians glued to their phones and cocooned via headphones or earbuds. Shouting LOOK OUT very loudly will pierce most headphone audio-blankets, and the sound envelope of the words seems to transcend any language barrier, but it’s not exactly a friendly or socially respectable approach and can lead to pedestrians freezing rather than moving to safety.

Škoda claims to have perfected a resonator that can produce frequencies low enough to evade digital cancellation (about 750Hz, apparently) without needing something the size and mass of Big Ben, as well as a mechanical system for clanging forth a sort-of random mess of higher frequencies in short bursts that the cancellation algorithms simply can’t keep up with.

The theory is that pedestrians will hear what sounds like a bicycle bell even if they have taken active measures to shut such sounds out.

All in something that’s not much bigger than a traditional bicycle bell. (Think of a traditional circular dome-shaped bell but extruded into a slightly squashed sphere.)

Seems you can’t actually buy one yet, so there’s no chance to do the ultimate peer review of trying it for yourself, but if it works it will be a cool example of an “analogue computer,” albeit one that would probably have been impossible to design and build without advanced digital computers and manufacturing processes :-)

https://www.skoda-storyboard.com/en/skoda-world/skoda-duobell-a-bicycle-bell-that-outsmarts-even-smart-headphones/

Škoda DuoBell: A bicycle bell that outsmarts even smart headphones - Škoda Storyboard
Škoda Storyboard

Škoda DuoBell: A bicycle bell that outsmarts even smart headphones - Škoda Storyboard

Pedestrians wearing headphones are exposed to an increased risk of accidents. In an effort to reduce collisions with cyclists, Škoda Auto, in collaboration with scientists, introduces an innovative bicycle bell whose sound can penetrate even active noise cancellation systems. In doing so, it helps prevent injuries to both pedestrians and cyclists.

2
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

RE: @zackwhittaker@mastodon.social

Anyone who has space to say things like "PEBKAC" or "trust in tech because humans are the weakest link" is either a misanthrope or a paid-on-commission cybersecurity salesperson :-)

For example, we still hear advice such as "don't open emails (or view attachments, or click links) from unknown sources" spouted as if it were usable, let alone useful, advice.

Yet many employees are assigned to tasks in which opening attachments from new senders is a vital part of their job - try working in HR and refusing to open resumes sent in apparently good faith. Try working in accounts payable or legal and refusing to look at what might be a formal legal challenge such as a financial lawsuit threat or a DMCA takedown request that requires a response.

Same with advice such as "never read out a 2FA code to anyone over the phone," when some orgs explicitly ask you to do just that to "prove" you have the claimed phone number under your control right now. (I've had SMS codes sent to identify myself *by voice over the phone* from both a bank and a telco. The requests were real, even though the bank's own online ADVICE IN BIG LETTERS was never, ever, to tell SMS codes to anyone.)

mastodon.social
2
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

Here’s how the news of a hyperactive cyber gang going by “TeamPCP” broke recently…

This is the Aqua Security/Trivy attack that kicked off global concern about this attack group - a great plain-English writeup that explains just how much data, with immediate real-world value, can be grabbed in a single compromise.

(And watch this space - 🦆 I shall be back over the coming weekend with a follow-up story covering *at least three more attacks by the same group* in recent days, and what you can do to protect yourself.)

Learn why blindly automating everything in your supply chain is a Bad Idea!

On the ☀️SolCyber (@solcybermss@bird.makeup) blog:

https://solcyber.com/what-if-a-cybersecurity-tool-turns-against-you/

solcyber.com
2
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

Catch me and co-host David Emerson (@d@merveilles.town) of human-friendly cybersecurity outfit ☀️SolCyber (@solcybermss@bird.makeup) in the latest episode of the funky no-sales-schpiel podcast TALES FROM THE SOC…

We have some strong words to say about “Back to Basics,” but we retain our intellectual objectivity and our good humour throughout. And you can trust me on that 😬

Please give us a listen, like, boost, comment, subscribe, etc. (And message us if you have any funky topics you think we should cover in future!)

Human-curated, readable transcript plus tightly-edited audio available here:
https://solcyber.com/tales-from-the-soc-back-to-basics-s1-ep022/

solcyber.com
2
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

A great read for the weekend about navigating the perils of cryptographic complexity!

A low-severity bug just patched in OpenSSL reminds us to be not only mindful of history, but also willing to move with the times.

Entertaining, educational, and in plain English… ahem, by me on the ☀️SolCyber blog:
https://solcyber.com/openssl-bugfix-highlights-post-quantum-crypto-dilemma/

solcyber.com
1
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

The latest iPhone bugfixes just arrived (version 26.4.1).

The Apple Security Portal was unmodified when I did the update - which was useless to me, considering the page from which I triggered the update explicitly advised me to look there for the full story :-)

But the portal page had been updated, by the time I had patched and rebooted, to say, “26.4.1 has no CVEs.”

(A CVE is a standardised, unique bug identification number widely used to denote a software flaw that constitutes at least some sort of cybersecurity risk).

You’d think it would be easy enough for Apple to update its portal page *before* updating its update servers (if you get my drift), rather than *after*, but there you go…

1
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

Location tracking? Sometimes we can’t opt out, even if we want to; at other times we can’t opt in, even when it might be really useful…

I report on a tragic story that reminds us of the important nuances in managing hazard and risk in privacy and cybersecurity.

On the ☀️SolCyber blog:
https://solcyber.com/location-tracking-there-when-you-dont-want-it-not-there-when-you-need-it/

solcyber.com
1
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

FreeBSD Forums and Linux.org (plus others) were hit by a cross-site scripting (XSS) attack, but seem to have caught and patched it before any real harm was done.

Apparently, an outdated “XenForo” installation allowed an attacker to [1] create a new account, [2] submit a first post requiring approval, [3] steal the authentication token of the admin that looked at the new post to review it, [4] sneak in using that stolen token to deface the site.

Both sites have easy-to-find writeups on their home pages, which are worth reading, and say that they quickly took their servers offline, found when the attack started, reverted everything back to that point (a matter of hours), patched, decided that the attack had gone no further than defacement, and brought their forums back up.

New accounts created and genuine posts made during the danger period will presumably be lost, which is annoying but not dramatic.

Seems that no end-user accounts were harmed during the period that the exploit was in play.

So much for passwords, 2FA, MFA, TOTP, passkeys, hardware security authenticators, etc., eh? Bypass the lot by grabbing a “proof of coolness” badge from someone who already went through the whole login process so you don’t have to…

1
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 3mo ago

Bug had 98% CVSS score, but was 100% exploited against Nissan and perhaps 100s more companies…

Explainer and actionable advice by me on the ☀️SolCyber blog:

https://solcyber.com/nissan-staff-hacked-via-oracle-zero-day-bug/

solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
Craneware says that some of the stolen data was public already - but not all of it was! Reports itself to the FBI in the US and to the ICO in the UK. Story and useful advice on the ☀️SolCyber blog: https://solcyber.com/craneware-group-reports-huge-healthcare-data-breach-plays-down-risks/
solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago

European supermarket chain Lidl is in the news for a data breach.

Reports suggest that that the company has published a breach warning online in NL, BE, and DE - but good luck spotting it if you're just a regular user. (As a challenge, see if you can spot the link to the notification on the main DE site, shown below. Hint: that's not where they published it :-)

Early reports suggest that the breach affects online shoppers (so if you went into a shop and bought items directly off the shelves, whether you paid by cash or card, it sounds as though you're OK), and happened at a third-party service provider with whom a selection of Lidl's data was shared.

According Lidl's official report, the stolen data definitely includes at least name, email address, phone number, birthdate, and customer number.

Lidl's own notification says words to the effect that "at this point," the company is ruling out that passwords, physical addresses, bank details and other payment information were stolen. (For example, in Dutch, the phrase used is "op dit moment"; in French, it is "pour le moment.")

But, as Bleeping Computer suggested earlier today, further investigation might rule it back in, because this is not quite the same as saying "we are already permanently certain that this did not happen."

Watch this space, and if you're a Lidl online customer with a Lidl account, be doubly careful of emails, DMs or other messages that offer to "help" you to secure yourself in the aftermath of this breach.

In particular, don't take any action based on phone numbers, links, download suggestions, or other "advice articles" sent to you, because they could have come from anywhere. Use official links or contact details you obtained well before the breach - from existing invoices, for example, or from printed correspondence.

Remember, too, that search engines and AI agents can be tricked by sponsorship or lured by fake content into recommending bogus links.

Even if those links weren't deliberately crafted by scammers in advance, criminals regularly look out for "hallucinated" links that they can register in the hope of catching out well-meaning internet users, in a type of online treachery known in the jargon by the memorable name of *slopsquatting*.

0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
11 years in prison between them, but they may have millions stashed away for when they get out. About the latest Scattered Spider convictions… by me on the ☀️SolCyber blog: https://solcyber.com/two-attackers-imprisoned-over-transport-for-london-cyberattack/
solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 1w ago
RE: https://infosec.exchange/@bontchev/117343817597525873 You really love using the word “idiot,” don’t you? You seem to grasp every chance to be insulting and demeaning when it simply isn’t needed. As I said, you need to get out more.
Open quoted post
Quoting
VessOnSecurity
@bontchev@infosec.exchange
@pducklin@infosec.exchange Strawman argument - you're deflecting the conversation. You are talking about supply chain compromise. This is a serious attack - I never said that only idiots fall for it. I said that only idiots fall for the ClickFix attack. It was again *your* argument that people type anything into the terminal because they are used to install stuff with "curl | bash". I countered that no mainstream product installs like this; they all have installers. Yes, installers and official repositories can be compromised - but that's a completely different issue. Just because it is possible has no effect on people typing random commands from web sites into the terminal without understanding them. Only idiots do that. You really *do* need to learn to read.
Open quoted post
infosec.exchange

VessOnSecurity: "@pducklin Strawman argument - you're deflecting t…" - Infosec Exchange

0
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 5mo ago
Replying to
@bontchev@infosec.exchange Plenty of .tgz and .txz files around in the Unix world! (I didn’t mention file endings like .tar.gz because the tag “tar” is there in plain sight.) As an example, the oldest Linux distro that’s still going publishes its packages with .txz at the end, and as far as I know has always used .t_z (the middle letter has varied as preferred compression formats have come and gone). It may well be that this comes from the early days of floppy-based distros with files written in old-school DOS format (only one dot possible) but that’s moot today… I accept that ‘tar’ used as the name of the program denotes “tape archiver,” because that is its purpose, but as the usual tag added at the end of any filename it generates or consumes, I am happy enough with the explanatory text “tape archive,” because that is what is is. (I know a tar *file* is not exactly a *tape*, but we still “dial” phones and “film” videos, so I am happy with the word “tape” in a sort of metaphorico-historical way.) So I think I’ll stick with tar —> tape archive. Think of ‘archive’ as a verb when running the binary and as a noun when referring to its output.
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 3mo ago
𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: Ever wondered why internet RFC docs avoid the word "byte"? If you want to sound fabulously pompous, say, "Terms such as 𝘣𝘺𝘵𝘦, 𝘸𝘰𝘳𝘥, 𝘥𝘸𝘰𝘳𝘥, 𝘴𝘩𝘰𝘳𝘵, 𝘭𝘰𝘯𝘨, and 𝘲𝘶𝘢𝘥𝘸𝘰𝘳𝘥 don't have an obvious semantic or historical relationship with the number of binary digits (𝘣𝘪𝘵𝘴, for short) that they contain, and remain dangerously ambiguous to this day when calculating how much memory they need. So it's better to choose words and abbreviations that more clearly denote the size they take up in memory or in network packets." If you want to keep it simple, say, "String quartet? 4 people. Quintet? 5 people. Octet? You know exactly how big the band is stright from the name, right? Same idea when you talk about an 𝘰𝘤𝘵𝘦𝘵 in computer memory. 8 𝘣𝘪𝘵𝘴 make an 𝘰𝘤𝘵𝘦𝘵. Done." Find heaps of human-friendly, non-AI-generated, plain-English advice from Amos and the team on the ☀️SolCyber blog: https://solcyber.com/blog #AmosAlmanac
SolCyber

MSSP Blog | SolCyber the Modern Managed Security Program

SolCyber provides the latest information on how to tackle cyberthreats and immediately boost your security posture.

0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: Microsoft Excel once had a flight simulator hidden in it! (Until understandable security concerns said, "Probably better not to do that.")

For awesome, community-centred cybersecurity content all year round, join me, Amos, and the team on the ☀️SolCyber blog:
https://solcyber.com/blog
#AmosArmadillo

SolCyber

MSSP Blog | SolCyber the Modern Managed Security Program

SolCyber provides the latest information on how to tackle cyberthreats and immediately boost your security posture.

0
0
1
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
TALES FROM THE SOC: Exploits versus Entropy - are the shiniest new threats worse than the disruptive disorder of history? David Emerson (@d@merveilles.town) is in great form, as always - thoughtfully outspoken but infectiously good humored at the same time. Find this awesome ☀️SolCyber podcast in your favorite podcast feed, or listen/read here: https://solcyber.com/tales-from-the-soc-exploits-versus-entropy-s1-ep025/
solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 1w ago
𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: The biter bit! Set a trap to trap the trappers... Lots more helpful advice on the ☀️ @SolCyber blog: https://solcyber.com/blog
SolCyber

MSSP Blog | SolCyber the Modern Managed Security Program

SolCyber provides the latest information on how to tackle cyberthreats and immediately boost your security posture.

0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

The 'TeamPCP' cybergang is all over the media - here's why, and what to do.

I take a look at TeamPCP’s latest string of attacks, how to spot if you’ve been a victim, and how to protect against this sort of software supply-chain criminality in the future. (All written in jargonbusting plain English :-)

By me on the ☀️SolCyber blog:
https://solcyber.com/return-of-the-worm-teampcp-versus-the-supply-chain/

Return of the Worm! TeamPCP versus the supply chain - SolCyber
SolCyber

Return of the Worm! TeamPCP versus the supply chain - SolCyber

The 'TeamPCP' cybergang is all over the media - here's why, and what to do

0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 5mo ago

A ‘Janus’ attack! Funky bug-o’-the day is CVE-2026-5704 in the venerable GNU ‘tar’ utility.

Tar is short for “tape archive,” and it’s one of the oldest and most widely-used package download formats around. (When you see files called *.tgz, or *.tbz, or *.txz, those are just tar archives that have subsequently been compressed.)

Each entry in the archive has a name, a list of access permissions and other attributes, a size, and (size) bytes’ worth of data. Some filenames, such as Unix or Windows symbolic links, refer to other files and don’t have any data of their own, so they are supposed to be stored with a size of zero, and zero bytes of data.

Except that GNU tar doesn’t check that archive items that shouldn’t have any data don’t have any data.

And it handles “no-data” objects differently depending on whether you *list* the archive (to see if it has any unwanted stuff in it) or you *extract* it.

When you list the contents, the program just skips over any data attached to any “no-data” files, without warning you about the presence of data that shouldn’t really be there.

But when you extract the archive, the program *doesn’t* skip over the unwanted data - it starts looking for the next archive item right away. So, if the “injected data that shouldn’t be there” has the same format as a regular entry in the archive… the program extracts it!

Those “injected data” files will therefore be hidden from view when you list the archive, yet will automatically be extracted when you unpack the very same archive :-)

If you’re a programmer, make sure you don’t let multiple, inconsistently coded error-checking routines creep into different parts of your project. (Be extra careful if you let some kind of vibe coding tool loose on different parts of a problem at different times!)

PS. The name ‘Janus attack’ comes from the Ancient Roman deity Janus, who was literally two-faced, one on each side of his head.

0
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 3mo ago

Apple updates arrive, including for phone users (iOS 26.5.2). Apparently no 0-days…

0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 6mo ago

𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: Like many of us, Amos is following NASA's Artemis II mission...

For awesome, community-centered cybersecurity content all year round, join us on the ☀️SolCyber blog:
https://solcyber.com/blog
#AmosArmadillo

SolCyber

MSSP Blog | SolCyber the Modern Managed Security Program

SolCyber provides the latest information on how to tackle cyberthreats and immediately boost your security posture.

0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 1w ago
iOS 27.0.1 is out already - there are no security fixes listed (just the words "this update has no published CVE entries"), but there's an interesting bug patched for iPhone 18 Pro and Pro Max models that "may unexpectedly restart when Face ID fails to authenticate." That's a "fail closed" situation, which beats "fail open" in a case like this, but that could, admittedly with a bit of a stretch and a wry look, be considered a potential DoS (denial of service) vulnerability... ...because one of those people whom you consider a friend-with-a-very-annoying-sense-of-humour could, I suppose, pick up your locked phone and force it to reboot simply by glaring or gurning at it, and thereby quite deliberately forcing it down the code path of a failed Face ID. They could offer the excuse, if confronted, that they had no intention of actually unlocking it, but were "just looking at your cool new phone" to see if they, too, were ready to splash out top money on one for themselves. (It's an interesting question whether deliberately triggering an unlock attempt that shouldn't work could be successfully prosecuted under unauthorised access laws. But even if it couldn't, my opinion is that doing so, even if you can guarantee the unlock will fail, violates the spirit of the law. It also messes with the unwritten social contract not to mess with other people's digital stuff, no matter how harmless or witty you think it might be. If in doubt, leave it out, eh?)
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
The EU has fined search juggernaut Google €890,000,000 (about $1 billion) for anti-competitive behaviour. The penalty covered two offences, dubbed "self-preferencing" (€460 million) and "anti-steering" (€430 million), whose names describe Google's unlawful activities. 𝘚𝘦𝘭𝘧-𝘱𝘳𝘦𝘧𝘦𝘳𝘦𝘯𝘤𝘪𝘯𝘨 refers to Google's practice of giving its own products and services better or more prominent billing than everyone else's. Self-preferencing falls under what Americans generally refer to as "anti-trust laws," regulations applied in free-market economies aimed at preventing rich, powerful and manipulative businesses from suppressing competition and undermining choice in the market. (The word "anti-trust" in this context comes from the 19th century, when the US legislature acted to regulate the creation of so-called corporate trusts, by means of which large companies could quietly band together into cartels powerful enough to manipulate the market, crush competitors, and thereby control prices. Outside North America, the term "anti-competitive" is now usually used instead.) 𝘈𝘯𝘵𝘪-𝘴𝘵𝘦𝘦𝘳𝘪𝘯𝘨 refers to Google Play rules that forced Play Store apps to pay fees for presenting ads and offers within the app. The EU noted that, "While Google can receive a fee for facilitating the initial acquisition of a new customer by an app developer via Google Play, the level of the steering-related fees charged by Google and the length of the charging period for these fees went beyond what is considered compliant with the Digital Markets Act." Teresa Ribera, head of the EU's delightfully named Commission for Clean, Just and Competitive Transition, summed up the reasons for the fine very simply by saying, "The best products should succeed because they’re better, not because they’re owned by the company running the search engine." Google, of course, thinks that the whole thing is a stitch-up, and its President of Global Affairs (he's a lawyer, and that really is his job title) has apparently insisted that the anti-steering judgement will "dismantle safety protections on Google Play." That's a bold claim from a company that dismissed vendors of Android security software outright, calling them "charlatans and scammers" back in 2011 (anti-malware protection, suggested Google's director of open source software at the time, was pointless given the security baked into Google itself), and whose head of security insisted, back in 2014, that the majority of Android users "do not need to install anti-virus and other security apps to protect them." Today, it seems, Android users and app creators alike not only need the security provided by Google's own Google Protect tools, but require those tools on terms and with settings decided by Google itself.
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
Firefox 152.0.6 is “just” a point release, not a major update, but it does fix two zero-days. Flagged as “critical,” CVE-2036-15718 and -15719 are listed as “exploit code for these are public,” but with no active attacks yet reported. The first sounds like an RCE (remote code execution) vuln, because it’s a memory pointer mismanagement bug in WebAssembly; the second sounds like a security bypass that might lead to trouble such as authentication token theft, because it’s a DOM (domain object model) bug. The DOM is what’s supposed to keep one site’s data safe from snooping by other sites you load at the same time. Help > About Firefox to check if you’re patched.
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
Replying to
Apple: https://podcasts.apple.com/us/podcast/ai-enterprise-best-practices-s1-ep026/id1755463306?i=1000778561277 Curated transcript: https://solcyber.com/tales-from-the-soc-ai-enterprise-best-practices-s1-ep026/ Open Spotify: https://open.spotify.com/episode/6MsZjJCobjBdlJykVdeE7c?si=m7ou14RnQ1mGNVvmTcmL7A Podbean: https://tales-from-the-soc.podbean.com/e/ai-enterprise-best-practices-s1-ep026/ Audible: https://www.audible.co.uk/pd/B0HBR8CX8J
podcasts.apple.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago

Patch Tuesday Mystery! A BitLocker bypass dubbed CVE-2026-50661 was patched in the July 2026 Windows update…

So far, media coverage is just repeating Microsoft’s basic report, which admits this was a zero-day (known and disclosed already) but not exactly which already-disclosed bug it relates to.

CrowdStrike, amongst others, has reasonably wondered whether, although “not confirmed at this time, this CVE may be the patch for [Nightmare Eclipse’s] GreatXML.”

I wrote up this exploit in detail (including how well it worked for him in real-world testing) when it was first disclosed last month.

https://solcyber.com/bitlocker-defender-zero-days-and-bragging-rights-more-ms-nightmares/

solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 4w ago
Apparently the new Patch Tuesday fixes two 0-days. Also, watch out for new Nightmare Eclipse Wednesday Exploits🙀 https://solcyber.com/tales-from-the-soc-nightmare-eclipse-where-next-for-bug-disclosures-s1-ep027/
solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2w ago
Understand ClickFix attacks, and help your colleagues, friends, and family (and your boss!) to avoid them… I trace the evolution of cybercriminal treachery in malware delivery, from old-school email attachments, through high-pressure “support” calls, to today’s approach of promising you a “fix” you can implement yourself in moments with the same sort of basic clicks and keystrokes you use in everyday life. Learn what to do to stay safe, and why “ClickFix” tricks work. On the ☀️SolCyber blog: https://solcyber.com/clickfix-when-criminals-trick-you-into-infecting-yourself/
ClickFix: When criminals trick you into infecting yourself - SolCyber
SolCyber

ClickFix: When criminals trick you into infecting yourself - SolCyber

The evolution of cybercriminal treachery in malware delivery.

0
1
1
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
𝕋𝔸𝕃𝔼𝕊 𝔽ℝ𝕆𝕄 𝕋ℍ𝔼 𝕊𝕆ℂ: AI - ENTERPRISE BEST PRACTICES Join me and @david@infosec.exchange Emerson for an informative guide to using AI safely in your business. Search "Tales From The SOC" in your favorite podcast feed, or listen directly on the ☀️@SolCyber podcast pages.
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
Apple iOS 26.6 is out. As well as promising to get you ready for iOS 27 (heigh ho!), there are lots of security fixes. None of these seem to be zero-days, but in plain language, there are one or more vulnerabilities of all these types, in no particular order ("Sec" = security bypass, "DoS" = denial of service, "EoP" = elevation of privilege, and "RCE" = remote code execution): Sec: Mirrored iPhones could leak sensitive data. Sec: Apps could track users via cookie-like telltales in device data. Sec: Apps could access sensitive data. DoS: Apps could crash the system. RCE: Booby-trapped data files could inject rogue code. EoP: Apps could acquire kernel-level powers. Sec: Apps could delete protected files. RCE: Unsigned apps could bypass attestation (!). Sec: Apps could add contacts without permission. Sec: Apps could read contacts without permission. Sec: Authentication tokens could end up on the wrong server (!). Sec: Sensitive data could be stolen from the Lock Screen (yet again). EoP: Apps could extract secret data from the kernel. EoP: Apps could get access to the root account. Sec: Websites could track clicks made from other pages. Sec: Web pages could present someone else's site name. Act now, folks! Visit Settings > General > Software Update as soon as you can.
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
𝔸𝕞𝕠𝕤 𝕥𝕙𝕖 𝔸𝕣𝕞𝕒𝕕𝕚𝕝𝕝𝕠'𝕤 𝔸𝕝𝕞𝕒𝕟𝕒𝕔: No Such Agency? Never Say Anything? Well, the NSA campus is on OpenStreetMap, and hosts the National Cryptologic Museum, which is open to the public... …and fascinating! They've not only got working Enigma machines from WW2, but also a US version of the Bombe device used to automate Enigma cracking. For great articles and explainers, join us on the ☀️SolCyber blog: https://solcyber.com/copy-fail-hype-versus-reality-the-full-story/ #AmosArmadillo
solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 3mo ago
RE: https://tribe.net/@AbsoluteMemery/116838728227285524 The bizarre thing is that the software that harvests some the most intimate stuff about you on an an absurdly consistent basis - taking full copies of programs you run that “seem to be new,” perhaps; recording the URLs you visit; tracking the DNS requests you make; copying every command line parameter you type in (which often includes passwords and other PII); reading your emails before you do just in case; scraping process memory and following software function calls to “learn” your usual computer behaviors; perhaps even decrypting your HTTPS web sessions at the behest of some sysadmin to “save you from yourself”… …is EDR software (or just anti-virus if you want to talk colloquially, in the same way we still talk about “dialling” numbers and “filming” videos). Lots of EDR tools then pride themselves on retaining all that data in a “data lake,” perhaps for weeks, months, or even longer, because you never know when it might help to save the world. Thing about “lakes” as a metaphor is that most of them have rivers flowing out the other end that drain them back into the global water system, and those that don’t give up their content through evaporation anyway.
Open quoted post
Quoting
Absolute Memery 🎭
@AbsoluteMemery@tribe.net
Sadly, it's true… #SwitchToThirdParties #SwitchToLinux #UseIndySoftware #IndependentSoftware #FOSS #OSS #Spyware #InfoSec #Internet #InternetLingo #Espionage. #Meme #Memes #Humour #Humor
Open quoted post
tribe.net
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2w ago
Replying to
@bontchev@infosec.exchange “Open source crap”? Software for “nerds”? Guess you are so wedded to Windows that you’ve fallen into the “proprietary installers are sure to be secure” vibe… please try to back down from treating everyone who is not you or your colleagues as “idiots,” or the idea that everyone needs to be a technical expert and it’s always their fault if the software isn’t a beacon of clarity. Plenty of mainstream tools and even official Microsoft hotfixes involve tweaks or state changes that are presented as script one-liners to download or to copy-paste. Even many experts aren’t always expert enough to complete tasks without snippets or even fully-formed code that’s churned out by a machine and they are expected to trust - you yourself admit to using AI to generate Python code to sidestep your own deficiencies in the language, and if you couldn’t write the code yourself it is very unlikely you could properly review it and objectively test it. We all have shortcomings that we rely on websites, prompts, or popups to advise us how to get past. No need to be pompous about users who rely on a different set of crutches to the ones you use…
0
1
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2mo ago
"Be smart and just pay," demand the attackers. Here are some lessons you can learn for yourself and your business. By me on the ☀️SolCyber blog: https://solcyber.com/blackmailers-going-by-exfilsquad-claim-breaches-against-uk-orgs-supporting-education-and-police/
solcyber.com
0
0
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 2w ago
Replying to
@bontchev@infosec.exchange The problem is that even mainstream products and official installers rely on behaviours of this sort (“open a command prompt, type ‘curl url | bash’, and press enter,” for example). We had, and still have, the same problem with fake support calls in which victims are talked or pressurised into opening up a remote access tool to allow a criminal to control their computer remotely. People like you blame the victims for being a “idiots” who cannot be taught, but the victims have just as much right to denounce the “experts” - their own (possibly outsourced) IT team, their (possibly outsourced) security operations folks, and so on - as bad teachers because their expectations and the behaviours they demand of their users are so often indistinguishable from what the crooks do. Be clear - this is a world where one of the biggest and richest cybersecurity companies in the world can push out a telemetry-related signature update (one that benefitted the company more than its users - it was for reasearch rather than for vital threat prevention) that it didn’t test in any meaningful way at all, which triggered a buffer overflow *in a kernel driver* that could only handle 20 such signatures at the same time but didn’t refuse a 21st, which crashed millions of computers and put them into boot loops that required a BitLocker recovery key to escape from. Blaming users for their own cybersecurity troubles is sometimes appropriate - for example if greed or dishonesty got the better of them - but assuming that all dangerous behaviours are “obvious” is perhaps really where the idiocy starts…
0
3
0
0
Open post
Paul Ducklin @pducklin@infosec.exchange
· 1mo ago
Cynicism? Not in the latest TALES FROM THE SOC podcast from ☀️SolCyber 🫢‼️😬 Join me and David Emerson (@d@merveilles.town) for a provocative take on breach disclosures, patching, and cybersecurity in general. Search and listen 🔈on your favourite podcast feed, or follow along with our carefully-curated transcript 📖 on the blog: https://solcyber.com/tales-from-the-soc-nightmare-eclipse-where-next-for-bug-disclosures-s1-ep027/
solcyber.com
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 12:35:37 UTC