Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Alexandre Borges

@alexandreborges@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Vulnerability Researcher | Exploit Developer

560 Followers
39 Following
50 Posts
Joined November 07, 2022
Website:
https://exploitreversing.com/
Twitter:
@ale_sp_brazil
LinkedIn:
https://www.linkedin.com/in/alexandreborgesexploit/
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1w ago

Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 1:

https://pgj11.com/posts/Windows-NCSI-Proxy-Auth-Coercion-Part-1/

Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 2:

https://pgj11.com/posts/Windows-NCSI-Proxy-Auth-Coercion-Part-2/

#cybersecurity #exploit #exploitation #vulnerability #drivers #infosec #informationsecurity #windows

pgj11.com
3
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1w ago

BleedingTooth: Linux Bluetooth Zero-Click Remote Code Execution:

https://google.github.io/security-research/pocs/linux/bleedingtooth/writeup.html

#cybersecurity #vulnerability #infosec #exploitation #linux #bluetooth #rce

google.github.io
2
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1w ago

Exploiting Reversing (ER) Series | Article 10: iOS Security Research (part 01)

223 pages, free. The first article in the series aimed at iOS itself, and the opening of a multi-part sequence.

Published on:

https://www.blackstormsecurity.com/research/

This article will be published on https://exploitreversing.com/ next week.

Hope you enjoy the read!

#iOS #VulnerabilityResearch #ExploitDevelopment #ReverseEngineering #KernelSecurity

blackstormsecurity.com
1
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2w ago

Beyond Prompt Injection: Hacking Apple's Private Cloud Compute:

https://blog.sentry.security/beyond-prompt-injection-hacking-apples-private-cloud-compute/

#apple #vulnerability #cybersecurity #informationsecurity #cve

blog.sentry.security
2
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1w ago

VM guest escape via 9p filesystem exploit:

https://gitlab.com/qemu-project/qemu/-/work_items/4491

#qemu #exploitation #vulnerability #informationsecurity #infosec #cybersecurity

gitlab.com
1
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2w ago

A quartet of Linux local root vulns: DirtyAH6, PPPoEject, TUNderflow, and DiagSpill:

https://heyitsas.im/posts/lpe-quartet/

#cybersecurity #vulnerability #exploit #infosec #linux

heyitsas.im
2
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

A "DoS only" bug to LPE and bypass the existing patch to win $10,500 in kernelCTF:

https://nebusec.ai/research/cve-2026-43501-route-of-root/

#cybersecurity #infosec #informationsecurity #lpe #linux #kernelctf #exploitation

nebusec.ai
5
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

It is with great pleasure that I announce I am a co-author of the Seventh Edition of Gray Hat Hacking, alongside outstanding cybersecurity minds such as Stephen Sims, Valentina Palmiotti, Natalie Silvanovich, Luna Tong, Pavel Yosifovich, Moses Frost, and Huascar Tejeda!

We are undoubtedly living through exciting times, and I hope readers appreciate this complete overhaul of modern, completely updated content. Stay tuned!

#cybersecurity #hacking #exploitation #exploit #programming #informationsecurity #infosec

infosec.exchange

Infosec Exchange

3
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

Unprivileged root via a use-after-free in DRM GEM change_handle (CVE-2026-46215):

https://cyberstan.co.uk/drm-lpe-linux/

#linux #kernel #vulnerability #cybersecurity #exploitation

cyberstan.co.uk

Unprivileged root via a use-after-free in DRM GEM change_handle (CVE-2026-46215) – cyberstan

7
0
3
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

The articles already published in the Exploiting Reversing series (ERS) are now hosted on a new website:

https://blackstormsecurity.com/research/

Future articles will be published primarily at this new address, and for a time, I will also publish them on my personal blog.

The series will continue with many more articles, which some are coming soon. Stay tuned.

Have an excellent day.

#exploit #vulnerability

blackstormsecurity.com
1
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

A Windows Kernel in a Browser Tab, Part I: Cold Boot, Fast Boot, and Four Megabytes:

https://www.msuiche.com/posts/nanokrnl-cold-boot-fast-boot/

#kernel #infosec #programming #rust #windows #hacking

A Windows Kernel in a Browser Tab, Part I: Cold Boot, Fast Boot, and Four Megabytes
Matt Suiche

A Windows Kernel in a Browser Tab, Part I: Cold Boot, Fast Boot, and Four Megabytes

nanokrnl is an NT-shaped kernel in Rust that boots in a browser tab through nanox, a 65 KB x86-64 emulator we wrote from scratch.

5
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

[0-Day] Windows USB Print Out-of-Bounds Read Vulnerability - The String Descriptor That Wasn’t

https://zeifan.my/usbtersakiti/

#cybersecurity #windows #vulnerability #infosec #exploitation

zeifan.my
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2mo ago

Malwoverview version 8.1.0 is available:

https://github.com/alexandreborges/malwoverview

To install it:

$ python -m pip install -U malwoverview

This version aims to:

01. Introduce new features.
02. Fix most existing issues, particularly those found between versions 8.0.0 and 8.0.5.
03. Address a number of security issues.

The number of changes is significant, so it is recommended reading the following sections of the README.md:

01. WHAT IS NEW IN 8.1.0, BY EXAMPLE
02. WHAT IS NEW IN 8.0.0 TO 8.0.5, BY EXAMPLE
03. EXAMPLES

#malware #threathunting #vulnerability #informationsecurity #infosec #cybersecurity

github.com
2
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

Dissecting and Exploiting Linux LPE Variant: DirtyClone (CVE-2026-43503):

https://research.jfrog.com/post/dissecting-and-exploiting-linux-lpe-variant-dirtyclone-cve-2026-43503/

#cve #linux #cybersecurity #informationsecurity #exploitation #vulnerability

research.jfrog.com

DirtyClone (CVE-2026-43503): Linux Kernel LPE - JFrog Security Research

DirtyClone (CVE-2026-43503) is a CVSS 8.8 Linux kernel LPE discovered independently by JFrog Security Research and Hyunwoo Kim. Patch to Linux v7.1-rc5 or apply the full 4-CVE fix chain.

4
0
5
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2mo ago

Hunting Memory Leaks in bsnmpd with DTrace:

https://oshogbo.com/blog/92/

#dtrace #cybersecurity #informationsecurity #infosec #performance

Hunting Memory Leaks in bsnmpd with DTrace
oshogbo//vx

Hunting Memory Leaks in bsnmpd with DTrace

One of my FreeBSD boxes runs `bsnmpd`, the base system SNMP daemon. The machine is on 15.0-p2, and the daemon kept growing until the kernel ran out of patience and OOM-killed it. That is not a good feature for a daemon. I could have just added a cron job to restart it and called it a day. But a leak that kills a long-running daemon is exactly the kind of thing I like to chase, and I already had a tool for it.

3
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

Lazarus and the FudModule Rootkit: Beyond BYOVD with an Admin-to-Kernel Zero-Day:

https://www.gendigital.com/blog/insights/research/lazarus-and-the-fudmodule-rootkit-beyond-byovd-with-an-admin-to-kernel-zero-day

#cybersecurity #infosec #informationsecurity #rootkit #vulnerability

gendigital.com
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

Bring Your Own EDR: How to Turn a Commercial EDR into a Trojan Horse

https://www.akamai.com/blog/security-research/bring-your-own-edr-turn-commercial-edr-trojan-horse

#edr #programming #cybersecurity #informationsecurity

akamai.com
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

Linux Bridge STP Timer Use-After-Free:

https://ssd-disclosure.com/linux-bridge-stp-timer-use-after-free/

#linux #exploit #exploitation #vulnerability #informationsecurity #cve #patch #cybersecurity

ssd-disclosure.com
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 6mo ago

Malwoverview v8.0 (codename: Revolutions) has been released:

https://github.com/alexandreborges/malwoverview

To install its complete version: pip install malwoverview[all]

Partial List of Improvements:

NEW SERVICE INTEGRATIONS (6):

01. http://URLScan.io — submit URLs, retrieve results, search scans, search by domain/IP (-u/-U)
02. Shodan — IP lookup and search queries (-s/-S, -ip 4)
03. AbuseIPDB — IP reputation checks (-ab/-AB, -ip 5)
04. GreyNoise — IP classification (-gn/-GN, -ip 6)
05. Whois/RDAP — domain and IP lookups (-wh/-WH)
06. LLM threat enrichment — Claude, Gemini, OpenAI, Ollama (--enrich, --llm)

NEW CAPABILITIES (16):

07. Cross-service hash correlation across VT, HA, Triage, AlienVault (--correlate-hash)
08. Batch hash check — Bazaar (-b 11), Hybrid Analysis (-a 16), Triage (-x 8)
09. Directory scan — Bazaar (-b 12), Hybrid Analysis (-a 17), Triage (-x 9)
10. Comprehensive IP lookup across all services (-ip 7)
11. IOC extraction from text, PDF, email, URL (--extract-iocs)
12. YARA rule scanning (--yara, --yara-target)
13. Interactive REPL mode with 22 commands (--interactive)
14. JSON and CSV structured output (--output-format)
15. Result caching with configurable TTL (--no-cache, --cache-ttl)
16. HTTP/HTTPS/SOCKS5 proxy support (--proxy)
17. MITRE ATT&CK technique mapping (--attack-map)
18. Quiet and verbose modes (--quiet, --verbose)
19. HTML/PDF report generation (--report)
20. TUI dashboard mode (--tui)
21. Context-aware LLM prompts — separate threat analysis and CVE analysis prompts
22. LLM provider override from CLI (--llm claude|gemini|openai|ollama)

#threathunting #malware #vulnerability #ai #informationsecurity #cybersecurity #cve

github.com
9
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 5mo ago

Malwoverview 8.0.1 is available:

https://github.com/alexandreborges/malwoverview

To update it:

python -m pip install -U malwoverview

#threathunting #malware #cve #vulnerability #cybersecurity #informationsecurity #incidentresponse

github.com
4
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 4mo ago

Striga: Lifting x86 to LLVM IR with Python:

https://secret.club/2026/05/21/striga.html

#python #reversing #llvm #informationsecurity #infosec #cybersecurity

Striga: Lifting x86 to LLVM IR with Python
secret club

Striga: Lifting x86 to LLVM IR with Python

Background While discussing with eversinc33 about lifting BinaryShield to LLVM IR I decided it would be useful to write a basic lifter in Python that can lift x86_64 instructions to LLVM IR. He has since released his blog post: Writing a Naive LLVM-based Devirtualizer, which I highly recommend you check out! This post assumes familiarity with the basics of LLVM IR. You can find some references at the end of this post. Over the years I noticed that a lot of people get stuck exploring lifters, bec

2
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2mo ago
The work continues... a third vulnerability in just a few days, and like the other two, this one also affects iOS 26.5 and iOS 26.5.2. The challenge, as usual, centers on the next steps for exploitation. #ios #vulnerability #apple
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

Redis 8.6: Remote Code Execution via Stream PEL Use After Free:

https://zerotistic.blog/posts/redis-stream-pel-uaf/

#linux #vulnerability #exploitation #informationsecurity #infosec #cybersecurity

Redis 8.6: Remote Code Execution via Stream PEL Use After Free
zerotistic

Redis 8.6: Remote Code Execution via Stream PEL Use After Free

A Redis 8.6 stream PEL ownership bug, a malformed RESTORE payload, and a jemalloc size class collision that turns a shared NACK into code execution.

1
1
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

BitLocker downgrade attacks:

https://archives.pass-the-salt.org/Pass%20the%20SALT/2026/slides/PTS2026-TALK-13-bitlocker_talk_deck.pdf

#windows #bitlocker #infosec #informationsecurity #cybersecurity #crypto

archives.pass-the-salt.org
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 7mo ago

I am excited to release the extended version of the sixth article in the Exploiting Reversing Series (ERS). Titled "A Deep Dive Into Exploiting a Minifilter Driver (N-day)" this 293-page deep dive offers a comprehensive roadmap for vulnerability exploitation:

https://exploitreversing.com/2026/02/11/exploiting-reversing-er-series-article-06/

Key updates in this extended edition:

[+] Dual Exploit Strategies: Two distinct exploit versions.
[+] Exploit ALPC Write Primitive Edition: elevation of privilege of a regular user to SYSTEM.
[+] Exploit Parent Process ID Spoofing Edition: elevation of privilege of an administrator to SYSTEM.
[+] Solid Reliability: A completely stable and working ALPC write primitive.
[+] Optimized Exploit Logic: Significant refinements to the codebase and technical execution for better stability and predictability.

For those who have read the original release, whose exploit was working, my strong recommendation is that you adopt this extended edition as definitive.

The article guides you through the entire lifecycle of an exploit: from initial reverse engineering and vulnerability analysis to multiple PoC developments and full exploitation.

I hope this serves as a definitive resource for your research. If you find it helpful, please feel free to share it or reach out with your feedback!

Enjoy your reading and have a great day.

#exploit #cve #nday #cybersecurity #informationsecurity #infosec #vulnerability

Exploiting Reversing (ER) series: article 06 | A Deep Dive Into Exploiting a Minifilter Driver (N-day)
Exploit Reversing

Exploiting Reversing (ER) series: article 06 | A Deep Dive Into Exploiting a Minifilter Driver (N-day)

I am excited to release the extended version of the sixth article in the Exploiting Reversing Series (ERS). Titled “A Deep Dive Into Exploiting a Minifilter Driver (N-day)” this 296-pag…

4
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

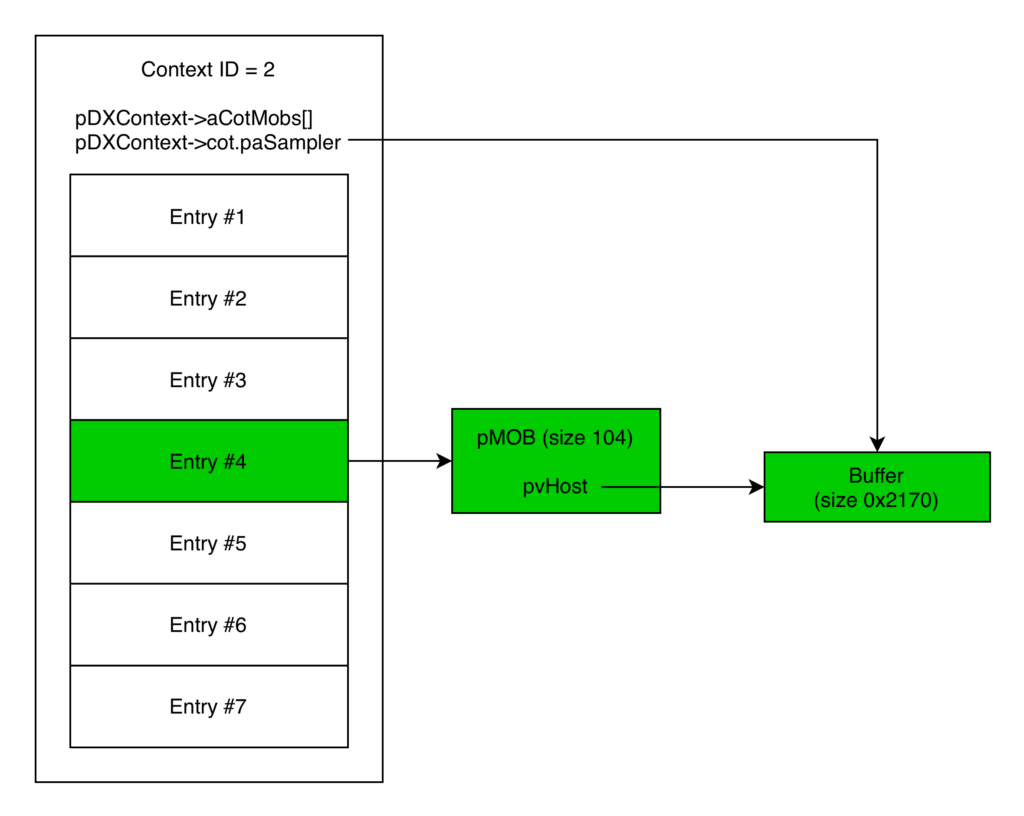
Zombie COTables: Resurrecting Freed Memory to Escape VirtualBox:

https://blog.exodusintel.com/2026/06/15/zombie-cotables-resurrecting-freed-memory-to-escape-virtualbox/

#vulnerability #exploitation #exploit #virtualbox #cybersecurity #infosec #informationsecurity

Zombie COTables: Resurrecting Freed Memory to Escape VirtualBox - Exodus Intelligence
Exodus Intelligence

Zombie COTables: Resurrecting Freed Memory to Escape VirtualBox - Exodus Intelligence

By Luca Ginex Overview This blog post discusses a use-after-free vulnerability that we found in VirtualBox in 2025. This vulnerability was patched on Oracle Critical Patch Update – January 2026. The vulnerability was also presented, along with others, at OffensiveCon 2026. This post describes the exploitation process for the vulnerability on a Linux system. First, a ... Read more Zombie COTables: Resurrecting Freed Memory to Escape VirtualBox

1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 4mo ago

Malwoverview 8.0.2 has been released:

https://github.com/alexandreborges/malwoverview

To install it:

python -m pip install -U malwoverview[all]

#malware #threathunting #informationsecurity #infosec #vulnerability #cve #dfir

github.com
1
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 4mo ago

Bypassing SSL Pinning on Play Store AVDs without Frida

https://www.mfumis.com/posts/bypassing-ssl-pinning-on-play-store-avds-without-frida/

#cybersecurity #informationsecurity #frida #mobiledevice #infosec #mobilesecurity #mobile

mfumis.com
1
0
3
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 4mo ago

Authenticated RCE via Argument Injection in Gogs (NOT FIXED):

https://www.rapid7.com/blog/post/ve-authenticated-rce-via-argument-injection-gogs-unfixed/

#cybersecurity #vulnerability #rce #informationsecurity #exploitation

rapid7.com
1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 7mo ago

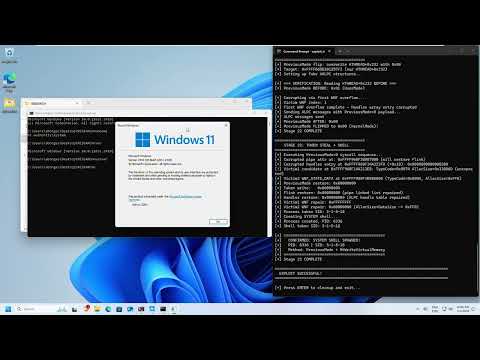
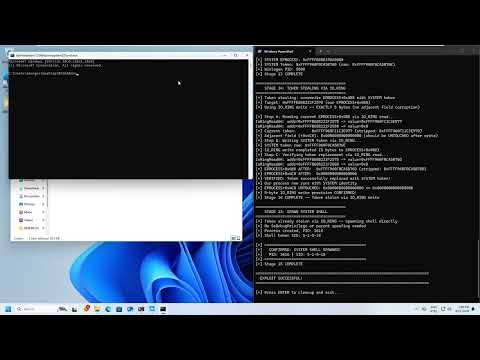
Exploiting Reversing (ER) series: article 07 | Exploitation Techniques | CVE-2024-30085 (part 01)

I am excited to release the seventh article in the Exploiting Reversing Series (ERS). Titled “Exploitation Techniques | CVE-2024-30085 (part 01)” this 119-page technical guide offers a comprehensive roadmap for vulnerability exploitation:

https://exploitreversing.com/2026/03/04/exploiting-reversing-er-series-article-07/

Key features of this edition:

[+] Dual Exploit Strategies: Two distinct exploit versions using Token Stealing and I/O Ring techniques.
[+] Exploit ALPC + PreviousMode Flip + Token Stealing: elevation of privilege of a regular user to SYSTEM.
[+] Exploit ALPC + Pipes + I/O Ring: elevation of privilege of a regular user to SYSTEM.
[+] Solid Reliability: Two complete working and stable exploits, including an improved cleanup stage.
[+] Optimized Exploit Logic: Significant refinements to the codebase and technical execution for better stability and predictability.

The article guides you through the two distinct techniques for exploiting the CVE-2024-30085 Heap Buffer Overflow vulnerability.

I hope this serves as a definitive resource for your research. If you find it helpful, please feel free to share it or reach out with your feedback!

Enjoy your reading and have an excellent day.

#exploit #vulnerability #cve #exploitation #infosec #informationsecurity #windows

Exploiting Reversing (ER) series: article 07 | Exploitation Techniques: CVE-2024-30085 (part 01)
Exploit Reversing

Exploiting Reversing (ER) series: article 07 | Exploitation Techniques: CVE-2024-30085 (part 01)

I am excited to release the seventh article in the Exploiting Reversing Series (ERS). Titled “Exploitation Techniques | CVE-2024-30085 (part 01)” this 119-page technical guide offers a comprehensiv…

2
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 7mo ago

I am pleased to announce the publication of the sixth article in the Exploiting Reversing Series (ERS). Titled "A Deep Dive Into Exploiting a Minifilter Driver (N-day)", this 251-page article provides a comprehensive look at a past vulnerability in a mini-filter driver:

https://exploitreversing.com/2026/02/11/exploiting-reversing-er-series-article-06/

It guides readers through the entire investigation process—beginning with binary diffing and moving through reverse engineering, deep analysis and proof-of-concept stages into full exploit development.

I would like to thank Ilfak Guilfanov (@ilfak on X) and Hex-Rays SA (@HexRaysSA@infosec.exchange on X) for their constant and uninterrupted support, which has helped me write these articles over time. 

I hope this serves as a valuable resource for your research. If you enjoy the content, please feel free to share it or reach out with feedback.

Have an excellent day!

#exploit #exploitation #vulnerability #nday #reverseengineering #windows

Exploiting Reversing (ER) series: article 06 | A Deep Dive Into Exploiting a Minifilter Driver (N-day)
Exploit Reversing

Exploiting Reversing (ER) series: article 06 | A Deep Dive Into Exploiting a Minifilter Driver (N-day)

I am excited to release the extended version of the sixth article in the Exploiting Reversing Series (ERS). Titled “A Deep Dive Into Exploiting a Minifilter Driver (N-day)” this 296-pag…

2
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 8mo ago

This presentation remains the go-to reference for learning the inner workings of the IDA Pro Hex-Rays decompiler:

(video) https://www.youtube.com/watch?v=T-YkhNElvng

(article) https://i.blackhat.com/us-18/Thu-August-9/us-18-Guilfanov-Decompiler-Internals-Microcode-wp.pdf

#decompiler #reverseengineer #informationsecurity #cybersecurity

Decompiler Internals: Microcode

2
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 8mo ago

[Cryptodev-linux] Page-level UAF exploitation:

https://nasm.re/posts/cryptodev-linux-vuln

#linux #cybersecurity #informationsecurity #uaf #exploitation #vulnerability

nasm.re
2
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 6mo ago

Before dropping my next article (ERS_08), I’ve updated the ERS 06 article (rev C.1):

https://exploitreversing.com/2026/02/11/exploiting-reversing-er-series-article-06/

This revision features a refined ALPC exploit with a new stage and an extended cleaner stage, ensuring a stable exit and preventing system crashes.

I’ve also fixed several minor issues and uploaded a new video demonstrating the practical execution.

Enjoy the read and have an excellent day!

#vulnerability #exploitation #cybersecurity #windows #exploit

Exploiting Reversing (ER) series: article 06 | A Deep Dive Into Exploiting a Minifilter Driver (N-day)
Exploit Reversing

Exploiting Reversing (ER) series: article 06 | A Deep Dive Into Exploiting a Minifilter Driver (N-day)

I am excited to release the extended version of the sixth article in the Exploiting Reversing Series (ERS). Titled “A Deep Dive Into Exploiting a Minifilter Driver (N-day)” this 296-pag…

1
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 8mo ago

TP-Link ER605 DDNS Pre-Auth RCE: Chaining CVE-2024-5242, CVE-2024-5243, CVE-2024-5244:

https://oobs.io/posts/er605-1day-exploit/

#exploit #vulnerability #rce #informationsecurity #cybersecurity #infosec

oobs.io
1
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago
(remember) Introducing usbliter8: https://ps.tc/pages/blog-usbliter8.html #cybersecurity #ios #exploitation #exploit #bootrom #iphone #informationsecurity #infosec
ps.tc

Paradigm Shift - Unavailable

This page is taking an unexpected detour...

0
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1w ago

Branch Target Reuse, BTR: New Spectre V2 Attack Targeting JIT Compilers:

https://www.vusec.net/projects/btr/

#cybersecurity #infosec #exploitation #vulnerability #jit #cpu

vusec.net
0
0
1
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2mo ago
SoK: 20 Years of Power, Privilege, and Peril in x86 System Management Mode https://vanbulck.net/files/woot26-smm.pdf #cybersecurity #smm #platformsecurity #informationsecurity #infosec
vanbulck.net
0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 6mo ago

The eighth article of the Exploiting Reversing Series (ERS) is now live. Titled “Exploitation Techniques | CVE-2024-30085 (Part 02)” this 91-page technical guide offers a comprehensive roadmap for vulnerability exploitation:

https://exploitreversing.com/2026/03/31/exploiting-reversing-er-series-article-08/

Key features of this edition:

[+] Dual Exploit Strategies: Two distinct exploit versions leveraging the I/O Ring mechanism.
[+] Exploit ALPC + WNF OOB + Pipe Attributes + I/O Ring: elevation of privilege of a regular user to SYSTEM.
[+] Replaced ALPC one-shot write with Pipe Attribute spray for I/O Ring RegBuffers corruption: more reliable adjacency control.
[+] Exploit WNF OOB + I/O Ring Read/Write: elevation of privilege of a regular user to SYSTEM.
[+] Pure I/O Ring primitive: eliminated ALPC dependency entirely. WNF overflow directly corrupts I/O Ring RegBuffers for arbitrary kernel read/write.
[+] Solid Reliability: Two complete, stable exploits, including an improved cleanup stage.

This article guides you through two additional techniques for exploiting the CVE-2024-30085 Heap Buffer Overflow. While demonstrated here, these methods can be adapted as exploitation techniques for many other kernel targets.

I hope this serves as a definitive resource for your research. If you find it helpful, please feel free to share it or reach out with your feedback!

Enjoy the read and have an excellent day.

#exploit #exploitdevelopment #windows #exploitation #vulnerability #minifilterdriver #kernel #heapoverflow #ioring

Exploiting Reversing (ER) series: article 08 | Exploitation Techniques: CVE-2024-30085 (part 02)
Exploit Reversing

Exploiting Reversing (ER) series: article 08 | Exploitation Techniques: CVE-2024-30085 (part 02)

Today I am releasing the eighth article in the Exploiting Reversing Series (ERS). In “Exploitation Techniques | CVE-2024-30085 (Part 02)” I provide a 91-page deep dive and a comprehensive roadmap f…

0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 5mo ago

The Exploiting Reversing Series (ERS) currently features 945 pages of exploit development based on real-world targets:

[+] ERS 08: https://exploitreversing.com/2026/03/31/exploiting-reversing-er-series-article-08/
[+] ERS 07: https://exploitreversing.com/2026/03/04/exploiting-reversing-er-series-article-07/
[+] ERS 06: https://exploitreversing.com/2026/02/11/exploiting-reversing-er-series-article-06/
[+] ERS 05: https://exploitreversing.com/2025/03/12/exploiting-reversing-er-series-article-05/
[+] ERS 04: https://exploitreversing.com/2025/02/04/exploiting-reversing-er-series-article-04/
[+] ERS 03: https://exploitreversing.com/2025/01/22/exploiting-reversing-er-series-article-03/
[+] ERS 02: https://exploitreversing.com/2024/01/03/exploiting-reversing-er-series-article-02/
[+] ERS 01: https://exploitreversing.com/2023/04/11/exploiting-reversing-er-series/

In the coming weeks, I will publish new articles covering exploration in areas such as Windows, Chrome, iOS/macOS, and hypervisors.

I sincerely hope these articles help other professionals define their own steps in this area.

Have a great day and enjoy reading.

#exploit #exploitation #windows #chrome #macOS #iOS #hypervisors #vulnerabilityresearch

Exploiting Reversing (ER) series: article 08 | Exploitation Techniques: CVE-2024-30085 (part 02)
Exploit Reversing

Exploiting Reversing (ER) series: article 08 | Exploitation Techniques: CVE-2024-30085 (part 02)

Today I am releasing the eighth article in the Exploiting Reversing Series (ERS). In “Exploitation Techniques | CVE-2024-30085 (Part 02)” I provide a 91-page deep dive and a comprehensive roadmap f…

0
0
2
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 1mo ago

CET-Compliant Callstack Spoofing via Thread Pool Enum Callback Trampolining:

https://mrtiz.github.io/cet-callstack-spoofing-thread-pool-trampoline

#cybersecurity #programming #infosec #hacking #redteam

mrtiz.github.io
0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago
Malwoverview 8.0.5 (Revolutions): https://github.com/alexandreborges/malwoverview #cybersecurity #malware #threathunting #informationsecurity #dfir
github.com
0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2w ago

Qualcomm’s Adreno X2 GPU:

https://chipsandcheese.com/p/qualcomms-adreno-x2-gpu

#gpu #infosec #qualcomm #engineering

chipsandcheese.com
0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2mo ago
Frag Gap: https://blog.qwerty.or.kr/en/posts/cdf3008a-c1a4-4eca-a373-aa3a2bcf1489/ #kernel #network #cybersecurity #informationsecurity #exploitation #vulnerability #cve
blog.qwerty.or.kr
0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

Another vulnerability in iOS 26.5 with a clear and reproducible crash, registers control, primitive and PoC confirmed, and possibly a working exploit... who knows... ;)

0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

Spiteful Fruit - AppleRAID Kernel Heap OOB Write:

https://ret2p.lt/2026/06/30/softraid-spite.html

#cybersecurity #informationsecurity #iOS #apple #vulnerability #informationsecurity #infosec #exploitation

Spiteful Fruit - AppleRAID Kernel Heap OOB Write
ret2p.lt

Spiteful Fruit - AppleRAID Kernel Heap OOB Write

This report is not eligible for credit. The issue had already been addressed in a public beta that was available prior to your submission.

0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 2w ago

Malwoverview 8.2.0 (codename: Revolutions)

This version adds a component vulnerability search, gives every NIST query a chosen ordering reference, and repairs the queries themselves.

https://github.com/alexandreborges/malwoverview

To install it:

python -m pip install -U malwoverview[all]

[+] New — --nist 6, list the CVEs of a component

Give it a component name, or the path to a local binary:

malwoverview --nist 6 --NIST openssl malwoverview --nist 6 --NIST "C:\Windows\System32\drivers\afd.sys"

The same works by name on any platform: ksmbd and nf_tables on Linux, iCloud and WebKit on macOS and iOS.

[+] New — --sort-by

Chooses what "most recent" means: the year in the CVE ID (default) or the NVD publication date. NVD often publishes a record years after the ID was assigned, so the two disagree on about 30% of rows. --time now bounds results by the same reference.

Note: check the ## WHAT IS NEW IN 8.2.0, BY EXAMPLE section from README.md to learn how to use the new options.

#malware #cybersecurity #infosec #informationsecurity #vulnerability #cve #threathunting #threatintelligence

github.com
0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 3mo ago

TrigonLegacy - Deterministic iOS 7-9 tfp0:

https://therealclarity.github.io/blog/trigon-legacy/

#ios #apple #exploitation #informationsecurity #cybersecurity #vulnerability #reverseengineering

TrigonLegacy - Deterministic iOS 7-9 tfp0 | Clarity

TrigonLegacy - Deterministic iOS 7-9 tfp0 | Clarity

TrigonLegacy exploits an integer overflow in the VM layer when creating memory entries. This allows arbitrary physical memory read/write, which is then used to build a tfp0 primitive. This exploit ...

0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 5mo ago

CFPsec is program to list Call For Papers or upcoming Hacking/Security Conferences based on cfptime.org website.

https://github.com/alexandreborges/cfpsec

To install it:

python -m pip install -U cfpsec

#cybersecurity #informationsecurity #conferences

GitHub

GitHub - alexandreborges/cfpsec: CFPsec is a client program that retrieves the list of Call For Papers or/and upcoming Hacking/Security Conferences based on cfptime.org website.

CFPsec is a client program that retrieves the list of Call For Papers or/and upcoming Hacking/Security Conferences based on cfptime.org website. - alexandreborges/cfpsec

0
0
0
0
Open post
Alexandre Borges @alexandreborges@infosec.exchange
· 4mo ago

GHSL-2026-140: Heap Buffer Write Overflow in 7-Zip (CVE-2026-48095):

https://securitylab.github.com/advisories/GHSL-2026-140_7-Zip/

#vulnerability #cybersecurity #informationsecurity #exploitation #cve

GHSL-2026-140: Heap Buffer Write Overflow in 7-Zip
GitHub Security Lab

GHSL-2026-140: Heap Buffer Write Overflow in 7-Zip

A heap buffer overflow vulnerability (GHSL-2026-140) exists in 7-Zip version 26.00, caused by an under-allocation in the NTFS compressed stream buffer (GetCuSize shift UB), potentially allowing attackers to exploit this issue for arbitrary code execution.

0
0
1
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 19:56:42 UTC