#microsoft365

29 posts · Last used 2h

🌩️ Dutch tax office ditches Microsoft 365 cloud for on-premises alternative 「 The Netherlands Tax and Customs Administration has abandoned its planned Microsoft 365 cloud migration in favor of services hosted on infrastructure it controls, alongside European open source alternatives. Email and calendars will move on-premises in 2027, followed by storage and collaboration services later that year and in 2028 」 https://www.theregister.com/on-prem/2026/10/07/dutch-tax-office-ditches-microsoft-365-cloud-for-on-premises-alternative/5301603 #netherlands #opensource #microsoft365
1
0
1
0
Just putting this out there... a few days ago I needed to do the "monthly" clean up (after three months) so while I was making a backup of our centrally-stored data on the old Linux desktop, I let #Ucheck do its thing on our two Windows laptops, then finished off with a quick Microsoft Store update, CCleaner registry clean and ShutUpWin safety check. Imagine my utter shock, therefore, when I went to edit an ODS spreadsheet yesterday and was confronted with EXCEL instead of #LibreOffice !!! Unless Ucheck did it deliberately (seems unlikely) something in Windows Update or WinGet actually *uninstalled #LibreOffice * then *installed #Microsoft365 / #MicrosoftOffice instead*! It happened on both Windows laptops. That is flabbergastingly low even for #Microsoft... I checked around and there were a couple of other people who complained about the exact same thing over the years...
0
2
0
0
CloudSEK reports BigBear 2.0, an Evilginx2-based PhaaS, compromised Microsoft 365 accounts at 258 organizations and stole 5,000+ records. It proxies logins to capture passwords, MFA data and session cookies for replay, bypassing standard MFA. Enforce phishing-resistant auth and token theft detection. #Microsoft365 #Phishing #MfaBypass https://cyberworldops.eu/en/bigbear-20-phishing-service-hijacked-microsoft-365-sessions-at-258
0
0
0
0
🟢 Was ist Microsoft Forms? Mit Forms erstellst Du Online-Formulare für Umfragen und Quiz. Die App wertet die abgegebenen Antworten für Dich aus. Mit einem Benutzerkonto für #Microsoft365 kannst Du Forms sofort nutzen: https://www.malter365.de/forms/was-ist-forms/ #MicrosoftForms #Malter365
0
1
0
0

🎯 Threat Intelligence

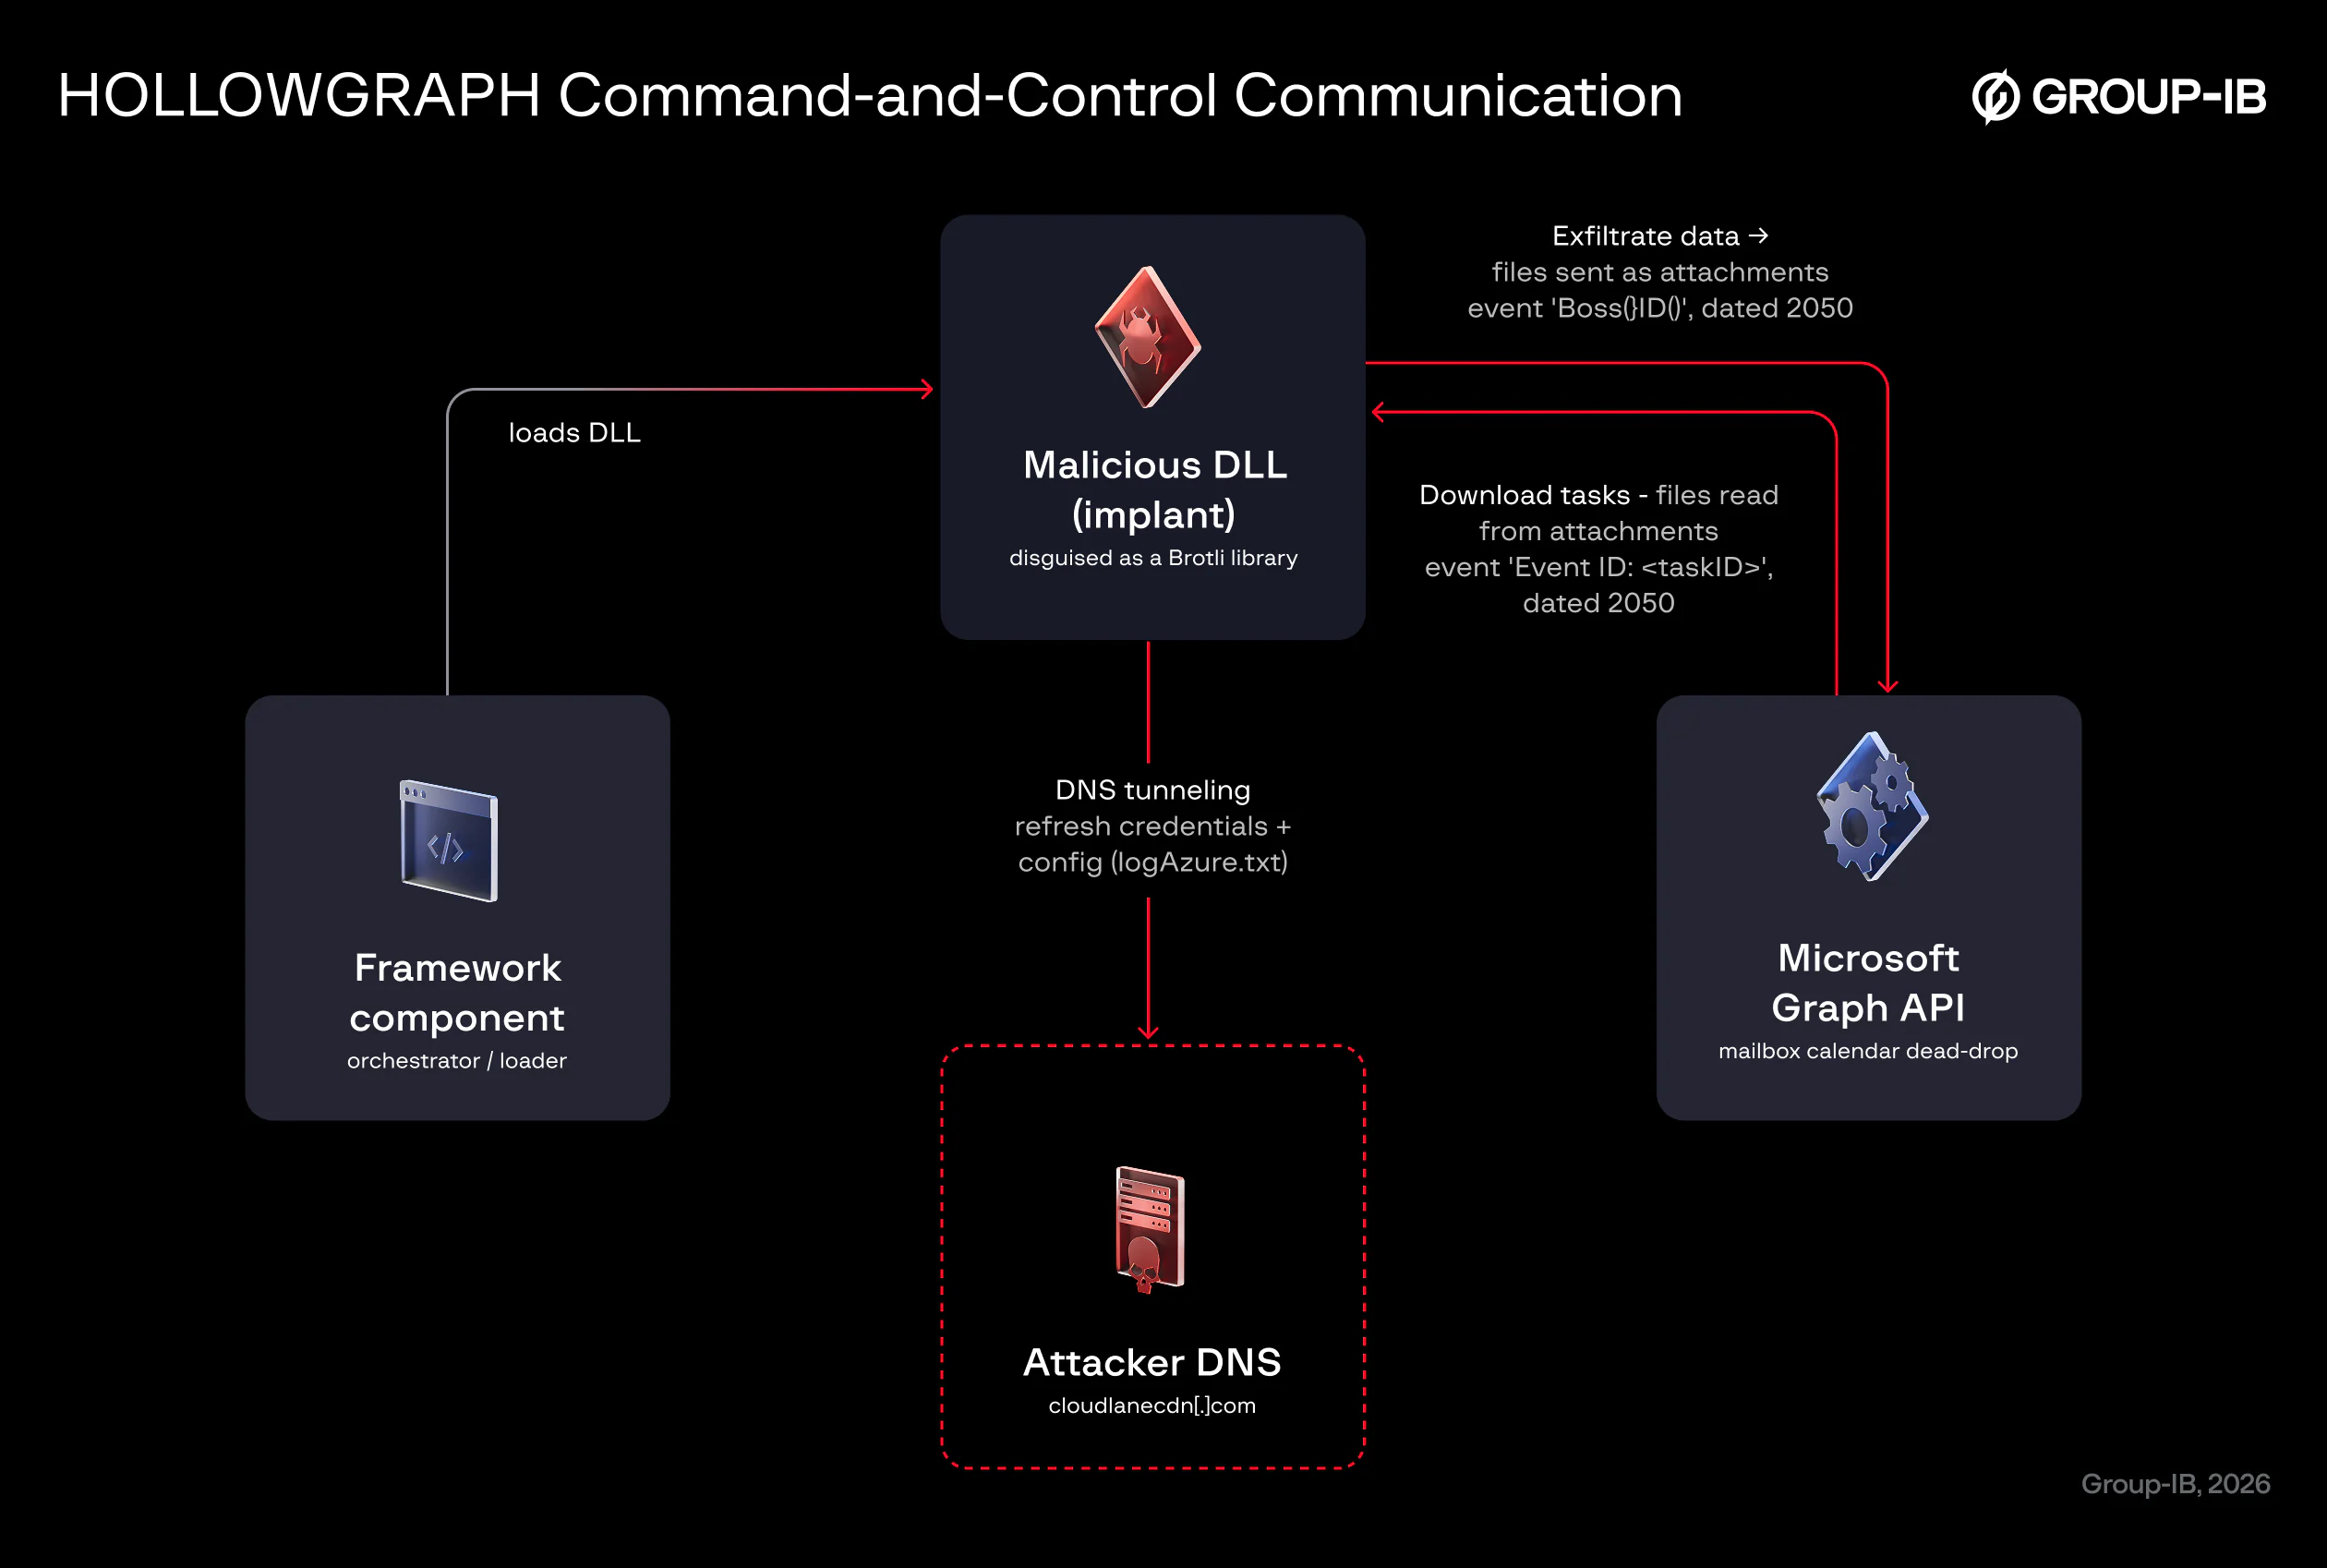
Group-IB Threat Intelligence has identified HOLLOWGRAPH, a .NET NativeAOT-compiled DLL malware attributed with high confidence to the Cavern backdoor framework. The malware transforms Microsoft 365 calendars into covert command-and-control channels using the Microsoft Graph API, communicating through a compromised Israeli mailbox.

🔹 Technical Overview

HOLLOWGRAPH operates with only two commands: get and send. Both execute exclusively through trusted Microsoft cloud infrastructure. The malware never reaches out directly to attacker-owned servers. Instead, it uses the Microsoft Graph API to treat a compromised mailbox's calendar as a two-way dead-drop.

🔹 C2 Mechanism

The calendar-based C2 works as follows:

  1. Tasking: Operators plant calendar events containing encrypted commands as attachments.
  2. Exfiltration: The implant creates its own calendar events with encrypted stolen data attached as files.
  3. Concealment: Every event is dated to 13 May 2050, ensuring the mailbox owner is unlikely to notice them.

All Graph payloads use hybrid RSA + AES encryption. Two separate key pairs keep tasking and exfiltration channels cryptographically independent.

🔹 Credential Renewal Channel

HOLLOWGRAPH maintains a secondary communication channel through DNS tunneling. It performs IPv6 AAAA record queries against the attacker-controlled domain cloudlanecdn[.]com to refresh its Microsoft Entra ID (Azure AD) credentials. Updated values are written to an on-disk configuration file named logAzure.txt.

This dual-channel architecture provides resilience. Even if the primary Graph API channel is disrupted, the malware can continue receiving refreshed authentication tokens through DNS.

🔹 Victimology

Group-IB identified 12 systems carrying the implant. Only approximately three were actively communicating with attacker infrastructure. The recovered indicators, an Israeli mailbox used for exfiltration and malware samples uploaded from Israel, suggest focused interest in Israeli entities rather than broad opportunistic compromise.

🔹 Detection Considerations

Defenders monitoring Microsoft 365 environments should look for: • Calendar events with future dates far beyond typical scheduling horizons (e.g., 2050) • Unusual file attachments on calendar entries • DNS queries to cloudlanecdn[.]com with AAAA record types • The on-disk artifact logAzure.txt • Authentication patterns from .NET NativeAOT binaries interacting with Microsoft Graph API

🔹 Attribution

Group-IB links HOLLOWGRAPH to the Cavern backdoor framework with high confidence, based on code and behavioral similarities with known Cavern components.

🔹 HOLLOWGRAPH #ThreatIntelligence #C2 #Microsoft365 #MalwareAnalysis

🔗 Source: https://www.group-ib.com/blog/hollowgraph-microsoft-365/
1
0
1
0
Primer: Use JSON Batching to Speed up Graph Processing JSON batching is one of the most effective ways to speed up the processing of Graph API requests. Although it might seem complicated, once you understand how batches are put together and submitted to the Graph batch endpoint, it’s not that hard. JSON batching is of particular interest to large Microsoft 365 tenants that might need to process tens of thousands of accounts, mailboxes, groups, and so on. All explained here, along with a PowerShell script to show how it’s done. https://office365itpros.com/2026/07/21/json-batching-primer/ #Microsoft365 #MicrosoftGraph
1
0
1
0
🎖️ Of course, I'm proud and grateful. This is my 12th consecutive year as a Microsoft MVP (Most Valuable Professional). This international award is given to selected community members in recognition of their expertise and contributions. I will continue to create and share independent content about Microsoft 365 – especially Copilot and OneNote. Looking forward to connecting with fellow MVPs around the world. Congratulations to all award recipients! 🙋🏻‍♂️ #MicrosoftMVP #MVPBuzz #Microsoft365
2
0
1
0