
Remote
~swapgs
@swapgs@infosec.exchange
 mastodon 4.8.0-alpha.3+glitch
zigzagging my way through cursed code and bugs
954 Followers
1635 Following
8 Posts
Joined November 07, 2022
blog:
Replying to
@postmodern For the price question, you can already go pretty far with 2nd hand NUC / Mac minis. Google will also happily run your harness on their oss-fuzz infra (and pay bounties for good integrations in upstream projects)
RE: https://infosec.exchange/@wdormann/116819969049945466
Be more like @wdormann@infosec.exchange! It takes literally 5 minutes to see that all these so-called bugs are pure slop :(
Quoting

Somebody posted a bunch of exploits on GitHub that claim to be 0days.
https://github.com/bikini/exploitarium
Let's look at the first one: A 7-Zip MotW bypass.
Problem #1: 7-Zip DOESN'T EVEN WRITE MOTW FOR EXTRACTED FILES BY DEFAULT. This doesn't have a CVE, because apparently CVE is difficult.
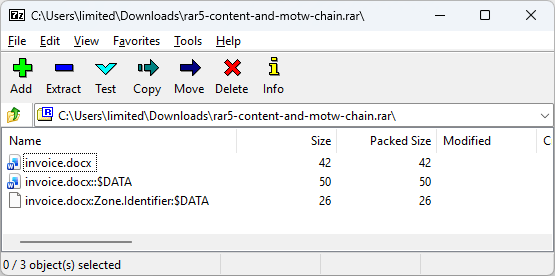
Problem #2: If you are a security-conscious person who enabled writing MotW in 7-Zip extracted files (contratulations!), you might notice that the archive contains a :Zone.Identifier:$DATA (MotW ADS) file in it and recognize shenanigans.
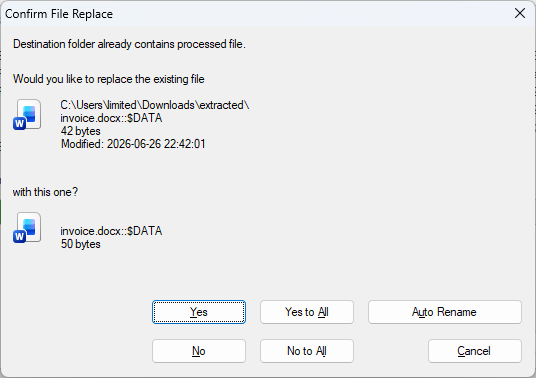
Problem #3: When you extract the file, you will be presented by the following dialog asking if you want to overwrite the ::DATA (primary data stream) of the file. And if you got this far, you're a security-conscious person, so you won't do this.
If you get past all of those hurdles, and click Yes in the dialog, then yes, you'll have a file extracted from a RAR that came from the internet that contains an attacker-controlled MotW (that says it didn't come from the internet).
Is this a vulnerability? Sure. But it both relies on a non-default 7-zip configuration, and it also relies on user interaction to succeed. As such, I can't say that I'm terribly interested in it.
How about the other 22 exploits in the repo? I skimmed through a few, and some seem quite contrived (sort of like the 7-zip one), but some may be legit.
But alas, I don't have the mental fortitude to sift through it all, based on what I've seen. Maybe somebody else here will.
Replying to on mastodon.sprawl.club
@ludicity@mastodon.sprawl.club "Huuum let me think about thaaaat" for 30 seconds and then proceeds to give a shallow encyclopedic definition of the keywords in the question while reading from another screen. To be fair, I’m not against Googling or LLMs _if_ they disclose it beforehand, but it shouldn’t be necessary on question about the achievements picked from their resume :)