Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

hanno

@hanno@mastodon.social
mastodon 4.8.0-nightly.2026-10-06
  • Open on mastodon.social

Freelance Journalist. Industry Decarbonization, Climate, Energy, IT-Security. #searchable

4399 Followers
378 Following
50 Posts
Joined April 03, 2017
Newsletter (Climate/Energy/Industry):
https://industrydecarbonization.com/
Web:
https://hboeck.de/
LinkedIn:
https://de.linkedin.com/in/hanno-boeck
Open post
hanno @hanno@mastodon.social
· 5mo ago
PSA: that linux root exploit is significant. Nobody cares about the number of bytes of the exploit. It's about as meaningless as the also popular "this attack takes only xx seconds / xx minutes". If attackers want to become root, they really don't care if you need 700 or 7000 or 70000 bytes. Or if it takes 2 seconds or 5 minutes. Irrelevant metrics for impact. Relevant Qs are: how reliable the exploit is, how widespread the vulnerability, etc.
103
3
74
0
Open post
hanno @hanno@mastodon.social
· 7mo ago

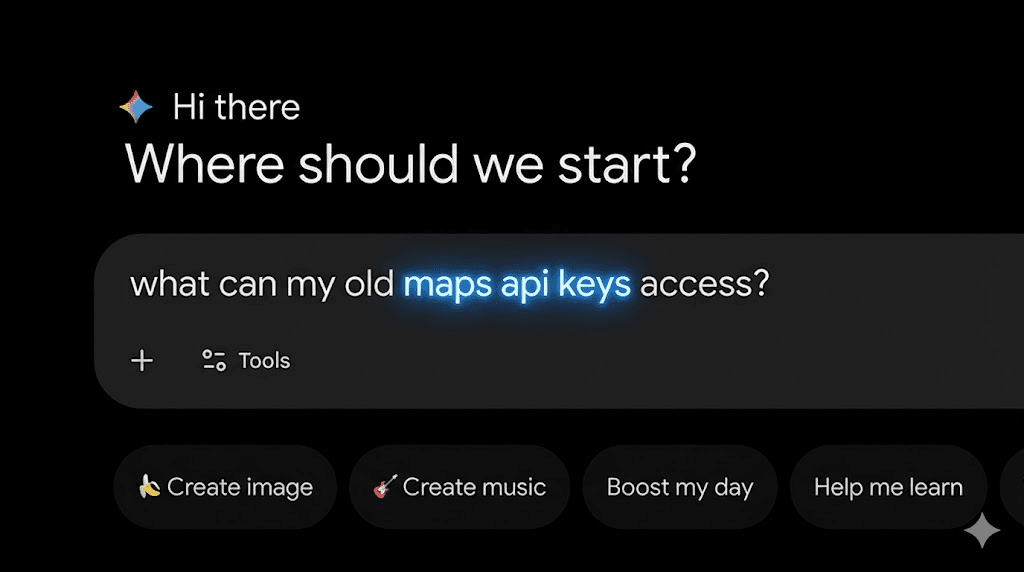
This is really a "WTF how could they ever think this is a good idea?" kind of vulnerability. Usually the kind of stuff you get from shady, incompetent startups, but this is Google...
https://trufflesecurity.com/blog/google-api-keys-werent-secrets-but-then-gemini-changed-the-rules

Google API Keys Weren
trufflesecurity.com

Google API Keys Weren

Google spent over a decade telling developers that Google API keys (like those used in Maps, Firebase, etc.) are not secrets. But that

185
9
208
4
Open post
hanno @hanno@mastodon.social
· 7mo ago

Ein Ü30-Landtagsabgeordneter macht super-creepy Kommentare über das Aussehen von Schülerinnen. Eine Frau weist darauf hin. Die Frau wird dafür kritisiert und bekommt Hasskommentare. Finde den Fehler...
https://www.spiegel.de/politik/deutschland/gruene-zoe-mayer-sie-hat-womoeglich-die-wahl-in-baden-wuerttemberg-entschieden-und-wird-jetzt-angefeindet-a-26d8aafb-0986-4f44-8912-f0ba97479991

spiegel.de
137
24
76
0
Open post
hanno @hanno@mastodon.social
· 8mo ago

Ihr sorgt Euch über den hohen Krankenstand? Wir haben da vor ein paar Jahren ein paar Dinge gelernt, wie man Infektionskrankheiten vermeidet. Impfungen, Luftfilter, Homeoffice, Masken, ...
Es ist schon bizarr, wie das komplett nicht Teil der Diskussion dazu ist.

179
0
113
0
Open post
hanno @hanno@mastodon.social
· 3mo ago

I never was a fan of VPN services to begin with, as they largely operate on claims based on outdated threat models. But if you thought Mullvad was the "cool" VPN, maybe reconsider?...
@jasmine@chaosfem.tw

chaosfem.tw

Jasmine running: "mullvad supports fascism apparently" - Chaosfem

28
3
23
0
Open post
hanno @hanno@mastodon.social
· 5mo ago

Completely boring take on IT security in the age of AI-discovered security vulnerabilities: Everything in IT security that was a good idea before is still a good idea. When security updates are available, install them. Reduce attack surface, avoid unnecessary complexity. Don't reuse passwords.

67
1
30
0
Open post
hanno @hanno@mastodon.social
· 3mo ago
Ich frag mich ja manchmal ob die Leute, viele bei großen Medien, die jahrelang Wagenknecht und ihr Umfeld als den linken Flügel der Linkspartei bezeichnet haben gelegentlich darüber reflektieren wie sehr sie damit daneben lagen https://www.spiegel.de/politik/deutschland/sahra-wagenknecht-will-rededuelle-mit-alice-weidel-und-schmiedet-regierungsplaene-a-fc38b70b-aa5f-4188-9d1d-149f20806792
spiegel.de
17
3
9
0
Open post
hanno @hanno@mastodon.social
· 4mo ago

Hey, we have another linux kernel local root exploit in IPSEC. If you build your own kernels: you probably don't need ipsec, disable INET{6,}_{ESP,AH}.

20
6
13
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
But that wasn't an isolated development either. It's clearly showing up everywhere. I'm running out of reasons not to think that AI tools got really good at finding security vulnerabilities. Obvious caveat: None of that changes that there are plenty of good reasons to be very worried about the whole AI thing.
20
17
6
0
Open post
hanno @hanno@mastodon.social
· 5mo ago

A lot of "AI security" really comes down to "maybe it's not the best idea to let something which is well known for hallucinating things give control over whether or not you still have your data tomorrow".

14
0
6
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
FWIW: I don't have a big conclusion here, I'm just sharing random thoughts and observations. /end thread
19
12
1
0
Open post
hanno @hanno@mastodon.social
· 3mo ago

Bin vor kurzem durch Zufall drauf gestoßen, dass das BSI vor längerer Zeit eine Live-CD namens BOSS (BSI OSS Security Suite) mit securitytools angeboten hat. Der Download lag auf der Domain bsi-bund-download[dot]de https://web.archive.org/web/20050621233640/http://www.bsi.bund.de/produkte/boss/index.htm
Die ist aktuell nicht registriert...
Ich hab nicht viele verweise drauf gefunden, und das ist alles sehr lang her, k.a. ob da noch relevanter Traffic ankommt. Aber falls sie jemand registrieren und mal gucken möchte...

web.archive.org
5
0
2
0
Open post
hanno @hanno@mastodon.social
· 3mo ago

Plastic Energy, one of the most promising chemical recycling🧪♻️ startups, is in financial peril💶

Plastic pyrolysis is a technology that promises to recycle plastic waste🗑️ that is too dirty or mixed to be recycled otherwise. It's also a controversial technology with a history littered with failures.
https://industrydecarbonization.com/news/chemical-recycling-pyrolysis-and-the-downfall-of-plastic-energy.html
🧵

industrydecarbonization.com
5
1
4
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
Something else happened, and that was *very* recently. Those reports grew in numbers. if I see 1-2 valid reports in a major open source lib from an AI tool, I'm not impressed. If I had enough funding, I could find valid vulns in a variety of ways. When the Mozilla/Antropic thing came out, that was what I was thinking. "Yeah, these are real bugs, but you know, if I had infinite funding like Antropic, and a team of top security people, you know how many bugs I could find in Firefox?"
15
18
2
0
Open post
hanno @hanno@mastodon.social
· 3mo ago

Ich habe hier einen Tomu übrig, das ist ein kleines, programmierbares Open-Hardware-USB-Gerät (kann im Slot versenkt werden), siehe https://tomu.im/ - will den jemand geschenkt? (bevorzugt in DE, dann kann ich's als normalen Brief verschicken.)
UPDATE: ist weg!

tomu.im
4
2
2
0
Open post
hanno @hanno@mastodon.social
· 6mo ago

There's a lot about the whole "AI topic" where I don't know what I should think. But I am quite worried what the flood of low-quality "AI" code will do to the free and open source ecosystems.
I found this mail from Michał Górny, one of the most active developers at Gentoo Linux (full disclosure: I'm also a Gentoo developer, but not one of the most active ones 🙂 ), about the issues the ecosystem is facing, quite insightful:
https://www.mail-archive.com/gentoo-dev@lists.gentoo.org/msg102518.html

mail-archive.com

[gentoo-dev] Dealing with (potential) slop packages

14
3
6
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
But why actively harmful? You're conditioning people to treat a "password" not like a secret. If you missed the sign at the entrance, you'll ask the next person for the wifi password. And, of course, they'll usually give it to you. That's obviously not how you should treat passwords. We call a thing a "password" if it serves a security purpose, locks access to something that's for you, not for random other people. We probably shouldn't call things "passwords" that aren't like that.
10
0
1
0
Open post
hanno @hanno@mastodon.social
· 3mo ago

One of the largest Green Methanol projects outside China has been cancelled 🌿🧪
The Beaver Lake Renewable Energy project was supposed to be a large-scale Biomethanol plant in Alexandria (Louisiana, USA). Plans were to do forest residue🌳🪵 gasification with technology from C2X (backed by A.P. Moller - Maersk) and combine it with CCS/CDR.
https://sungasrenewables.com/sungas-announces-cessation-of-beaver-lake-biofuels-project/
🧵

sungasrenewables.com
4
1
4
0
Open post
hanno @hanno@mastodon.social
· 6mo ago

Anyone good in statistics who can quickly answer a question? Assume I have an n-digit random binary number (for IT people: a bitstring). I calculate the number of 1s vs. 0s ("Hamming weight"). Expected to be usually ~0.5/50%. How does one calculate the probability for a given length n that it's above or below a certain value, i.e. <=40% or >=60%? And how many inputs would one on average need to get at least one such outlier?

9
13
11
0
Open post
hanno @hanno@mastodon.social
· 2mo ago
I suggest if you find a remote code execution vuln in the most popular CMS system in the world and make a web page for it, expect some traffic... https://wp2shell.com/ is currently down... In other news, if you use Wordpress and have disabled security-autoupdates, you shouldn't have done that. But if you have, you should probably update ASAP. And then re-enable autoupdates.
wp2shell

wp2shell: Pre Authentication RCE in WordPress Core

Check whether your WordPress site is affected by the pre-authentication RCE in WordPress Core. A free checker from Searchlight Cyber.

2
0
2
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
The most visible thing how AI impacted security vulnerabilities early on were slop reports. Famously, @bagder shared plenty of experiences with AI written garbage reports. But there's another more recent development. Real, and valuable security reports show up. I heard those starting early this year. Those were single instances, but they were clearly showing that there are companies out there developing tools that spit out real vulnerabilities, with proof of concepts, and sometimes even patches.
9
19
1
0
Open post
hanno @hanno@mastodon.social
· 3mo ago

Has anyone else experienced that with the latest firefox (152, on Linux/Gtk+) saving files with the keyboard only no longer works? (I.e. I do "Save Page as" -> press enter and it ignores the enter key and I can only save by clicking on the "Save" button)

3
2
0
1
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
From what I could gather, and what really was the information I was lacking: your average USB-C-to-USB-C cable probably does not support "SuperSpeed" / >=5Gbps. My implicit assumtion was "USB3 has been around for a while, probably every cable these days supports that." Well, wrong. I noticed that when I looked at USB cables in a shop, and saw that the average USB-C-to-USB-C cable in my supermarket explicitly said "480 Mbps" (aka "High Speed", not "SuperSpeed").
8
8
1
0
Open post
hanno @hanno@mastodon.social
· 10mo ago
I do wonder whether @TimPhSchaefers plans to transfer the domain back to them or keep it. I guess the latter would be safer for them. Otherwise we may have an update to that story again in 10 years that they lost it again or something...
17
3
1
0
Open post
hanno @hanno@mastodon.social
· 7mo ago
Replying to
Ok, I guess I know what they were thinking. They outsourced the thinking to an AI, and that probably made that change. One more sign of the quality deterioration at Github... Unfortunately, the network effects are strong, and even I'm fully aware how Github is getting worse all the time, not sure that'll make me switch to something else...
10
3
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
Occasionaly, you read tipps like "might be the cable", "try another cable". Of course, I tried another cable. I tried all usb-c-to-usb-c and some usb-a-to-usb-c cables I had laying around. No change. I dismissed the "it might be the cable" tipps, as my main USB-C cable came from what I always read is a very reliable USB cable vendor, and multiple other cables didn't change a thing. Turns out: it was the cable(s).
7
2
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
What security goal does that password serve? I'd say, there's no reasonable "threat" you're defending against. The password is freely shared. Yeah, you're "protecting" your Wifi from being used by a random stranger sitting somewhere close enough to use it, but not a guest of your facility/event/... - but is that really something it's worth to protect against?
6
5
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
And here's the good news: N2O is composed of Nitrogen and Oxygen💨, so one can turn it into Nitrogen and Oxygen. And that's really cheap💶 compared to almost anything else you could do to reduce emissions. After having covered this already twice in my newsletter📰, I made a short video🎥 about it: https://www.youtube.com/watch?v=RByupbPSGd0
5
1
2
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
It's pretty much: If you want to use very fast USB connections, you need a special cable, the average cable you have laying around probably won't support it. They're a bit more expensive, but not excessively so. (There are also many newer standards enabling speeds up to 80Gbps.) I now have a cable with up to 80 Gbps (my HD only does 5, but looks like that's backwards compatible), and my external HD connects with SuperSpeed without any problems.
5
2
0
0
Open post
hanno @hanno@mastodon.social
· 7mo ago

RE: @TimPhSchaefers@chaos.social

Aus Fehlern lernen, so unterschätztes Konzept...
@TimPhSchaefers@chaos.social@mastodon.social

chaos.social
6
0
3
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
Europe's🇪🇺 failure to scale Green Methanol production leads to a compounding failure to attract one of the most promising projects for a fossil-free future chemical industry🌱⚗️🏭 It all feels like what played out in the Solar☀️ industry. China invests early and big. More in my latest newsletter.
4
1
1
0
Open post
hanno @hanno@mastodon.social
· 8mo ago
Replying to on mastodon.social
@publictorsten@mastodon.social Das ist definitiv aus der Kategorie "ob das Satire ist oder echt kann man wirklich nicht wissen, beides ist ungefähr gleich plausibel"
6
1
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
(Ok, not sure that's how it goes for other people, but if I get interested in something, that's how it goes.) Why should you care? Well, you should care if you care about super-cheap options to reduce Greenhouse Gas emissions💨🏭. The production of Nitric Acid and a few other chemicals🧪 causes N₂O, which is the third-most important Greenhouse Gas, and has a warming effect 273 times larger than CO₂.
3
1
1
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
Was this real? Announcing things is cheap; building things matters🏗️ In 2025, it became clear that it is real. 4 industrial-scale Green Methanol plants are operational in China. In Europe? 1 In 2024, A.P. Møller Holding (owners of Maersk🚢) created the startup VioNeo, with plans for a fossil-free plastics plant in Antwerp🇧🇪. In 2026, they changed plans & want to build "in China near green methanol supply"
2
1
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
@bluca @bagder @gregkh to that I'll just say that you have the same problem with humans. It's often easier to spot a bug than to decide whether it's a security bug. (And the latter is also, to some degree, a value judgement. Is something that isn't in itself exploitable but could become an attack vector in combination with other bugs a vulnerability? People keep fighting about such cornercases and whether they deserve CVEs, because nobody can clearly define what "a vulnerability" is.)
2
0
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
Here's what I wrote about N₂O emissions in 2023: https://industrydecarbonization.com/news/the-avoidable-super-greenhouse-gas-from-fertilizer-nylon-and-vitamin-b3-production.html And here more recently about the situation of European Caprolactam producers, and how, unfortunately, many low-emitting factories in the EU are shutting down: https://industrydecarbonization.com/news/some-of-the-cleanest-polyamide-and-nylon-precursor-factories-are-shutting-down.html
industrydecarbonization.com
2
0
2
0
Open post
hanno @hanno@mastodon.social
· 33mo ago

Ja, bitte macht das endlich... https://www.spiegel.de/politik/deutschland/karl-lauterbach-will-homoeopathie-als-kassenleistung-streichen-a-dab09eda-6a6e-4432-a343-457d5202f914

spiegel.de
38
1
14
0
Open post
hanno @hanno@mastodon.social
· 10mo ago
Replying to
@cosmiction but even then, this is, of course, technical debt. If they start doing this today, they could still be harmed by their 15 year old abandoned domains.
4
0
0
0
Open post
hanno @hanno@mastodon.social
· 7mo ago
Replying to
@bws@social.linux.pizza network effects are that people are much less likely to find my code, much less likely to submit PRs, if it's on codeberg or somewhere else. Yeah, I can somewhat get around this by mirroring on github and accept PRs there, but it's a lot more hassle.
2
0
0
0
Open post
hanno @hanno@mastodon.social
· 6mo ago
Replying to
@eingemaischt bei dem das ich gekauft hab und auch anderen angeboten die ich gesehen hab steht die Zahl auf dem stecker drauf. Ich glaube als Faustregel kannst Du "wenn es mehr als 480Mbps kann steht's warscheinlich drauf" nehmen.
1
0
0
0
Open post
hanno @hanno@mastodon.social
· 4mo ago
Replying to
@mdione@en.osm.town https://www.openwall.com/lists/oss-security/2026/05/13/3
openwall.com
0
0
1
0
Open post
hanno @hanno@mastodon.social
· 4mo ago
Replying to
@dalias@hachyderm.io I think in both vulnerability cases it was in ESP (esp{4,6} modules for IPv4/v6). But AH is also "something from IPSEC", so I disabled that as well. I'm not super familiar with IPSEC beyond "it's something I do not use and do not need"...
0
1
0
0
Open post
hanno @hanno@mastodon.social
· 10mo ago
Replying to
@Lapizistik @TimPhSchaefers bmftr[dit]de? steht zum verkauf, steht allerdings kein Preis dran, man kann ein Angebot abgeben.
0
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:45:13 UTC