Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Exa :calim:

@Exagone313@share.elouworld.org
mastodon 4.6.9
  • Open on share.elouworld.org

Full Stack Devops Engineer
⭐️ #web #sysadmin #programming #infosec #privacy
:archlinux: Arch Linux :sway: Sway :neovim: neovim

334 Followers
893 Following
38 Posts
Joined April 03, 2017
About me:
https://elou.world/about
Matrix (private messages):
https://matrix.to/#/@exagone313:matrix.org
Languages:
🇫🇷 FR, EN
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 1w ago
Replying to
@Crell@phpc.social @outofcontrol@phpc.social Yes, but you need to enable the Podman socket and set an environment variable and it's not documented enough. No need to install podman compose. systemctl --user enable --now podman.socket export DOCKER_HOST="unix://${XDG_RUNTIME_DIR}/podman/podman.sock" Note that there are a few differences, e.g. in network isolation, and that as your user you can't publish reserved ports. But for development stuff it is nice. Note that root in your container is equivalent to your user on the host, so you need to use images that do not change the default user if you want to share the same uid:gid as your host user on the files. If you need to "become root" in your terminal, without running a container, you can use "podman unshare". You can then also access a container rootfs with: cd "$(podman mount your-container)"
1
5
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Trademark Violation: Fake Notepad++ for Mac Someone vide-coded a macOS app with Notepad++ source code as input. They claimed it is an official macOS port, which is not the case. They used the name Notepad++ for Mac, with the same logo and registered a domain name with a "-mac" suffix appended to the official one. Exactly like phishing. They even included information on Notepad++ core developer without authorization. And their repository don't include Git history with the attribution of the hundreds of contributors. Various news outlets have started reporting on this as an official project. It needs to stop. https://notepad-plus-plus.org/news/npp-trademark-infringement/
notepad-plus-plus.org

Trademark Violation: Fake Notepad++ for Mac | Notepad++

39
3
79
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@cyrielle_chatelain@piaille.fr Bon bah la représentante de Wero a dit qu'ils ont "aucun lien avec les États-Unis", et c'est dit sous serment. Ça pose un problème.
4
2
1
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@dcoderlt I'm wondering if the article is fully written by a human, the numbered sections seem odd to me.
2
3
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 34mo ago
Replying to
@devxvda@mastodon.ie That can't be right, the world is due to end in 2012.
42
12
3
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@randomfelix Notepad++ is an open source project. The developer doesn't use Apple devices, why would they port their software? This not a commercial project where you want to convert new users. They are not against having a third-party port as long as it respects their trademarks. Immediate report is the legal thing to do. Even if Notepad++ is not a commercial project, it is still trademarked.
1
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to on universeodon.com
@bgrier@universeodon.com Hello, this application is not endorsed by the Notepad++ project. This is actually a vide-coded rip-off. https://notepad-plus-plus.org/news/npp-trademark-infringement/
notepad-plus-plus.org

Trademark Violation: Fake Notepad++ for Mac | Notepad++

1
1
1
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@aeris@firefish.imirhil.fr T'as pas pu être auditionné dans la commission d'enquête sur le numérique et la souveraineté ? Bon c'est peut-être pas le bon cadre :calim:
1
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
Replying to on phpc.social
@ramsey@phpc.social I'd rather use ++C
1
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
Replying to on infosec.exchange
@AAKL@infosec.exchange I thought the picture showed a graveyard
1
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 7mo ago
Replying to on gardenstate.social
@stefan@gardenstate.social Same for me, watched 13 episodes when it came out and I didn't feel attached to the MC so I dropped it. I don't understand why so many people enjoy this anime.
1
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 7mo ago
Replying to on mastodon.social
@Le_M_Poireau@mastodon.social C'est une copie de l'article en accès libre.
1
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago

Someone apparently found some security issues in Forgejo but isn't willing to follow the security procedure of the project.

What is troubling me is that their posts calling out of the potential vulnerabilities are getting removed on Mastodon, first on infosec[.]exchange then on mastodon[.]social.

What is the limit on rules against harassment when it targets an entity (the Forgejo/Codeberg project) and not individuals? Is it okay to downplay or hide the potential security issues in this story?

I'm happy to host my own instance with my own rules.

https://dustri.org/b/carrot-disclosure-forgejo.html

EDIT: The post in question was restored on infosec[.]exchange.

dustri.org

Carrot disclosure: Forgejo

Personal blog of Julien (jvoisin) Voisin

0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@sanji@mamot.fr Bonjour, Possible de supprimer ce post ? Il ne s'agit pas d'un port officiel mais d'une violation de marque. Demain ça sera utilisé pour une utilisation malveillante, c'est sûr. https://notepad-plus-plus.org/news/npp-trademark-infringement/
notepad-plus-plus.org

Trademark Violation: Fake Notepad++ for Mac | Notepad++

0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 1w ago
Replying to
@Crell@phpc.social @outofcontrol@phpc.social Note that Docker also supports rootless, but it is also not known enough and less practical than Podman: https://docs.docker.com/engine/security/rootless/
Rootless mode
Docker Documentation

Rootless mode

Run the Docker daemon as a non-root user (Rootless mode)

0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 1w ago
Replying to
@Crell@phpc.social @outofcontrol@phpc.social docker-compose was primarily done for rootful docker. and podman was primarily done for socket-less usage
0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 7mo ago
Replying to
@robb Have you considered releasing the base (svg and basic css for placing it in a corner) in a public domain license, for adopting without having credits required? MIT License for assets is a bit weird too (it only mentions software and docs).
0
2
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 1w ago
Replying to
@Crell@phpc.social @outofcontrol@phpc.social For production stuff I recommend using Quadlet which integrates Podman into systemd units: https://docs.podman.io/en/latest/markdown/podman-systemd.unit.5.html
docs.podman.io

podman-systemd.unit — Podman documentation

0
4
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 32mo ago
Replying to
@samhenrigold@hachyderm.io But their app doesn't have an adblocker and it can get more data for advertising 😉
0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to

I just don't like this part:

All EPI and Wero data is stored in European data centers, and is encrypted and protected against potential extraterritorial access through appropriate security measures.

The application that runs on AWS surely has access to the encryption keys. Sounds like an excuse. Unless proven otherwise it doesn't prevent extraterritorial access.

0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@macgeneration@social.macg.co Désolé pour mon ton 😅 Leur annonce mentionne exactement ça mais n'explique pas ce que ça veut dire.
0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@bortzmeyer@mastodon.gougere.fr @pb@mast.eu.org @Octopuce@mamot.fr C'est fix sur Arch 😅 Mais effectivement pas sur Debian stable https://security.archlinux.org/CVE-2026-31431 https://security-tracker.debian.org/tracker/CVE-2026-31431
security.archlinux.org

CVE-2026-31431 - linux - Arch Linux

0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
Replying to on mastodon.social
@canardpc@mastodon.social La page Itch n'existe pas, j'y ai cru
0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to

@macgeneration@social.macg.co Euh ... C'est incompréhensible techniquement ça.

Là où beaucoup de protocoles font transiter le trafic de plusieurs personnes dans un tunnel partagé, Surfshark explique que Dausos attribue à chacun son propre tunnel dédié. Autrement dit, les données ne circulent pas dans le même couloir que celles des autres utilisateurs, ce qui doit limiter certaines pertes d’efficacité et renforcer l’isolation du trafic.

C'est quoi un tunnel partagé ? Un VPN dans le sens qu'on l'entend est un NAT + un tunnel pour chaque utilisateur.

Et plus rapide qu'AES je veux bien voir ça, sachant que les CPU ont un support matériel pour AES depuis des années.

0
2
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 10mo ago
Replying to
@b0rk@social.jvns.ca Hmm, are those extra fields stored in the commit itself or can arbitrary metadata be stored in Git? For some context (and it might have been experimented on already), Mercurial has an extension called evolve that is providing "obsolescence markers", which are pushed (and pulled) in the remote repository. Those obsolescence markers let you know when a commit was rewritten in history, e.g. after a rebase or after modifying it, and this is used to automatically "evolve" a branch modified by your peers (and also for the server to forbid pushing outdated changes, like with force-with-lease). I'm wondering if evolve could be ported to Git.
0
2
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@adngdb@tutut.delire.party Yes it may be relevant to my perception.
0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 19mo ago
Replying to
@torgo@mastodon.social The article you linked is only describing a copy command, which is not something new and it is not related to the permission to see the content of the clipboard which landed last year. @CuillereNessie@mastodon.social @yatil@yatil.social
0
2
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 8mo ago
Replying to on neondystopia.world
@Saorsa@neondystopia.world I'm included in the "seirdy[.]one" blocklist and they don't answer emails about asking for a reason. @xaetacore@neondystopia.world
0
0
1
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
Replying to on shelter.moe
@TritTriton@shelter.moe 8 Mbps en down sur de la fibre ?
0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@aeris@firefish.imirhil.fr @lord@pleroma.lord.re J'ai testé autre chose : envoyer à Claude un dépôt, lui dire de détailler le fonctionnement d'une fonctionnalité principale, puis ensuite lui dire de réimplémenter en utilisant cette spec. Ça marche plutôt bien mais j'ai bien évidemment de fortes ressemblances avec le code d'origine. Mais comment définir précisément ce qui est considéré comme "trivial" et ce qui est vraiment sous copyright ou droit d'auteur ?
0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 8mo ago
I have read the archives of the old issues on the Oliphant blocklist debacle and I realize this happened only three years ago. Recently, someone created a project on GitHub called vouch, which can be used to create public block lists of users. They plan to make it possible for multiple projects to share block lists. This is even worse than Oliphant because it directly contains usernames and not merely instance domain names (which can also refer to individuals). And of course, no reasons need to be provided, appeal is impossible. https://github.com/mitchellh/vouch/issues/33
github.com
0
0
1
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 5mo ago
Replying to
@tanavit @cyrielle_chatelain Oui c'est possible qu'elle ne soit pas au courant. Pour l'hypothèse de se réfugier derrière les décisions du sous-traitant ça rappelle certaines montages financiers. Mais si on met la main sur le cahier des charges on peut vérifier comment cette décision a été prise.
0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
Replying to on shelter.moe
@TritTriton@shelter.moe N'hésite pas à activer l'option pour avoir une IPv4 dédiée. Et bon courage parce qu'elle n'est pas fixe, et même le bloc IPv6 peut changer.
0
1
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 7mo ago

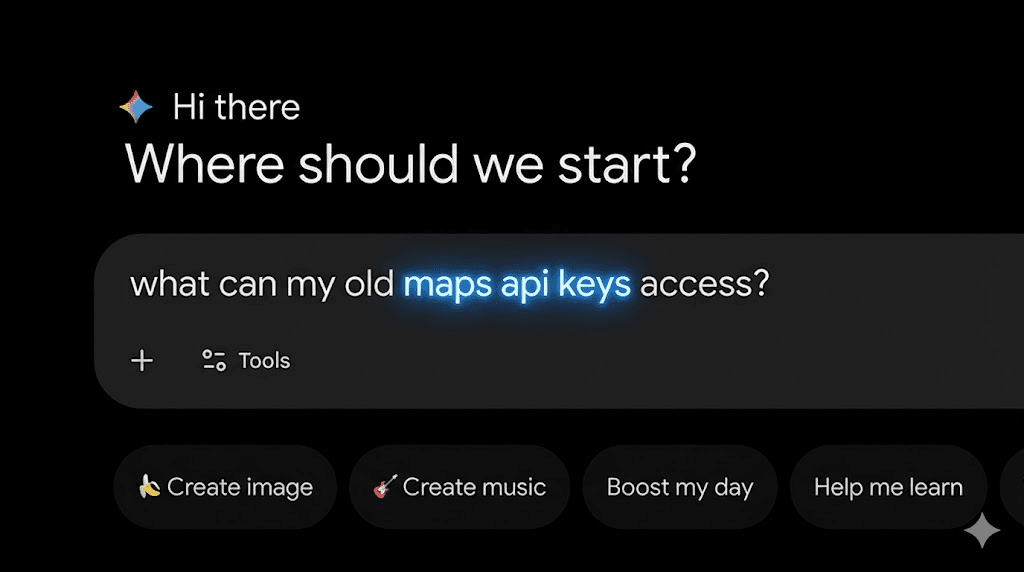
We scanned millions of websites and found nearly 3,000 Google API keys, originally deployed for public services like Google Maps, that now also authenticate to Gemini even though they were never intended for it. https://trufflesecurity.com/blog/google-api-keys-werent-secrets-but-then-gemini-changed-the-rules via https://news.ycombinator.com/item?id=47156925

Google API Keys Weren
trufflesecurity.com

Google API Keys Weren

Google spent over a decade telling developers that Google API keys (like those used in Maps, Firebase, etc.) are not secrets. But that

0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
I'm seeing an increasing number of tools that do not provide a "latest" version to install. The reasoning is that without a "latest" version, users will read breaking changes before upgrading to a newer version. Personally, I want to decrease the time needed for maintenance and for my own stuff I prefer to be bold: I have backups in place if something goes wrong, and I'd rather have automated upgrades to the latest version that go wrong rather than having to follow versions and make upgrades manually. So I end up making scripts that fetches the latest version and upgrades to it, which I make it run daily. And it works. Note: For some "core" services that I can't afford to be down, I prefer to play it safe. But for most apps, it is not a big deal if I have to SSH-in and rollback.
0
0
0
0
Open post
Exa :calim: @Exagone313@share.elouworld.org
· 6mo ago
Replying to on mastodon.gougere.fr
@bortzmeyer@mastodon.gougere.fr Attend que Trump découvre qu'on a l'arme nucléaire et qu'on va renforcer notre arsenal dans les prochaines années.
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 11:23:18 UTC