🚨 Critical VMware Advisory
Broadcom has patched multiple critical VMware vulnerabilities affecting vCenter Server and ESXi, including an authentication bypass (CVSS 9.8), directory traversal leading to RCE (CVSS 9.8), and a VM escape via VMXNET3 (CVSS 9.3). Organizations should prioritize patching vCenter and ESXi infrastructure as soon as possible.
Technical breakdown, affected versions, and mitigation:
https://thecybersecguru.com/news/critical-vmware-vcenter-auth-bypass-rce-vm-escape-vulnerabilities/
#InfoSec #CyberSecurity #VMware #vCenter #ESXi #Virtualization #RCE #ThreatIntel #BlueTeam #SysAdmin #CVE
#vcenter
2 posts · Last used Jul 30
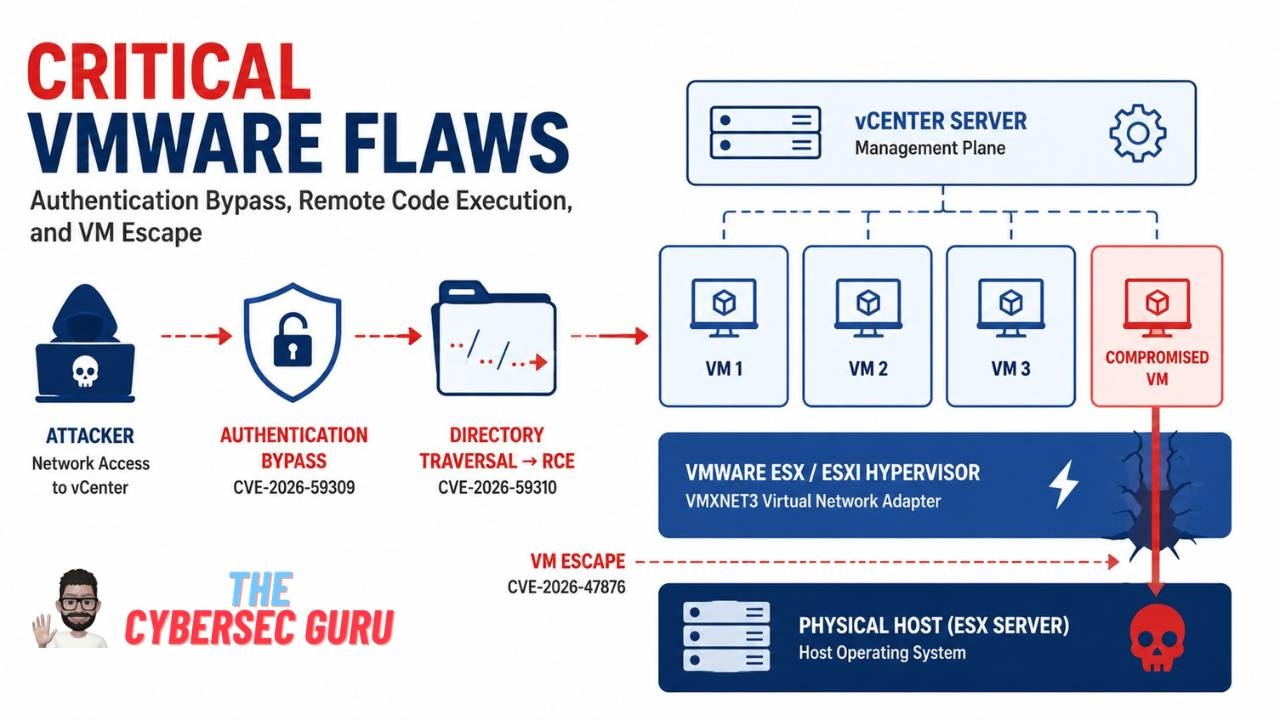


Broadcom patched a critical VMware vCenter vulnerability. CVE-2026-59309 and CVE-2026-59310 both score 9.8 CVSS and allow auth bypass or code execution.
#VMware #vCenter #CVE202659309 #CVE202659310 #ESXi #InfoSec
https://meterpreter.org/vmware-vcenter-cve-2026-59309/?utm_source=mastodon&utm_medium=jetpack_social


You've seen all posts