
#identity
55 posts · Last used 14d

📚️ 🇺🇸
The Rhetoric of White Slavery and the Making of National Identity
"At the turn of the twentieth century, the white slavery panic pervaded American politics, influencing the creation of the FBI, the enactment of immigration law, and the content of international treaties. At the core of this controversy was the maintenance of white national space."
🔗 https://msupress.org/9781611864595/the-rhetoric-of-white-slavery-and-the-making-of-national-identity/
#Race #Rhetoric #Identity #Reading #UniversityPress #Academia #History #Histodons #C20th #20thCentury #USA #US #UnitedStates #America #Book #Books #Bookstodon
Looking in the Mirror of My Past as a Korean Adoptee in the United States
https://lithub.com/trying-to-look-into-the-mirror-of-my-past-as-a-korean-adoptee-in-the-united-states/
#Memoir #Identity #Adoption


An ID verification company is suspected of being responsible for a data breach involving 153 million identity cards that were put up for sale to criminals! The cache includes drivers licenses, travel documents, medical cards, and other government IDs.
Companies are storing private identity documents which are being hacked by criminals.
We need better privacy rights.
https://matthewrosenquist.substack.com/p/153-million-reasons-to-rethink-identity
#privacy #cybersecurity #databreach #Identity
Boosted by @welcome@friends.deko.cloud
#introduction
Hi, I'm Merten. I've been a software engineer for 24+ years, and earlier this year I very nearly got taken by a phishing scam. I caught it late enough that it genuinely rattled me, and the fact that I came that close at all got me wondering why this is still a problem after all this time. If all that experience isn't enough to save you, it probably isn't a user-education problem.
What I found was that SMTP has never had a way to prove who actually sent a message. SPF, DKIM and DMARC all check the domain and the server, but never the person, so a lookalike domain can pass all three and still land in your inbox looking perfectly fine. Everything built since has been trying to guess at the answer from the outside, which is a good part of why we are all still guessing.
I couldn't find anyone working on that particular part, so I thought I'd have a go at it myself. I've always found that turning something intricate into something simple is where the real value is, and the simple version here is that the address is a keypair, verifiable all the way up to its domain and the servers hosting it, so a message either checks out against the sender's key or it doesn't. There's a spec and a reference server, both Apache-2.0, and it'll run in a single container if you'd like to poke at it.
I moonlight on it, so it moves at evenings-and-weekends pace. I'll mostly be posting about mail infrastructure and protocol design, and occasionally about being wrong on both.
If you spot something I've got wrong, I'd genuinely like to hear it.
Spec, code and docs are all at https://dmcn.dev
#infosec #email #identity #dmcn
A password login and a passkey login are the same verified persona, holding the same role, with a completely different answer to "how strongly did you just prove that." Modelling session assurance and step-up in OpenFGA as a public wildcard plus a condition that stores nothing on the tuple at all - and why the elevated session behind it has to stay genuinely ephemeral for any of it to be honest.
https://tobytes.com/articles/session-assurance-step-up-fga
#auth0 #fga #identity
Building an apidays workshop demo with Claude Code doing the implementation, I had it run an adversarial review of the build plan before either of us wrote application code. It found a structural flaw in the Auth0 FGA model, not a polish problem - the check was always true, so there was nothing for an AI agent to be denied and nothing to delegate.
https://tobytes.com/articles/why-the-apidays-workshop-plan-restarted-from-scratch
#auth0 #fga #ai #identity

Rebalancing or retreat? Canada's peacekeeping legacy fades away
After decades of gradual decline, Canada’s peacekeeping tradition is entering its final chapter. The Defence Department is shutting down four overseas missions and shrinking another, arguing troops are needed elsewhere. Critics warn the move sacrifices a defining national identity and surrenders diplomatic influence to countries such as Ch...
https://www.cbc.ca/news/politics/peacekeeping-canada-troops-nato-latvia-9.7297599?cmp=rss

Auth0's Passkey APIs let you build passkey sign-in directly into your own UI instead of redirecting to Universal Login. Wrote up how the two fit together, hand-rolled vs pre-built self-service passkey management, and one Allowed Origins (CORS) setting worth checking before you go chasing a WebAuthn bug that isn't there.
https://tobytes.com/articles/building-embedded-passkey-login-with-auth0
#auth0 #passkeys #identity
Running the same OpenFGA model, unchanged, across six industries - and the interesting part isn't that it's reused, it's which primitive gets reused for what. Joint ownership vs a permanent limited role vs an actual delegation, and where flattening them would go wrong.
https://tobytes.com/articles/one-fga-model-twelve-industries
#auth0 #fga #identity
What is a homeland? It is not a question to be answered and forgotten. It is your life, and it is your cause🇵🇸🇵🇸💔❤️🩹
#GazaVerified ✅
https://chuffed.org/project/177144
#Palestine #FreePalestine #Homeland #Identity #Justice
#Gaza #Palestine @mutualaid@fedigroups.social@DailyGaza@kolektiva.social @kathimmel@mstdn.social @DrALJONES@mastodon.social @simon_brooke@mastodon.scot @wrzky@kolektiva.social @Majden888@snowfan.it @MajDen@sociale.network @raphaellakay@mastodon.world @eldadoinquieto@mastorol.es @sallytheflame@mastodon.world @BylinesScotland@mastodon.social

CW: Mental health
Auth0 Anonymous Sessions sets the auth0_anon cookie only on a genuine create call, never on a renewal - confirmed by testing both explicit session_token and cookie-only renewals. Metadata is fixed at creation too, by design. Same underlying reason for both, and it forces a different pattern for tracking anything (a cart, in my case) across the handoff to login.
https://tobytes.com/articles/auth0-anonymous-sessions-fixed-at-creation
#auth0 #identity #webdev
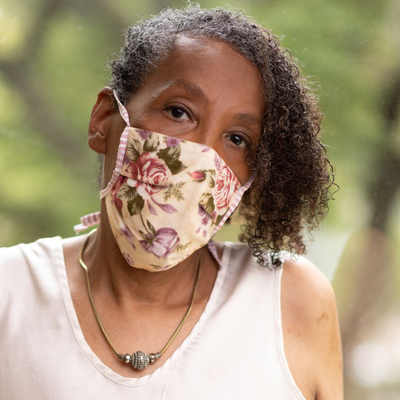
At the back end of 69, I'm still not sure which is the more isolating, the relentless, cynical ageism of the young, or the cultural infantilization and internalized ageism of my fellow seniors.
Why the “Boomer” Label Fails Black Americans Born Under Jim Crow – ΆLETHEIA-ENGIN
#US #Culture #History #BlackFedi #BlackMastodon #Identity #Racism #Ageism #ClassHierarchy #Boomer #List #Essay #Rant
https://aletheng.org/2026/08/why-the-boomer-label-fails-black-americans-born-under-jim-crow/

A login and the person behind it aren't the same security principal. Extending the delegated-access model from earlier this year with person/persona/business, and mapping it to real Auth0 sub claims for a personal login versus one federated through a workplace IdP.
https://tobytes.com/articles/separating-people-from-accounts-persona-model
#auth0 #identity #fga
Work does not deserve your full self
https://www.npr.org/2026/07/31/nx-s1-5913708/work-does-not-deserve-your-full-self
#WorkLife #Identity #Culture
My live Auth0 session and token demo grew three new patterns since I first wrote this up: CIBA against a real Guardian push (now with a Rich Authorization Requests toggle), the Device Authorization Grant, and a comparison against a real Hono app on Cloudflare Workers. The session view also moved out of a single profile page into a sidebar that's visible on every page in the app.
https://tobytes.com/articles/auth0-token-session-demo
#auth0 #oauth #identity
Updated my Auth0 session and token management taxonomy with two grant types I'd left out the first time: CIBA and the Device Authorization Grant. Both are decoupled from the requesting device's own browser but solve different problems. Also added what Rich Authorization Requests (part of Highly Regulated Identity) changes on a CIBA push - structured fields instead of one opaque string.
https://tobytes.com/articles/auth0-session-token-management-options-explained
#auth0 #oauth #identity