#attack

100 posts · Last used 13d

Arista Networks Patches Critical VeloCloud Orchestrator Zero-Day Exploited in the Wild

Arista Networks disclosed a critical CVSS 10.0 vulnerability (CVE-2026-93952) in VeloCloud Orchestrator On-Prem that is being actively exploited to gain unauthenticated remote access to orchestrator hosts and managed edge devices.

If you run VeloCloud Orchestrator On-Prem, this is urgent. Make sure its web interface is not reachable from the internet and is accessible only from trusted admin networks, then update right away to a fixed version (5.2.3.16, 6.4.2.8 or later). Attackers are already using this flaw to take full control without any password. After patching, look for the hidden file /usr/local/sbin/.vcnode.js or the x-vc-opt header in your web logs, and if you find either, treat the orchestrator and every connected Edge device as compromised. #cybersecurity #infosec #attack #activeexploit https://beyondmachines.net/event_details/arista-networks-patches-critical-velocloud-orchestrator-zero-day-exploited-in-the-wild-4-k-v-7-w/gD2P6Ple2L
0
0
0
0
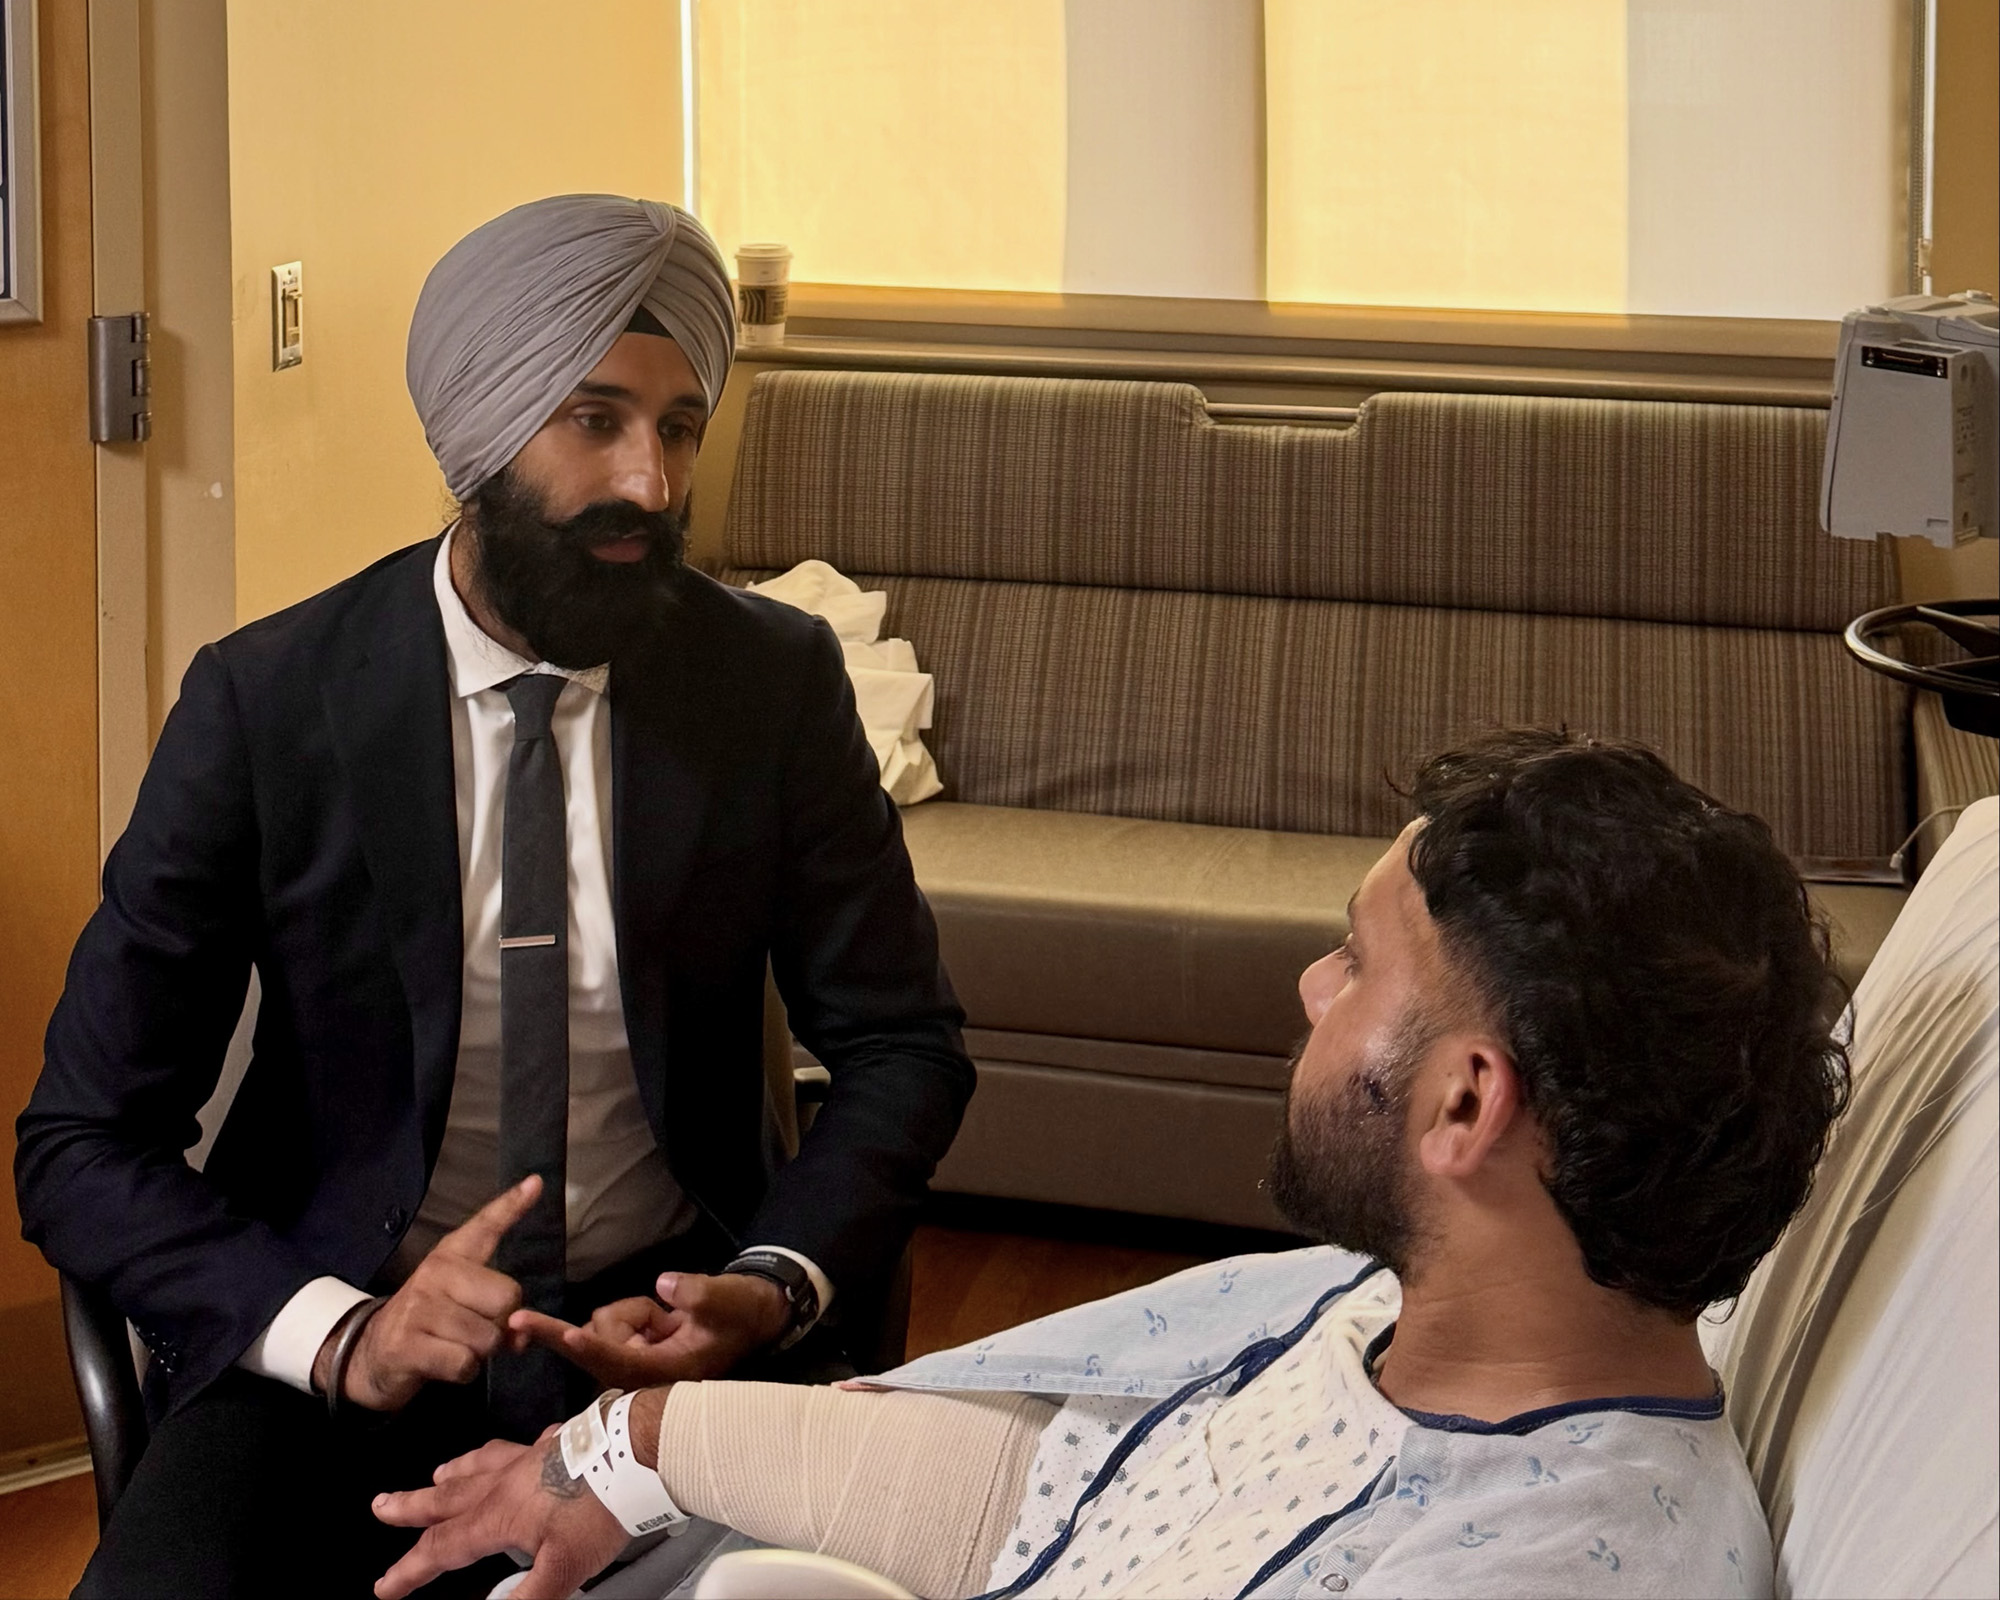
Punjabi #Sikh tucker nearly killed in #Wyoming truck stop attack. Suspect in custody is a fellow big rig driver who stabbed a fellow California man 17 times. Within 90 minutes, a suspect with #Slavic heritage last name was taken into custody thanks in part to an apparent #Mexican heritage family at the rest area that heard the #attack occur and helped pursue the suspect and care for the victim. The suspect apparently is from Southern California with a previous address in #Pennsylvania. The attack occurred four days after a post on #MelonHusk Xitter by the U.S. Department of Homeland Security that showed a Transformer facing off against a Sikh man. and read “#AmericaForAmericans. Get off our roads, you don’t know how to drive Mr. Singh,” the official #DHS account post said. https://wyofile.com/sikh-truck-driver-stabbed-at-wyoming-rest-stop-suspect-faces-attempted-murder-charge/ The Great American #MeltingPot Plot continues...
0
0
1
0
🔴 BREAKING: The majority of UK newspapers on Saturday featured the fallout from Earl Spencer’s new book on Princess Diana, splashing headlines like “Monstrous words” and warning that “Russia to ramp up war”. The book’s revelations have sparked a media firestorm and renewed geopolitical speculation. 🕐 05:00 UTC Read more: https://rawfeednews.com/post/mu7x5gka.html #Attack #Russia
0
0
2
0

WSO2 Warns of Active Exploitation Targeting Critical Authentication Bypass

WSO2 is warning of active exploitation of a critical authentication bypass vulnerability (CVE-2026-5430) that allows attackers to take over administrative accounts and steal sensitive API credentials. The flaw affects multiple middleware products and has been targeted in the wild since mid-September 2026.

If you run WSO2 API Manager, API Control Plane, Traffic Manager, or Universal Gateway, check for affected versions and patch immediately to the latest update level from WSO2. If you are using open source version apply the public GitHub fix. Attackers are already using forged tokens to gain full admin access. After patching, assume your secrets were exposed and rotate all API keys, backend credentials, consumer keys, and application secrets, and check your logs for suspicious access since September 13, 2026. #cybersecurity #infosec #attack #activeexploit https://beyondmachines.net/event_details/wso2-warns-of-active-exploitation-targeting-critical-authentication-bypass-6-5-6-k-k/gD2P6Ple2L

0
0
0
0
Replying to
Since August 31, #NATO fighter jets have taken off three times after #Russian aircraft violated NATO airspace. #Russia has increased its violations of NATO airspace, which has raised concern over a possible Russian #attack on neighboring NATO member states. https://kam.lt/reagavimo-i-orlaiviu-skrydzius-prie-baltijos-valstybiu-sienu-duomenys-rugpjucio-31-rugsejo-6-d/
2
2
5
0
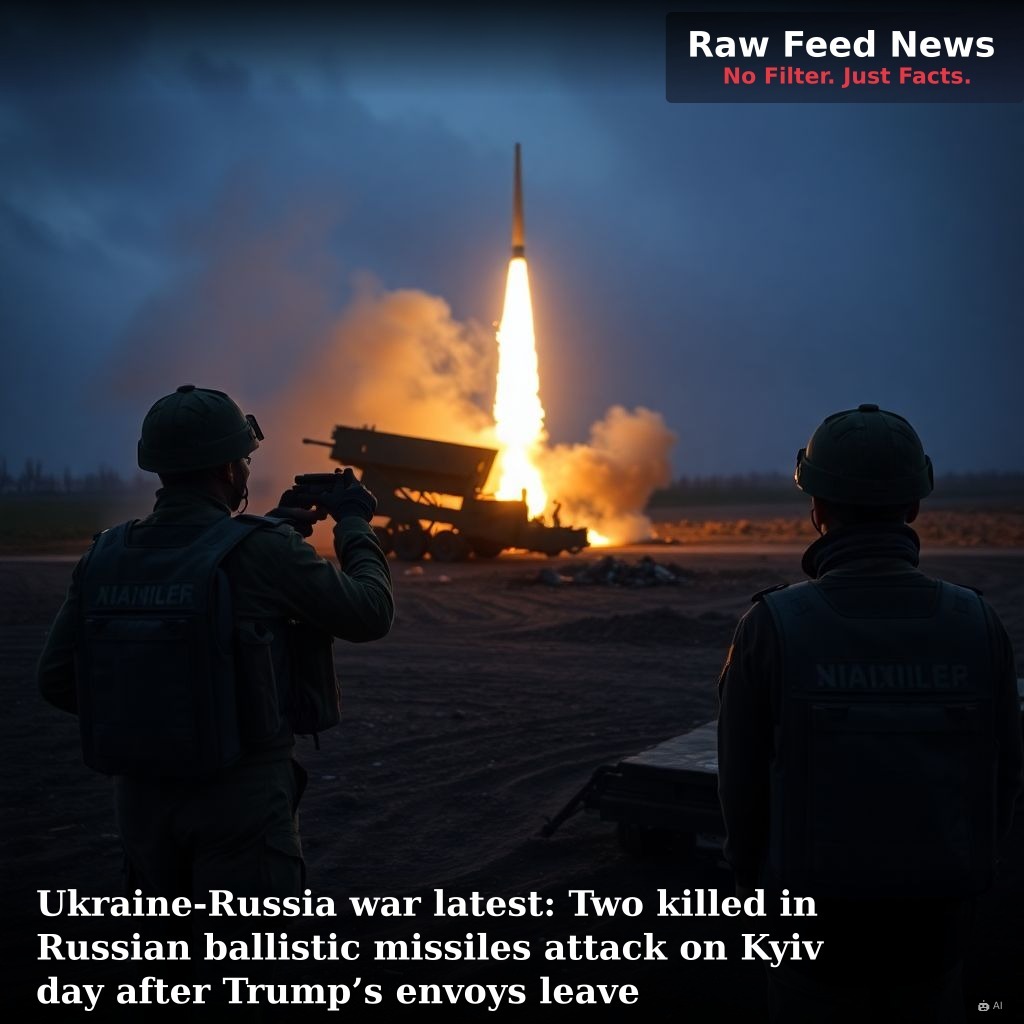
🔴 BREAKING: Two civilians killed as Russian ballistic missiles struck Kyiv, injuring several others. The attack came a day after US peace envoys held a press conference with President Zelensky, highlighting the fragile cease‑fire hopes. 🕐 05:02 UTC Read more: https://rawfeednews.com/post/mts7e9m2.html #Russia #Attack
0
0
2
0
Zelenskyy says North Korean ballistic missiles used by Russia in deadly attack in Ukraine Russian forces ‌killed six people early on Tuesday in an attack on the southeastern Ukrainian city of Zaporizhzhia that involved North Korean ballistic missiles, Ukrainian President Volodymyr Zelenskyy said. https://www.cbc.ca/news/world/russia-ukraine-war-1630-9.7302823?cmp=rss
0
0
0
0
Replying to
@GeraldKutney@noc.social #Climate #deniers don't deal in #science & #truth, & have NEVER done so - the #attack now is quite explicitly against science & truth themselves. If #politics won't do the trick ("climate #scientists are all #communists"), they'll resort to #religion ("climate scientists are all atheists"), & if THAT won't do, they'll resort to #magic, & reject the entire #scientific #enterprise, as it has been constructed since the 17th Century.
0
1
0
0

Metabase Patches Critical Zero-Day SQL Injection Exploited in the Wild

Metabase patched a critical zero-day SQL injection vulnerability (GHSA-vwf4-m7j8-wcjf, CVSS 10.0) that is actively exploited to gain administrator access and steal database credentials.

If you run self-hosted Metabase (version 1.58 or newer), this is urgent. Your Metabase is under attack. Update immediately to the patched release for your branch (0.58.24, 0.59.21, 0.60.17, 0.61.11, 0.62.9, or 0.63.5). if you can't patch right now, block all traffic to the /api/session/reset_password endpoint as a stopgap. After patching, check your application and ingress logs for a failed password-reset POST followed straight away by a successful /api/user/current request. Tf you see it, treat the instance as breached: clear the core_session table to log everyone out, rotate all connected database passwords, and check your admin accounts for anything you didn't create. #cybersecurity #infosec #attack #activeexploit https://beyondmachines.net/event_details/metabase-patches-critical-zero-day-sql-injection-exploited-in-the-wild-g-o-s-u-u/gD2P6Ple2L

0
0
0
0