Boosted by @trending@homestead.social
Never trust how you feel about your life on less than four hours of sleep.
 mastodon 4.7.3
💚 Friend
🏳️⚧ Trans, nonbinary, they/them
😷 Caring, careful
🔑 Passkeys & passwords
🧛🏻♀️ It’s not a phase
🦔 Speedrunner
RE: https://mastodon.social/@monkeydom/117382425456803989
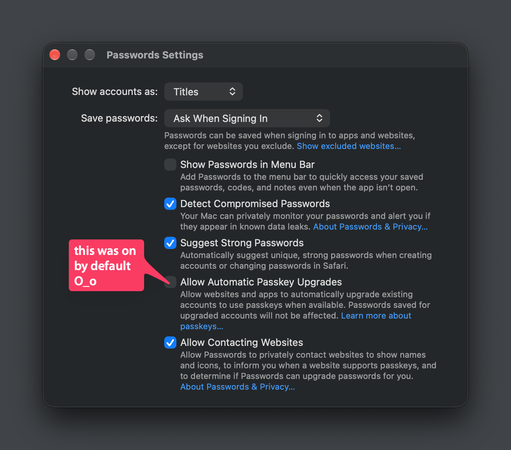
100% true. “Automatic passkey upgrades” is a feature of WebAuthn that allows for websites and apps to turn around and add a passkey to your saved account in a password manager right after you sign in with your password, assisted by that password manager.
Apple Passwords allows these upgrades by default (and tells users when it happens!) and I strongly believe it’s the right default. Why?
Passkeys make signing into accounts faster than passwords + traditional, phishable 2FA. If the user is already using the Passwords app for their password for an account, they’ve asked for the software to help them have a secure and smooth experience. Once someone has a passkey and starts using it in place of their password, one day, a website can start retiring passwords for users who are comfortable with that, which will finally deliver the phishing-resistance benefits of passkeys to accounts themselves.
Do not underestimate how many people are hurt by phishing every day. You might think that you’re safe, but nobody is truly safe from phishing until phishable sign-in and recovery mechanisms are removed from an account. This might not be achievable or desirable for some people, but people who use the computers and the internet should have a path to secure accounts.
I discuss this and more in this talk I gave: https://www.youtube.com/watch?v=yVadD-Lfrfk
Over the weekend, a person armed with a coding agent opened 479 pull requests against the Password Manager Resources project. As open source maintainers, what are we supposed to do about this?
All of the justification prose is written in clear AI dialect, with awkward phrasing. The normal benefit of the doubt I am able to give to contributors of the project, including that the changes they’re submitted are motivated by something that makes sense, are out the window.
Here’s the blog post I promised y’all on how I recommend switching password managers in 2026! It covers:
https://rmondello.com/2026/09/07/switching-password-managers-2026/
I’m not sure I’ve ever purchased an upgrade to software faster than with Soulver 4. Soulver helps me with so many little things in my life. https://soulver.app/
I think that Ky Decker’s blog post about “AI” and burnout (https://ky.fyi/posts/ai-burnout ) is worth reading. I am experiencing a bunch of similar feelings, and the paragraph starting with, “I encountered each of these scenarios over the past few years”, is a description of a living nightmare.
I am thankful to work with skilled and thoughtful people who are grappling with these things, and luckily, my passion for helping people is, so far, catapulting me through the moral injury of “Claude said this” and “Claude did that”.
Funny enough, today also marks my 14th year of working at Apple, adjusted for when I started my internship. Despite the broader industry getting more morally perilous, more full of shit, and less fun, I’m far from done trying to make authentication technologies more usable, delightful, and secure. Onward.
I love taking my socks off.
RE: @brandonbutler@mastodon.social
Today, you cannot save an Apple Account passkey to an arbitrary passkey manager. If that were to change, I will yell it from the rooftops, because it will eliminate a lot of confusion for folks, especially in the Apple Developer community and better model how passkeys should ideally work.
smol dog goes awoo (quietly)
Sunday night (derogatory)
“You saw [speedrunner] climb up those rocks? That’s a trick that we call ‘rock climbing’.”
I love Summer Games Done Quick. :)
I’ve been to lots of outdoor shows over the years, but this is the first with an AQI over 200. Thank goodness for N95s. (Death Cab, Philly.)
A small but important thing: The Passwords app on macOS 26.4 has a more “stable” main menu than in previous versions, with stronger adherence to the “Always show the same set of menu items” bit of the Human Interface Guidelines. If this was bothering you, it’s fixed now.
We been spending most our lives shitting with a tummy parasite.
I have a weird feeling that Graham Platner is going to fuck us all one day.
I don’t recommend using the word “passkey” to describe a credential saved to a hardware security key because the experience of having a phishing-resistant credential saved in a password manager is really, really different than having a dedicated hardware key. Radically different.
Which kind of person is a “Baby On Board” bumper sticker supposed to change the behavior of? People aren’t thoughtfully and defensively driving 100% of the time??
I wrote a shortcut to make it easier to look up credit card information saved for AutoFill in Wallet. Some of y’all might find it useful: https://rmondello.com/credit-cards-shortcut/
And don’t forget that if you tap on any text area on iPhone and iPad > AutoFill > Credit Card, you can fill details into fields.
“Meta builds AI version of Mark Zuckerberg to interact with staff”
oh yeah? well, they’re also building an AI to immortalize me. it just says “I think I’m missing some context” over and over again.
RE: @ultranurd@tacobelllabs.net
A TOTP provides very little value on top of a passkeys if it’s saved in the same place, with the same access control as your passkey. So in practice, no, you don’t need one. Importantly, note that a TOTP is just as easily phished as a password or an SMS one-time verification code.
Now, if your TOTP is stored and accessed separately, it may provide some value, but at that point, your threat model should be pretty advanced and off the beaten path for the risk you’re introducing of locking yourself out of an account.
okay, I’ll bite. Who is Charlie Kirk?
These sorts of tunnels are some of my favorite things.
From the UK’s “National Cyber Security “Centre””. https://www.ncsc.gov.uk/blogs/passkeys-are-more-secure-than-traditional-ways-to-log-in
all my Senate gone
I am unexpectedly finding myself in New Delhi, India a week from yesterday. There for a few days, then to Mumbai.
This is my first time visiting India. What should I do in these places? What things should I do to prepare for my visit?
“What’s the matter, trainer?”
I regret to inform y’all that zombo.com has been snatched up by someone.
The Brooklyn Paramount wouldn’t not let me in because I have a pair of over-the-ear headphones in a small bag, would they? Headphones aren’t listed as prohibited (well, I suppose they are “Audio recording devices”), but it would ruin my evening if I had to find a place to stash them. https://www.brooklynparamount.com/visit