Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Kim Zetter

@kimzetter@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Journalist - cybersecurity/national security. Author COUNTDOWN TO ZERO DAY: Stuxnet and the Launch of the World's First Digital Weapon. Speaker/Signal. Newsletter is called Zero Day. Find it here: https://www.zetter-zeroday.com/. Become a paid subscriber to help support my independent journalism.

12653 Followers
530 Following
13 Posts
Joined November 11, 2022
Book:
https://www.amazon.com/Countdown-Zero-Day-Stuxnet-Digital/dp/077043617X/ref=tmm_hrd_swatch_0?_encoding=UTF8&qid=&sr=
Zero Day news site:
https://www.zetter-zeroday.com/
Twitter:
https://twitter.com/KimZetter
Open post
Kim Zetter @kimzetter@infosec.exchange
· 1w ago
Boosted by @gvenema@fairmove.net
Exclusive: Israeli spyware maker Paragon positions itself as more responsible than its competitor NSO Group. But the company's new US CEO says in a candid interview that while they will cut off customers who misuse their spyware they have no ability to detect or investigate customer misuse, nor do they want that ability. Their tools also don't log customer activity by default. Though customers can configure some tools to do logging, Paragon doesn't have ability to force customers to provide those logs if allegations of abuse arise. Paragon says instead that it relies on third parties like Citizen Lab to detect abuse by its customers, and even praises Citizen Lab for uncovering suspected abuse in 2025, yet at the same time the company actively works to prevent Citizen Lab and others from detecting its spyware on infected systems, thus thwarting their ability to uncover abuse. Here's my story: https://www.wired.com/story/the-secrets-of-the-us-spyware-king/
The Secrets of a US Spyware King
WIRED

The Secrets of a US Spyware King

In an exclusive interview with WIRED, Paragon Solutions CEO Andrew Boyd reveals the limits of the company’s promise to keep bad actors from abusing its powerful espionage tool.

47
0
57
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 2mo ago
Exclusive: Guess who designed this year's Defcon badges? None other than famed hardware hacker Andrew "bunnie" Huang. The badges feature a new, secure and open-source chip that Huang created (the Baochip), which doubles as a security token after the con. Hardware hackers will love the specs @defcon@defcon.social https://www.wired.com/story/defcon-34-badge-baochip-andrew-bunnie-huang/
The New Defcon Badges Pack a Unique Open Source Chip That Doubles as a Security Key
WIRED

The New Defcon Badges Pack a Unique Open Source Chip That Doubles as a Security Key

Created by legendary hardware hacker Andrew “bunnie” Huang, the badges for this year’s famed security conference aim to push the boundaries of security and transparency.

77
1
40
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 7mo ago

When a hacker who goes by the names "Waifu" and "Judische" began posting death threats against security researcher Allison Nixon, she had no idea why he targeted her. So she set out to unmask him. The quest led her to uncover the identity of Connor Riley Moucka, a 25-yr-old Canadian who was ringleader of the infamous Snowflake/AT&T hacks as well as Cameron John Wagenius (aka Kiberphant0m
online), an active-duty US Army soldier, who both were arrested. Here's my story, as well as a free link below that.

https://www.technologyreview.com/2026/02/16/1132526/allison-nixon-hackers-security-researcher

https://archive.is/20260216131016/https://www.technologyreview.com/2026/02/16/1132526/allison-nixon-hackers-security-researcher

Hackers made death threats against this security researcher. Big mistake.
MIT Technology Review

Hackers made death threats against this security researcher. Big mistake.

Allison Nixon had helped arrest dozens of members of the Com, a loose affiliation of online groups responsible for violence and hacking campaigns. Then she became a target.

269
0
246
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 2mo ago
When Peter Stokes (Scattered Spider's "Bouquet") was arrested in Finland this month, people speculated that his real identity had been unmasked by Microsoft using the Windows GDID assigned to his computer. GDID *was* used to trace crimes to his computer, but Unit 221B's Allison Nixon tells me he had been unmasked in 2023, long before he committed the biggest crimes mentioned in his indictment. I spoke with her about tracking Stokes and other members of The Com, and why these cybercriminals brag about their crimes online and are so reckless about drawing attention to themselves and leaving a trail of evidence. We also talked about why, if Stokes had been identified in 2023, it took until 2026 to arrest him. https://www.zetter-zeroday.com/tracking-peter-stokes-and-the-com-allison-nixon-and-her-work-unmasking-cybercriminals/
Tracking Peter Stokes and The Com: Allison Nixon and Her Work Unmasking Cybercriminals
ZERO DAY

Tracking Peter Stokes and The Com: Allison Nixon and Her Work Unmasking Cybercriminals

Any time a member of The Com gets arrested, there’s a good chance Allison Nixon played a role in it. Nixon is chief research officer at the cyber investigations firm Unit 221B, named after the apartment number of famed literary detective Sherlock Holmes. She has built her career tracking

40
6
21
2
Open post
Kim Zetter @kimzetter@infosec.exchange
· 5mo ago

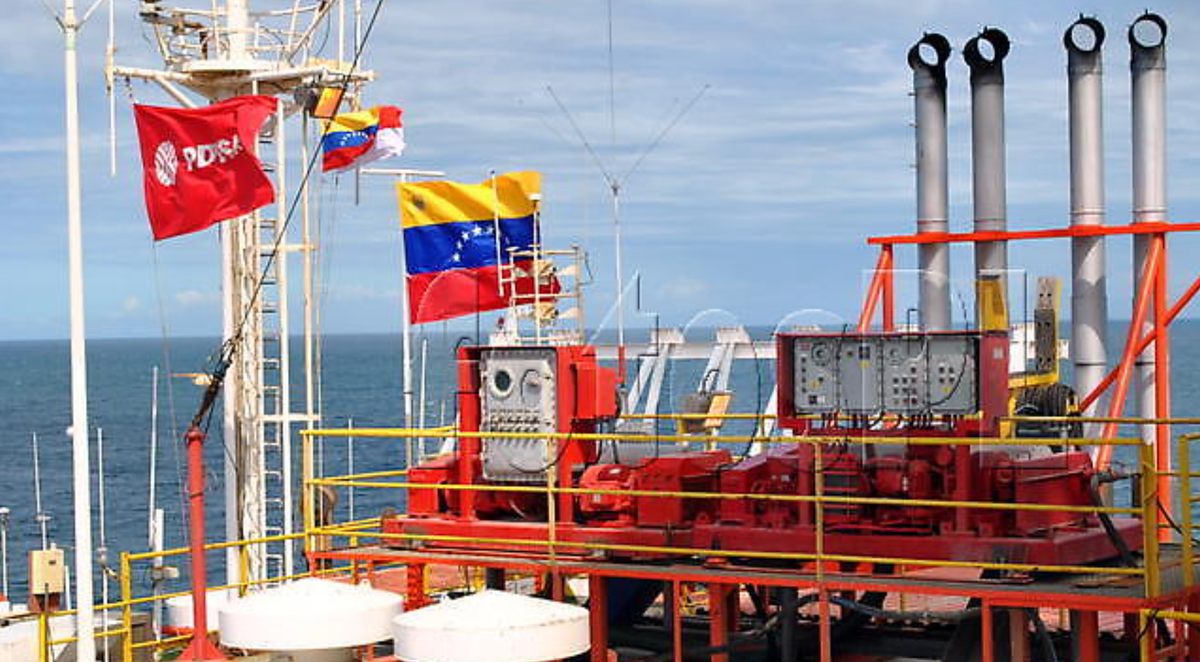
The mystery around a cyberattack against Venezuela's state-run oil company last December deepens with the discovery this week of a "highly destructive" wiper that may have been used in the attack. Previous reports had indicated that the December attack was a ransomware incident. But the wipr found this week was compiled last September, and hard-coded into it is the domain for Petróleos de Venezuela (PDVSA) , the state-run oil company. The hard-coded domain means the attackers had designed their precision weapon to only destroy data on the oil company's systems, not on any other system outside the company's domain. My story is below. Please consider becoming a paid subscriber if you like my work.

https://www.zetter-zeroday.com/hwiper-targeting-venezuelas-state-oil-company-discovered/

Mystery Around Venezuelan Cyberattack Deepens, with New Discovery of "Highly Destructive" Wiper
ZERO DAY

Mystery Around Venezuelan Cyberattack Deepens, with New Discovery of "Highly Destructive" Wiper

The mystery around a cyberattack that struck Venezuela's state-owned oil company in December is growing, following an announcement by researchers this week that they had discovered a "highly destructive" wiper program that appears to have been designed to target the oil company and may have been used in

79
8
78
1
Open post
Kim Zetter @kimzetter@infosec.exchange
· 6mo ago

Former Trenchant exec who stole exploits from his employer and sold them to a Russian broker says he was suffering depression & money troubles when he decided to sell the exploits. Also, new info reveals the nature of the work he did for an Australian intel agency before joining Trenchant. My story is linked below. Please consider becoming a paid subscriber if you like my work on this piece. It's 4,000 words and I'm making it available for free to everyone. But I can only do that because some subscribers have generously become paid subscribers.

https://www.zetter-zeroday.com/trenchant-exec-says-he-had-depression-money-troubles-when-he-decided-to-sell-zero-days-to-russian-buyer-also-new-info-reveals-nature-of-his-work-for-australian-intelligence-agency/?ref=zero-day-newsletter

The Sad Decline of Trenchant Exec Who Had Everything, Before Deciding to Steal and Sell Zero Days to Russian Buyer
ZERO DAY

The Sad Decline of Trenchant Exec Who Had Everything, Before Deciding to Steal and Sell Zero Days to Russian Buyer

Peter Joseph Williams, a former L3 Trenchant executive recently convicted of secretly selling zero-day exploits to a Russian broker, says he was suffering anxiety, burnout, years of depression, and financial difficulties when he decided to steal exploits from his US employer and sell them to the Russian buyer. Williams,

21
1
17
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 7mo ago

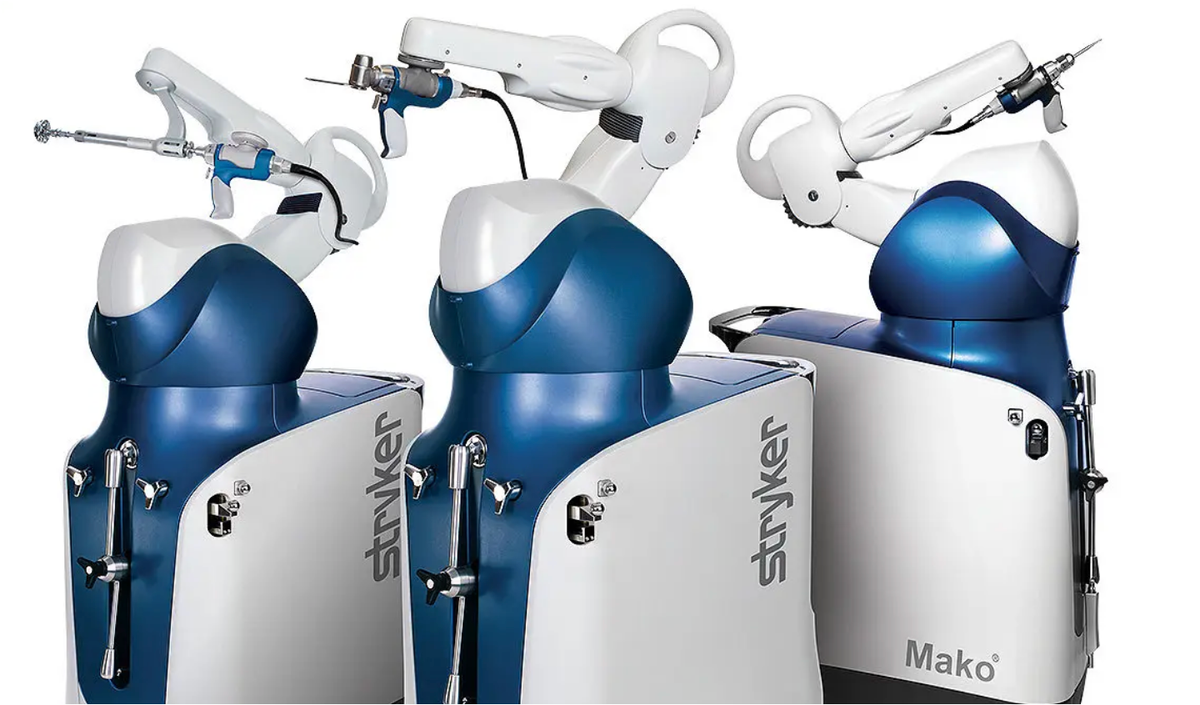
Iranian hacktivists hit US medical device maker Stryker with a "severe" attack that wiped systems and shut down global operations for the company. The hacktivist group, Handala, claim they hit the company in retaliation for the US bombing of a girls' school in Iran and that they struck more than 200,000 of Stryker's servers, systems and devices and remotely wiped many of them. https://www.zetter-zeroday.com/iranian-hacktivists-strike-medical-device-maker-stryker-in-severe-attack-that-wiped-systems/

Iranian Hacktivists Strike Medical Device Maker Stryker in "Severe" Attack that Wiped Systems
ZERO DAY

Iranian Hacktivists Strike Medical Device Maker Stryker in "Severe" Attack that Wiped Systems

Stryker, a leading maker of medical devices, was hit early this morning with a cyberattack that has reportedly caused the company's systems to shut down globally. The company has acknowledged the attack and called it "severe" in communication with employees. A known Iranian hacktivist group named Handala posted messages

26
2
27
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 2mo ago
Replying to on tech.lgbt
@gwen@tech.lgbt @xethos@mastodon.xethos.net @DaveMWilburn@infosec.exchange If you think that the only thing that members of The Com are doing is "doing damage to capitalist constructs" then you have very little understanding of what the members do. I included a link in this pice to a more lengthy story I published about Nixon and The Com earlier this year. You might find it more enlightening because it goes int greater detail about the violence they engage in - inciting mass school shootings, targeting young girls with sextortion, encouraging youths to kill their pets or harm random elderly people. The financial crimes are only one part of their activity.
3
4
1
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 8mo ago
The hackers behind a cyberattack that targeted Poland's grid infrastructure in December disabled communication devices for at least 30 sites across a number of energy facilities in different parts of the country. The attackers were able to render the communication devices --known as remote terminal units or RTUs -- not only inoperable but also unrecoverable. This new information, combined with my story last week that the attack used a wiper aimed at erasing IT systems, shows that the attack was a multi-pronged operation targeting both IT and OT systems. Nonetheless, researchers are calling this an opportunistic attack rather than a fully planned one https://www.zetter-zeroday.com/attack-against-polands-grid-disrupted-communication-devices-at-about-30-sites/
Attack Against Poland's Grid Disrupted Communication Devices at About 30 Sites
ZERO DAY

Attack Against Poland's Grid Disrupted Communication Devices at About 30 Sites

The hackers behind a cyberattack that targeted Poland's grid infrastructure in December disabled communication devices for at least 30 sites across a number of energy facilities in different parts of the country.  The hackers succeeded in disabling the communication systems, known as remote terminal units or RTUs, that are

14
0
20
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 21mo ago

Last month as drones over NY/NJ made headlines, a radiation-monitoring site reported spikes in radiation in NY, seemingly supporting a theory that the drones were tracking a dirty bomb on the loose there. Only the spikes were fake. I wrote about how the fake info got reported and how it spread on social media

https://www.zetter-zeroday.com/anatomy-of-a-nuclear-scare/

Anatomy of a Nuclear Scare
ZERO DAY

Anatomy of a Nuclear Scare

How fake radiation readings in New York and New Jersey, coupled with a mysterious drone swarm, fueled a nuclear scare and became a harbinger for things to come The ongoing mystery around a New Jersey drone swarm ignited a number of theories last month about who owned the drones and

67
2
53
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 2mo ago
Replying to
re: Physical abuse, 4th paragraph
@xethos@mastodon.xethos.net Apologies for including you in that reply. I should have just responded directly to the other poster
1
0
0
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 46mo ago

Regarding the malicious drivers getting signed, Microsoft says activity was limited to the abuse of several developer program accounts and that no compromise has been identified.

"We’ve suspended the partners' seller accounts..."

(hat tip to @ryanaraine@infosec.exchange for pointing to Microsoft's statement)

https://msrc.microsoft.com/update-guide/vulnerability/ADV220005

msrc.microsoft.com

Security Update Guide - Microsoft Security Response Center

17
0
8
0
Open post
Kim Zetter @kimzetter@infosec.exchange
· 2mo ago
Replying to
@gwen@tech.lgbt I would say that's my fault. I edited the Q&A because it was too long. She did speak more extensively about this and talked about the need for mental health professionals and also for parents to be engaging with their children to understand what they are doing online. But unfortunately, many members of The Com come from homes where parental engagement is either nonexistent or toxic, which is part of the reason their children seek community and understanding onilne.
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 09:39:17 UTC