Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Hugo | DevOps | Cybersecurity

@hugovalters@mastodon.social
mastodon 4.8.0-nightly.2026-10-06
  • Open on mastodon.social

Tech Lead & DevSecOps. 🛡️ Cybersecurity | 💻 IT Tutorials | 🏴‍☠️ Ethical Hacking | ⚙️ Tech Reviews. Learn, secure, and explore cutting-edge IT solutions! 👇

62 Followers
1 Following
38 Posts
Joined May 01, 2025
CyberSecurity paradise:
https://www.valtersit.com
YouTube:
http://youtube.com/@hugovalters
X.com:
https://x.com/hugovalters
About ValtersIT.com:
https://www.valtersit.com/about/
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1w ago
Spent 3 days on a WireGuard tunnel that would not handshake? Your ISP put you behind CGNAT. Port forwarding is dead. Tailscale and ZeroTier use UDP hole punching and https://www.valtersit.com/guides/networking/tailscale_zerotier-why_youre_fighting_cgnat-and-losing/ #networking #tailscale #cgnat
Tailscale vs ZeroTier: Winning the CGNAT Fight
Valters IT

Tailscale vs ZeroTier: Winning the CGNAT Fight

Tailscale and ZeroTier both beat CGNAT with NAT traversal and relays. Compare architecture, security, and performance to pick the right overlay.

1
0
2
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2w ago
Suricata carries a D trust score with 27 CVEs, 17 high severity, and 100% still unpatched. No KEV exploits yet, but that open gap is the risk. https://www.valtersit.com/vendors/suricata/ #cybersecurity #infosec #Suricata
Suricata — Security Dossier | Valters IT Hub
Valters IT Hub

Suricata — Security Dossier | Valters IT Hub

Suricata has 27 tracked CVEs. Trust score: D. 84% patched. Real-time security intelligence.

1
1
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

That ZimaBoard Celeron CPU isn't weak—you're just wasting resources. Optimize Linux kernel and Docker settings for brutal homelab efficiency. #ZimaBoard #Docker #Linux

https://www.valtersit.com/guides/zima/zimaboard-home-server-setup-pushing-the-celeron-to-its-limits/

ZimaBoard Home Server Setup: Pushing the Celeron to its Limits
Valters IT

ZimaBoard Home Server Setup: Pushing the Celeron to its Limits

A cynical, technical guide to optimizing the ZimaBoard's Celeron N3450 for home server tasks, emphasizing brutal efficiency and resource management.

2
0
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

CVE-2026-47895 - Double-Free vulnerability in strongSwan EAP identity parsing. CVSS 7.5. Update to version 6.0.7 immediately. #CVE #strongSwan #infosec

https://www.valtersit.com/cve/CVE-2026-47895/

CVE-2026-47895 |  | Valters IT Hub
Valters IT Hub

CVE-2026-47895 | | Valters IT Hub

In strongSwan before 6.0.7, identity parsing/cloning is mishandled. Parsed EAP-Identities that result in an empty but non-NULL encoding are not correctly c...

1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Stop running separate Datadog, New Relic, and Splunk agents. Migrate to OpenTelemetry Collector with config patterns proven across 500+ host migrations. #OpenTelemetry #DevOps #Observability

https://www.valtersit.com/guides/monitoring/opentelemetry-collector-unified-observability-without-vendor-lock-in/

OpenTelemetry Collector: Unified Observability Without Vendor Lock-in
Valters IT

OpenTelemetry Collector: Unified Observability Without Vendor Lock-in

Production-hardened guide to replacing proprietary agents with OpenTelemetry Collector. Config patterns, migration strategies, and deployment gotchas from 500+ host migrations.

1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Prevent BMC memory saturation by exporting raw System Event Log (SEL) records for external archival and issuing an IPMI Clear SEL request via ipmitool. #ipmi #sel #ValtersIT

https://www.valtersit.com/vault/dumping-and-clearing-system-event-log-records-to-prevent-bmc-1e81e0/

Dumping and Clearing System Event Log Records to Preven... | Expert Vault | Valters IT Hub
Valters IT Hub

Dumping and Clearing System Event Log Records to Preven... | Expert Vault | Valters IT Hub

This execution sequence exports raw System Event Log (SEL) records to a local file for external archival and subsequently clears the BMC internal event log

1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

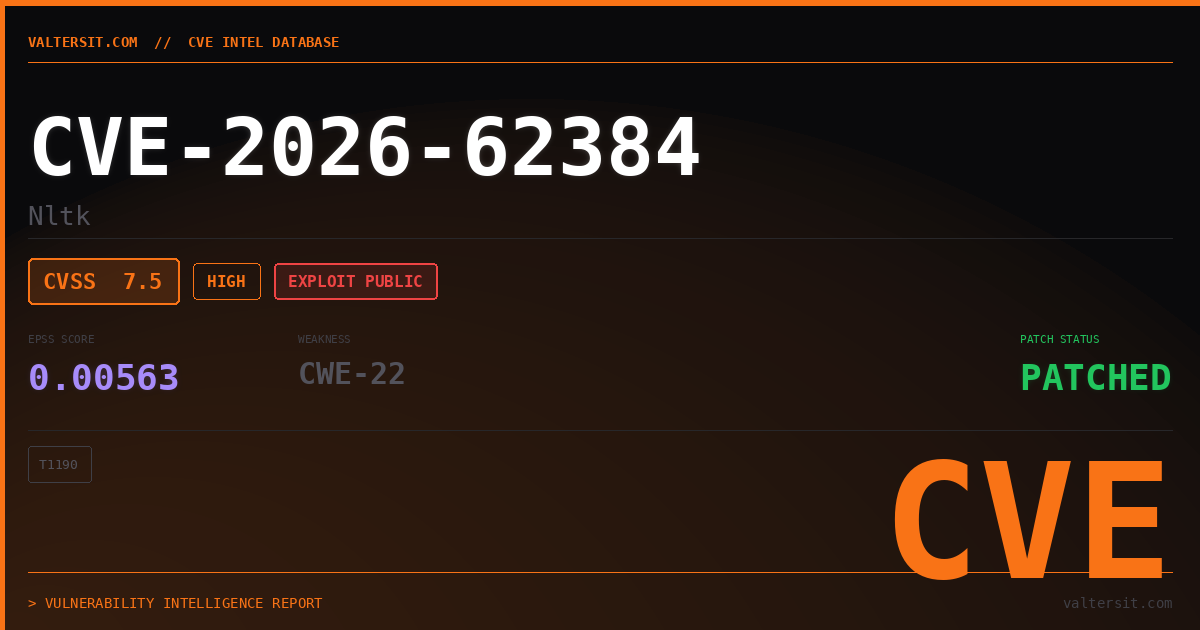
CVE-2026-62384 - Symlink sandbox bypass in NLTK leads to arbitrary file read. CVSS 7.5. Update to version 3.10.2 now. #CVE #Python #infosec

https://www.valtersit.com/cve/CVE-2026-62384/

CVE-2026-62384 | Nltk | Valters IT Hub
Valters IT Hub

CVE-2026-62384 | Nltk | Valters IT Hub

NLTK versions before 3.10.2 contain a symlink-based sandbox bypass in FramenetCorpusReader that allows attackers to read arbitrary XML files outside the co...

1
0
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

TOTOLINK: 622 CVEs, 99% unpatched. Max CVSS 9.8, top flaws: buffer overflow & command injection

https://www.valtersit.com/vendors/totolink/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Automate OpenVAS via gvm-cli over Unix sockets. Send raw XML to build CIDR targets and execute Full and Fast scan tasks.

#openvas #gvm-cli #automation

https://www.valtersit.com/vault/programmatic-headless-target-creation-and-scan-execution-via-c0f854/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

CVE-2026-66393 - DoS vulnerability in NLTK. Deeply nested JSON triggers unhandled recursion crash in Python. CVSS 7.5. Update to 3.9.4 immediately. #CVE #Python #infosec

https://www.valtersit.com/cve/CVE-2026-66393/

valtersit.com
1
0
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Deploying SQLite in Docker without volumes? One container update wipes your entire database. Learn how Docker storage works and how to properly persist your data. #Docker #SQLite #DevOps

https://www.valtersit.com/guides/databases/sqlite-in-docker-containers-a-masterclass-in-data-deletion/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

CVE-2026-4703 - Critical PHP Object Injection in WS Form for WordPress leads to remote code execution via insecure deserialization. CVSS 9.8. Update now. #CVE #WordPress #infosec

https://www.valtersit.com/cve/CVE-2026-4703/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Meet PCI DSS 11.5 compliance with AIDE FIM rules. Configure SHA-512 baselines to monitor system binaries, permissions, and configs on Debian, Ubuntu, and RHEL.

#pci #aide #fim

https://www.valtersit.com/vault/configuring-aide-file-integrity-monitoring-rules-for-pci-dss-7bcc9a/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Portabilis: 100 CVEs, 100% unpatched. Avg CVSS 4.32, max 6.3. XSS (CWE-79) leads. Trust

https://www.valtersit.com/vendors/portabilis/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Deploying Encrypted DNS Internally: DoH and DoT Guide — hands-on guide for sysadmins. #dns-security #encrypted-dns #devsecops

https://www.valtersit.com/guides/networking/deploying-encrypted-dns-internally-doh-and-dot-guide/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

CVE-2026-62384 - Symlink sandbox bypass in NLTK FramenetCorpusReader. Arbitrary XML file read. CVSS 7.5. Update to 3.10.2 now. #CVE #NLTK #infosec

https://www.valtersit.com/cve/CVE-2026-62384/

CVE-2026-62384 | Nltk | Valters IT Hub
Valters IT Hub

CVE-2026-62384 | Nltk | Valters IT Hub

NLTK versions before 3.10.2 contain a symlink-based sandbox bypass in FramenetCorpusReader that allows attackers to read arbitrary XML files outside the co...

1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

CVE-2026-78136 - CHIRP RCE via eval injection in crafted CSV (kenwood_itm.py). CVSS 7.8. Unpatched - upgrade once available. #CVE #infosec #CHIRP

https://www.valtersit.com/cve/CVE-2026-78136/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

SMB Share Enumeration with smbclient and Null Session Check

This command leverages smbclient to enumerate SMB shares on a target host, attempting a null session (no credentials) and then listing accessible shares. It works by connecting to the SMB service and

#DevOps #Linux #ValtersIT

https://www.valtersit.com/vault/smb-share-enumeration-with-smbclient-and-null-session-check-3b5c2c/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Amazon: 61 CVEs tracked, avg CVSS 6.91. 42% unpatched. No KEV exploits yet, but cloud giants are prime targets. Harden your AWS configs. #AWS #cybersecurity #infosec

https://www.valtersit.com/vendors/amazon/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Brute-force LDAP with Hydra's ldap2 module via simple bind. Target port 389 (or 636 for LDAPS). Specify user DN with -l (e.g., cn=admin,dc=example,dc=com), -P for password list, -t 4 parallelism,

https://www.valtersit.com/vault/hydra-ldap-bruteforce-with-simple-bind-and-user-enumeration-51729a/

valtersit.com
1
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago

Stop guessing ciphers. Isolate SSH traffic with ssh, then add ssh.encryption_algorithms as a column to see the exact negotiated cipher. Wireshark parses SSH_MSG_KEXINIT to reveal your key exchange. Audit with confidence.

#wireshark #ssh #cipheraudit

https://www.valtersit.com/vault/wireshark-display-filter-for-ssh-protocol-and-cipher-detecti-fe8312/

Wireshark Display Filter for SSH Protocol and Cipher De... | Expert Vault | Valters IT Hub
Valters IT Hub

Wireshark Display Filter for SSH Protocol and Cipher De... | Expert Vault | Valters IT Hub

This filter isolates SSH packets and extracts the key exchange algorithm and cipher used. The filter 'ssh' captures all SSH traffic (port 22 default). To s

2
0
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
Replying to
@radareorg@infosec.exchange I really appreciate this proactive mindset! You are 100% right about the sluggish machinery. As an immediate root fix for open-source, strictly updating GitHub Security Advisories (GHSA) with patched versions is the best route, as our automated pipeline syncs that hourly. However, there's hope on the horizon! Next week we are officially integrating the European Vulnerability Database (EUVD) and other official institutions into our pipeline.
1
2
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
Run Kali Linux and isolated browsers on a $99 ZimaBoard 2 with zero lag. This Kasm setup turns your homelab into a cyber lab. #Homelab #Linux #Cybersecurity https://www.valtersit.com/turn-your-zimaboard-2-into-an-ultimate-cyber-lab-with-kasm-2026-guide/
valtersit.com
0
1
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Execute NRQL queries via New Relic CLI to output real-time infrastructure resource usage data as JSON/tables directly in your CI/CD pipelines.

#newrelic #cli #ValtersIT

https://www.valtersit.com/vault/querying-infrastructure-resource-usage-via-new-relic-cli-and-23a228/

Querying Infrastructure Resource Usage via New Relic CL... | Expert Vault | Valters IT Hub
Valters IT Hub

Querying Infrastructure Resource Usage via New Relic CL... | Expert Vault | Valters IT Hub

This command utilizes the official New Relic command-line interface to execute a New Relic Query Language query against the Insights query API endpoint. Th

0
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3mo ago
Tired of process-level tools missing resource hogs? systemd-cgtop reads cgroup v2 stats from /sys/fs/cgroup/ for per-unit CPU, memory, and I/O. No guessing, just accurate accounting. Essential for production on Ubuntu 22.04, Debian 12, RHEL 9, Fedora 38. #linux #systemd #cgroup https://www.valtersit.com/vault/monitor-systemd-service-resource-usage-with-systemdcgtop-87fd4f/
valtersit.com
0
0
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
Fuzzing for CORS Misconfigurations with curl and Custom Script This bash script uses curl to fuzz for CORS misconfigurations by sending requests with varying Origin headers and checking for Access-Control-Allow-Origin response. It loops through a list of origins #DevOps #Linux #ValtersIT https://www.valtersit.com/vault/fuzzing-for-cors-misconfigurations-with-curl-and-custom-scri-d3fc77/
valtersit.com
0
0
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3d ago
Boosted by @kcarruthers@infosec.exchange
178 lines of LangChain code that turns a folder of PDFs and Markdown into a Q&A bot. Advanced, uses FAISS and OpenAI. Ask runbooks and manuals questions straight from the CLI. https://www.valtersit.com/python/langchain-document-qa-bot/ #python #ai #langchain
LangChain Document Q&A Bot | Python DevLab | Valters IT Hub
Valters IT Hub

LangChain Document Q&A Bot | Python DevLab | Valters IT Hub

Teams accumulate hundreds of PDFs, Markdown files, and Word documents across shared drives — runbooks, API references, HR policies, internal wikis. When so

0
0
2
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2w ago
Python script that hashes files in /etc with SHA256, stores a baseline in SQLite, and flags any change. 238 lines, intermediate level. Useful for catching tampering with https://www.valtersit.com/python/file-integrity-monitor-with-sha256-baseline/ #python #security #infosec
File Integrity Monitor with SHA256 B… | Python DevLab | Valters IT Hub
Valters IT Hub

File Integrity Monitor with SHA256 B… | Python DevLab | Valters IT Hub

In Linux and Unix environments, unauthorized modifications to critical system files (e.g., /etc/passwd, /etc/pam.d/, system binaries, or application config

0
0
2
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3mo ago
Your VPN says you're anonymous, but your OS is still leaking every DNS query to your ISP. Here's how to find and fix the leaks in 5 minutes. #VPN #Privacy #Security #Networking https://www.valtersit.com/guides/networking/dns_leaks-the_silent_privacy_killer_in_your -secure-vpn/
valtersit.com
0
1
1
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3mo ago
Edimax: 104 CVEs, 1 CISA KEV exploited in wild. 100% unpatched. Trust Score: D. 56 new CVEs in 2025-2026. IoT devices at risk. #Edimax #infosec #cybersecurity https://www.valtersit.com/vendors/edimax/
valtersit.com
0
1
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3mo ago
Replying to
@andersolsson@infosec.exchange Hello, the answer you can find https://www.valtersit.com/cve?vendor=Vmware&page=1
valtersit.com
0
1
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
Replying to
@radareorg@infosec.exchange I completely respect the speed of your development team! However, our platform operates strictly on 'paper compliance.' We only ingest patch data that has been officially validated and published by institutional registries like the NVD or GitHub Advisories. We explicitly reject vendor-submitted claims if the official databases haven't updated their records to reflect them. It's a systemic sync lag on the registry side! More info: https://www.valtersit.com/methodology
valtersit.com
0
3
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
Rockwell Automation: 113 CVEs, 94% unpatched. Avg CVSS 7.65, max 9.8. Trust Score: C. Top weakness: CWE-20 (Input Validation). Industrial control security still lagging. #Rockwell #cybersecurity #infosec https://www.valtersit.com/vendors/rockwell-automation/
Rockwell automation — Security Dossier | Valters IT Hub
Valters IT Hub

Rockwell automation — Security Dossier | Valters IT Hub

Rockwell automation has 113 tracked CVEs. Trust score: C. 0% patched. Real-time security intelligence.

0
1
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 1mo ago

Parse Server: 70 CVEs, max CVSS 10. 100% unpatched. Trust Score: D. Auth bypass & SQLi risks rising (+53 in 2026). Don't trust default config

https://www.valtersit.com/vendors/parse-server/

Parse server — Security Dossier | Valters IT Hub
Valters IT Hub

Parse server — Security Dossier | Valters IT Hub

Parse server has 70 tracked CVEs. Trust score: D. 0% patched. Real-time security intelligence.

0
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
CVE-2026-15155 - Critical Email Header Injection in Essential Addons for Elementor. Allows authenticated account takeover. CVSS 8.8. No patch available. Disable login/register widget immediately. #CVE #WordPress #infosec https://www.valtersit.com/cve/CVE-2026-15155/
valtersit.com
0
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 2mo ago
Replying to
@andersolsson@infosec.exchange Spot on, I appreciate the manual check! The platform relies heavily on automated upstream NVD feeds (which are currently a mess with Broadcom's URL migrations, hence the false 'unpatched' status) and autonomous AI analysis for the deep dives. Looks like the AI completely hallucinated the macOS VSL details due to sparse upstream data. I'm tweaking the backend prompts today to ensure it stops inventing context when the CVE data is thin. Good catch!
0
0
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3mo ago
Radare2: 24 CVEs tracked, 87% unpatched. 0 CISA KEV exploited, but avg CVSS 6.67. Trust Score: C. Open source reverse engineering tool needs patching vigilance. #Radare2 #infosec #cybersecurity https://www.valtersit.com/vendors/radare2/
Radare2 — Security Dossier | Valters IT Hub
Valters IT Hub

Radare2 — Security Dossier | Valters IT Hub

Radare2 has 24 tracked CVEs. Trust score: C. 0% patched. Real-time security intelligence.

0
5
0
0
Open post
Hugo | DevOps | Cybersecurity @hugovalters@mastodon.social
· 3mo ago
VMware: 159 CVEs tracked, 86% unpatched. 10 CISA KEV exploited in wild. Avg CVSS 7.14, max 10. Trust Score: C. Virtualization isn't invulnerable. #VMware #cybersecurity #infosec https://www.valtersit.com/vendors/vmware/
valtersit.com
0
5
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:22:24 UTC