Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

JayeLTee

@JayeLTee@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Leaks, leaks everywhere.

344 Followers
44 Following
7 Posts
Joined December 19, 2023
Index of my public finds:
https://jltee.substack.com/p/the-hub-of-stupi-misconfigs-index
Open post
JayeLTee @JayeLTee@infosec.exchange
· 15mo ago

I received an email earlier this week from EA asking if I wanted to be added to a public acknowledgement page they were creating for individuals who responsibly disclosed vulnerabilities to them.

For all the shit people give EA, of the 100+ companies I contacted in the last two years, they were the only company I would say had a decent incident response.

They fixed the issue within 12 hours after validating it as critical, and proactively provided me multiple updates over time.

When the IR was done on their side, they reached out again with some more information about the potential impact if the issue hadn't been solved quickly, and also offered me a reward.

I did not have to keep chasing anyone for updates, I wasn't asked for non-disclosure, or offered money in exchange for it, and people replied instead of ignoring me.

I wasn't blamed for their mistake, either, or reported to the authorities.

Unfortunately, at least one or multiple of the things mentioned above are present in most of my other incidents reported; it's a real shit show out there.

#cybersecurity #infosec #responsibledisclosure #vulnerability #ea #electronicarts
infosec.exchange

Infosec Exchange

219
12
111
0
Open post
JayeLTee @JayeLTee@infosec.exchange
· 15mo ago

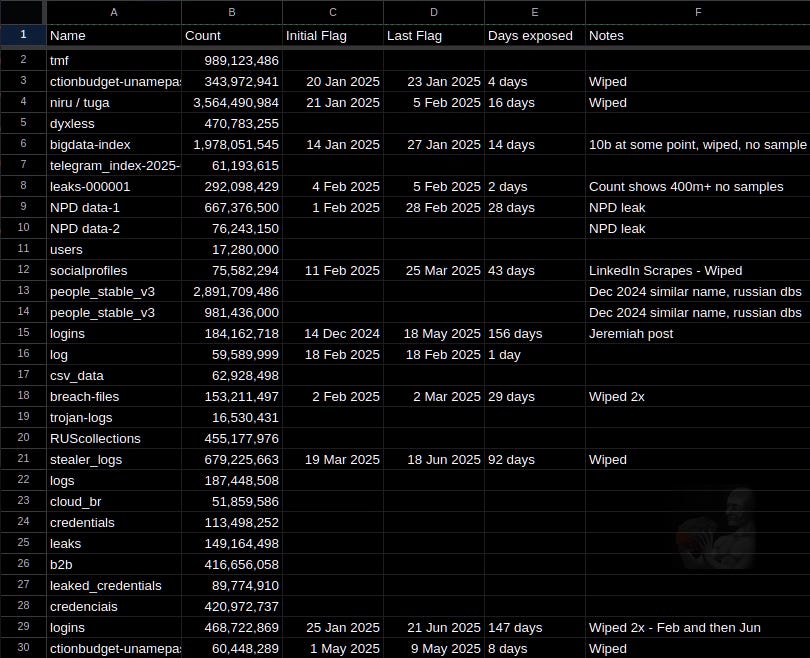
Cybernews made a post about a "record-breaking data breach", one they created themselves in their head.

They seem to keep updating their post with more information, and it's now a mix of false claims and contradictions.

I called @Scary@infosec.exchange and we went digging through our logs to show you just how much effort they put into researching for that article and how much of it is overblown.

https://jltee.substack.com/p/fact-checking-claims-by-cybernews

#cybersecurity #infosec #infostealer #cybernews #data #databreach #news

Fact-Checking Claims By Cybernews: The 16 Billion Record Data Breach That Wasn't
jltee.substack.com

Fact-Checking Claims By Cybernews: The 16 Billion Record Data Breach That Wasn't

From dumps with no login credentials at all, to direct connections to txtbase leaks from Telegram and old breaches, Cybernews tried to pass this as new and unseen, but data says otherwise.

20
0
14
0
Open post
JayeLTee @JayeLTee@infosec.exchange
· 11mo ago

@cR0w@infosec.exchange Lost count of the amount of times I told a company about an exposed endpoint they had no idea they even owned. Sometimes it took months for them to even get access to it and fix the issue 😂

5
0
0
0
Open post
JayeLTee @JayeLTee@infosec.exchange
· 15mo ago
Replying to
@adamshostack@infosec.exchange Oh, I did, yeah. Their response was so different from everything else I dealt with that I had to give them some positive feedback about it. Even official bug bounty programs for billion-dollar companies, I have to deal with one message in two months, and it's the company asking me how to connect to their server :blobshrug:
6
2
1
0
Open post
JayeLTee @JayeLTee@infosec.exchange
· 15mo ago
Replying to on infosec.exchange
@masek@infosec.exchange Thanks to you and @PogoWasRight@infosec.exchange for all the help with this and other incidents :ablobcatheart: Without that help, it would be a way bigger challenge to get this closed, as any time I try to contact any agency or LE in the US, I just get ignored :blobshrug:
4
1
2
0
Open post
JayeLTee @JayeLTee@infosec.exchange
· 14mo ago

@cR0w@infosec.exchange @reverseics@infosec.exchange

I would add to be aware of the tricks and bullshit this companies try to pull in regards to disclosures too.

I had a company try to add me to a private, invite only, no disclosure VDP for simply filling a form in their website.

Edit: This billion dollar company has a paid bug bounty program, but the form in their website linked to something else instead though :)

https://jltee.substack.com/p/risk-a-ban-by-alerting-100000-people

Risk a ban by alerting 100,000 people their data was exposed? It was an easy choice.
jltee.substack.com

Risk a ban by alerting 100,000 people their data was exposed? It was an easy choice.

I got put into a Private, invite-only, Non-Disclosure Program by submitting a form to Newfold, you get to read this post instead.

2
0
0
0
Open post
JayeLTee @JayeLTee@infosec.exchange
· 13mo ago

@giaco@geraffel.social @masek@infosec.exchange

Their reply to the report was asking for my full dox basically, I also followed up either way with more information and got ignored :blobshrug:

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 14:58:31 UTC