#threatdetection

6 posts · Last used 9d

#BSidesLuxembourg2026 recording: "𝐌𝐚𝐬𝐭𝐞𝐫𝐢𝐧𝐠 𝐈𝐧𝐜𝐢𝐝𝐞𝐧𝐭 𝐑𝐞𝐬𝐩𝐨𝐧𝐬𝐞 𝐖𝐢𝐭𝐡 𝐊𝐚𝐧𝐯𝐚𝐬" by Ardit Beu https://www.linkedin.com/in/ardit-beu-309165185/ Find all the talks from this track/village here: https://archive.org/details/BSidesLuxembourg2026/d2+t2+01+Mastering+Incident+Response+With+Kanvas+-+Ardit+Beu.mkv #BSidesLuxembourg2026 #BSidesLux #cybersecurity #infosec #threatdetection #incidentresponse #hacking
2
0
1
0
IDS evasion often starts with traffic analysis. If your detection only watches signatures, attackers blend in with jitter, fragmentation, and protocol tunneling. Tip: baseline east-west flows, not just perimeter. Lateral movement hides in normal SMB/RDP. Practical labs: bug404found https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=en #cybersec #infosec #security #netsec #threatdetection #blueteam
1
0
0
0
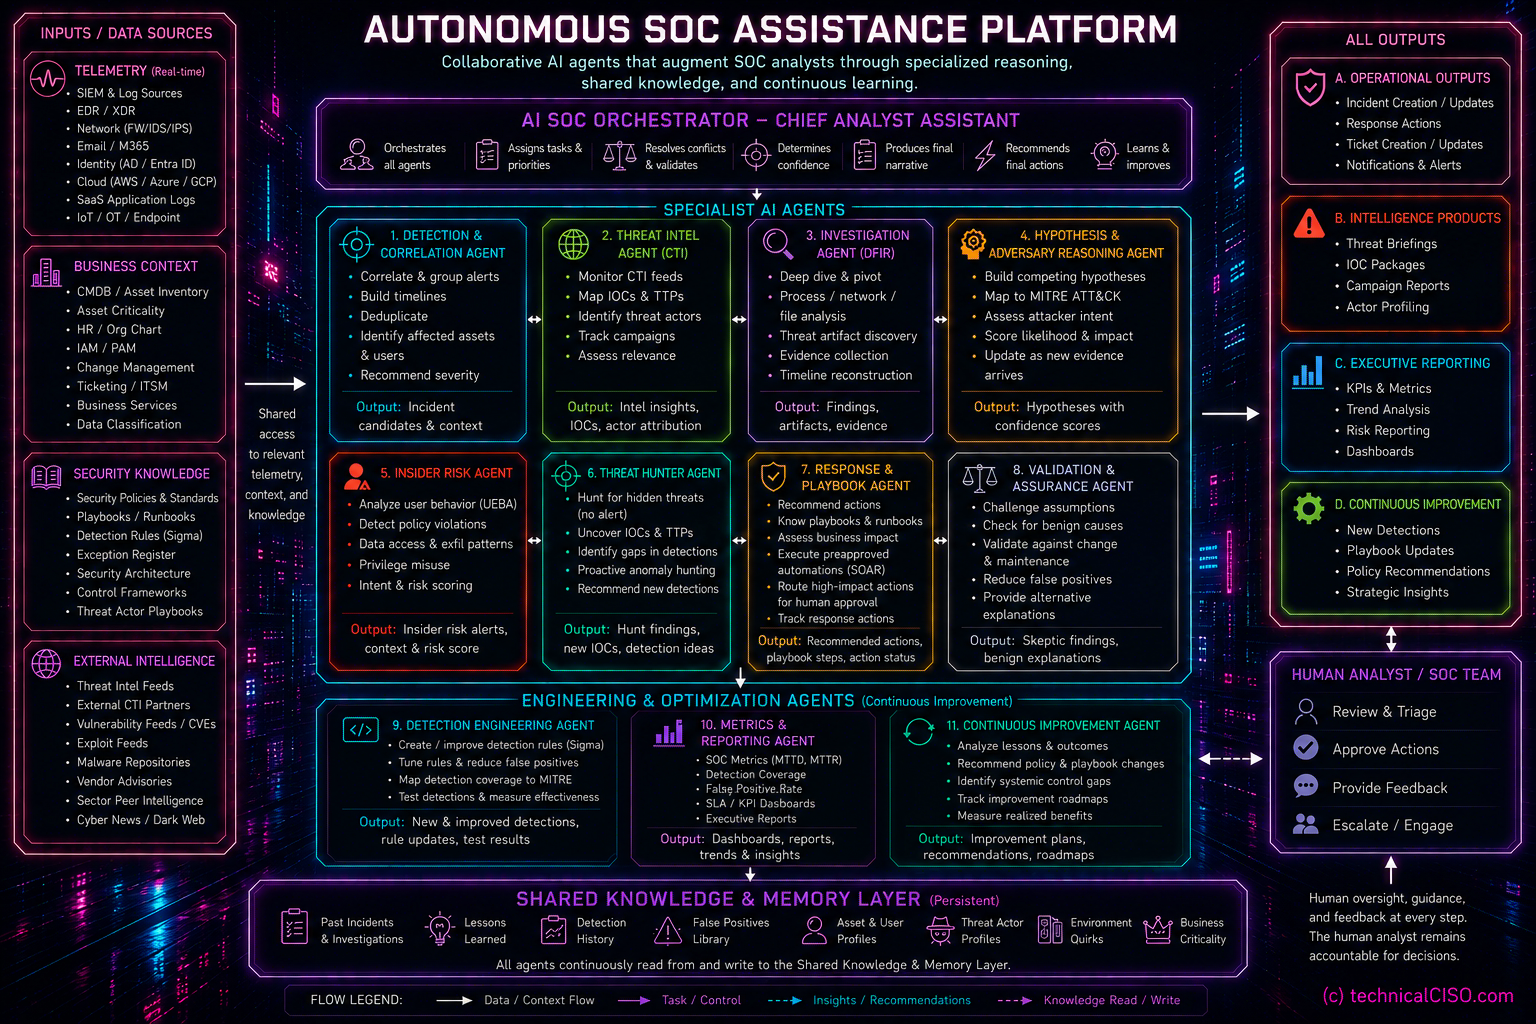
𝗪𝗵𝗮𝘁 𝗶𝗳 𝗲𝘃𝗲𝗿𝘆 𝗮𝗻𝗮𝗹𝘆𝘀𝘁 𝗵𝗮𝗱 𝗮𝗻 𝗲𝗻𝘁𝗶𝗿𝗲 𝗔𝗜 𝗦𝗢𝗖 𝘄𝗼𝗿𝗸𝗶𝗻𝗴 𝗮𝗹𝗼𝗻𝗴𝘀𝗶𝗱𝗲 𝘁𝗵𝗲𝗺? https://technicalciso.com/tc-visual-ai-soc-agents/ #CyberSecurity #SOC #SecurityOperations #AgenticAI #ArtificialIntelligence #ThreatDetection #ThreatHunting #IncidentResponse
0
0
0
0
Once attackers gain initial access, lateral movement is how they expand their reach without tripping alarms. They mimic legitimate admin behavior to pivot toward domain controllers, sensitive file shares, and databases. Our latest blog covers the techniques attackers use and the strategies (segmentation, least privilege, MFA, Zero Trust) that help security teams detect and contain it early. https://graylog.org/post/lateral-movement-security-risk-and-mitigation-strategies/ #CyberSecurity #SIEM #InfoSec #ThreatDetection
0
0
0
0
You've seen all posts