#idor
6 posts · Last used Jul 28
Boosted by @GroupNebula563@mastodon.social
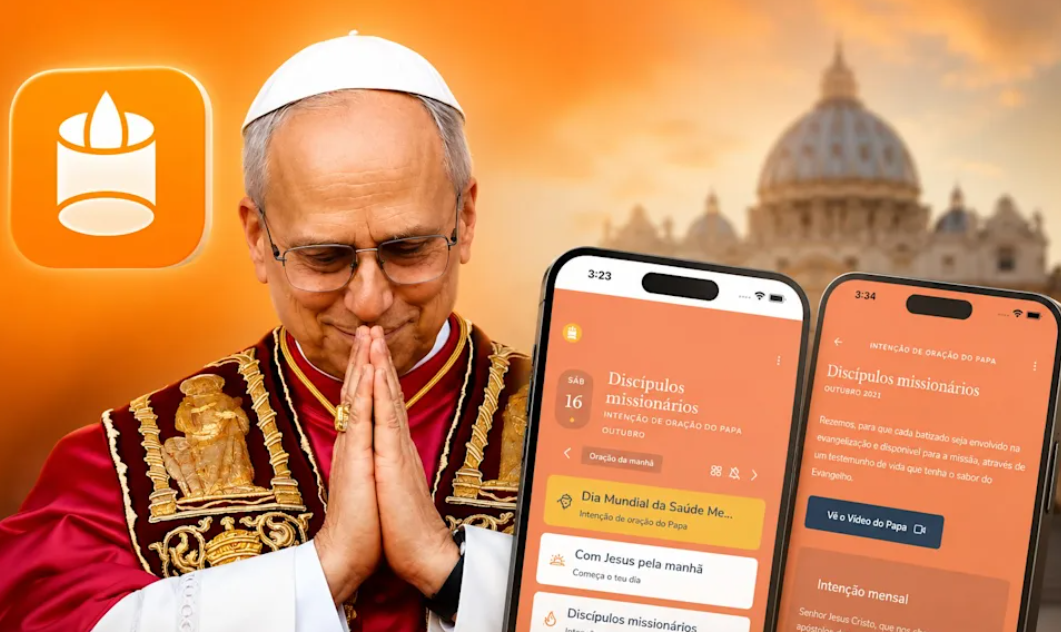
How I found that anyone can pull the email address, name, country, and date of birth of any of the 719,517 users on Click To Pray, the Pope's official prayer app, with a single GET request. Reported January 3rd. Still live six months later. Nobody has ever responded.
An #IDOR Vulnerability in the Vatican's 'Click to Pray' Mobile App Leaks Names, Emails, and Administrative Privileges Across the Globe:
#OWASPTop10
https://techstory.in/sacred-intentions-unsecured-endpoints-vaticans-click-to-pray-exposes-700000-users/
🙏 New Blog Post
The Pope's official prayer app has an IDOR that lets anyone pull user data for all 719,517 accounts. One GET request per user. No auth check.
What's exposed:
Email addressesNamesCountryDate of birth (they call it "borned_date" lol)Account role (it's "PRAYER" for everyone, obviously)
Also found:
Signup endpoint returns the email verification token in the response body, so you can verify accounts without accessing the inboxTheir verification emails fail their own domain's authentication requirements
Reported January 3rd. Emailed 9 people. A journalist also contacted them. Zero responses. Still live six months later. Vow of silence I guess.
Full writeup: https://bobdahacker.com/blog/click-to-pray
#InfoSec #BugBounty #ResponsibleDisclosure #IDOR #Security #CyberSecurity #Privacy #DataExposure #ClickToPray #Vatican #APISecurity
SolarWinds patched three critical Serv-U vulnerabilities (CVE-2026-28307/28308/28321). They allow privilege escalation and RCE. Update Serv-U to 2026.3.
#SolarWinds #ServU #PrivilegeEscalation #RCE #IDOR #Cybersecurity #Vulnerability
http://securityonline.info/solarwinds-serv-u-vulnerabilities/?utm_source=mastodon&utm_medium=jetpack_social
Four critical Coolify vulnerabilities let low-privileged users reach remote code execution and cross-tenant server access. Update to v4.1.2 now.
#Coolify #RCE #IDOR #PrivilegeEscalation #DevOps
https://securityonline.info/coolify-vulnerabilities-rce/?utm_source=mastodon&utm_medium=jetpack_social
#Hello World
Neighbour merupakan Room CTF dari Tryhackme dimana kita memanfaatkan celah kerentanan IDOR untuk dapat mengakses halaman profil administrator.
Baca selengkapnya:
https://analis-siber-purwakarta.blogspot.com/2026/07/tryhackme-neighbour-ctf-challenge-writeup.html
#tryhackme #ctf #cybersecurity #ethicalhacking #websecurity #idor #writeup #infosec #penetrationtesting
You've seen all posts