Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Privacity

@privacity@social.linux.pizza
mastodon 4.7.3
  • Open on social.linux.pizza

Una città della privacy

371 Followers
397 Following
50 Posts
Joined October 08, 2022
Web:
https://privacity.org
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Claude Code ha scoperto una vulnerabilità di Linux rimasta nascosta per 23 anni.

Nicholas Carlini , ricercatore scientifico presso #Anthropic, ha riferito alla conferenza sulla sicurezza dell'IA [un]prompted di aver utilizzato #Claude Code per trovare diverse vulnerabilità di sicurezza sfruttabili da remoto nel kernel #Linux, tra cui una rimasta sconosciuta per 23 anni

https://mtlynch.io/claude-code-found-linux-vulnerability/

@aitech

#IntelligenzaArtificiale

social.linux.pizza
5
0
7
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago
chatcontrol e oscuramento: la guerra alla crittografia è in aumento. A causa di una losca collaborazione tra Stati Uniti e Unione Europea. Sorveglianza di massa statale Dopo la denuncia di Snowden nel 2013, ampie porzioni di Internet sono diventate crittografate, consentendo comunicazioni private e sicure. Non tutti hanno accolto con favore questo cambiamento. In particolare, l'FBI e altre agenzie governative statunitensi hanno combattuto quella che viene spesso definita la "crypto war", la guerra alla crittografia. Negli ultimi anni, a loro si è unita la Commissione Europea. Con lo slogan "e i bambini?", cercano di introdurre la sorveglianza di massa totale di tutti i cittadini dell'UE, prima attraverso la proposta di legge sul controllo delle chat e poi attraverso le iniziative Going Dark e ProtectEU. https://mullvad.net/it/why-privacy-matters/going-dark @privacypride
mullvad.net
5
0
9
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Secondo un sondaggio, quasi due terzi degli europei sostengono la sostituzione della tecnologia statunitense

Secondo una ricerca di YouGov condivisa con Tech Policy Press, quasi due terzi degli europei intervistati ritengono che sostituire i servizi tecnologici americani con alternative europee sia una buona idea, ma gli intervistati sono divisi se questo cambiamento è realistico.

L'analisi arriva mentre i leader dell'Unione Europea portano avanti piani di sovranità digitale sempre più assertivi per ridurre la dipendenza del blocco di 27 paesi dagli Stati Uniti per tutto, dal cloud computing ai social network. Ciò include le proposte del francese E olandese i governi sostituiranno i servizi statunitensi come quelli di Microsoft e Amazon con alternative europee.

https://www.techpolicy.press/almost-two-thirds-of-europeans-back-replacing-us-tech-poll-finds/

@lealternative

Almost Two-Thirds of Europeans Back Replacing US Tech, Poll Finds
Tech Policy Press

Almost Two-Thirds of Europeans Back Replacing US Tech, Poll Finds

EU leaders are pursuing digital sovereignty plans to reduce the 27-country bloc’s dependence on the United States, writes Mark Scott.

2
0
3
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Continua la frenesia del forking dopo che il lancio di #EuroOffice scatena la reazione negativa di #OnlyOffice
68 bolla di commenti su bianco

Nel frattempo, Collabora si separa da LibreOffice Online a seguito delle accuse secondo cui TDF avrebbe espulso "tutto il personale e i partner di Collabora"

https://www.theregister.com/2026/04/02/eurooffice_forks_onlyoffice/

@informatica

social.linux.pizza
2
0
4
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Posso eseguire l'intelligenza artificiale in locale?

Scopri quali modelli di intelligenza artificiale il tuo computer è effettivamente in grado di eseguire.

https://www.canirun.ai/

@aitech

canirun.ai
2
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

La Francia si muove per rompere la messaggistica crittografata: il parlamento francese ha appena approvato l'idea che ogni crittografo al mondo ha già sfatato e la definisce un compromesso.

La delegazione francese dell'intelligence in parlamento ha formalmente sostenuto la violazione della crittografia che protegge le conversazioni di WhatsApp, Signal e Telegram, raccomandando che a magistrati e agenti dell'intelligence venga concesso quello che i legislatori descrivono come un accesso mirato a messaggi che le piattaforme attualmente non possono leggere nemmeno da sole.

https://reclaimthenet.org/france-moves-to-break-encrypted-messaging

@privacypride

France Moves to Break Encrypted Messaging
Reclaim The Net: Free Speech, Privacy, Digital Rights

France Moves to Break Encrypted Messaging

France's parliament just endorsed the one idea every cryptographer on earth has already debunked and they're calling it a compromise.

1
1
8
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Protezione dei minori online, il nodo che il dibattito ignora

Verifica dell’età, potere delle piattaforme e i limiti di una critica che si ferma alla sorveglianza. L'UE prova a suggerire delle soluzioni per una tutela necessaria dentro un web dominato dagli interessi delle Big Tech.

https://centroriformastato.it/protezione-dei-minori-online-il-nodo-che-il-dibattito-ignora/

@privacypride

centroriformastato.it
1
0
6
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago

Il Comitato europeo per la protezione dei dati (EDPB) individua le sfide che ostacolano la piena attuazione del diritto all'oblio

Bruxelles, 18 febbraio - Il Comitato europeo per la protezione dei dati (EDPB) ha adottato una  relazione sull'azione del suo Coordinated Enforcement Framework (CEF) sul diritto all'oblio (art. 17 GDPR) . Il  Comitato si è concentrato questa discussione in quanto si tratta uno dei diritti GDPR più frequentemente esercitati e uno in merito al quale le autorità di protezione dei dati ricevono frequentemente reclami da parte dei cittadini.

https://www.edpb.europa.eu/news/news/2026/edpb-identifies-challenges-hindering-full-implementation-right-erasure_en

@privacypride

edpb.europa.eu
1
0
3
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

FPF Papers for Policymakers: Impactful Privacy and AI Scholarship for a Digital Future
https://fpf.org/blog/fpf-papers-for-policymakers-impactful-privacy-and-ai-scholarship-for-a-digital-future/
@privacy@lemmy.ml
FPF recently concluded its 16th Annual Privacy Papers for Policymakers (PPPM) events, hosting two dynamic virtual ceremonies on March 4 and March 11, 2026. This year’s program centered on the most pressing areas in privacy and AI governance, bringing together global awardees to

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Questo truffatore ha usato una ragazza #MAGA generata dall'IA per raggirare uomini "super stupidi".

Uno studente di medicina afferma di aver guadagnato migliaia di dollari vendendo foto e video di una giovane donna conservatrice da lui creata utilizzando strumenti di grafica generativa. E non è il solo.

https://www.wired.com/story/ai-generated-maga-girls/

@politica

social.linux.pizza
0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago

Red Lines under the EU AI Act: Unpacking the Prohibition of Individual Risk Assessment for the Prediction of Criminal Offences
https://fpf.org/blog/red-lines-under-the-eu-ai-act-unpacking-the-prohibition-of-individual-risk-assessment-for-the-prediction-of-criminal-offences/
@privacy@lemmy.ml
Blog 4 | Red Lines under the EU AI Act Series This blog is the fourth of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can find the whole

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Per un anno a Linate il nostro volto è stato un “passaporto”, ora sappiamo anche perché quel FaceBoarding fosse illecito

Il Garante della Privacy ha dichiarato illecito il FaceBoarding dell'aeroporto di Linate: dati biometrici centralizzati, scarso controllo degli utenti e consenso non davvero informato

https://www.wired.it/article/milano-linate-faceboarding-passaporto-illecito-garante-privacy/

@privacypride

wired.it
0
0
3
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

The New(ish) Architecture of Consumer Health and Artificial Intelligence
https://fpf.org/blog/the-newish-architecture-of-consumer-health-and-artificial-intelligence/
@privacy@lemmy.ml
The rise of AI-powered health tools is prompting new thinking about how, where, and when sensitive health information receives legal protection. According to media reports, consumers are now using general-purpose AI tools to upload or query health information, including medical records, and several companies

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago
Q&A With FPF Vice President for U.S. Policy, Matthew Reisman https://fpf.org/blog/qa-with-fpf-vice-president-for-u-s-policy-matthew-reisman/ @privacy@lemmy.ml In a new Q&A, our new Vice President for U.S. Policy, Matthew Reisman, takes a deeper look at the privacy landscape, particularly his interests in the space, what to look forward to in the U.S. and AI sector, and what is key for stakeholders to pay attention to. What brought you into the privacy and […]
fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Red Lines under the EU AI Act: Understanding the ban of the untargeted scraping of facial images and facial recognition databases 
https://fpf.org/blog/red-lines-under-the-eu-ai-act-understanding-the-ban-of-the-untargeted-scraping-of-facial-images-and-facial-recognition-databases/
@privacy@lemmy.ml
Blog 5 | Red Lines under the EU AI Act Series This blog is the fifth of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can find the

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago
Deanonimizzazione online su larga scala con LLM Gli LLM possono essere utilizzati per eseguire una deanonimizzazione su larga scala. Con un accesso completo a Internet, il nostro agente può reidentificare gli utenti di Hacker News e i partecipanti ad Anthropic Interviewer con elevata precisione, dati solo profili e conversazioni online pseudonimi, un'operazione che richiederebbe ore a un investigatore umano dedicato. Progettiamo quindi attacchi per l'ambiente chiuso. Dati due database di individui pseudonimi, ciascuno contenente testo non strutturato scritto da o su quell'individuo, implementiamo una pipeline di attacco scalabile che utilizza LLM per: (1) estrarre caratteristiche rilevanti per l'identità, (2) cercare corrispondenze candidate tramite incorporamenti semantici e (3) ragionare sui candidati principali per verificare le corrispondenze e ridurre i falsi positivi. Rispetto ai precedenti lavori di deanonimizzazione (ad esempio, sul premio Netflix) che richiedevano dati strutturati o l'ingegneria manuale delle funzionalità, il nostro approccio funziona direttamente sui contenuti utente grezzi su piattaforme arbitrarie. Costruiamo tre set di dati con dati di ground-truth noti per valutare i nostri attacchi. Il primo collega Hacker News ai profili LinkedIn, utilizzando riferimenti multipiattaforma presenti nei profili. Il nostro secondo set di dati confronta gli utenti delle community di discussione cinematografica di Reddit; il terzo suddivide la cronologia di un singolo utente su Reddit nel tempo per creare due profili pseudonimi da confrontare. In ogni contesto, i metodi basati su LLM superano notevolmente le prestazioni delle linee di base classiche, raggiungendo fino al 68% di recall con una precisione del 90%, rispetto a quasi lo 0% del miglior metodo non LLM. I nostri risultati mostrano che l'oscurità pratica che protegge gli utenti pseudonimi online non è più valida e che i modelli di minaccia per la privacy online devono essere riconsiderati. https://arxiv.org/abs/2602.16800 @aitech
Large-scale online deanonymization with LLMs
arXiv.org

Large-scale online deanonymization with LLMs

We show that large language models can be used to perform at-scale deanonymization. With full Internet access, our agent can re-identify Hacker News users and Anthropic Interviewer participants at high precision, given pseudonymous online profiles and conversations alone, matching what would take hours for a dedicated human investigator. We then design attacks for the closed-world setting. Given two databases of pseudonymous individuals, each containing unstructured text written by or about that

0
0
0
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

More Parties, More Risks, More Opportunity? Evolving Governance to Support Cyber Resilience Amidst Evolving Policy and Technological Change
https://fpf.org/blog/more-parties-more-risks-more-opportunity-evolving-governance-to-support-cyber-resilience-amidst-evolving-policy-and-technological-change/
@privacy@lemmy.ml
*Special thanks to Jim Siegl and Jocelyn Aqua for their advice and expertise. Summary: Artificial Intelligence (AI) presents fundamental opportunities and challenges for defense of

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

The Chatbot Moment: Mapping the Emerging 2026 U.S. Chatbot Legislative Landscape
https://fpf.org/blog/the-chatbot-moment-mapping-the-emerging-2026-u-s-chatbot-legislative-landscape/
@privacy@lemmy.ml
Special thanks to Rafal Fryc, U.S. Legislation Intern, for his research and development of the resources referenced. If there is one area of AI policy that lawmakers seem particularly eager to regulate in 2026, it’s chatbots. As state legislative sessions ramp up across the country, policymakers

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Adapting the Privacy Profession to Changing Times
https://fpf.org/blog/adapting-the-privacy-profession-to-changing-times/
@privacy@lemmy.ml
As spring comes into full bloom, the changing of the seasons offers an opportunity for privacy teams to start thinking about how they can be more effective in their workplaces. Privacy work needs to evolve in a couple of important ways, and the value of that work for the organization may have its highest manifestation […]

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Android 17 Beta 3, tutte le novità su geolocalizzazione e privacy

Google ha rilasciato una nuova build di test di Android 17, la Beta 3: è importante per gli sviluppatori perché raggiunge la cosiddetta Platform Stability, ma introduce anche alcune novità dal punto di vista della privacy che vale la pena guardare un po’ più da vicino - soprattutto per quanto riguarda geolocalizzazione e posizione. Le modifiche sono pensate per rendere più trasparente e controllato l’accesso ai dati più sensibili e delicati.

https://www.hdblog.it/smartphone/articoli/n653322/android-17-beta-3-posizione-permessi-novita/

@general-discussion

hdblog.it
0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

FPF on the Securing and Establishing Consumer Uniform Rights and Enforcement Over Data (“SECURE Data”) Act
https://fpf.org/press-releases/fpf-on-the-securing-and-establishing-consumer-uniform-rights-and-enforcement-over-data-secure-data-act/
@privacy@lemmy.ml
The U.S. is overdue to adopt comprehensive federal consumer privacy legislation. Baseline protections for personal information in a federal privacy law would provide an essential foundation for progress on other Congressional priorities,

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

The Price is Right: Responsible Uses of Personal Data in Pricing
https://fpf.org/blog/the-price-is-right-responsible-uses-of-personal-data-in-pricing/
@privacy@lemmy.ml
The way prices are set is changing: more accessible data, sophisticated algorithms, and ubiquitous online shopping have given retailers the ability to automatically tailor offers to customers in real-time or near-real-time based on increasing amounts of data about markets and consumers. A number of pricing strategies involving

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Red Lines under the EU AI Act: Restricting Real-time Remote Biometric Identification Systems for Law Enforcement Purposes
https://fpf.org/blog/red-lines-under-the-eu-ai-act-restricting-real-time-remote-biometric-identification-systems-for-law-enforcement-purposes/
@privacy@lemmy.ml
Blog 8 | Red Lines under the EU AI Act Series This blog is the eighth of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can find the whole

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago
2026 Chatbot Legislation Tracker https://fpf.org/blog/2026-chatbot-legislation-tracker/ @privacy@lemmy.ml Co-authored by Rafal Fryc With nearly 100 chatbot-specific bills introduced across states in 2026, a complex and increasingly fragmented compliance landscape is quickly emerging. This tracker helps stakeholders understand that landscape by highlighting chatbot legislation advancing through initial chambers in state legislatures and Congress, and organizing key provisions across proposals
fpf.org
0
0
0
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Incentives or Obligations? The U.S. Regulatory Approach to Voluntary AI Governance Standards
https://fpf.org/blog/incentives-or-obligations-the-u-s-regulatory-approach-to-voluntary-ai-governance-standards/
@privacy@lemmy.ml
By FPF Legal Intern Rafal Fryc As artificial intelligence gets increasingly deployed across every sector of the economy, regulators find themselves grappling with a fundamental challenge: how to govern a technology that defies traditional regulatory frameworks and changes

Incentives or Obligations? The U.S. Regulatory Approach to Voluntary AI Governance Standards
Future of Privacy Forum

Incentives or Obligations? The U.S. Regulatory Approach to Voluntary AI Governance Standards

This shift toward incorporating non-binding technical standards into legal requirements represents more than just regulatory convenience – it is creating a new legal regime in which voluntary industry guidelines are influencing everything from negligence determinations and punitive damage calculations to affirmative defenses for regulatory actions. Understanding how these soft law approaches are influencing legal expectations has become essential for anyone building, deploying, or governing AI s

0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago
Red Lines under the EU AI Act: Understanding ‘Prohibited AI Practices’ and their Interplay with the GDPR, DSA https://fpf.org/blog/red-lines-under-the-eu-ai-act-understanding-prohibited-ai-practices-and-their-interplay-with-the-gdpr-dsa/ @privacy@lemmy.ml Blog 1/ Red Lines under the EU AI Act Series   The EU AI Act prohibits certain AI practices in the European Union (hereinafter also “the Union”or “the EU”), at the top of the pyramid of its layered approach: harmful manipulation and
Red Lines under the EU AI Act: Understanding ‘Prohibited AI Practices’ and their Interplay with the GDPR, DSA
Future of Privacy Forum

Red Lines under the EU AI Act: Understanding ‘Prohibited AI Practices’ and their Interplay with the GDPR, DSA

This blog, first in a series, examines banned AI practices under the EU AI Act, Article 5, covering legal scope, enforcement, compliance, and EU digital rules.

0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

I vincitori del Premio letterario “DATA! The game” 2026
https://www.istitutoitalianoprivacy.it/2026/03/15/i-vincitori-del-premio-letterario-data-the-game-2026/
@informatica
Roma, 15 marzo 2026 – La Giuria del Premio letterario “DATA! The game®” 2026, composta dagli esperti italiani di diritto dei dati e delle tecnologie Anna Cataleta, Federica De Stefani, Fernanda Faini, Riccardo Giannetti, Rosario Imperiali d’Afflitto, Rocco Panetta, ha riconosciuto la vittoria del primo...

istitutoitalianoprivacy.it
0
0
3
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Navigating Autonomy and Privacy in Emerging AgeTech: Insights from the FPF Roundtable
https://fpf.org/blog/navigating-autonomy-and-privacy-in-emerging-agetech-insights-from-the-fpf-roundtable/
@privacy@lemmy.ml
As AgeTech expands into homes across the country—seeking to enable older adults to live independently longer—fundamental questions about autonomy, privacy, and trust are coming into sharper focus. How do we balance caregiver support with individual privacy? Should data pertaining to

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Contextualizing the Proposed SECURE Data Act in the State Privacy Landscape
https://fpf.org/blog/contextualizing-the-proposed-secure-data-act-in-the-state-privacy-landscape/
@privacy@lemmy.ml
Special thanks to FPF’s Dr. Gabriela Zanfir-Fortuna, VP of Global Policy, for her contributions to this analysis. The House Committee on Energy and Commerce’s Republican data privacy working group released their long-awaited comprehensive consumer privacy bill on April 22, titled the “Securing and

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Meta sospende il lavoro con Mercor dopo che una violazione dei dati ha messo a rischio i segreti del settore dell'intelligenza artificiale

Importanti laboratori di intelligenza artificiale stanno indagando su un incidente di sicurezza che ha avuto ripercussioni su Mercor, uno dei principali fornitori di dati. L’incidente avrebbe potuto esporre dati chiave su come addestrano i modelli di intelligenza artificiale.

https://www.wired.com/story/meta-pauses-work-with-mercor-after-data-breach-puts-ai-industry-secrets-at-risk/

@aitech

wired.com
0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago

Violazione dei dati di IDMerit: 1 miliardo di record di dati personali esposti nella fuga di dati KYC

Un database non protetto collegato a IDMerit ha reso pubblici un miliardo di dati personali in 26 paesi.

  • I dati trapelati includono documenti d'identità nazionali, nomi completi, indirizzi, numeri di telefono e potenziali metadati di telecomunicazioni.
  • Gli Stati Uniti sono stati la nazione più colpita, con oltre 203 milioni di dati personali esposti.
  • Anche il Messico, le Filippine e nazioni europee come la Germania avevano milioni di record esposti.

https://cybernews.com/security/global-data-leak-exposes-billion-records/

@privacypride

cybernews.com
0
0
0
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago
Red Lines under the EU AI Act: Understanding Manipulative Techniques and the Exploitation of Vulnerabilities https://fpf.org/blog/red-lines-under-the-eu-ai-act-understanding-manipulative-techniques-and-the-exploitation-of-vulnerabilities/ @privacy@lemmy.ml Blog 2/ Red Lines under the EU AI Act Series   This blog is the second of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can read the first episode here and find the whole
fpf.org
0
0
0
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Celebrating Another Year of Privacy and AI Governance: FPF at the 2026 IAPP Global Summit
https://fpf.org/blog/celebrating-another-year-of-privacy-and-ai-governance-fpf-at-the-2026-iapp-global-summit/
@privacy@lemmy.ml
Authored by FPF Communications Intern Celeste Valentino FPF experts participated in the 2026 IAPP Global Summit and hosted FPF privacy executive convenings in Washington, D.C. from March 31 to April 2. As a major gathering for privacy professionals, the event featured a heavy

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago

From Proposal to Passage: Enacted U.S. AI Laws, 2023–2025
https://fpf.org/blog/from-proposal-to-passage-enacted-u-s-ai-laws-2023-2025/
@privacy@lemmy.ml
Over the past three years, lawmakers across the United States have increasingly enacted AI-related laws that shape the development and deployment of AI systems. Between 2023 and 2025, the Future of Privacy Forum tracked 27 pieces of enacted AI-related legislation across 14 states, along with one federal law (the TAKE IT DOWN Act) that carry

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Africa’s Data Protection Reforms: A Continental Perspective on the Drivers of Change in Legal Frameworks
https://fpf.org/blog/africas-data-protection-reforms-a-continental-perspective-on-the-drivers-of-change-in-legal-frameworks/
@privacy@lemmy.ml
1. Introduction Within an evolving digital landscape, several African jurisdictions have proposed a variety of reforms to existing and novel legal frameworks that regulate the processing of personal data, and the development and deployment of new

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Gli uomini acquistano strumenti di hacking da usare contro mogli e amici

Nei gruppi Telegram, gli uomini condividono migliaia di immagini non consensuali di donne e ragazze, acquistano spyware e praticano doxing e abusi sessuali.

https://www.wired.com/story/men-are-buying-hacking-tools-to-use-against-their-wives-and-friends/

@privacypride

wired.com
0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Red Lines under the EU AI Act: Understanding the prohibition of biometric categorization for certain sensitive characteristics 
https://fpf.org/blog/red-lines-under-the-eu-ai-act-understanding-the-prohibition-of-biometric-categorization-for-certain-sensitive-characteristics/
@privacy@lemmy.ml
Blog 7 | Red Lines under the EU AI Act Series This blog is the seventh of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can find the

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

L'intelligenza artificiale locale deve diventare la norma

Una delle tendenze attuali nel software moderno è che gli sviluppatori inseriscano chiamate API a OpenAI o Anthropic per integrare funzionalità nelle proprie app. Si potrebbe discutere sull'effettivo valore aggiunto che queste funzionalità apportano agli utenti, ma ciò di cui voglio parlare è il concetto fondamentale di dipendenza da un modello di intelligenza artificiale ospitato nel cloud per le applicazioni.

Questa pigrizia sta creando una generazione di software fragile, che viola la privacy e che è fondamentalmente difettoso. Stiamo sviluppando applicazioni che smettono di funzionare nel momento in cui il server si blocca o una carta di credito scade.

Dobbiamo tornare all'abitudine di sviluppare software in cui il lavoro viene svolto dai nostri dispositivi locali.

https://unix.foo/posts/local-ai-needs-to-be-norm/

@aitech

unix.foo
0
1
2
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago

Red Lines under the EU AI Act: Unpacking Social Scoring as a Prohibited AI Practice 
https://fpf.org/blog/red-lines-under-the-eu-ai-act-unpacking-social-scoring-as-a-prohibited-ai-practice/
@privacy@lemmy.ml
Blog 3 | Red Lines under the EU AI Act Series  This blog is the third of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can find the whole series here. The prohibition of AI-enabled social scoring is among the red lines

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Privacy Protections Coming Sooner Rather Than Later to the Sooner State
https://fpf.org/blog/privacy-protections-coming-sooner-rather-than-later-to-the-sooner-state/
@privacy@lemmy.ml
Oklahoma has become the latest U.S. state to enact a comprehensive consumer privacy law after Governor Stitt signed SB 546 into law on March 20. This ends two long legislative droughts: First, this is the long-awaited 20th state comprehensive privacy law and the first since the Rhode Island Data Transparency and

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago

Un utente di Reddit ha criticato l'ICE. Trump sta cercando di smascherarli trascinando l'agenzia davanti a un gran giurì segreto.

La richiesta dell'ICE di rivelare l'identità dell'utente è fallita. Gli attivisti temono che il ricorso a un gran giurì segnali un'escalation nella guerra al dissenso.

https://theintercept.com/2026/04/10/reddit-ice-protest-grand-jury/

@politica

A Redditor Criticized ICE. Trump Is Trying to Unmask Them by Dragging the Company to a Secret Grand Jury.
The Intercept

A Redditor Criticized ICE. Trump Is Trying to Unmask Them by Dragging the Company to a Secret Grand Jury.

An ICE summons to get the user’s identity failed. Advocates worry the move to a grand jury signals an escalation of the war on dissent.

0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Rilasciata la versione 3.2 di GIMP .

«Siamo lieti di presentare la prima versione di GIMP 3.2 ! Questo traguardo rappresenta un anno di progettazione, sviluppo e test da parte di volontari e della community, nell'ambito del nostro piano per semplificare le release dopo GIMP 3.0 . Non vediamo l'ora di mostrarvi le nuove funzionalità offerte dalla versione 3.2!»

@gnulinuxitalia

https://www.gimp.org/news/2026/03/14/gimp-3-2-released/

GNU/Linux Italia - Feddit.it
feddit.it

GNU/Linux Italia - Feddit.it

Gruppo di discussione GNU/Linux. Non ti sto dando una birra gratis la sto condividendo. Gnu Not Unix Telegram [https://t.me/GNULinuxItaliaOpen] Matrix [https://matrix.to/#/#linuxitalia:mozilla.org] #linux #gnulinux #gnu #softwarelibero #opensource #fedi22 #gruppi #forum

0
0
3
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Red Lines under EU AI Act: Unpacking the prohibition of emotion recognition in the workplace and education institutions
https://fpf.org/blog/red-lines-under-eu-ai-act-unpacking-the-prohibition-of-emotion-recognition-in-the-workplace-and-education-institutions/
@privacy@lemmy.ml
Blog 6 | Red Lines under the EU AI Act Series This blog is the sixth of a series that explores prohibited AI practices under the EU AI Act and their interplay with existing EU law. You can find the whole series here.

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Microsoft afferma che gli aggressori stanno avvelenando i risultati di ricerca per diffondere falsi client VPN che rubano le credenziali.

La campagna reindirizza le ricerche software agli installatori trojanizzati su GitHub che mostrano falsi prompt VPN mentre Hyrax ruba le credenziali.

https://thehackernews.com/2026/03/storm-2561-spreads-trojan-vpn-clients.html

@informatica

thehackernews.com
0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 7mo ago
Replying to on poliverso.org
@piratepost Thank you! @progressivepolitics
0
0
0
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

"Snoopy", "Adolf" e "Password": le password del governo ungherese esposte online

Quasi 800 indirizzi e-mail del governo ungherese e le relative password stanno circolando online, rivelando vulnerabilità di base nei protocolli di sicurezza dei ministeri coinvolti in attività classificate e sensibili.

Un’analisi di Bellingcat dei dati della violazione mostra che 12 dei 13 ministeri del governo sono stati colpiti, il che in alcuni casi ha rivelato le informazioni riservate di personale militare e funzionari pubblici distaccati all’estero. 

https://www.bellingcat.com/news/2026/04/09/the-hungarian-government-passwords-exposed-online/

@informatica

bellingcat.com
0
0
2
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

Gli hacker cinesi prendono di mira le milizie del sud-est asiatico con il malware AppleChris e MemFun

Una sospetta operazione di spionaggio informatico con sede in Cina ha preso di mira organizzazioni militari del sud-est asiatico come parte di una campagna sponsorizzata dallo stato che risale almeno al 2020.

L'Unità 42 di Palo Alto Networks sta monitorando l'attività di minaccia con il nome CL-STA-1087, dove CL si riferisce a cluster e STA sta per motivazione sostenuta dallo stato.

https://thehackernews.com/2026/03/chinese-hackers-target-southeast-asian.html

@informatica

thehackernews.com
0
0
3
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

The Rest of the West: Oregon and Washington Build on California Chatbot Law
https://fpf.org/blog/the-rest-of-the-west-oregon-and-washington-build-on-california-chatbot-law/
@privacy@lemmy.ml
Introduction The West Coast now has a full set of chatbot laws on the books. Following California’s SB 243 (signed in 2025 and effective January 1, 2026) both Oregon (SB 1546) and Washington (HB 2225) enacted companion chatbot laws that will take effect on January 1, 2027. Together, these laws establish a

fpf.org
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 6mo ago

L'Iran minaccia il data center Stargate di OpenAI ad Abu Dhabi.

Un video diffuso dal Corpo delle Guardie Rivoluzionarie Islamiche iraniane suggerisce che, qualora gli Stati Uniti attaccassero le sue centrali elettriche, prenderanno di mira il data center che OpenAI intende costruire.

@aitech

https://www.theverge.com/ai-artificial-intelligence/907427/iran-openai-stargate-datacenter-uae-abu-dhabi-threat

feddit.it
0
0
1
0
Open post
Privacity @privacity@social.linux.pizza
· 5mo ago
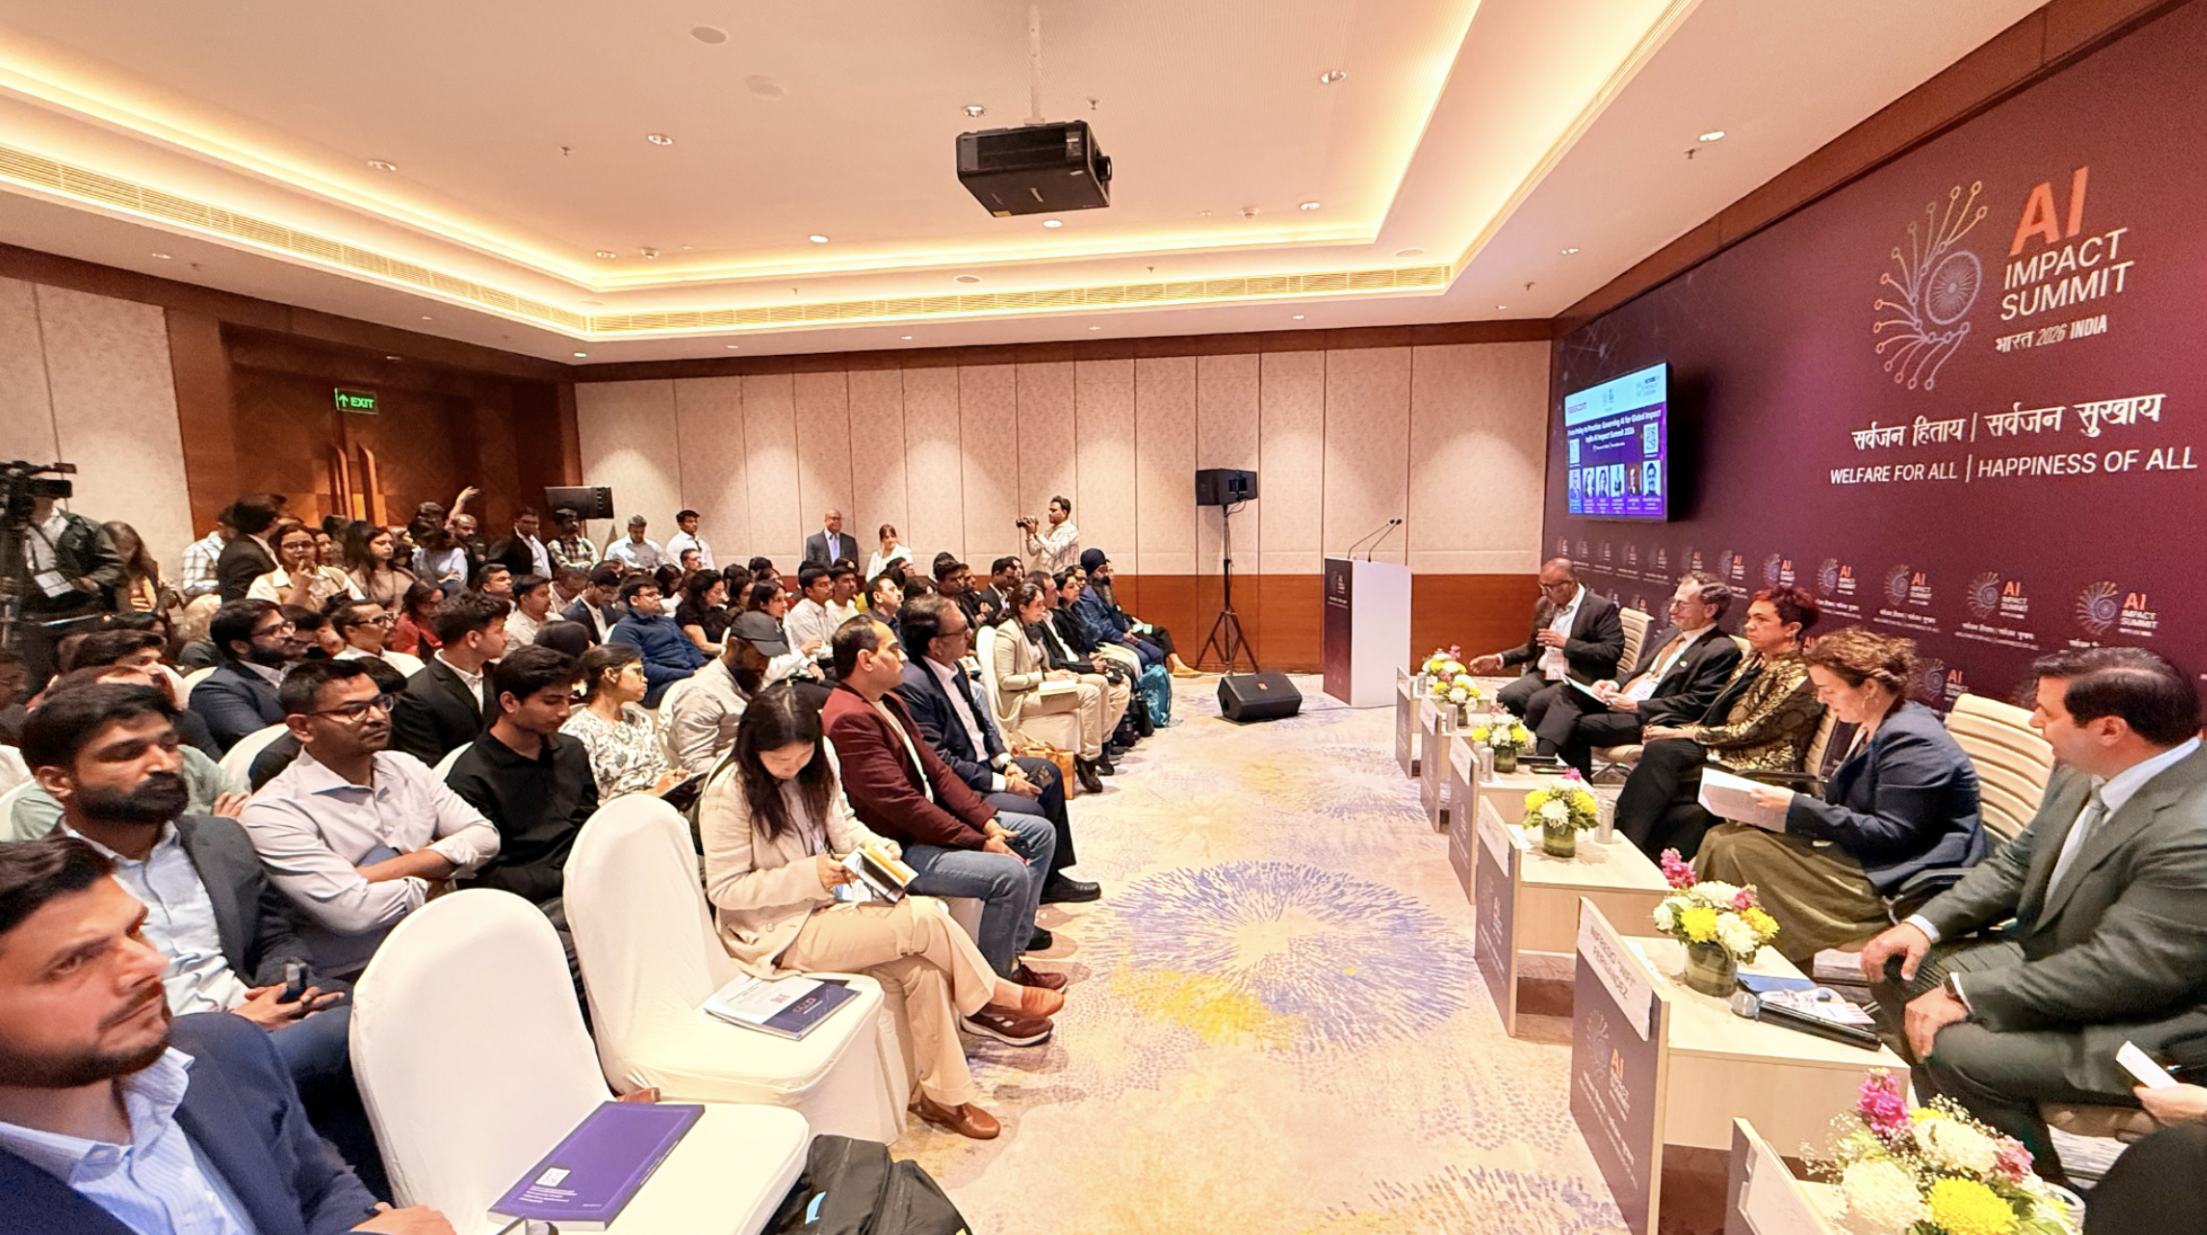
Taking stock: The Impact of the India AI Impact Summit 2026 https://fpf.org/blog/taking-stock-the-impact-of-the-india-ai-impact-summit-2026/ @privacy@lemmy.ml India’s hosting of the AI Impact Summit 2026 was an ambitious undertaking. With 600,000 attendees and 92 signatories to the New Delhi Declaration, the Summit was a showcase of a Global South country taking a leading role in shaping the AI governance agenda. The Summit’s official framing centered on infrastructure, compute, and equitable
Taking stock: The Impact of the India AI Impact Summit 2026
Future of Privacy Forum

Taking stock: The Impact of the India AI Impact Summit 2026

This post reflects on India AI Summit’s key outcomes and FPF’s engagements in New Delhi, exploring emerging themes in global AI policy: the rise of regulatory sandboxes, challenges of geopolitical fragmentation, and urgent questions around children’s safety and agentic AI systems.

0
0
1
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 15:15:30 UTC