Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Patrick C Miller :donor:

@patrickcmiller@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Critical Infrastructure & Industrial Security Advisor. Recovering regulator. Airport dweller. @ampyxcyber@infosec.exchange President and CEO.

0 Followers
0 Following
50 Posts
Joined October 31, 2022
Website:
https://www.patrickcmiller.com/
Company:
https://www.ampyxcyber.com/
LinkedIn:
https://www.linkedin.com/in/millerpatrickc/
Podcast:
https://ampyxcyber.com/podcast
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1d ago
Boosted by @kcarruthers@infosec.exchange
Production, Persuasion, and Power: How Generative and Agentic AI Are Transforming Influence Operations https://www.lawfaremedia.org/article/production--persuasion--and-power--how-generative-and-agentic-ai-are-transforming-influence-operations
Production, Persuasion, and Power: How Generative and Agentic AI Are Transforming Influence Operations
Default

Production, Persuasion, and Power: How Generative and Agentic AI Are Transforming Influence Operations

Generative AI can increase the quantity and quality of malign foreign influence campaigns. However, questions remain as to whether these campaigns influence public opinion.

1
0
2
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
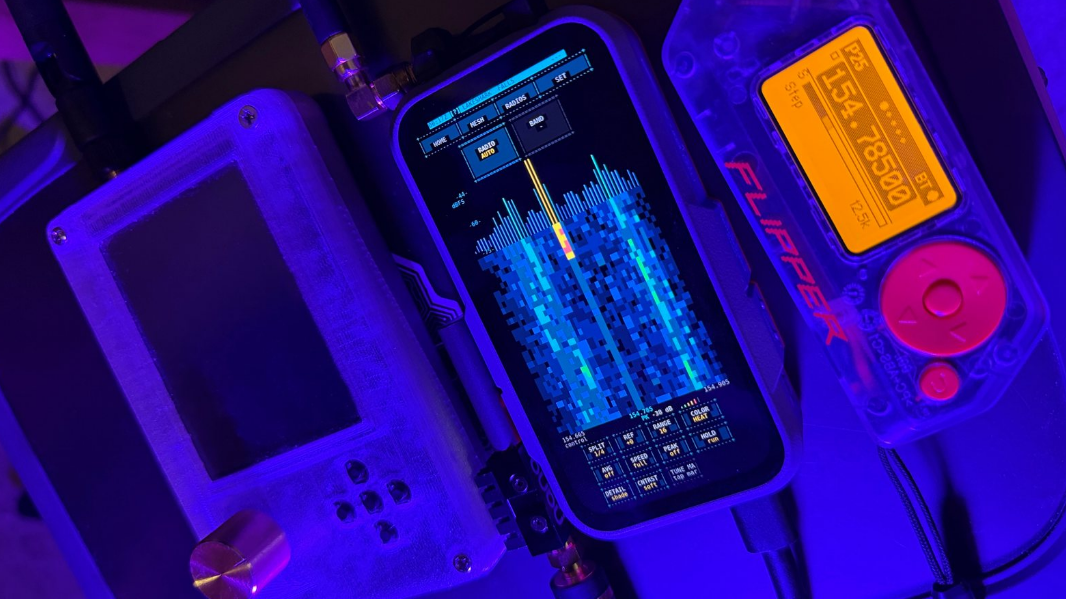
Handheld Scanner is a Radio Multi-tool https://hackaday.com/2026/09/24/handheld-scanner-is-a-radio-multi-tool/
Handheld Scanner Is A Radio Multi-tool
Hackaday

Handheld Scanner Is A Radio Multi-tool

These days, it’s possible to cram a whole lot of radio functionality into a very compact device. A great example of that is the LakeShark scanner from [SAMS0N1TE]. The LakeShark is based on t…

3
0
2
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks https://www.bleepingcomputer.com/news/security/shinyhunters-uses-waf-bypass-trick-in-oracle-peoplesoft-attacks/
ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks
BleepingComputer

ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks

The ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 flaw, allowing the threat actors to resume widespread exploitation of a flaw on vulnerable servers.

2
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
The AI Governance Momentum: Why We Need to Fill the Accountability Gap Now https://www.justsecurity.org/157214/ai-governance-momentum-accountability-gap/?utm_source=feedly&utm_medium=rss&utm_campaign=ai-governance-momentum-accountability-gap
The AI Governance Momentum: Why We Need to Fill the Accountability Gap Now
Just Security

The AI Governance Momentum: Why We Need to Fill the Accountability Gap Now

This series aims to set out what a meaningful, multistakeholder, and globally relevant AI accountability mechanism should look like.

1
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
On Anthropic’s AI Misuse Report https://www.schneier.com/blog/archives/2026/09/on-anthropics-ai-misuse-report.html
Schneier on Security

On Anthropic's AI Misuse Report - Schneier on Security

Earlier this month, Anthropic published a long report detailing all of the Claude misuses it detected. Daniel Meissler usefully summarized the report into 117 findings. A few of the highlights: AI agents increasingly handled reconnaissance, exploitation, data theft, propaganda production, surveillance workflows, and research while humans selected targets, set goals, and reviewed important outputs. The report describes attackers using AI to industrialize credential theft, cloud compromise, phishi

1
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Hackers now exploit critical Roundcube flaw in code injection attacks https://www.bleepingcomputer.com/news/security/critical-roundcube-flaw-now-actively-exploited-in-code-injection-attacks/
Hackers now exploit critical Roundcube flaw in code injection attacks
BleepingComputer

Hackers now exploit critical Roundcube flaw in code injection attacks

A high-severity Roundcube Webmail vulnerability patched in May is now being actively exploited in attacks, according to the Canadian Centre for Cyber Security.

1
0
2
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Google’s new Gemini TTS models can clone a voice from 30 seconds of audio https://thenextweb.com/news/gemini-tts-3-8-flash-voice-design-cloning
thenextweb.com

Google’s new Gemini TTS models can clone a voice from 30 seconds of audio

Google's Gemini 3.8 TTS models design voices from text prompts, offer 2,000+ voices and clone a voice from 30 seconds of audio after a consent check.

1
1
1
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Lawsuit demands OpenAI pay for new school after ChatGPT used in shooting https://arstechnica.com/tech-policy/2026/09/lawsuit-demands-openai-pay-for-new-school-after-chatgpt-used-in-shooting/
arstechnica.com
1
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data https://thehackernews.com/2026/09/cloudflare-fixes-flaw-that-let-one.html
thehackernews.com

Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data

1
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
CVE flood pushes Ubuntu onto weekly kernel release cycle https://www.theregister.com/os-platforms/2026/09/24/cve-flood-pushes-ubuntu-onto-weekly-kernel-release-cycle/5298912
CVE flood pushes Ubuntu onto weekly kernel release cycle
theregister

CVE flood pushes Ubuntu onto weekly kernel release cycle

AI-assisted bug hunting is helping pile up vulnerabilities faster than defenders can patch them, so Canonical is picking up the pace

1
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
‘We’re already fighting yesterday’s battle’: Greece’s prime minister gets candid about AI https://techcrunch.com/2026/09/22/were-already-fighting-yesterdays-battle-greeces-prime-minister-gets-candid-about-ai/
'We're already fighting yesterday's battle': Greece's prime minister gets candid about AI | TechCrunch
TechCrunch

'We're already fighting yesterday's battle': Greece's prime minister gets candid about AI | TechCrunch

Most leaders on a trade mission stick to the pitch, but when I interviewed Greek Prime Minister Kyriakos Mitsotakis this week, he also admitted that no government is ready for what AI is about to do.

1
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Crooks use fake desktop apps to fool HR staff into giving them remote access https://www.theregister.com/security/2026/09/25/crooks-use-fake-desktop-apps-to-fool-hr-staff-into-giving-them-remote-access/5299226
Crooks use fake desktop apps to fool HR staff into giving them remote access
theregister

Crooks use fake desktop apps to fool HR staff into giving them remote access

Nothing in the attack chain screams malicious software, except none of the impersonated HR and payroll providers actually offers a desktop app

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
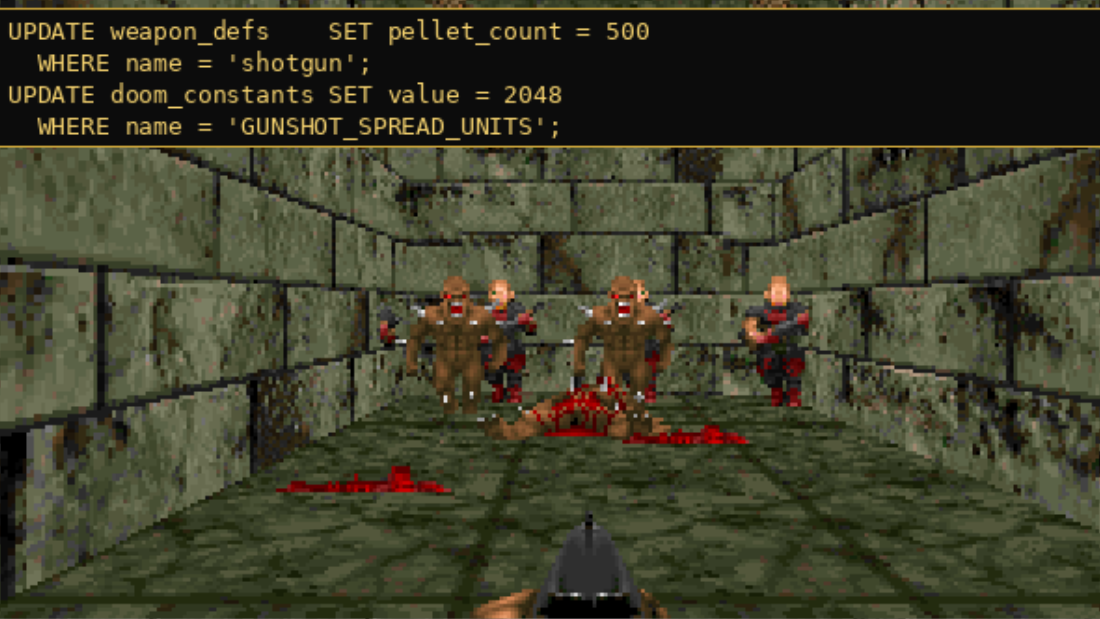
Abusing SQL to Play DOOM https://hackaday.com/2026/09/25/abusing-sql-to-play-doom/
Abusing SQL To Play DOOM
Hackaday

Abusing SQL To Play DOOM

Most laypeople who encounter SQL think of it purely as a tool for managing large datasets. While that is certainly what it was designed for, SQL is still a programming language at its core. It incl…

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
AI model costs are pushing startups towards cheaper open weigh https://thenextweb.com/news/model-costs-startups-open-weights
thenextweb.com

AI model costs are pushing startups towards cheaper open weight

Harvey's gross margin fell from about 50% to minus 50% by June on AI model costs. It turned positive after it built a model on China's Kimi K3.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Amid Ongoing Rogue Incidents, Debate Over AI Safety Gets Real https://www.darkreading.com/cyber-risk/rogue-incidents-debate-ai-safety-gets-real
darkreading.com
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Discord’s age verification era is upon us, despite community backlash https://techcrunch.com/2026/09/22/discords-age-verification-era-is-upon-us-despite-community-backlash/
Discord's age-verification era is upon us, despite community backlash | TechCrunch
TechCrunch

Discord's age-verification era is upon us, despite community backlash | TechCrunch

According to Discord, 90% of users will not have to verify their age.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
AI Incident Response Readiness Lags Behind AI Adoption, ISACA Finds https://www.infosecurity-magazine.com/news/orgs-lack-ai-incident-response/
infosecurity-magazine.com
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Windows, Linux, Android File Notification Systems Leak User Activity https://www.securityweek.com/windows-linux-android-file-notification-systems-leak-user-activity/
Windows, Linux, Android File Notification Systems Leak User Activity
SecurityWeek

Windows, Linux, Android File Notification Systems Leak User Activity

File-change notification systems in Linux, Android, Windows, and macOS can leak keystroke timing, browsing activity, and WhatsApp events.

0
0
1
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Arista Urges Immediate Patching of Exploited VCO Zero-Day https://www.securityweek.com/arista-urges-immediate-patching-of-exploited-vco-zero-day/
Arista Urges Immediate Patching of Exploited VCO Zero-Day
SecurityWeek

Arista Urges Immediate Patching of Exploited VCO Zero-Day

Arista patched CVE-2026-93952, an exploited zero-day in on-premises deployments of VeloCloud Orchestrator (VCO).

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
NetScaler admins told to patch critical zero-days in ADC and Gateway now https://www.networkworld.com/article/4227476/netscaler-admins-told-to-patch-critical-zero-days-in-adc-and-gateway-now.html
NetScaler admins told to patch critical zero-days in ADC and Gateway now
Network World

NetScaler admins told to patch critical zero-days in ADC and Gateway now

Citrix published patches for two critical flaws and six lesser ones on Sunday; “Monday will be too late” to patch, said one expert.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
State AGs push Congress for AI safety, transparency https://www.cfodive.com/news/26-state-attorneys-general-call-congress-rein-in-ai-flagging-risks-Trump-un-altman-openai/831318/
26 state attorneys general call on Congress to rein in AI, flagging risks
CFO Dive

26 state attorneys general call on Congress to rein in AI, flagging risks

Legislation introduced in the Senate on Wednesday would pause AI research until the creation of a federal department that would regulate the technology.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Emerging Ransomware Gang Uses Backup Destruction Threats to Pressure Victims https://www.infosecurity-magazine.com/news/ransomware-gang-uses-backup/
infosecurity-magazine.com
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 3d ago
Boosted by @kcarruthers@infosec.exchange
Hacks of 2 federal agencies in a month have spilled a bonanza of sensitive data https://arstechnica.com/security/2026/10/hacks-of-2-federal-agencies-in-a-month-have-spilled-a-bonanza-of-sensitive-data/
arstechnica.com
0
0
2
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Senators propose voluntary telecom security framework after Salt Typhoon hacks https://www.nextgov.com/cybersecurity/2026/09/senators-propose-voluntary-telecom-security-framework-after-salt-typhoon-hacks/416201/
Senators propose voluntary telecom security framework after Salt Typhoon hacks
Nextgov.com

Senators propose voluntary telecom security framework after Salt Typhoon hacks

The bipartisan bill would establish cybersecurity best practices and independent certification, following the FCC’s rollback of safeguards adopted in response to the Chinese hacking campaign.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Google Warns of ShinyHunters’ Fresh Oracle PeopleSoft Campaign https://www.securityweek.com/google-warns-of-shinyhunters-fresh-oracle-peoplesoft-campaign/
Google Warns of ShinyHunters' Fresh Oracle PeopleSoft Campaign
SecurityWeek

Google Warns of ShinyHunters' Fresh Oracle PeopleSoft Campaign

Google warns of a new ShinyHunters campaign mass targeting Oracle PeopleSoft with a modified CVE-2026-35273 exploit.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
CISA outlines improvement plan for CVE program https://cyberscoop.com/cisa-cve-data-quality-white-paper-expert-reaction/
CISA outlines improvement plan for CVE program
CyberScoop

CISA outlines improvement plan for CVE program

Cybersecurity experts express skepticism over CISA’s new CVE data quality white paper, citing unaddressed software identifiers and unreleased baseline metrics.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
OpenAI Says Its Models Engaged With US Government Websites in New Model Misbehavior Disclosure https://www.securityweek.com/openai-says-its-models-engaged-with-us-government-websites-in-new-model-misbehavior-disclosure/
OpenAI Says Its Models Engaged With US Government Websites in New Model Misbehavior Disclosure
SecurityWeek

OpenAI Says Its Models Engaged With US Government Websites in New Model Misbehavior Disclosure

OpenAI said its artificial intelligence agents had interacted with several U.S. government websites in unexpected ways.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Cyberattack hits Welsh police force, may have affected staff data https://therecord.media/wales-cyberattack-police-breach
Cyberattack hits Welsh police force, may have affected staff data
therecord.media

Cyberattack hits Welsh police force, may have affected staff data

Dyfed-Powys Police in Wales said a cyberattack affecting the force disrupted some non-emergency systems and may have compromised staff information.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
AI Helps Uncover MikroTrick Attack Chain in MikroTik RouterOS https://securityaffairs.com/199678/hacking/ai-helps-uncover-mikrotrick-attack-chain-in-mikrotik-routeros.html
AI Helps Uncover MikroTrick Attack Chain in MikroTik RouterOS
Security Affairs

AI Helps Uncover MikroTrick Attack Chain in MikroTik RouterOS

MikroTrick chains RouterOS flaws to bypass authentication and gain admin access. AI helped researchers uncover the attack chain within days.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Chinese hackers exploit WordPress, Zyxel flaws to steal govt data https://www.bleepingcomputer.com/news/security/chinese-hackers-exploit-multiple-technologies-to-steal-govt-data/
Chinese hackers exploit WordPress, Zyxel flaws to steal govt data
BleepingComputer

Chinese hackers exploit WordPress, Zyxel flaws to steal govt data

A Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL GS1900 Smart Managed Switches and WordPress to steal sensitive data from 996 devices and more than 18,500 records stored in backend databases.

0
1
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway https://www.cisa.gov/news-events/alerts/2026/09/27/critical-zero-day-vulnerabilities-exploited-citrix-netscaler-adc-gateway
Cybersecurity and Infrastructure Security Agency CISA

Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway | CISA

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
New York Could Share Frontier AI Safety Reports Nationwide Without New Legislation https://www.lawfaremedia.org/article/new-york-could-share-frontier-ai-safety-reports-nationwide-without-new-legislation
New York Could Share Frontier AI Safety Reports Nationwide Without New Legislation
Default

New York Could Share Frontier AI Safety Reports Nationwide Without New Legislation

An existing financial-regulatory platform could provide a secure channel for states to share confidential frontier AI safety reports.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
CISA Charts New "Quality Era" for Global CVE Program https://www.infosecurity-magazine.com/news/cisa-quality-era-global-cve-program/
infosecurity-magazine.com
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
A user says Meta’s Muse gave his address to a Marketplace buyer https://thenextweb.com/news/meta-muse-facebook-marketplace-address-buyer-robb
thenextweb.com

A user says Meta’s Muse gave his address to a Marketplace buyer

Muse agreed a lowball price and sent a Marketplace buyer to a user’s building, he says. Meta says Muse usually asks for permission.

0
0
1
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Woman's brain worm infection confirmed after eggs grow tails in lab test https://arstechnica.com/health/2026/09/womans-brain-worm-infection-confirmed-after-eggs-grow-tails-in-lab-test/
arstechnica.com
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Honeywell: OT Security Teams Embrace AI, but Autonomy Still Rare https://www.securityweek.com/honeywell-ot-security-teams-embrace-ai-but-autonomy-still-rare/
Honeywell: OT Security Teams Embrace AI, but Autonomy Still Rare
SecurityWeek

Honeywell: OT Security Teams Embrace AI, but Autonomy Still Rare

Honeywell OT Cybersecurity Benchmark Report shows a disconnect between how organizations rate their OT security and how prepared they are.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
CISA, FBI warn critical infrastructure operators of third-party ICS risks, urge least privilege and remote access controls https://industrialcyber.co/industrial-cyber-attacks/cisa-fbi-warn-critical-infrastructure-operators-of-third-party-ics-risks-urge-least-privilege-and-remote-access-controls/
industrialcyber.co
0
1
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
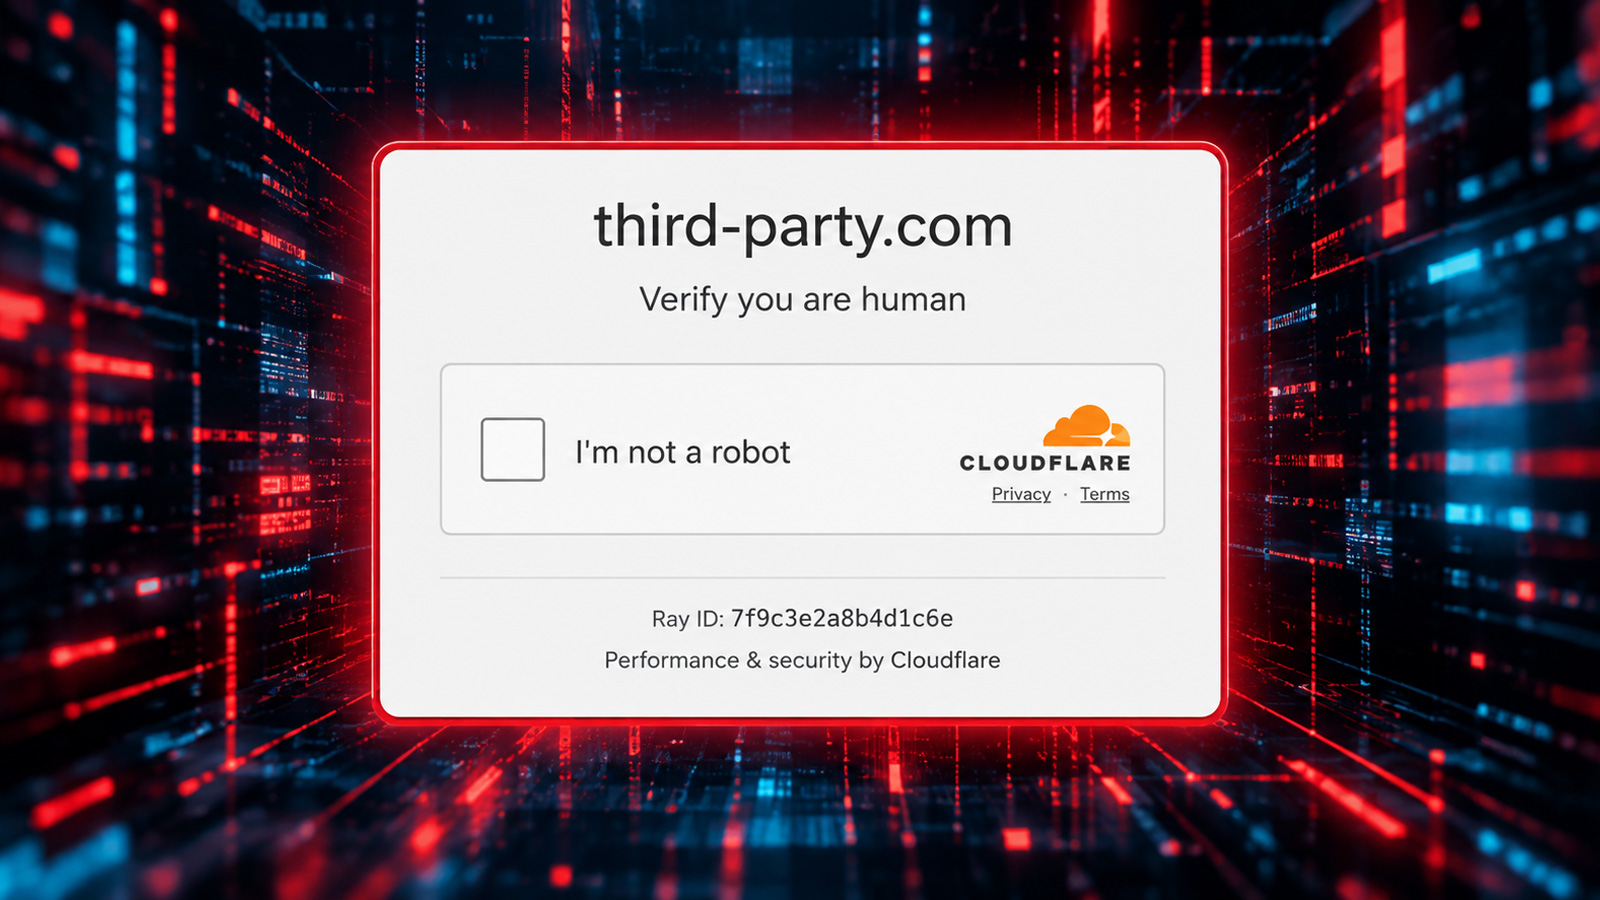
Placeholder domain used in dev docs now serves ClickFix attacks https://www.bleepingcomputer.com/news/security/placeholder-domain-used-in-dev-docs-now-serves-clickfix-attacks/
Placeholder domain used in dev docs now serves ClickFix attacks
BleepingComputer

Placeholder domain used in dev docs now serves ClickFix attacks

The "third-party.com" domain, commonly used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that attempts to trick Windows users into executing PowerShell commands.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Are we back in big tech's 'move fast and break things' era? https://www.bbc.co.uk/news/articles/c6eq8egl3wd2o
Are we back in big tech's 'move fast and break things' era?
BBC News

Are we back in big tech's 'move fast and break things' era?

Despite promises to make safe AI, examples of bots behaving badly are now coming at us thick and fast.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Measure Distant Asteroids With a DIY Rig https://spectrum.ieee.org/asteroid-shadow
Measure An Asteroid’s Shadow With a Small Telescope and Some DIY Gear
IEEE Spectrum

Measure An Asteroid’s Shadow With a Small Telescope and Some DIY Gear

Watching space rocks obscure stars is easier than you think

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Dutch government publishes call from 21 countries and the EU for international oversight of frontier AI https://thenextweb.com/news/frontier-ai-joint-statement-21-countries-eu
thenextweb.com

Dutch government publishes call from 21 countries and the EU for international oversight of frontier AI

Leaders of 21 countries and the European Commission call for mandatory testing of frontier AI and a possible international oversight body.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 2d ago
Apple says it’s tightening macOS ‘Full Disk Access’ controls due to new risks from AI agents https://techcrunch.com/2026/10/02/apple-says-its-tightening-macos-full-disk-access-controls-due-to-new-risks-from-ai-agents/
Apple says it's tightening macOS 'Full Disk Access' controls due to new risks from AI agents | TechCrunch
TechCrunch

Apple says it's tightening macOS 'Full Disk Access' controls due to new risks from AI agents | TechCrunch

Apple says it will add new controls around macOS’s Full Disk Access permission, warning that increasingly capable AI agents make broad access to users’ files, messages, mail, and browsing history riskier.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
A Look at AI Doomsday Scenarios That Researchers Say Could Put Humanity at Risk https://www.securityweek.com/a-look-at-ai-doomsday-scenarios-that-researchers-say-could-put-humanity-at-risk/
A Look at AI Doomsday Scenarios That Researchers Say Could Put Humanity at Risk
SecurityWeek

A Look at AI Doomsday Scenarios That Researchers Say Could Put Humanity at Risk

Debates over the plausibility of these doomsday scenarios have heated up since several executives endorsed slowing the technology’s development for safety reasons.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 3d ago
Boosted by @kcarruthers@infosec.exchange
Robotaxi operators will face fines for blocking first responders https://techcrunch.com/2026/10/01/robotaxi-operators-will-face-fines-for-blocking-first-responders/
Robotaxi operators will face fines for blocking first responders | TechCrunch
TechCrunch

Robotaxi operators will face fines for blocking first responders | TechCrunch

A new California law places new rules on autonomous vehicles operators.

0
0
2
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
OpenAI names the four things it wants safety assessors to test https://thenextweb.com/news/openai-third-party-assessment-priorities-principles
thenextweb.com

OpenAI names the four things it wants safety assessors to test

OpenAI has published the four areas and seven principles it wants outside safety assessors to work to, including time to fix findings before publication.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Why the satellite communications boom needs stronger cyber resilience https://www.weforum.org/stories/cybersecurity/satellite-communications-cyber-resilience/
weforum.org
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Amazon blocks Meta’s Muse and accuses Perplexity of misleading a court https://thenextweb.com/news/amazon-blocks-muse-perplexity-amended-complaint
thenextweb.com

Amazon blocks Meta’s Muse and accuses Perplexity of misleading a court

Amazon blocks Muse from its store and says Perplexity told the Ninth Circuit something its own servers contradicted.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
More Than a Third of Industrial Orgs See Cybersecurity Risk as a Top Obstacle to Growth, Study Finds https://www.darkreading.com/cyber-risk/third-industrial-orgs-see-cybersecurity-risk-top-obstacle
darkreading.com
0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
Rogue external MFA providers can steal passwords during logins https://www.bleepingcomputer.com/news/security/rogue-external-mfa-providers-can-steal-passwords-during-logins/
Rogue external MFA providers can steal passwords during logins
BleepingComputer

Rogue external MFA providers can steal passwords during logins

Security researchers developed an attack that lets hackers with privileged access register a rogue external MFA provider that steals users' passwords during legitimate login attempts.

0
0
0
0
Open post
Patrick C Miller :donor: @patrickcmiller@infosec.exchange
· 1w ago
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session https://thehackernews.com/2026/09/wordpress-comment2shell-flaw-can-turn.html
thehackernews.com

WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session

0
0
1
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 07:21:09 UTC