Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Ivan Ožić Bebek

@obivan@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

:hacker_h: :hacker_a: :hacker_c: :hacker_k: :hacker_e: :hacker_r: :hacker_m: :hacker_a: :hacker_n:

204 Followers
128 Following
50 Posts
Joined November 05, 2022
Location:
Zagreb, Croatia
Web:
https://iozicbeb.github.io
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Apparently Windows 11 writes full WebAuthn assertions into the event log https://specterops.io/wp-content/uploads/sites/3/2026/08/Pass-the-Passkey_A4_v2.pdf
specterops.io
13
2
10
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 1mo ago
The firmware security analyzer https://github.com/e-m-b-a/emba
GitHub

GitHub - e-m-b-a/emba: EMBA - The firmware security analyzer

EMBA - The firmware security analyzer. Contribute to e-m-b-a/emba development by creating an account on GitHub.

1
0
1
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
This is interesting, I wasn't aware that clipboard inside of VM listens for host clipboard all the time. Same behaviour on VMware Workstation. https://windows-internals.com/random-windows-things-part-2-unexpected-clipboard-data-behavior/
windows-internals.com

Random Windows Things Part 2: Unexpected Clipboard Data Behavior – Winsider Seminars & Solutions Inc.

3
0
2
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Identity Crisis: Novel Vulnerabilities Leading to Kerberos Downgrade, DoS, and Full Domain Takeover https://www.semperis.com/blog/identity-crisis-novel-vulnerabilities-leading-to-kerberos-downgrade-dos-and-full-domain-takeover/
AD Research: Two new vulnerabilities could lead to full domain takeover
Semperis

AD Research: Two new vulnerabilities could lead to full domain takeover

Read the research that led to the discovery of Active Directory privilege escalation vulnerabilities CVE-2026-25177 and CVE-2026-27912.

1
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Borrowing Windows Hello keys for authentication and persistence https://dirkjanm.io/borrowing-windows-hello-keys/
dirkjanm.io
1
0
1
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Can we *really* automate with AI? https://blog.ninetailedf0x.com/posts/can-we-really-automate-with-ai-p2/
NineTailedF0x Security Blog

Can we *really* automate with AI?

I roasted every AI pentester on GitHub in P1, so heres how I actually built mine: real Burp Suite, three MCP servers, machine-verified evidence, and a coverage gate the LLM cant talk its way past.

1
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Special Token Injection (STI) Attack Guide https://blog.sentry.security/special-token-injection-sti-attack-guide/
Special Token Injection (STI) Attack Guide
Checkmate

Special Token Injection (STI) Attack Guide

Large Language Models introduce security issues reminiscent of early-2000s software bugs. Special Token Injection (STI) exploits how LLMs parse structured prompts. This post breaks down what STI is, how it works, where it appears, and why it matters—through a pentester’s lens.

1
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
WDAC / AppLocker Bypass Capability Scanner https://github.com/AlloySecureGroup/LOL-Forager
GitHub

GitHub - AlloySecureGroup/LOL-Forager: Living off the Land Binary Capability Discovery

Living off the Land Binary Capability Discovery. Contribute to AlloySecureGroup/LOL-Forager development by creating an account on GitHub.

1
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
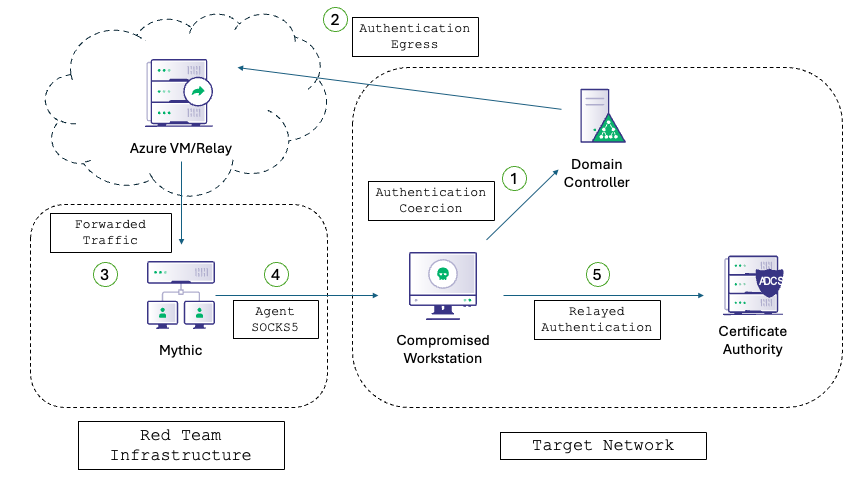
There and Back Again: An Operators Guide on NTLM Relaying Egress https://specterops.io/blog/2026/07/15/there-and-back-again-an-operators-guide-on-ntlm-relaying-egress/
There and Back Again: An Operators Guide on NTLM Relaying Egress
SpecterOps

There and Back Again: An Operators Guide on NTLM Relaying Egress

See how the "There and Back Again" NTLM relay attack coerces outbound auth to compromise Active Directory, plus the defenses that stop it.

1
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
The Bug Bounty Singularity: Our Hackbot https://josephthacker.com/hacking/2026/07/01/we-built-a-hackbot.html
The Bug Bounty Singularity: Our Hackbot
josephthacker.com

The Bug Bounty Singularity: Our Hackbot

This past December, it became feasible for any skilled hacker to scale up a hacking agent, spending hundreds in token cost to find thousands in bounties. I call this the “Bug Bounty Singularity”. This is the story of JD (xssdoctor) and I building a hackbot which found 126 bugs in the last 5 months.

1
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
Roblox, Minecraft, and the Insidious Internet for Children https://censys.com/blog/roblox-minecraft-and-the-insidious-internet-for-children/
Roblox, Minecraft, and the Insidious Internet for Children - Censys
Censys

Roblox, Minecraft, and the Insidious Internet for Children - Censys

An exploration of Roblox and Minecraft offerwalls and phishing lures — infrastructure that isn’t well covered by conventional threat intelligence.

1
0
1
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
FastJson 1.2.83 RCE (CVE-2026-16723) https://fearsoff.org/research/fastjson-1-2-83-rce
FastJson 1.2.83 Remote Code Execution
fearsoff.org

FastJson 1.2.83 Remote Code Execution

Turning fastjson 1.2.83 into remote code execution with AutoType off and no gadget on the classpath: an SSRF inside checkAutoType, the @JSONType bypass, and a /proc/self/fd trick that carries it from JDK 8 to 25. By FearsOff.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
The New Hotness in Phishing: Device Code Attacks in M365 https://trustedsec.com/blog/the-new-hotness-in-phishing-device-code-attacks-in-m365
trustedsec.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
PoC for CVE-2026-61511, unauthenticated vBulletin RCE https://ssd-disclosure.com/vbulletin-runtime-template-runmaths-preauth-rce/
ssd-disclosure.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
CVE-2026-50469 - ProjFS File Delete https://bad-jubies.github.io/projected-file-system-file-delete-cve-2026-50469
bad-jubies.github.io

CVE-2026-50469 - ProjFS File Delete

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Introducing Burp AT: agentic AI, built on two decades of Burp Suite https://portswigger.net/blog/introducing-burp-at
Introducing Burp AT: agentic AI, built on two decades of Burp Suite
PortSwigger Blog

Introducing Burp AT: agentic AI, built on two decades of Burp Suite

Introduction of Burp AT. PortSwigger's agentic AI capabilities, now accessible in Burp Suite Professional. Public beta now open.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Did an AI Really Hack Hugging Face? https://youtu.be/q2KCrmQz9WE

Did an AI Really Hack Hugging Face?

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
Poc for CVE-2026-48282, a path traversal vulnerability in Adobe ColdFusion's Remote Development Service (RDS) https://github.com/imbas007/CVE-2026-48282
GitHub

GitHub - imbas007/CVE-2026-48282

Contribute to imbas007/CVE-2026-48282 development by creating an account on GitHub.

0
1
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Open Weights and American AI Leadership https://www.microsoft.com/en-us/corporate-responsibility/topics/open-weight/
Open Weights and American AI Leadership
Microsoft Corporate Responsibility

Open Weights and American AI Leadership

Open weight AI can expand access, strengthen competition, improve security, and help sustain American AI leadership.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
CVE-2025-45422: Proximus b-box UPnP Persistence & Access Control Bypass https://github.com/Cedrico03/CVE-2025-45422---Bbox
github.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
SharePoint SE preauth RCE PoC https://gist.github.com/testanull/0868e02d81d57d6c59a91261969f7f81
gist.github.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
The AI Pentesting Winners May Not Be AI Startups https://pentesterlab.com/blog/the-ai-pentesting-winners-may-not-be-ai-startups
pentesterlab.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
wp2shell (CVE-2026-63030 + CVE-2026-60137): Independent Root Cause Analysis https://github.com/tcyph3r/wp2shell-cve-2026-63030-root-cause
GitHub

GitHub - tcyph3r/wp2shell-cve-2026-63030-root-cause

Contribute to tcyph3r/wp2shell-cve-2026-63030-root-cause development by creating an account on GitHub.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Authentication bypass for Check Point Security Management Server and Multi-Domain Security Management Server https://github.com/sfewer-r7/CVE-2026-16232
GitHub

GitHub - sfewer-r7/CVE-2026-16232: A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.

A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token. - sfewer-r7/CVE-2026-16232

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
So OpenAI (Sol) hacked HuggingFace? https://openai.com/index/hugging-face-model-evaluation-security-incident/
openai.com
0
1
1
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 1mo ago
Debian LPE PoC (CVE-2026-80714) https://github.com/NebuSec/CyberMeowfia/tree/main/security-research/Linux-CVE-2026-80714-Debian-6.12.101
github.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
AdaptixC2 & Domain Trusts: Chained Compromise of a Multi-Forest Active Directory Environment https://medium.com/@Xotourliff/adaptixc2-domain-trusts-chained-compromise-of-a-multi-forest-active-directory-environment-8e9f9dfa2ff7
medium.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
A deep dive into rasta-mouse's Crystal-Loaders https://racoten.github.io/Self-Taught-Course/Project/CrystalLoaders/CrystalLoaders_index.html
racoten.github.io
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Security incident disclosure — July 2026 https://huggingface.co/blog/security-incident-july-2026
Security incident disclosure — July 2026
huggingface.co

Security incident disclosure — July 2026

We’re on a journey to advance and democratize artificial intelligence through open source and open science.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
Finding SOCKS with Proxywatch https://specterops.io/blog/2026/07/09/finding-socks-with-proxywatch/#
specterops.io
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Related to ESC17, this tool opens so many possibilities for man-in-the-middle and relay attacks in Active Directory https://github.com/qu35t-code/adecrypt
github.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Custom Adaptix-compatible C2 agent - PIC beacon + Stardust UDRL + Go extender plugins https://github.com/MaorSabag/NaX
GitHub

GitHub - MaorSabag/NaX: Custom Adaptix-compatible C2 agent - PIC beacon + Stardust UDRL + Go extender plugins

Custom Adaptix-compatible C2 agent - PIC beacon + Stardust UDRL + Go extender plugins - MaorSabag/NaX

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Pure-impacket parallel local-admin discovery via RBCD https://github.com/nnnnino/rbcdbrute
GitHub

GitHub - nnnnino/rbcdbrute: Pure-impacket parallel local-admin discovery via RBCD.

Pure-impacket parallel local-admin discovery via RBCD. - nnnnino/rbcdbrute

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
My team placed second on Rogue Labs CTF! It was a huge lab with 29 hops, a fun mix of initial access, privilege escalation, lateral movement and pivoting techniques. https://ctf.roguelabs.io/
ctf.roguelabs.io
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
The Biggest HackRF Upgrade in Over a Decade https://www.youtube.com/watch?v=n-khaJyY50Y
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
The SID that wasn't there: bypassing KB5014754 to Domain Admin on a fully patched AD CS https://0xmaz.me/posts/certsrv-id-cmc-addExtensions-KB5014754-bypass/
Mohamed Alzhrani

The SID that wasn’t there: bypassing KB5014754 to Domain Admin on a fully patched AD CS

A fully patched AD CS issued me a client-auth certificate with no szOID_NTDS_CA_SECURITY_EXT in it at all. No requester SID. Not mine, not anyone’s. The extension that is the entire point of KB5014754 was simply absent from the issued certificate.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
Windows Privilege Abuse: How Attackers Escalate from Accounts with Dangerous Rights to Active Directory Compromise https://www.semperis.com/blog/windows-privilege-abuse-can-lead-to-active-directory-compromise/
Windows Privilege Abuse: Attackers' Path to Active Directory Compromise
Semperis

Windows Privilege Abuse: Attackers' Path to Active Directory Compromise

Learn how attackers exploit Windows privileges to escalate and extend their foothold in Active Directory ... even in well-patched environments.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
ESC17 - Beyond WSUS https://research.qu35t.pw/en/series/esc17-beyond-wsus/
research.qu35t.pw
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Clustered Points of Failure https://specterops.io/blog/2026/07/29/clustered-points-of-failure/#
Clustered Points of Failure
SpecterOps

Clustered Points of Failure

Windows Server Failover Clusters share credentials across every node: compromise one, and you compromise the entire cluster

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
GitLab Oj RCE PoC https://github.com/wupco/gitlab-rce-demo
GitHub

GitHub - wupco/gitlab-rce-demo

Contribute to wupco/gitlab-rce-demo development by creating an account on GitHub.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Windows Privileges Explained: SeDebugPrivilege and AdjustTokenPrivileges in C++ https://trainsec.net/library/windows-internals/windows-privileges-sedebugprivilege/
Windows Privileges Explained: SeDebugPrivilege and AdjustTokenPrivileges in C++ » TrainSec
TrainSec - CyberSecurity online training

Windows Privileges Explained: SeDebugPrivilege and AdjustTokenPrivileges in C++ » TrainSec

Pavel Yosifovich explains what Windows privileges are, why they live in the token, and how to enable SeDebugPrivilege in C++ with OpenProcessToken, LookupPrivilegeValue, and AdjustTokenPrivileges.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
Hook Chains (how I built Crystal Kit incorrectly*) https://rastamouse.me/cpl-hook-chains/
Hook Chains (how I built Crystal Kit incorrectly*)
Rasta Mouse

Hook Chains (how I built Crystal Kit incorrectly*)

Despite what some would lead you to believe, Crystal Kit is not, and was never intended to be, an all-encompassing nirvana of evasion tradecraft. It was a simple project to experiment with Crystal Palace (CPL) by applying evasion tradecraft to Cobalt Strike's Beacon. There are some capabilities of

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Harnessing the Power of Cobalt Strike Profiles for EDR Evasion – Part 3 https://whiteknightlabs.com/2026/06/15/harnessing-the-power-of-cobalt-strike-profiles-for-edr-evasion-part-3/
Harnessing the Power of Cobalt Strike Profiles for EDR Evasion – Part 3 | White Knight Labs
White Knight Labs

Harnessing the Power of Cobalt Strike Profiles for EDR Evasion – Part 3 | White Knight Labs

This blog post is a continuation of the previous entry “Harnessing the Power of Cobalt Strike Profiles for EDR Evasion“ and its follow-up, Part 2. Following

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Privacy-Perserving Attack Path Analysis for Bloodhound https://github.com/abhisek3122/HoundMasker
GitHub

GitHub - abhisek3122/HoundMasker: Privacy-Perserving Attack Path Analysis for Bloodhound

Privacy-Perserving Attack Path Analysis for Bloodhound - abhisek3122/HoundMasker

0
0
1
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
TLS Encryption and Compliance https://trustedsec.com/blog/tls-encryption-and-compliance
trustedsec.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Pentest and Red Team TTPs with RustPack https://www.msecops.de/blog/posts/rustpack-features/
msecops.de

Pentest and Red Team TTPs with RustPack · MSec Operations Blog

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 3mo ago
White Knight Labs has released a free AI for Offensive Security course https://training.whiteknightlabs.com/academy#
training.whiteknightlabs.com
0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
PoC's for nginx RCE (CVE-2026-42530, CVE-2026-42533) https://github.com/DepthFirstDisclosures/Nginx-Rift/
GitHub

GitHub - DepthFirstDisclosures/Nginx-Rift: NGINX RCE exploits

NGINX RCE exploits. Contribute to DepthFirstDisclosures/Nginx-Rift development by creating an account on GitHub.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
AI Assisted Vulnerability Research on Embedded Targets https://quentinkaiser.be/security/2026/07/18/ia-assisted-vuln-research/
AI Assisted Vulnerability Research on Embedded Targets
QTNKSR

AI Assisted Vulnerability Research on Embedded Targets

I gave an AI agent access to a cable modem, a serial console, Ghidra, and a custom GDB stub, then asked it to reverse the firmware and hunt for bugs. It re-discovered known vulnerabilities, found new ones, and wrote working exploits. This post covers the setup, what it managed to do on its own, and where I still had to step in. The real problem is that the same approach now works on millions of devices nobody plans to fix.

0
0
0
0
Open post
Ivan Ožić Bebek @obivan@infosec.exchange
· 2mo ago
Sophos Intercept X: A Technical Bypass https://yenn503.github.io/posts/sophos-intercept-x-bypass/
Sophos Intercept X: A Technical Bypass
JYenn

Sophos Intercept X: A Technical Bypass

Why Zig I got bored again. So I started learning Zig syntax and how it could be beneficial when it comes to writing loaders. I just wanted something new to try, and with Zig being early days still I thought why not. There aren’t many variations out there currently, so in terms of signatures and pattern detection Zig plays a role here although the underlying behaviour is the same. If you’re new to Windows internals there are some amazing resources and tools out there to help, such as SysWhispers

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 09:38:10 UTC