Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Matthew McPherrin

@mattm@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

SRE at Let's Encrypt, though these toots are my own.

446 Followers
312 Following
13 Posts
Joined November 10, 2022
Open post
Matthew McPherrin @mattm@infosec.exchange
· 2mo ago
I’m at BSidesLV and DEFCON this week. Find me and say hello!
6
0
2
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 6mo ago

Have you ever needed to make sure your website has an expired or revoked certificate? No, that's not a problem people have. But we do, because CAs have to run test sites with them.

I just wrote a blog post post about this problem, and our new tool that we use to host ours:

https://letsencrypt.org/2026/04/10/test-sites

The difficulty of making sure your website is broken
Let's Encrypt

The difficulty of making sure your website is broken

Have you ever needed to make sure your website has a broken certificate? While many tools exist to help run an HTTPS server with valid certificates, there aren’t tools to make sure your certificate is revoked or expired. This is not a problem most people have. Tools to help manage certificates are always focused on avoiding those problems, not creating them. Let’s Encrypt is a Certificate Authority, and so we have unusual problems we need to solve.

20
0
15
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 2mo ago
The headphones being used for DEFCON talks are stereo FM, easily received on your SDR of choice CH 1: 920.1Mhz CH 2: 920.7Mhz CH 3: 921.2Mhz CH 4: 921.9Mhz CH 5: 922.3Mhz CH 6: 922.8Mhz CH 7: 923.4Mhz CH 8: 924.2Mhz CH 9: 924.7Mhz CH10: 925.9Mhz CHA1: 920.5Mhz CHA2: 922.4Mhz CHA3: 926.7Mhz
GitHub

GitHub - mcpherrinm/defcon-headphones: DEFCON 34 Headphones

DEFCON 34 Headphones. Contribute to mcpherrinm/defcon-headphones development by creating an account on GitHub.

2
0
0
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 4mo ago

Huh, that’s a message I haven’t seen before

5
0
0
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 6mo ago

Firefox's new "security alert" and "no connection" error page illustrations are pretty great

6
0
5
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 19mo ago

We've issued our first short-lived (6 day) certificate! https://letsencrypt.org/2025/02/20/first-short-lived-cert-issued/

We Issued Our First Six Day Cert
Let's Encrypt

We Issued Our First Six Day Cert

Earlier this year we announced our intention to introduce short-lived certificates with lifetimes of six days as an option for our subscribers. Yesterday we issued our first short-lived certificate. You can see the certificate at the bottom of our post, or here thanks to Certificate Transparency logs. We issued it to ourselves and then immediately revoked it so we can observe the certificate’s whole lifecycle. This is the first step towards making short-lived certificates available to all subscr

23
0
14
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 18mo ago

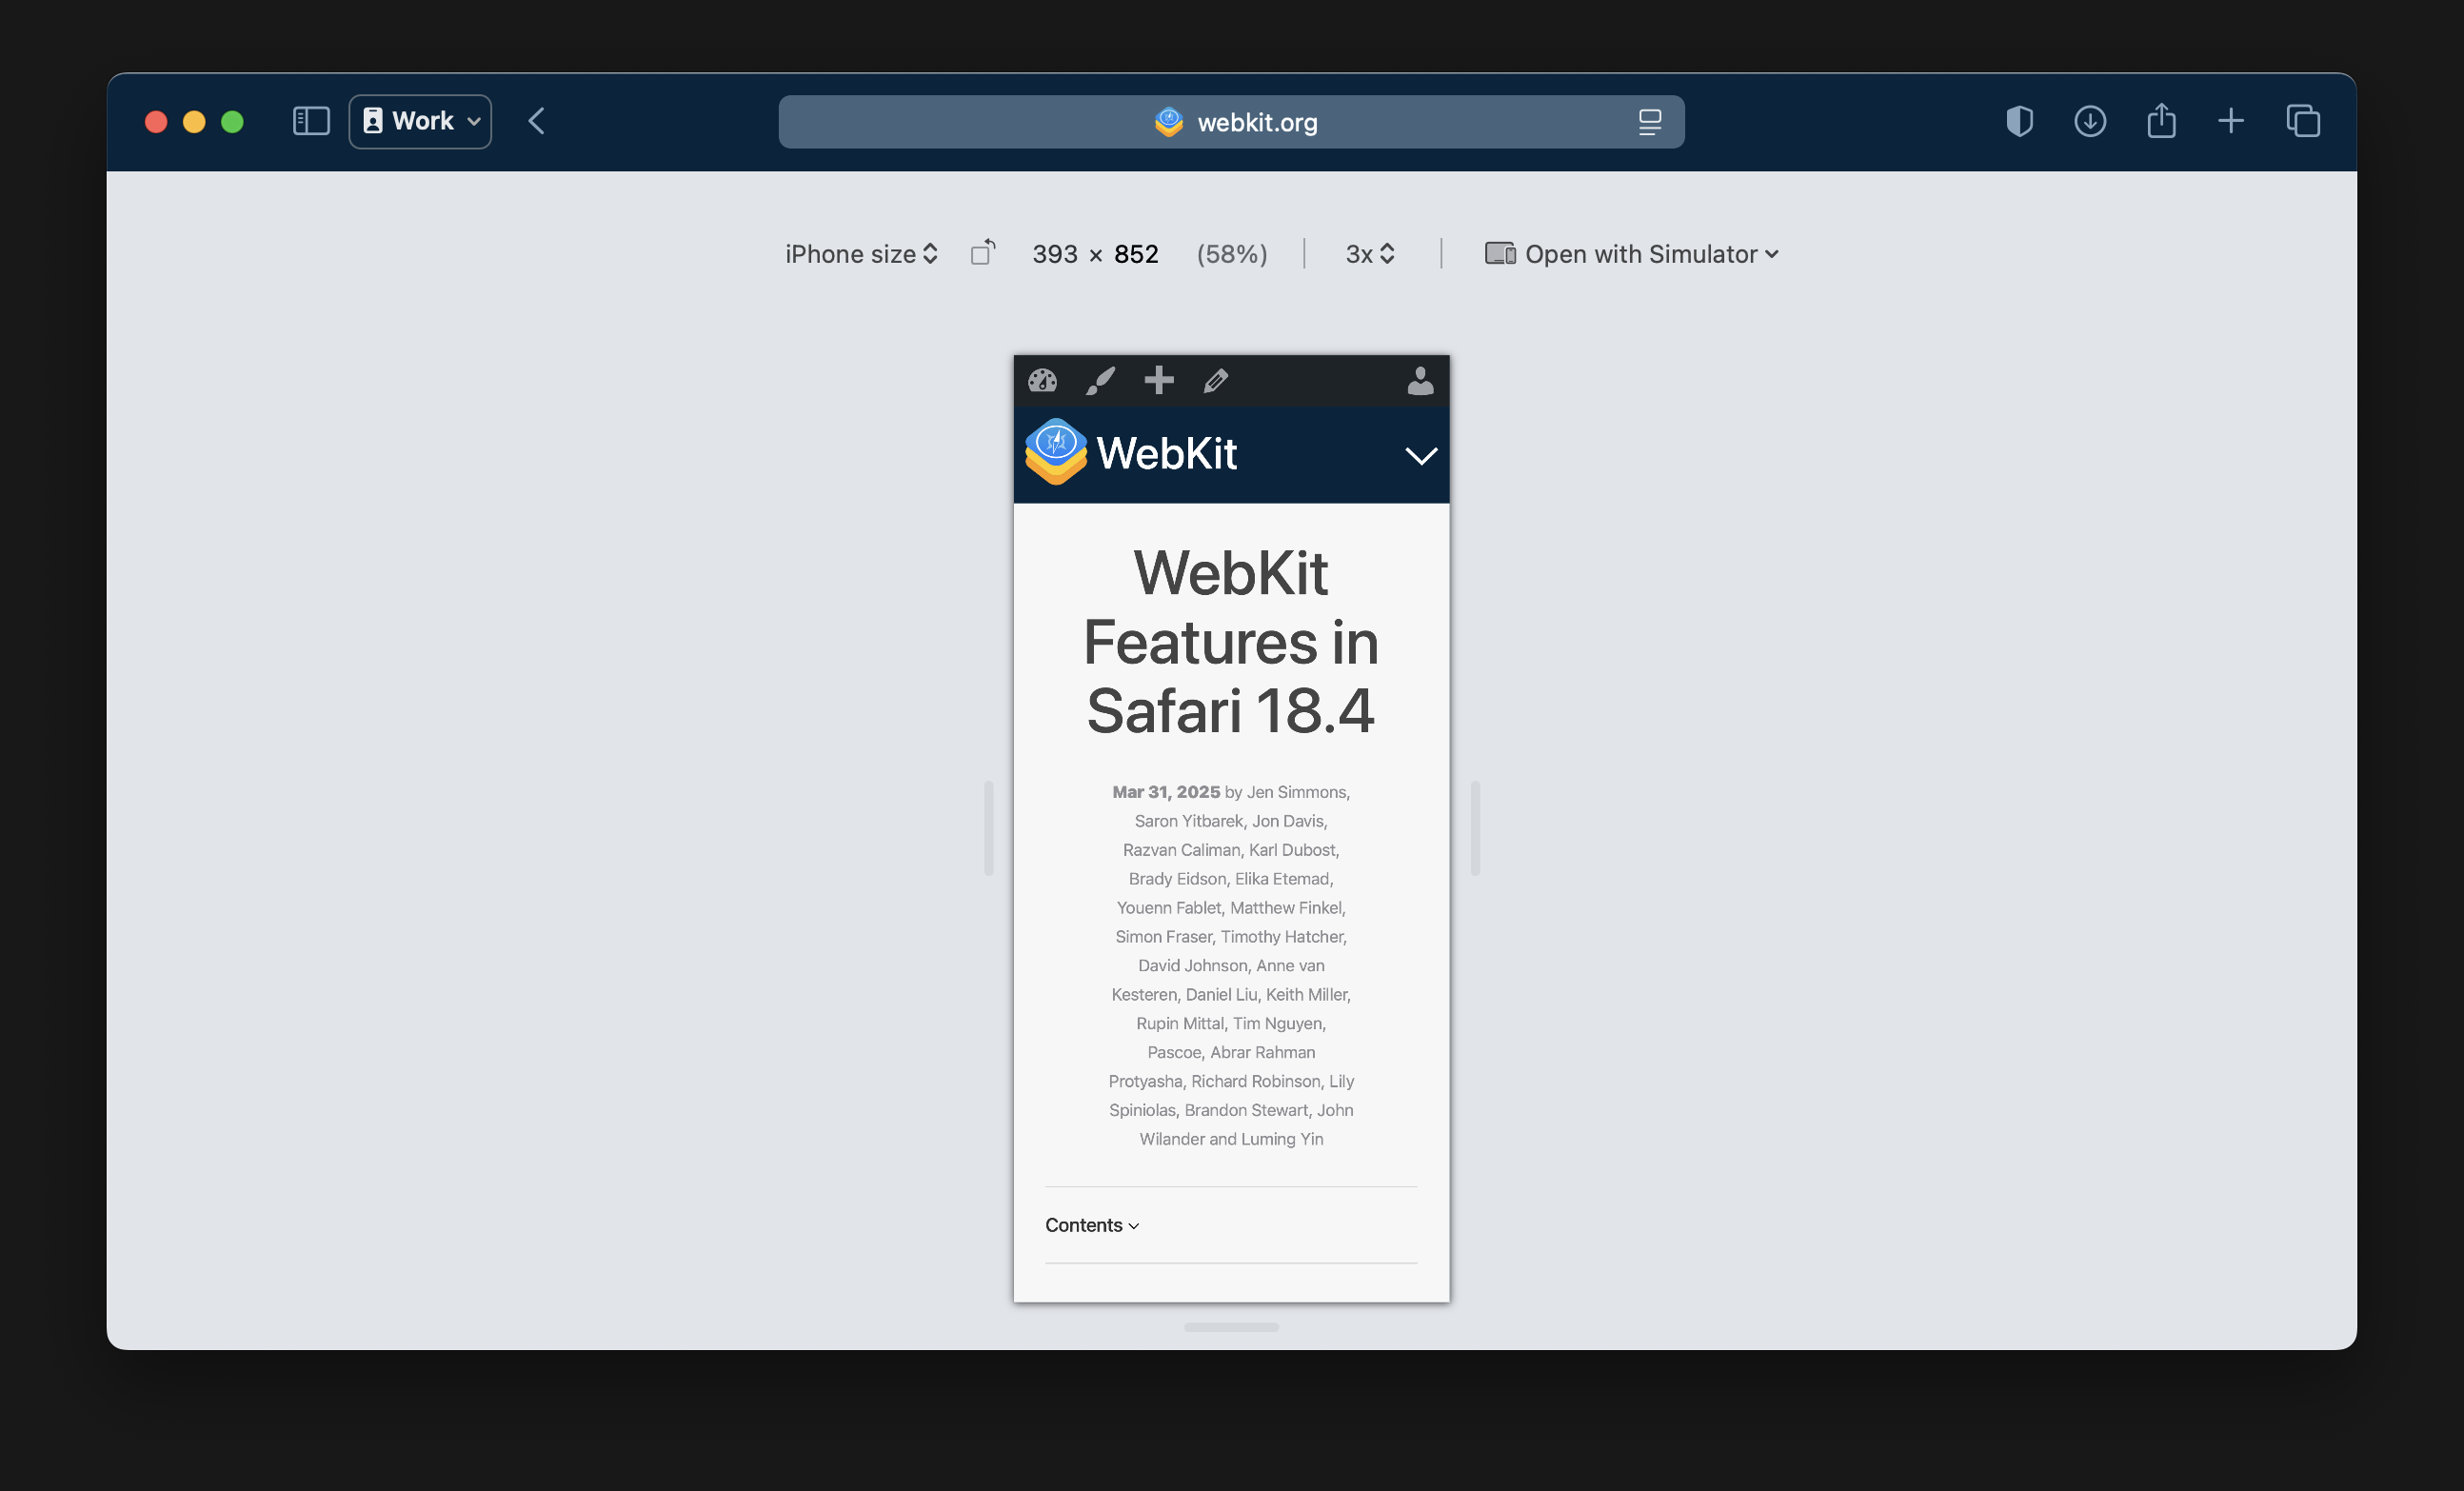
Of all the things I didn’t expect to ever happen, iOS Safari actually got a certificate viewer in 18.4! https://webkit.org/blog/16574/webkit-features-in-safari-18-4/#connection-security

WebKit Features in Safari 18.4
WebKit

WebKit Features in Safari 18.4

Safari 18.4 is here!

12
0
5
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 20mo ago

Chrome has published version 1.6 of their root store policy.

Notably, this contains a timeline for deprecating use of the TLS Client Auth extended-key-usage inside the PKIs included in their program.
If you currently use TLS Client Auth from a publicly trusted CA, you may need to take action.

> ... certificates issued on or after June 15, 2026 MUST include the extendedKeyUsage extension and only assert an extendedKeyUsage purpose of id-kp-serverAuth.

https://www.chromium.org/Home/chromium-security/root-ca-policy/#32-promote-use-of-dedicated-tls-server-authentication-pki-hierarchies

chromium.org
4
3
3
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 16mo ago

Firefox's telemetry has data on how many times a CA is used to successfully validate certificates. This is a pretty good measure for how "big" a CA is. The data is hard to view in Mozilla's site, so I've made a script to combine a few data sources and graph it! https://github.com/mcpherrinm/cert-count

GitHub

GitHub - mcpherrinm/cert-count

Contribute to mcpherrinm/cert-count development by creating an account on GitHub.

2
1
0
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 16mo ago

@cybeej@infosec.exchange Internet Security Research Group is the name of the organization that runs Let's Encrypt (ie, in #3 position)

1
0
0
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 16mo ago

Inspired by the classic xeyes program, I made a thing:

ssh teyes.fly.dev

Or go install github.com/mcpherrinm/teyes@latest && teyes

Give your mouse a wiggle over the terminal!

1
0
0
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 17mo ago

I'll be speaking at the Ontario Cryptography Day!

https://ontario-crypto-day.github.io/

Where: University of Waterloo Davis Centre (DC) 1301 and 1302
When: Friday, June 6, 2025, from 10am to approx. 4:30pm

I hope anyone in the area interested in cryptography is able to attend. It's a free event, but registration is required.
Ontario Cryptography Day

Ontario Cryptography Day

Wednesday, December 9, 2026 • University of Waterloo

1
0
2
0
Open post
Matthew McPherrin @mattm@infosec.exchange
· 37mo ago
Replying to on infosec.exchange
Of course the malware was only successful because of a browser exploit, but plaintext HTTP allows much wider exposure to network-based attackers who can freely inject content.
0
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 09:49:54 UTC