Remote
Intego Mac Security 
@intego@infosec.exchange
Intego is the leader in Mac security, protecting Apple users from the dangers of the Internet since 1997. Follow for The Mac Security Blog and Podcast updates. https://www.intego.com
83 Followers
11 Following
20 Posts
Joined November 08, 2022
🔒 Podcast:
Homepage:
:twitter: :facebook: etc.:
Overall takeaway:
macOS security threats are not standing still. Attackers are leaning harder on trusted tools, fake apps, and social engineering.
That makes patching, careful downloads, and clear user education more important than ever.
#macOS #iOS #AppleSecurity #MacSecurity #Cybersecurity
Open post
Replying to
2/8 XCSSET is back.
Unit 42 analyzed a new version of this Mac malware, which hides inside Xcode projects. When a developer builds an infected project, the malware runs and can infect other Xcode projects on the Mac. Those projects can then spread through shared repositories.
https://unit42.paloaltonetworks.com/xcsset-v40-malware-analysis/
0
6
0
0
Open post
Replying to
3/8 Apple addressed 210 unique vulnerabilities across its July security updates. The relevant releases include:
• iOS and iPadOS 26.6
• macOS Tahoe 26.6
• macOS Sequoia 15.7.8
• macOS Sonoma 14.8.8
Apple’s advisories don’t identify any of the vulnerabilities as actively exploited.
0
5
0
0
Open post
Replying to
5/8 Another campaign used malicious ads and search results to send Mac users to a fake full-screen restart or update sequence.
The screen was actually a web page. It copied a command to the clipboard, then told the user to open Terminal and paste it in. Following those instructions installed the malware.
0
3
0
0
Open post
Replying to
4/8 One notable fix affects ImageIO, which Apple devices use to process images. A maliciously crafted image could potentially allow code execution.
Because images may be processed automatically in apps and previews, researchers consider this one of the more significant fixes in the release.
https://www.thezdi.com/blog/2026/7/29/the-july-2026-apple-security-update-review
0
4
0
0
Open post
Replying to
8/8 Three things to do this week:
• Install the latest update available for your iPhone, iPad, or Mac.
• Never paste a Terminal command copied from a website claiming to update or restart your Mac.
• If you use Xcode, inspect unfamiliar projects and unexpected build phases before building or sharing them.
Learn more about protecting your Mac from social engineering attacks:
https://www.intego.com/mac-security-blog/mac-security-blog-mac-social-engineering-attacks/
0
0
0
0
Open post
Replying to
7/8 Apple’s bug-reporting limits also came under scrutiny.
The company introduced submission caps after receiving a surge of low-quality, AI-generated reports. Those limits then prevented a research company that had submitted many automated reports from reporting a genuine Mac Screen Sharing flaw. Apple independently found and fixed it in macOS Tahoe 26.6.
0
1
0
0
Open post
Replying to
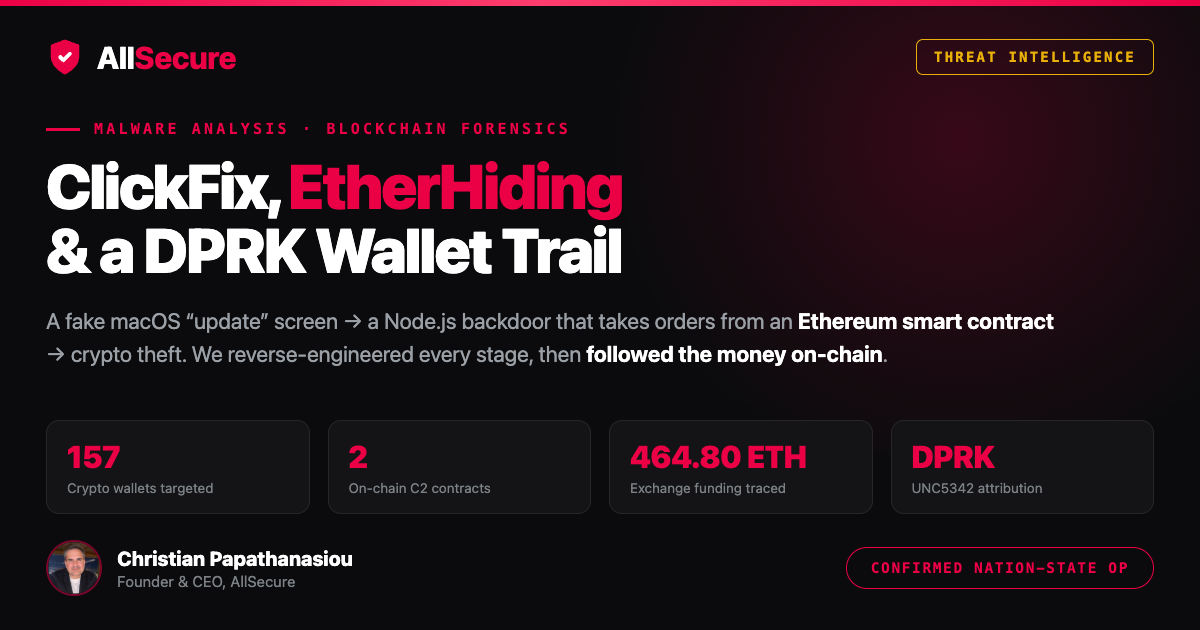
6/8 The malware could steal cryptocurrency wallet data, browser information, and developer credentials. It also used Ethereum smart contracts to retrieve its current command-and-control server addresses, making its infrastructure easier for the attackers to change.
https://www.allsecure.io/blog/clickfix-etherhiding-dprk-wallet/
0
2
0
0
Open post
Weekly macOS & iOS threat update: June 29–July 6, 2026
A few notable developments this week:
Remote support tools are being abused, macOS infostealers are getting more targeted, ClickFix-style attacks are adapting, and Apple has shipped a major security update cycle.
Thread below.
0
0
0
0
Open post
Remote support tools remain a high-value target.
Attackers are exploiting a critical SimpleHelp vulnerability to deploy Djinn Stealer, a newly reported cross-platform infostealer targeting macOS, Windows, and Linux.
The key point: attackers don’t always need to break in through “unknown” tools. They often abuse trusted software and remote access workflows users already recognize.
Source: BleepingComputer: Hackers exploit critical SimpleHelp flaw to deploy new Djinn infostealer, TaskWeaver malware
0
0
0
0
Open post
macOS infostealers continue to evolve.
Jamf Threat Labs reported PamStealer, a Rust-based macOS infostealer disguised as the Maccy clipboard manager.
The campaign is a reminder that fake or tampered apps can look familiar, especially when they borrow the name of a popular utility.
Source: Jamf Threat Labs
0
0
0
0
Open post
Apple shipped a major security update cycle.
The latest iOS, iPadOS, macOS Tahoe, and Safari updates address dozens of vulnerabilities, including kernel and WebKit issues.
Users should update supported devices as soon as practical.
Sources: Apple / Zero Day Initiative
0
0
0
0
Open post
CrashStealer disguises itself as an Apple crash-reporting tool.
The malware was distributed through a signed and Apple-notarized app and can steal browser data, Keychain information, password-manager data, and cryptocurrency wallet files.
It’s another reminder that a familiar name and a macOS security check don’t guarantee an app is safe.
0
0
0
0
Open post
Weekly macOS & iOS threat update: July 13–20, 2026
A newly documented Mac infostealer called ClickLock is using fake human-verification pages to trick people into pasting malicious commands into Terminal.
Once launched, it can repeatedly close Finder, Terminal, Activity Monitor, and System Settings while displaying a fake password prompt. It also targets browser data, the macOS Keychain, password managers, and cryptocurrency wallets.
The practical rule is simple: a legitimate website won’t ask you to paste a command into Terminal to prove you’re human.
Apple is also facing a proposed class action over Hide My Email. The lawsuit alleges that some masked addresses could be linked to a user’s real email address. These claims haven’t been proven in court.
#MacSecurity #macOS #Cybersecurity
0
0
0
0
Open post
4/8 One notable fix affects ImageIO, which Apple devices use to process images. A maliciously crafted image could potentially allow code execution.
Because images may be processed automatically in apps and previews, researchers consider this one of the more significant fixes in the release.
https://www.thezdi.com/blog/2026/7/29/the-july-2026-apple-security-update-review
0
0
0
0
Open post
3/8 Apple addressed 210 unique vulnerabilities across its July security updates. The relevant releases include:
• iOS and iPadOS 26.6
• macOS Tahoe 26.6
• macOS Sequoia 15.7.8
• macOS Sonoma 14.8.8
Apple’s advisories don’t identify any of the vulnerabilities as actively exploited.
0
0
0
0
Open post
6/8 The malware could steal cryptocurrency wallet data, browser information, and developer credentials. It also used Ethereum smart contracts to retrieve its current command-and-control server addresses, making its infrastructure easier for the attackers to change.
https://www.allsecure.io/blog/clickfix-etherhiding-dprk-wallet/
0
0
0
0
Open post
5/8 Another campaign used malicious ads and search results to send Mac users to a fake full-screen restart or update sequence.
The screen was actually a web page. It copied a command to the clipboard, then told the user to open Terminal and paste it in. Following those instructions installed the malware.
0
0
0
0
Open post
7/8 Apple’s bug-reporting limits also came under scrutiny.
The company introduced submission caps after receiving a surge of low-quality, AI-generated reports. Those limits then prevented a research company that had submitted many automated reports from reporting a genuine Mac Screen Sharing flaw. Apple independently found and fixed it in macOS Tahoe 26.6.
0
0
0
0