Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

DarkWebSonar

@darkwebsonar@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Advanced threat intelligence platform monitoring dark web activity, data breaches, and DDoS attacks.

100 Followers
0 Following
50 Posts
Joined October 23, 2025
website:
https://darkwebsonar.io/
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
Carding incidents surged to 388 this week, up 557.6% from the previous 7 days. Financial Services saw the sharpest pressure, climbing to 395 incidents with a 226.4% increase. #Carding #FinancialServices #ThreatIntel
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a data breach claim by expl0itwastaken listing AdvancedHealth, a Tennessee-based physician group. The actor claims access to over 1.5 million patient records, with a 10,000-line sample posted. We've logged 1 incident from this actor in the past 7 days across our monitoring. #DataBreach #Healthcare #ThreatIntel Details + live feed → https://go.darkwebsonar.io/expl0itwastaken-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇲🇽 We tracked a data breach claim by homercracker listing CADPE, the Michoacán State Government's procurement portal in Mexico. The actor claims 58GB+ of data including INE national IDs, fiscal records, and documents tied to government suppliers and contractors. We've logged 5 homercracker listings in the past 30 days, all government sector. #DataBreach #Government #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/homercracker-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2w ago
🇮🇩 We tracked a data breach claim by DBHunter listing Universitas Singaperbangsa Karawang (UNSIKA), an Indonesian university. The actor claims to have accessed a database containing lecturer personal information: names, employee IDs, national ID numbers, study programs, and email addresses. We've logged 27 DBHunter listings originating from Indonesia. #DataBreach #Education #ThreatIntel This entry + more → https://go.darkwebsonar.io/dbhunter-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 3w ago
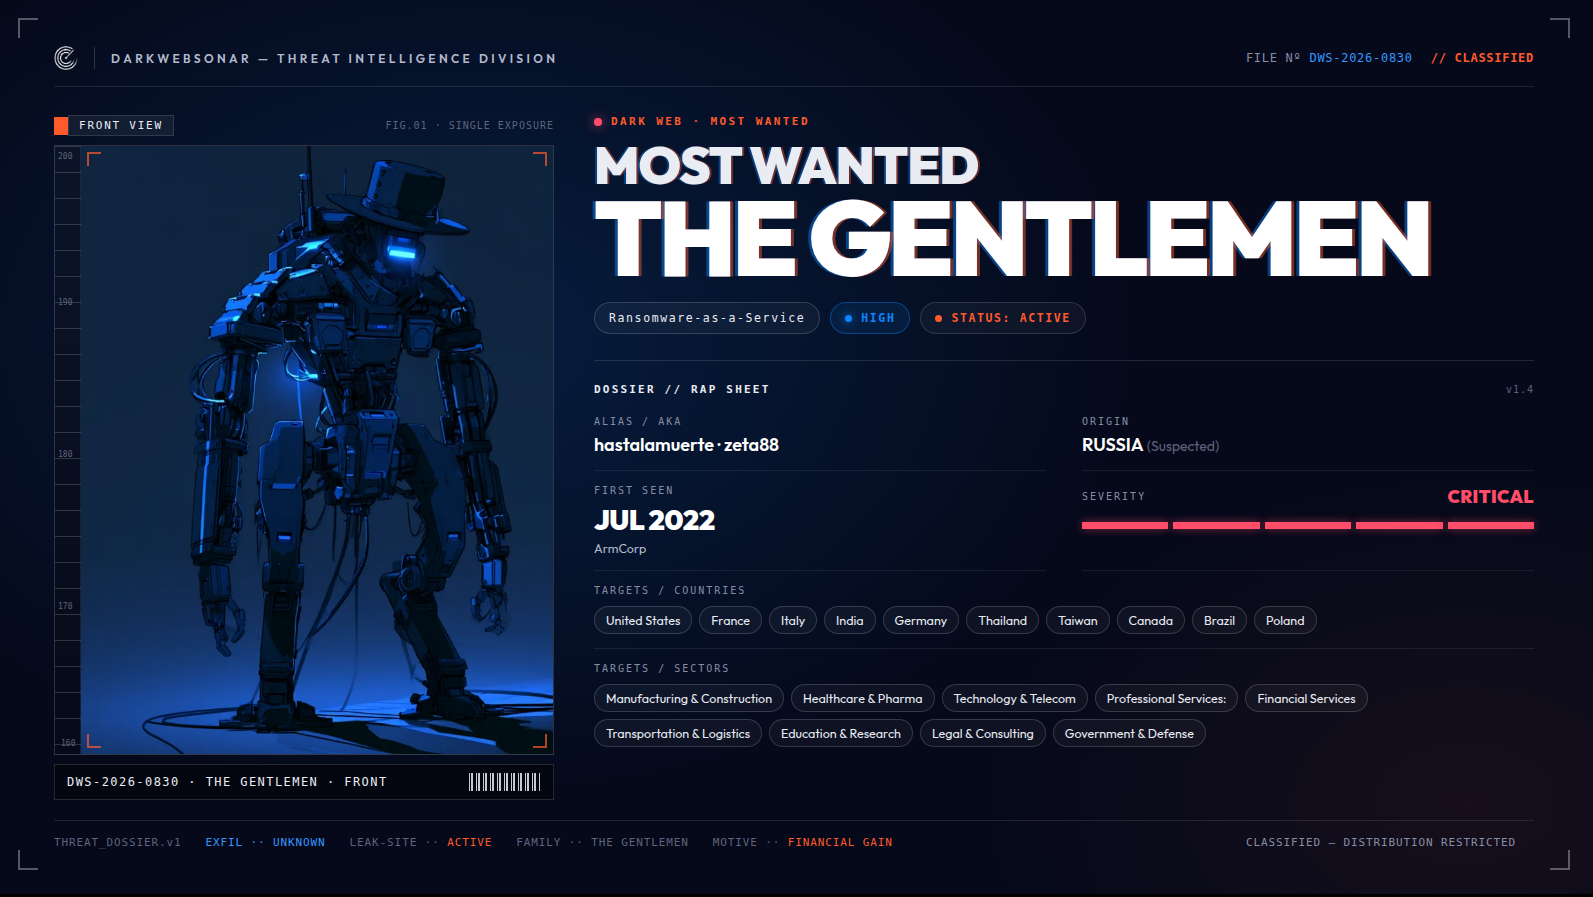
Threat actor spotlight: The Gentlemen (3/4) One August batch from this group's leak site: a Swiss security integrator for police and banks, a semiconductor test supplier, a lottery-tech provider, and a small UK construction subcontractor. Not all big names, but every one sits inside someone's critical supply chain. Manufacturing and construction make up 28% of 610 total claims across 75 countries. Full profile: https://darkwebsonar.io/blog/dark-web-most-wanted-2026-the-gentlemen/ #ThreatIntel #Ransomware
Dark Web Most Wanted 2026: The Gentlemen Ransomware
darkwebsonar.io

Dark Web Most Wanted 2026: The Gentlemen Ransomware

The Gentlemen ransomware has claimed 610 victims across 75 countries. Explore DarkWebSonar victimology, manufacturing targeting, August 2026 batch telemetry, and how the group compares to Qilin on 90-day volume.

0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇹🇷 We tracked a data-leak claim by rape naming Turkey's AK Party as victim, alleging databases from its Akbis information system and Akgençlik youth branch totaling approximately 30 million records. The data is reportedly being distributed freely via Google Drive. rape has logged 7 incidents in our tracking since we began monitoring the actor. #DataLeak #Government #ThreatIntel Details + live feed → https://go.darkwebsonar.io/rape-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇲🇽 We tracked a data leak claim by cenfecracked naming Poder Judicial de Michoacán, the judicial branch of Mexico's Michoacán state. The actor distributed 135 GB via Telegram rather than selling it. We've logged 17 cenfecracked incidents in the past 30 days, concentrated in Mexican government and defense sectors. #DataLeak #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/cenfecracked-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 1mo ago
🇪🇸 We tracked a data leak claim by updap naming Spain's Policia Nacional and DNIE (national identity document) systems as victims. The actor alleges certificates were exfiltrated via an HTTP certificate upload server in 2021. updap has 256 listings in our tracking over the past 30 days. #DataLeak #Government #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/updap-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a ransomware claim by INSOMNIA listing Park Place Behavioral Health Care, a mental health and substance use services provider in Florida offering crisis intervention and telehealth services. We've logged 2 INSOMNIA listings in the past 30 days. #Ransomware #Healthcare #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/insomnia-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2w ago
🇺🇸 We tracked a data breach claim by ShinyHunters naming ShipMonk, a shipping and fulfillment provider. The actor alleges theft of a 91GB database containing approximately 239,000 customer records spanning the United States, United Kingdom, Sweden, Colombia, Brazil, Italy, and Portugal. We've logged 73 ShinyHunters listings in the past 30 days. #DataBreach #Transportation #ThreatIntel Details + live feed → https://go.darkwebsonar.io/shinyhunters-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
Combo List incidents climbed to 2838 this week, up 20.6% from the previous 7 days. The category now accounts for over three quarters of all monitored events. #ComboList #DataBreach #ThreatIntel
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇦🇷 We tracked a data breach claim by APT IRAN مرکز تحقیقاتی naming six organizations across Argentina, Thailand, France, Indonesia, and Brazil. Stolen data ranges from PII and medical insurance records to government retiree information and municipal records. We've logged 2 incidents from this actor in our tracking. #DataBreach #Healthcare #ThreatIntel This entry + more → https://go.darkwebsonar.io/apt-iran-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇷🇴 We tracked NoName057(16) claiming unauthorized access to CCTV surveillance at a Romanian nursing home, reporting real-time access to 15 camera feeds covering multiple facility areas. Actor attributes the access to weak security practices. We've logged 80 incidents from this actor in the past 30 days. #InitialAccess #Healthcare #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/noname057-16-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
Combo List incidents surged to 2332 this week, up 1032.0% from the previous 7 days. The category now dominates our monitoring, accounting for the bulk of overall activity growth. #ComboList #DataBreach #ThreatIntel
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇪🇸 We tracked a data breach claim by mor3nako listing Instituto Nacional de la Seguridad Social (INSS), Spain's social security administration. The actor claims a database of over 3.1 million pensioner records in JSON format. We've logged 2 mor3nako incidents in the past 30 days across our monitoring. #DataBreach #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/mor3nako-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2w ago
🇧🇷 We tracked a data leak claim by Synq1xxs naming Brazil's Receita Federal do Brasil, the Federal Revenue Service. The actor claims roughly 70 million records from the CNPJ registry, including company legal names, CNPJ identification numbers, tax classifications, and location data. Synq1xxs has logged 9 listings in the last 30 days across our monitoring. #DataLeak #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/synq1xxs-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 1mo ago
🇮🇱 We tracked a data breach claim targeting the Israeli Government Data Portal (info.data.gov.il). A forum post by a group identifying as Cyber Team Indonesia alleges leaked database content accessible via external file-sharing. NATION OF SAVIORS has 110 incidents in our tracking, with 12 linked to Israel and a focus on Government & Defense targets. #DataBreach #Government #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/nation-of-saviors-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇮🇶 We tracked a data breach claim by MrDarkRoot naming the Kurdistan Region Ministry of Justice, alleging unauthorized network access and exfiltration of approximately 120,300 personal records from the Ministry, Kurdistan Region Lawyers Foundation, and Khabat Organization. We've logged 6 MrDarkRoot incidents in our tracking, with activity concentrated in government and defense sectors. #DataBreach #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/mrdarkroot-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇲🇽 We tracked a data leak claim by homercracker listing SEPyC, the Secretaría de Educación Pública y Cultura in Sinaloa, Mexico. The alleged dataset includes employee personal details, addresses, CURPs, and RFCs distributed via Telegram. homercracker has 4 tracked incidents, all targeting Mexican government entities. #DataLeak #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/homercracker-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇪🇸 We tracked a data breach claim by DBHunter listing Lopesan Hotel, a Spanish hospitality and food service operator. The claim alleges 27,629 records dated 2024. We've logged 50 DBHunter listings in the past week in our monitoring. #DataBreach #ThreatIntel Details + live feed → https://go.darkwebsonar.io/dbhunter-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
We picked up forum user Rici144 allegedly offering webshell access to multiple .edu domain institutions, providing initial access into educational networks. We've tracked Rici144 across 12 incidents, mostly in the education and government sectors, with activity spiking recently. #InitialAccess #Education #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/rici144-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇬🇧 We tracked a ransomware claim by CHAOS naming Craneware Group, a UK health-tech firm. CHAOS alleges the breach exposed sensitive data contrary to the company's public characterization of the stolen information. We've logged 4 CHAOS listings in the United Kingdom in our tracking. #Ransomware #Healthcare #ThreatIntel Details + live feed → https://go.darkwebsonar.io/chaos-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇵🇭 We tracked a data breach claim by XPLOITZ targeting the Philippine Mines and Geosciences Bureau, part of the Department of Environment and Natural Resources. The actor claims to have external documentation of the exploit. We've logged 114 XPLOITZ listings in the past 30 days across our monitoring. #DataBreach #Government #ThreatIntel Details + live feed → https://go.darkwebsonar.io/xploitz-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
Threat actor spotlight: Miyako Here's an anomaly worth flagging in this initial access broker's data: China is their second most listed country, behind only the US. That rarely happens. Chinese organizations almost never surface on Western ransomware leak sites, so China ranking this high is a real divergence from the datasets most CTI teams calibrate on. It points to either opportunistic exposure of Chinese edge devices or deliberate inventory diversification, and either way it's a reminder that leak-site data alone is a partial map of who's actually being targeted. Full profile and historical telemetry: https://darkwebsonar.io/blog/dark-web-most-wanted-2026-miyako/ #ThreatIntel #AccessBroker #China
darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2w ago
🇵🇪 We tracked a data breach claim by Frouzenx naming the Government of Peru. The actor alleges a SQL injection attack against government systems with exfiltration of employee records. We've logged 13 Frouzenx listings in the past 30 days, concentrated in government and defense sectors across the region. #DataBreach #ThreatIntel Details + live feed → https://go.darkwebsonar.io/frouzenx-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
We picked up a data-leak claim by Iron Atlas New Generation naming INTERPOL, the international law enforcement organization. The actor claims unauthorized access to an INTERPOL database. We've tracked 2 Iron Atlas New Generation listings in the past 30 days across our monitoring. #DataLeak #ThreatIntel This entry + more → https://go.darkwebsonar.io/iron-atlas-new-generation-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 1mo ago
🇮🇹 We tracked a ransomware claim by BravoX listing Verona 83, a transportation and logistics operator in Italy. BravoX has logged 4 listings in the past 30 days, with recent activity spiking to 3 incidents in the last week. #Ransomware #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/bravox-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇧🇴 We tracked a data-leak claim by 'SALDIRGAN listing Utepsa University, a higher education institution in Bolivia. The actor claims to have leaked a database containing 67,027 records. We've logged 3 'SALDIRGAN listings in the past 30 days across our monitoring. #DataLeak #Education #ThreatIntel Details + live feed → https://go.darkwebsonar.io/saldirgan-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇬🇹 We tracked a data leak claim by sc4r_0x00 listing AUXPMAG, an education organization in Guatemala. The claimed exposure includes debt collection records with national ID numbers, payment data, and location information for over 100,000 teachers. We've logged 4 sc4r_0x00 listings in the past 30 days across our monitoring. #DataLeak #Education #ThreatIntel Details + live feed → https://go.darkwebsonar.io/sc4r-0x00-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇮🇩 We tracked a data breach claim by BABAYO EROR SYSTEM targeting sipraja.kuduskab.go.id, the population information system operated by Kudus Regency Government in Indonesia. The actor alleges resident and personal data has been exfiltrated from the regional government entity. We've logged 14 incidents from BABAYO EROR SYSTEM in the past 30 days across our monitoring. #DataBreach #Government #ThreatIntel Details + live feed → https://go.darkwebsonar.io/babayo-eror-system-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 3w ago
🇬🇷 We tracked a data leak claim by 'SALDIRGAN listing National Technical University of Athens research infrastructure, alleging a MariaDB database containing 13,905 records. We've logged 10 'SALDIRGAN listings in the past 30 days across education and research sectors. #DataLeak #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/saldirgan-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a ransomware claim by SAFEPAY listing BNP Distributing Company, a New York-based distributor serving the restaurant, hotel, and retail sectors. We've logged 33 SAFEPAY listings in the past 30 days across our monitoring. #Ransomware #ThreatIntel Details + live feed → https://go.darkwebsonar.io/safepay-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a ransomware claim by Global Secret Group listing Pavillon, a North Carolina-based substance abuse treatment facility with 100-200 employees. The actor alleges exfiltration of 646 GB of data across 47,950 files. We've logged 13 Global Secret Group listings in the past 30 days, mostly targeting manufacturing and financial services. #Ransomware #Healthcare #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/global-secret-group-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a ransomware claim by INC Ransom listing Virginia Peninsula Regional Jail, a regional correctional facility in Williamsburg, Virginia. We've logged 34 INC Ransom listings in the past 30 days, with 12 in just the last week. #Ransomware #Government #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/inc-ransom-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇲🇽 We tracked a data leak claim by sc4r_0x00 listing Mexico's Hidalgo Health Secretariat. The actor claims 14,050 employee records including full names, CURP national ID numbers, tax IDs, positions, and salary information. We've logged 5 sc4r_0x00 listings in the last 30 days, mostly targeting government and defense sectors across Mexico and Central America. #DataLeak #Government #ThreatIntel Details + live feed → https://go.darkwebsonar.io/sc4r-0x00-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a data-leak claim by Golden falcon naming the U.S. Department of Defense. The actor alleges coordinates of multiple U.S. defense systems in the Middle East have been shared with Iranian entities. We've logged 1 Golden falcon listing in the past 7 days across our monitoring. #DataLeak #Defense #ThreatIntel Details + live feed → https://go.darkwebsonar.io/golden-falcon-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇲🇽 We tracked a data breach claim by Julianigz18 advertising a 1TB database compilation sourced from Mexican government agencies (ISSSTE, IMSS, IFE-INE), financial institutions (Bancomer, Banorte), and telecom providers (AT&T Mexico, Telcel, CFE, REPUVE). We've logged 3 incidents linked to Julianigz18, with 2 in the past week. #DataBreach #ThreatIntel This entry + more → https://go.darkwebsonar.io/julianigz18-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 1w ago
🇧🇩 We tracked blacknet-00 claiming unauthorized access to Bangladesh Army network infrastructure at Qadirabad Cantonment. The actor alleges compromise of over 400 devices with access to PPPoE connections, backup files containing passwords, login logs, and router configurations. blacknet-00 has logged 19 incidents in the past week across our monitoring. #InitialAccess #ThreatIntel This entry + more → https://go.darkwebsonar.io/blacknet-00-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇮🇩 We tracked a data breach claim by ERROR SYSTEM listing Kudus Regency Government in Indonesia. The actor claims access to a population database and is soliciting $2,500 USD in Bitcoin via Telegram. We've logged 11 ERROR SYSTEM listings in the last 30 days across our monitoring. #DataBreach #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/error-system-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇧🇷 We tracked a data breach claim by BENABDELOHZZ listing Prefeitura de Fortaleza, Brazil's Fortaleza municipal government. The actor claims a large SQL database dump from the city portal containing internal records, surveys, intranet systems, password tables, and city project platforms. We've logged 3 BENABDELOHZZ listings in the past 30 days across our monitoring. #DataBreach #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/benabdelohzz-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇵🇭 We tracked a data leak claim by hhhhhaplus naming eight Philippine government agencies including AFP, BFP, PNP, NaPolCom, and SSS. The actor claims access to personnel and pension database records. We've logged 12 hhhhhaplus incidents since tracking began, with 2 in the past week. #DataLeak #Government #ThreatIntel Details + live feed → https://go.darkwebsonar.io/hhhhhaplus-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇮🇱 We tracked a data breach claim by Cyber Support Front naming IMCO Industries, an Israeli military-industrial company. The actor claims access to approximately 250TB of data, with 30TB exfiltrated including technical documents, production files, and defense contractor information. We've logged 7 Cyber Support Front listings in the past 30 days, mostly targeting Israeli entities. #DataBreach #GovernmentDefense #ThreatIntel Details + live feed → https://go.darkwebsonar.io/cyber-support-front-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked a ransomware claim by CHAOS naming Vit-Best Nutrition, a US-based nutrition supplier. The actor alleges complete data exfiltration with 3% of data already published and threatens to release the remaining 97% within 48 hours. We've logged 14 CHAOS listings in the past 30 days across our monitoring. #Ransomware #Healthcare #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/chaos-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2w ago
🇺🇸 We tracked a data breach claim by ShinyCorps listing Valley Health Team, a US healthcare provider. ShinyCorps claims the database contains 160,870 patient records, 4.18 million diagnoses, and 7.6 million unencrypted EHR scans. We've logged 4 ShinyCorps listings in the past week across our monitoring. #DataBreach #Healthcare #ThreatIntel More on this and other incidents → https://go.darkwebsonar.io/shinycorps-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇷🇺 We tracked a data leak claim by BENABDELOHZZ listing an aggregated dataset of 238 million Russian personal records. The data is claimed to include names and dates of birth from FSSP, traffic police, mobile operator, and residency databases covering 1990–2022. We've logged 3 BENABDELOHZZ listings in the past 30 days. #DataLeak #Government #ThreatIntel Details + live feed → https://go.darkwebsonar.io/benabdelohzz-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇺🇸 We tracked forum actor miyako advertising alleged initial access to a large US casino and resort property, listed for $500 with escrow transaction through a designated middleman. We've logged 22 miyako listings in the past 30 days across our monitoring. #InitialAccess #Hospitality #ThreatIntel Details + live feed → https://go.darkwebsonar.io/miyako-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇮🇳 We tracked a data breach claim by kazu listing PappyJoe, an India-based healthcare practice management platform. The actor claims 413GB exfiltrated including PII for 6.8 million patients, with a $250k ransom demand and 05/08/2026 deadline. We've logged 11 kazu listings in the past 30 days. #DataBreach #Healthcare #ThreatIntel Details + live feed → https://go.darkwebsonar.io/kazu-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 2mo ago
🇵🇪 We tracked a data leak claim by yar1ner listing RENIEC, Peru's national civil registry agency. The actor alleges approximately 31 million records exposed from the registry database. We've logged 1 yar1ner incident in the past week across our monitoring. #DataLeak #Government #ThreatIntel This entry + more → https://go.darkwebsonar.io/yar1ner-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 1mo ago
🇮🇹 We tracked a data leak claim by DaOnlySpark listing LivTours, an Italian-based European tour booking platform. The claimed 1.5GB database includes 295 tables spanning orders, bookings, traveler records, vouchers, payment logs, and marketing data. We've logged 12 DaOnlySpark listings in the last 30 days. #DataBreach #Hospitality #ThreatIntel This entry + more → https://go.darkwebsonar.io/daonlyspark-mastodon
go.darkwebsonar.io
0
0
0
0
Open post
DarkWebSonar @darkwebsonar@infosec.exchange
· 3w ago
🇧🇴 We tracked a data breach claim by DBHunter listing Universidad Autónoma Tomás Frías, a public university in Bolivia. The actor claims a database of student and applicant records from 2004-2025 containing national ID card numbers, full names, degree programs, and student IDs. DBHunter has 91 listings in the past 30 days across our monitoring. #DataBreach #Education #ThreatIntel This entry + more → https://go.darkwebsonar.io/dbhunter-mastodon
go.darkwebsonar.io
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 09:39:07 UTC