Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Barberousse

@barberousse_bin@todon.eu
mastodon 4.7.3+todon
  • Open on todon.eu

Malware Researcher at @ESETresearch@infosec.exchange
:anarchistflagblack: :blackcat: :antifa:
Based in Montreal
He/Him, Il/lui :polyamory:

307 Followers
285 Following
9 Posts
Joined October 31, 2022
Keybase:
https://keybase.io/barberousse
WeLiveSecurity (Work blog):
https://www.welivesecurity.com/author/acotecyr/
Twittodon:
https://twittodon.com/share.php?t=barberousse_bin&m=barberousse_bin@todon.eu
Open post
Barberousse @barberousse_bin@todon.eu
· 2w ago
RE: https://infosec.exchange/@ESETresearch/117285559180479202 I want to thank the threat actors 🐦‍⬛ for using a version of Mbed TLS that contains an excerpt of Lewis Carroll's Jabberwocky poem. It was a great source of inspiration when it came to naming the backdoor and the report 😄
Open quoted post
Quoting
ESET Research
@ESETresearch@infosec.exchange
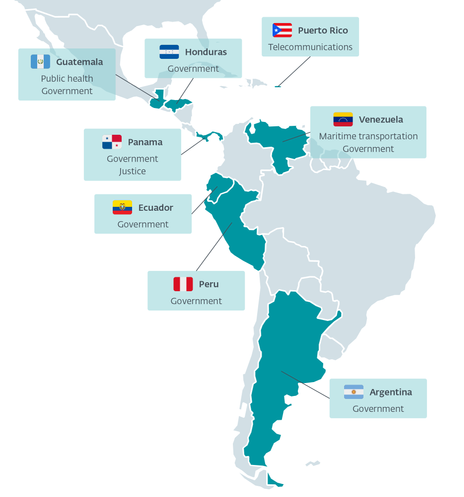
#ESETresearch discovered SparroWocky, a new backdoor of the #FamousSparrow APT group. This new malware has quickly replaced SparrowDoor as the 🇨🇳 China-aligned group’s flagship backdoor. https://www.welivesecurity.com/en/eset-research/beware-sparrowock-backdoor-bites-commands-catch/ The switch to SparroWocky happened shortly after FamousSparrow started targeting Latin America almost exclusively, going mainly after governmental entities. This is most probably part of 🇨🇳 China’s reaction to the increased 🇺🇸 US interest in the region. SparroWocky is a highly modular C++ backdoor built with stealthiness in mind. Its capabilities include collecting general info about the compromised machine, exfiltrating files, and taking screenshots. It can also load and execute BOF (Beacon Object File) files. With the transition to the new backdoor, FamousSparrow started to incorporate code from open-source projects directly into its malware. Specifically, we noticed that SparroWocky uses Mbed TLS, MinHook, and COFF Loader. The developers also implemented various anti-analysis techniques: SilentMoonwalk for call spoofing, concealing thread start address from security products using the MinHook library, and a custom PE loader with integrated host process camouflage. IoCs available in our GitHub repo: https://github.com/eset/malware-ioc/tree/master/famoussparrow
Open quoted post
infosec.exchange

ESET Research: "#ESETresearch discovered SparroWocky, a new backd…" - Infosec Exchange

5
1
3
0
Open post
Barberousse @barberousse_bin@todon.eu
· 2mo ago
Replying to
@WeirdWriter@caneandable.social At least a few sites have been using this kind of fake font shenanigans as DRM for a while. It's a nightmare for accessibility, and just generally a terrible user-experience (as any kind of DRM usually is): Screen reader -> Broken, or sounds like it's possessed by an evil robot Copy-paste -> Garbage Search -> Haha, no Translate -> Good luck hand-copying that language you don't know I can't remember which exact site it was, but it was one of those that let you read limited previews of scientific papers.
14
1
5
0
Open post
Barberousse @barberousse_bin@todon.eu
· 6mo ago

@ESETresearch@infosec.exchange is looking for an additional Strategic Threat Analyst to join our team!
The role is mostly focused on the socio/geopolitical context of the APT/cyberespionage landscape (i.e. don't expect to reverse engineer malware 😉)

My colleague who's been doing this job for about a year just said that it's "the coolest job in the world". I'm not sure how much of that was a joke, but he doesn't seem to be too miserable in his role 😄

#FediHire #FediJob

https://jobs.eset.com/en-US/ESET_External/job/Analyste-du-renseignement-stratgique-sur-les-menaces---Cyberespionnage---Strategic-Threat-Intelligence-Analyst---Cyberespionage_JR-05715

todon.eu
9
3
12
1
Open post
Barberousse @barberousse_bin@todon.eu
· 6mo ago

Just found myself using MUST and SHOULD in a discussion with a colleague. This is your brain on RFC2119 kids.
Please read RFCs in moderation; over-consumption can have real long-term impacts

5
0
0
0
Open post
Barberousse @barberousse_bin@todon.eu
· 6mo ago
Replying to
@Deidzoeb @Em0nM4stodon Not only did we circumvent age restrictions; bypassing restrictions sometime became a goal in and of itself. I certainly wasn't the only kid who did stupid stuff just to see if I could outsmart the restrictions, regardless of what they were keeping me from😅
4
0
0
0
Open post
Barberousse @barberousse_bin@todon.eu
· 7mo ago
Replying to
@mttaggart@infosec.exchange You should also read this one then :) https://sightlessscribbles.com/posts/the-bookstore-hope/
sightlessscribbles.com

The Bookstore Hope, Sightless Scribbles

A fabulously gay blind Romance author.

3
0
1
0
Open post
Barberousse @barberousse_bin@todon.eu
· 5mo ago

@GossiTheDog@cyberplace.social "How I solved Cyber using Anatidae-assisted immersion"

1
0
0
0
Open post
Barberousse @barberousse_bin@todon.eu
· 6mo ago

The whois module we were using in an internal tool has been unmaintained for a while... so I'm learning more about RDAP than I ever wanted to 🤓

Thank the ICANN for providing a reference client implementation (https://github.com/icann/icann-rdap), but what's up with that default output format?

I don't mind the ASCII tables so much, but centering them based on the width of the terminal window just feels wrong 😅
(yes, I know you can change the format through various options)

github.com
1
0
0
0
Open post
Barberousse @barberousse_bin@todon.eu
· 5mo ago
Replying to
@tek For Canada: Fulfilled requests from Canada for IP address and/or phone number: Q1 —134 Affected users: Q1 —142
0
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 04:51:22 UTC